01 | Tool Specifications & Architectural Profile
Compiled as an intermediate language (CIL/MSIL) PE32 executable targeting .NET Framework v2.0 through v4.6. Binary sections consist of standard MSIL metadata headers (.text, .rsrc, .reloc), lacking native x86 machine opcodes prior to JIT compilation. Common crypter overlays include PureCrypter, CypherIT (AutoIt wrapper), and custom XOR/AES stagers that store the payload inside embedded resource blobs or bitmap pixel data (steganography). The runtime resolves external dependencies dynamically via System.Reflection.Assembly.Load, evading disk-based static file signatures.
02 | Operator Interface & Configuration Struct Model
The builder utility is developed in WinForms (.NET GUI) and provides operator configuration for delivery conduits: SMTP Server (Host, Port, SSL toggle, Username, Password, Target Recipient), FTP (Host, User, Pass, Port, Subfolder), Telegram Bot (API Token, Target Chat ID), and Discord Webhook URL. It exposes toggles for local surveillance modules: Keylogger (Interval minutes), Screenshot Capturer (JPEG quality 50-100%, interval), Clipboard Logger, Webcam Grabber, and Target Application Checklists. Configuration variables are compiled directly into the binary either as a .NET resource named 'Properties.Settings' or initialized within the static constructor (.cctor) of an obfuscated class via multi-stage Base64 decoding and single-byte or multi-byte XOR masking.
struct Agent_Tesla_Config {
    uint32_t magic;
    char c2_host[128];
    uint16_t port;
    char install_path[260];
    char mutex[64];
    uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
Execution relies on Process Hollowing (RunPE). The unpacked stub creates a suspended legitimate Windows process (e.g., RegSvcs.exe, RegAsm.exe, vbc.exe, cvtres.exe, or MSBuild.exe) using CreateProcessW(CREATE_SUSPENDED = 0x00000004). It queries the suspended thread context via GetThreadContext, carves the original executable memory via NtUnmapViewOfSection / ZwUnmapViewOfSection, allocates replacement virtual memory with VirtualAllocEx(PAGE_EXECUTE_READWRITE = 0x40), and writes the decompressed Agent Tesla PE headers and sections using WriteProcessMemory. The entry point register (EAX on x86, RCX on x64) or PEB base (EBX+8 / RDX+0x10) is rewritten, followed by SetThreadContext and ResumeThread. Memory evasion features include AMSI patching by writing a ret instruction (0xC3) to amsi.dll!AmsiScanBuffer and ETW suppression via EtwEventWrite nop-sledging.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Agent Tesla binary:
Low-level keyboard hook installed via SetWindowsHookExW(idHook=WH_KEYBOARD_LL=13). Intercepts virtual key codes, translates them using GetKeyboardState and ToAscii, and prefixes entries with active window titles captured via GetForegroundWindow and GetWindowTextW.
Parses SQLite databases and configuration files across 50+ applications: Chromium-based browsers (extracts encrypted_value from Login Data and decrypts AES-256-GCM using keys decrypted from Local State via CryptUnprotectData DPAPI), Mozilla Firefox (loads nss3.dll dynamically and invokes PK11SDR_Decrypt on logins.json / key4.db), Outlook (parses Windows Registry values under HKCU\Software\Microsoft\Office and Windows NT Profiles), Thunderbird, FileZilla (sitemanager.xml, recentservers.xml), WinSCP, CoreFTP, and VPN clients.
Monitors clipboard content via polling loops or AddClipboardFormatListener, buffering copied strings into memory logs.
Captures desktop screen coordinates via System.Drawing.Graphics.CopyFromScreen, compresses bitmaps to JPEG format, and schedules asynchronous transmission.
Installs registry keys under HKCU\Software\Microsoft\Windows\CurrentVersion\Run or registers a scheduled task via schtasks.exe /create /tn <task_name> /tr <path> /sc onlogon.
05 | Wire Protocol & C2 Communication Framing
Exfiltration channels operate over one of four selectable transports: 1) SMTP: Connects via System.Net.Mail.SmtpClient using STARTTLS (TCP 587) or SMTPS (TCP 465). Generates an email with subject line '<ComputerName>/<UserName> Agent Tesla Keylogger - <Timestamp>'. The message body contains HTML-formatted keylog text and attached ZIP/TXT archives of recovered credentials. 2) FTP: Uploads log files named 'log.html' and 'passwords.txt' using FtpWebRequest in passive mode. 3) Telegram: Posts JSON multipart/form-data to 'https://api.telegram.org/bot<TOKEN>/sendDocument' with the 'chat_id' parameter and file attachment. 4) HTTP POST: Issues HTTP/1.1 POST requests to an operator panel URL containing Base64-encoded, DES/AES-encrypted POST parameters.
06 | Verified Detection Signatures (YARA & Sigma)
rule Mal_Win_AgentTesla_Engine {
    meta:
        description = "Detects unpacked Agent Tesla MSIL payload and credential recovery routines"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        hash = "7e8c0e1e6f7797e883a2d2fb41b71d9d936e355c7a40b90e66ecb708b73fa6c5"
        threat_id = "TF-006"
    strings:
        $s1 = "GetSubKeyNames" ascii wide
        $s2 = "webcam" ascii wide fullword
        $s3 = "Account:" ascii wide
        $s4 = "Password:" ascii wide
        $s5 = "mail.smtp." ascii wide
        $s6 = "api.telegram.org/bot" ascii wide
        $s7 = "System.Net.Mail" ascii
        $hook = { 6A 00 68 0D 00 00 00 FF 15 [4] } // PUSH 0; PUSH 13 (WH_KEYBOARD_LL); CALL SetWindowsHookEx
        $msil_meta = { 42 53 4A 42 } // BSJB signature
    condition:
        uint16(0) == 0x5A4D and
        $msil_meta at 0 and
        4 of ($s*)
}title: Suspicious Outbound SMTP from Non-Mail Native Processes
id: b8a72e90-c034-4b52-9856-11f44e12e006
status: production
description: Detects native Windows .NET utility binaries establishing direct outbound SMTP/SMTPS connections, indicative of Agent Tesla exfiltration.
references:
- https://cybertrace.io/threats/agenttesla-whitepaper.html
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
category: network_connection
product: windows
detection:
selection_process:
Image|endswith:
- '\RegSvcs.exe'
- '\RegAsm.exe'
- '\vbc.exe'
- '\cvtres.exe'
- '\MSBuild.exe'
- '\InstallUtil.exe'
selection_port:
DestinationPort:
- 25
- 465
- 587
condition: selection_process and selection_port
falsepositives:
- Legitimate bespoke administrative automation scripts (rare)
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
7e8c0e1e6f7797e883a2d2fb41b71d9d936e355c7a40b90e66ecb708b73fa6c5
4cf16ae8e1d51a66a7b7381ff574b5eb020739cbe49852899464e8e50b4ec7b8
d89fb6a3459c5d140e698822008ad921509fa2f0f4a21191ec4d9a218d6a8b94
smtp.mail.ru:587
smtp.zoho.com:587
api.telegram.org:443
ftp.interlocklogistics[.]com:21
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\Updates
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\ClientCore
%APPDATA%\Roaming\SubDir\FileName.exe
%TEMP%\log.html
%TEMP%\passwords.txt
Tesla-Client-Instance-Mutex
AgentTesla_Singleton_Lock
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
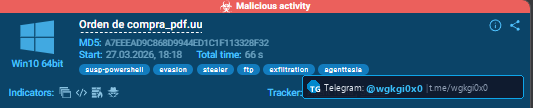
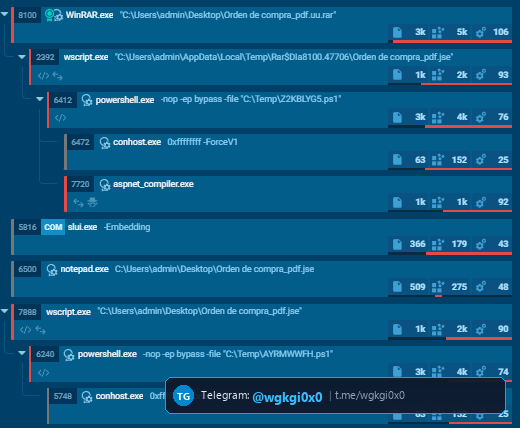
Forensic sandbox process hierarchy showing weaponized office document execution and payload staging.
Decompiled .NET routine responsible for packaging keystroke logs and dispatching them via TLS SMTP channels.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and SMTP, FTP, Telegram Webhooks, Discord API command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Agent Tesla (Spyware)
Commercial-grade spyware framework compiled in .NET with modular exfiltration pipelines (SMTP, FTP, Telegram, Webhook) and low-level Win32 keyboard hooks.
C2 Architecture: Exfiltration channels operate over one of four selectable transports: 1) SMTP: Connects via System.Net.Mail.SmtpClient using STARTTLS (TCP 587) or SMTPS (TCP 465). Generates an email with subject line '<ComputerName>/<UserName> Agent Tesla Keylogger
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Agent Tesla (Spyware)
Детальный технический анализ Agent Tesla — это Шпионское программное обеспечение и кейлоггер, разработанный на стеке .NET Framework 4.5 / MSIL (Visual Basic .NET / C#). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (SMTP over TLS (Port 587/465), FTP Passive Mode, Telegram HTTPS API, Discord Webhook) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием SMTP over TLS (Port 587/465), FTP Passive Mode, Telegram HTTPS API, Discord Webhook, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Agent Tesla (Spyware) विश्लेषण
Agent Tesla एक परिष्कृत स्पाइवेयर और कीलॉगर निगरानी टूल है जिसे .NET Framework 4.5 / MSIL (Visual Basic .NET / C#) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (SMTP over TLS (Port 587/465), FTP Passive Mode, Telegram HTTPS API, Discord Webhook) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: SMTP over TLS (Port 587/465), FTP Passive Mode, Telegram HTTPS API, Discord Webhook आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).