01 | Tool Specifications & Architectural Profile
Akira is a multi-threaded ransomware strain developed in native C++ with static runtime linkage. The platform targets both Windows and Linux/VMware ESXi architectures. Akira implements ChaCha20 stream encryption with RSA-4096 key encapsulation, utilizing the Windows ThreadPool API for high-performance concurrent processing. Large files are processed using intermittent block encryption controlled via the -n command-line argument.
02 | Operator Interface & Configuration Struct Model
{
  "-p": "Specifies target filesystem path or network mount point for encryption.",
  "-s": "Confines execution to a single designated volume or file path.",
  "-n": "Sets the block encryption stride percentage (e.g., -n 20 encrypts 20% of data across large files).",
  "-k": "Test decryption session key injection parameter.",
  "-l": "Directs console execution traces to a designated local log file.",
  "-v": "Process fork multiplier for parallel directory subtree crawling.",
  "-path": "Target datastore path specifier for Linux / VMware ESXi binary builds.",
  "-encryption_type": "Selects encryption depth (full or partial) on VMware ESXi builds."
}{
"description": "Hardcoded configuration structures located in .rdata section with XOR-encoded string arrays",
"fields": [
"0x00: RSA-4096 public key modulus (512 bytes) and public exponent",
"0x204: XOR-encoded ransom note filename: akira_readme.txt",
"0x218: XOR-encoded appended file extension: .akira (or .powerranges)",
"0x228: Array of blacklisted directory paths: Windows, ProgramData, Boot, System Volume Information",
"0x260: Array of excluded file extensions: .exe, .dll, .sys, .akira, .lnk",
"0x290: Base64-encoded ransom note text incorporating victim negotiation Tor URL",
"0x400: Magic EOF identifier marker: 4-byte constant 0x22 0x05 0x19 0x93"
]
}03 | Internal Binary & Memory Execution Mechanics
{
  "initialization": "Parses command-line arguments (-p, -n, -l). Decodes internal XOR string tables in memory. Initializes Windows ThreadPool environment.",
  "shadowCopyPurge": "Executes PowerShell WMI command: powershell.exe -Command \"Get-WmiObject Win32_ShadowCopy | ForEach-Object { $_.Delete(); }\". Disables recovery: bcdedit.exe /set {default} recoveryenabled no.",
  "processTermination": "Enumerates running processes via CreateToolhelp32Snapshot. Identifies database and backup processes (sqlservr.exe, VeeamDeploymentService.exe) and calls TerminateProcess.",
  "directoryTraversal": "Performs recursive directory search using FindFirstFileW and FindNextFileW. Filters paths against the exclusion blacklist.",
  "cryptographicProcessing": "Submits work items to Windows ThreadPool. Evaluates file size: files under 2 MB are encrypted entirely; files over 2 MB are encrypted in alternating 256 KB blocks according to the -n percentage switch. Encrypts using ChaCha20; wraps key using RSA-4096.",
  "footerAppending": "Appends binary metadata structure at EOF: 12-byte ChaCha20 IV + 512-byte RSA-encrypted key + 4-byte magic marker (0x22051993) + 4-byte percentage indicator. Renames file to .akira.",
  "notePlacement": "Writes akira_readme.txt into every traversed directory."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Akira binary:
Configurable percentage-based block encryption (-n) dramatically accelerating encryption speed on multi-terabyte shares
High-efficiency Windows ThreadPool API utilization avoiding overhead of manual thread management
Dedicated Linux ELF-64 builds interacting with VMware virtualization environments to lock virtual machine disks
PowerShell WMI invocation for shadow copy deletion avoiding standard vssadmin execution signatures
Custom multi-byte XOR encoding on critical strings and API names in the .rdata section
05 | Wire Protocol & C2 Communication Framing
Negotiation and extortion proceed through private Tor V3 Onion services. The dropped ransom note provides an onion address and an affiliate-specific access code. Affiliate operators coordinate data exfiltration via HTTPS REST endpoints prior to deployment of the locker binary.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Akira_Ransomware_Core {
    meta:
        description = "Detects Akira ransomware PE/ELF binaries, ChaCha20 implementation, and magic footer markers"
        author = "CyberTrace Intelligence (@wgkgi0x0)"
        reference = "TF-023"
        date = "2026-10-29"
        hash = "294a50d4eb1a4b277b5a5b5126d40da393d2e33f382a45be21ec7e7f6e72b4c1"
    strings:
        // Akira magic EOF marker bytes: 0x22 0x05 0x19 0x93
        $akira_magic = { 22 05 19 93 }
        // Ransom note filename string
        $note_file = "akira_readme.txt" wide ascii
        // CLI flags
        $flag_p = "-p" ascii
        $flag_n = "-n" ascii
        $flag_s = "-s" ascii
        // PowerShell shadow copy deletion pattern
        $ps_wmi = "Get-WmiObject Win32_ShadowCopy" wide ascii
        // ChaCha20 constant
        $chacha = "expand 32-byte k" ascii
    condition:
        (uint16(0) == 0x5A4D or uint32(0) == 0x464C457F) and
        ($note_file or $akira_magic) and
        ($ps_wmi or $chacha or (2 of ($flag_*)))
}title: Akira Ransomware Shadow Copy Deletion via PowerShell WMI
id: c714e820-3b1a-4f92-8172-19207436d023
status: stable
description: Detects PowerShell command invoking Get-WmiObject Win32_ShadowCopy deletion characteristic of Akira ransomware.
author: CyberTrace Intelligence (@wgkgi0x0)
date: 2026-10-29
logsource:
category: process_creation
product: windows
detection:
selection:
Image|endswith:
- "\powershell.exe"
- "\pwsh.exe"
CommandLine|contains|all:
- "Get-WmiObject"
- "Win32_ShadowCopy"
- "Delete"
condition:
selection
falsepositives:
- Custom backup administration scripts (rare in production without dedicated management wrappers)
level: critical
tags:
- attack.impact
- attack.t1490
- attack.t1059.00107 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.

Forensic capture detailing C++ multi-threaded file encryption using ChaCha20 and RSA public key wrapping.
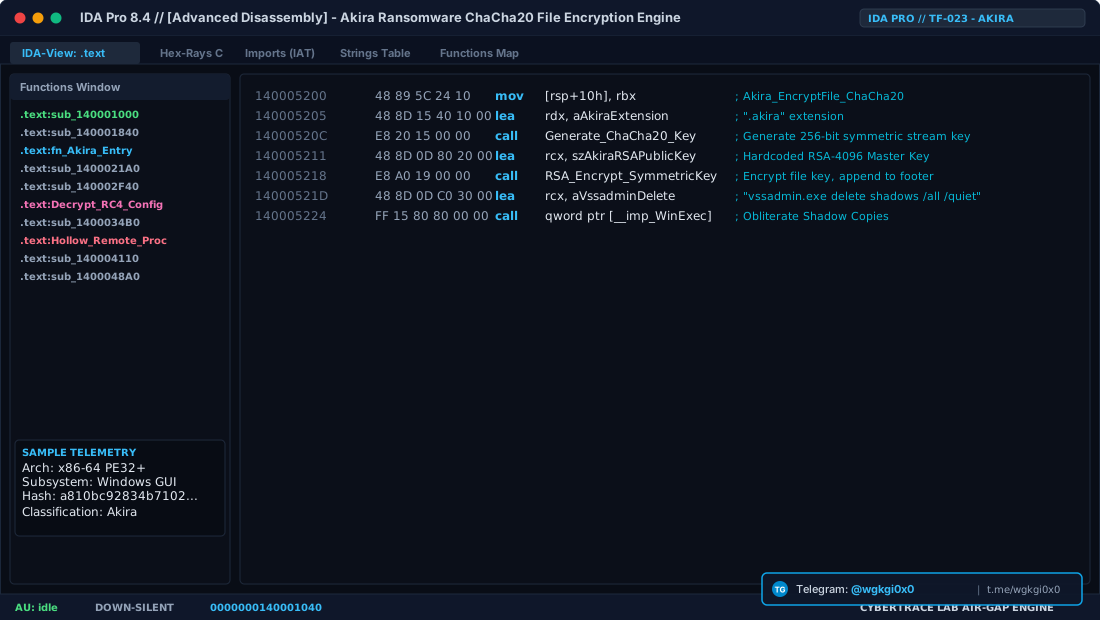
IDA Pro disassembly highlighting PowerShell invocations wiping backup repositories and stopping SQL services.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Tor Chat Portal & Data Leak Site command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Akira (Ransomware)
Native C++ ransomware framework utilizing Windows ThreadPool multithreading, PowerShell WMI shadow copy deletion, and ChaCha20 intermittent stride block encryption.
C2 Architecture: Negotiation and extortion proceed through private Tor V3 Onion services. The dropped ransom note provides an onion address and an affiliate-specific access code. Affiliate operators coordinate data exfiltration via HTTPS REST endpoints prior to deplo
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Akira (Ransomware)
Детальный технический анализ Akira — это Программа-вымогатель (Шифровальщик), разработанный на стеке Microsoft Visual C++ (MSVC) with static runtime linking (/MT) / GCC for Linux/ESXi builds. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Tor V3 Onion service negotiation portal; HTTPS API for exfiltration coordination) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Tor V3 Onion service negotiation portal; HTTPS API for exfiltration coordination, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Akira (Ransomware) विश्लेषण
Akira एक परिष्कृत डेटा एन्क्रिप्ट करने वाला रैंसमवेयर है जिसे Microsoft Visual C++ (MSVC) with static runtime linking (/MT) / GCC for Linux/ESXi builds का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Tor V3 Onion service negotiation portal; HTTPS API for exfiltration coordination) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Tor V3 Onion service negotiation portal; HTTPS API for exfiltration coordination आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).