01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C# Compiler (csc.exe)",
  "runtime": ".NET Common Language Runtime (CLR) 4.0.30319",
  "binary_footprint": "Single executable PE32 (.NET assembly), typ. 30 KB - 120 KB uncompressed stub",
  "stub_size": "45,056 bytes (vanilla stub), expanding to 200 KB - 1.5 MB when packed with loaders or obfuscators",
  "packer_obfuscation": "ConfuserEx, KoiVM, Beds-Protector, Donut shellcode stagers, or multi-stage PowerShell/BAT loaders",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "Client.Program.Main() -> Mutex verification -> Settings.InitializeSettings() -> AntiProcess/AntiVM checks -> Install persistence -> BeginConnect() asynchronous socket loop",
  "technical_summary": "AsyncRAT is an open-source, modular remote access trojan engineered in C#. It operates asynchronously over raw TCP sockets via the .NET System.Net.Sockets namespace, wrapping traffic in mutual TLS and serialized MessagePack payloads. Its execution model relies on dynamic in-memory plugin execution via AppDomain.CurrentDomain.Load without writing functional modules to disk."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "GUI Builder / Operator Console",
  "builder_tabs_options": [
    {
      "tab": "Connection",
      "options": [
        "Ports: Comma-separated TCP port listening array (default: 6606, 7707, 8808)",
        "DNS / IP: Dynamic DNS hostnames or static IP endpoints",
        "Pastebin: Optional raw Pastebin URL used for dynamic C2 address resolution"
      ]
    },
    {
      "tab": "Install",
      "options": [
        "Install Switch: Boolean flag enabling persistent dropped binary placement",
        "File Path: Drop directory selection (AppData, Temp, ProgramFiles)",
        "File Name: Masqueraded binary name (e.g., svchost.exe, runtime.exe)",
        "SubFolder: Directory name created under chosen root",
        "Hide File / Hide Folder: Applies FILE_ATTRIBUTE_HIDDEN and FILE_ATTRIBUTE_SYSTEM attributes"
      ]
    },
    {
      "tab": "Miscellaneous",
      "options": [
        "Mutex: Unique string for single-instance enforcement via System.Threading.Mutex",
        "Anti-Analysis: Toggles for Anti-VM, Anti-Process, and VirtualBox/VMware/Sandboxie detection",
        "BSOD Protection: RtlSetProcessIsCritical watchdog crashing Windows upon process termination",
        "Keylogger: Background WH_KEYBOARD_LL hook logging to %AppData%\\Logs",
        "Delay Execution: Initial sleep timer in seconds prior to first C2 connection"
      ]
    },
    {
      "tab": "Assembly",
      "options": [
        "Clone Assembly Information: Clones Title, Description, Company, Product, Copyright, and Version from clean binaries (e.g., explorer.exe, chrome.exe)",
        "Icon Changer: Extracts and embeds multi-resolution .ico resources into PE header"
      ]
    },
    {
      "tab": "Build",
      "options": [
        "Output Type: Standard .exe or in-memory .dll",
        "Certificate Generation: Generates self-signed X.509 certificate (CN=AsyncRAT Server) or imports external .cer/.p12",
        "AES Secret Key derivation using PBKDF2 (Rfc2898DeriveBytes)"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "Settings.Ports",
      "field": "Ports",
      "type": "String",
      "description": "Encrypted comma-separated listener ports"
    },
    {
      "offset": "Settings.Hosts",
      "field": "Hosts",
      "type": "String",
      "description": "Encrypted C2 hostname/IP array"
    },
    {
      "offset": "Settings.Version",
      "field": "Version",
      "type": "String",
      "description": "Client version string (e.g., 0.5.7B)"
    },
    {
      "offset": "Settings.Install",
      "field": "Install",
      "type": "String",
      "description": "Boolean 'true'/'false' for persistence deployment"
    },
    {
      "offset": "Settings.InstallFolder",
      "field": "InstallFolder",
      "type": "String",
      "description": "Target directory identifier (%AppData% / %Temp%)"
    },
    {
      "offset": "Settings.InstallFile",
      "field": "InstallFile",
      "type": "String",
      "description": "Target dropped executable name"
    },
    {
      "offset": "Settings.Key",
      "field": "Key",
      "type": "String",
      "description": "AES-256 decryption passphrase string"
    },
    {
      "offset": "Settings.Bdos",
      "field": "Bdos",
      "type": "String",
      "description": "Boolean flag for RtlSetProcessIsCritical enablement"
    },
    {
      "offset": "Settings.Anti",
      "field": "Anti",
      "type": "String",
      "description": "Boolean flag for sandbox/debugger/VM evasion checks"
    },
    {
      "offset": "Settings.Certificate",
      "field": "ServerCertificate",
      "type": "String",
      "description": "Base64-encoded raw X.509 certificate bytes"
    }
  ],
  "payload_generation_flags": [
    "Target Framework: v4.0",
    "Obfuscation Preset: Normal / Maximum",
    "Digital Signature Stripping: Enabled"
  ],
  "operator_commands": [
    "ClientInfo: Returns OS version, active user, privileges, AV product, CPU/GPU",
    "SendFile: Uploads and executes payload from disk or in-memory",
    "RemoteDesktop: Streams GDI/DXGI screen buffers with adjustable quality/FPS",
    "Keylogger: Retrieves offline keystroke logs or initiates live capture",
    "ReverseProxy: Establishes SOCKS5 proxy tunnel via client socket",
    "Shell: Spawns interactive cmd.exe or powershell.exe pipe",
    "ProcessManager: Enumerates, suspends, and terminates process tree",
    "Uninstall: Removes persistence hooks, drops self-delete batch script, and exits"
  ],
  "interface_telemetry_analysis": "The operator interface is a Windows Forms client featuring a real-time listview populated by active client connections. Each row details IP, country flag, machine name, active window title, client version, operating system, ping latency, and privilege integrity. Server context menus expose payload compilation dialogs, dynamic plugin push triggers, and interactive telemetry windows."
}struct AsyncRAT_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Process Hollowing: Target spawned via CreateProcessW with CREATE_SUSPENDED (0x00000004) -> NtUnmapViewOfSection to detach target code -> VirtualAllocEx allocating image base with PAGE_EXECUTE_READWRITE -> WriteProcessMemory writing PE headers and sections -> SetThreadContext updating EAX/RCX entry point -> ResumeThread restoring execution.",
  "ntapi_functions": [
    "ntdll!NtUnmapViewOfSection",
    "kernel32!VirtualAllocEx",
    "kernel32!WriteProcessMemory",
    "kernel32!GetThreadContext",
    "kernel32!SetThreadContext",
    "kernel32!ResumeThread",
    "ntdll!RtlSetProcessIsCritical"
  ],
  "process_hollowing_target": "RegSvcs.exe, RegAsm.exe, aspnet_compiler.exe, or svchost.exe",
  "persistence_mechanics": [
    "Scheduled Task: schtasks.exe /create /f /sc onlogon /rl highest /tn \"{InstallFile}\" /tr \"{InstallPath}\"",
    "Registry Run Key: HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run\\{InstallFile}",
    "Startup Folder: %AppData%\\Microsoft\\Windows\\Start Menu\\Programs\\Startup\\{InstallFile}.lnk"
  ],
  "evasion_hooks": [
    "AMSI Bypass via AmsiScanBuffer memory patching (writing 0xB8, 0x57, 0x00, 0x07, 0x80, 0xC2, 0x18, 0x00)",
    "ETW Patching via EtwEventWrite patch (RET 0x14)",
    "Process protection watchdog: RtlSetProcessIsCritical(1, NULL, 0) causing BugCheck 0xEF (CRITICAL_PROCESS_DIED) if killed"
  ],
  "anti_analysis": [
    "VMware/VirtualBox check via WMI: 'SELECT * FROM Win32_ComputerSystem' checking Manufacturer and Model for 'VMware', 'VirtualBox', 'QEMU'",
    "Process Blacklist check: Process.GetProcesses() checking for taskmgr, processhacker, procexp, wireshark, fiddler, x64dbg, ollydbg",
    "Disk space check (< 40 GB) and RAM check (< 2 GB) to detect automated sandboxes"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the AsyncRAT binary:
[ "Chromium-based browser database collection (Login Data, Web Data, Cookies)", "DPAPI master key decryption via CryptUnprotectData", "Gecko-based browser collection via nss3.dll extraction", "Discord token extraction from Local Storage\\leveldb", "Telegram session (tdata) directory copying" ]
[ "Low-level keyboard hook (SetWindowsHookExW with WH_KEYBOARD_LL) capturing keystrokes and active window title changes", "Desktop streaming via System.Drawing.Graphics.CopyFromScreen with JPEG compression", "Audio capture via DirectShow / waveIn API streams", "Webcam surveillance via AForge.Video framework plugins" ]
[ "Interactive reverse CMD/PowerShell shell redirected over TLS stream", "SOCKS5 reverse proxy module facilitating internal network pivot", "File Manager with upload, download, execute, delete, and directory tree enumeration" ]
[ "Automated document grabber filtering by extension (.txt, .pdf, .doc, .docx, .kdbx)", "Drive scanner targeting removable USB storage devices" ]
[ "Clipboard monitoring hook inspecting clipboard text changes", "Bitcoin address regex substitution: ^[13][a-km-zA-HJ-NP-Z1-9]{25,34}$", "Ethereum address regex substitution: ^0x[a-fA-F0-9]{40}$", "Tron/USDT address regex substitution: ^T[A-Za-z1-9]{33}$" ]
[ "Windows Defender exclusion injection via powershell Add-MpPreference -ExclusionPath", "UAC elevation via fodhelper.exe or computerdefaults.exe registry hijacking", "System reboot, shutdown, and Blue Screen of Death trigger" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "4-byte Little-Endian unsigned integer prefix specifying the payload length in bytes, followed by the payload",
  "serialization": "MessagePack binary serialization format (MsgPack.dll) structured as a key-value dictionary",
  "handshake": "Client establishes TCP connection -> Initiates TLS 1.2 handshake -> Server validates client or presents X.509 cert (CN=AsyncRAT Server) -> Client verifies certificate thumbprint -> Mutual cryptographic channel established",
  "cryptography": "AES-256-CBC with PKCS7 padding. Key derived via PBKDF2 (Rfc2898DeriveBytes, HMAC-SHA256, 50,000 iterations) using hardcoded salt (32 bytes) from Settings.Password. IV (16 bytes) prepended to the ciphertext.",
  "packet_types": [
    {
      "header": "Packet: ClientInfo",
      "payload": "HWID, Username, OS, CPU, GPU, RAM, Antivirus, Version",
      "direction": "Client -> Server"
    },
    {
      "header": "Packet: Ping",
      "payload": "Empty heartbeat timestamp ping",
      "direction": "Client -> Server"
    },
    {
      "header": "Packet: Pong",
      "payload": "Heartbeat acknowledge",
      "direction": "Server -> Client"
    },
    {
      "header": "Packet: SendFile",
      "payload": "Binary buffer, file extension, execution flags",
      "direction": "Server -> Client"
    },
    {
      "header": "Packet: Shell",
      "payload": "Interactive terminal input/output buffer",
      "direction": "Bidirectional"
    }
  ],
  "traffic_signature": "TLS ClientHello containing custom extensions followed by encrypted TLS application records. In non-TLS custom builds, raw TCP streams display 4-byte LE length prefix followed by MessagePack byte markers (0x80-0x8F for map, 0xA0-0xBF for str)."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_AsyncRAT_Payload {
    meta:
        description = "Identifies unpacked AsyncRAT .NET payloads based on configuration classes, string artifacts, and crypto routines"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "AsyncRAT"
        hash = "7e63b39be8217bbba9d28e75cf0db87fb69e8b9f6974db368677c72f12255da1"
    strings:
        $s1 = "AsyncRAT" ascii wide
        $s2 = "Settings" ascii
        $s3 = "ServerCertificate" ascii
        $s4 = "ServerSignature" ascii
        $s5 = "BDOS" ascii
        $s6 = "RtlSetProcessIsCritical" ascii
        $s7 = "Pastebin" ascii wide
        $s8 = "InstallFolder" ascii
        $op1 = { 7E ?? ?? ?? 04 6F ?? ?? ?? 0A 74 }
        $msgpack = "MsgPack.Serialization" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 2MB and
        (5 of ($s*) or ($msgpack and 3 of ($s*)))
}title: AsyncRAT Execution and Process Protection Watchdog
id: 9a7b3c2d-1e4f-4a8b-9c0d-e2f3a4b5c6d7
status: stable
description: Detects scheduled task creation and process injection behaviors characteristic of AsyncRAT installations.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S0397/
tags:
- attack.execution
- attack.t1059.001
- attack.persistence
- attack.t1053.005
- attack.defense_evasion
- attack.t1055.001
logsource:
category: process_creation
product: windows
detection:
selection_schtasks:
Image|endswith: '\schtasks.exe'
CommandLine|contains|all:
- '/create'
- '/sc onlogon'
- '/rl highest'
selection_injection:
ParentImage|endswith:
- '\powershell.exe'
- '\cmd.exe'
- '\wscript.exe'
Image|endswith:
- '\RegSvcs.exe'
- '\RegAsm.exe'
- '\aspnet_compiler.exe'
condition: selection_schtasks or selection_injection
falsepositives:
- Administrative maintenance scripts configuring system logon triggers.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
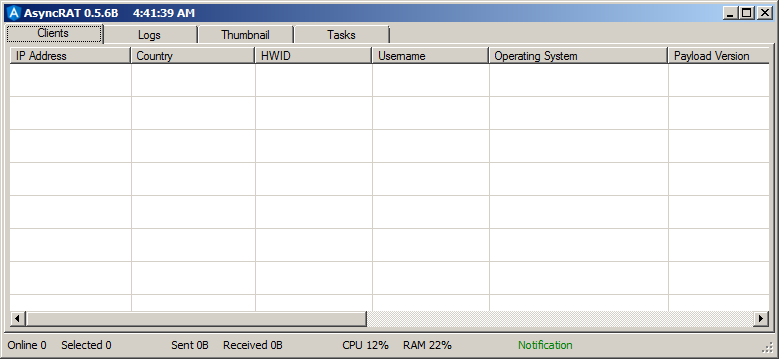
Operator configurator GUI showing TLS X.509 certificate generation, keylogger toggles, process injection, and persistence configuration.

Interactive desktop surveillance module capturing victim screen buffers and keystroke telemetry streams.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Dynamic DNS, Cloudflare Tunnels, TLS CN=AsyncRAT command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
AsyncRAT (RAT)
Modular C# remote access trojan communicating via TLS-wrapped asynchronous sockets and MessagePack serialization.
C2 Architecture: {'framing': '4-byte Little-Endian unsigned integer prefix specifying the payload length in bytes, followed by the payload', 'serialization': 'MessagePack binary serialization format (MsgPack.dll) structured as a key-value dictionary', 'handshake': 'C
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ AsyncRAT (RAT)
Детальный технический анализ AsyncRAT — это Троян удаленного доступа (RAT), разработанный на стеке Microsoft C# Compiler (csc.exe / Roslyn) targeting .NET Framework 4.0/4.5. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Asynchronous TCP Sockets wrapped in TLS 1.2/1.3 with AES-256-CBC packet encryption) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Asynchronous TCP Sockets wrapped in TLS 1.2/1.3 with AES-256-CBC packet encryption, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
AsyncRAT (RAT) विश्लेषण
AsyncRAT एक परिष्कृत रिमोट एक्सेस ट्रोजन (RAT) है जिसे Microsoft C# Compiler (csc.exe / Roslyn) targeting .NET Framework 4.0/4.5 का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Asynchronous TCP Sockets wrapped in TLS 1.2/1.3 with AES-256-CBC packet encryption) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Asynchronous TCP Sockets wrapped in TLS 1.2/1.3 with AES-256-CBC packet encryption आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).