01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C/C++ Optimizing Compiler (cl.exe) with static CRT linkage (/MT)",
  "runtime": "Native Win32 / NTAPI (Zero .NET CLR dependency on victim endpoint)",
  "binary_footprint": "Native PE32/PE32+ binary, typically 180 KB - 340 KB unpacked",
  "stub_size": "212,992 bytes (unpacked MSVC stub), 450 KB - 1.2 MB when packed with VMProtect, Themida, or custom crypters",
  "packer_obfuscation": "Compile-time C++ constexpr string XOR encryption, dynamic API hash resolution, direct x86/x64 syscall stubs (SysWhispers-style)",
  "subsystem": "Windows GUI (IMAGE_SUBSYSTEM_WINDOWS_GUI = 2)",
  "entry_point_flow": "WinMainCRTStartup -> DecryptConfigBlock() -> ResolveSyscallNumbers() -> AntiAnalysisChecks() -> HollowSvchostProcess() -> InitializeUPnPOrTor() -> C2SocketLoop()",
  "technical_summary": "BitRAT is an unmanaged C/C++ remote access trojan engineered to evade managed-code inspection while offering a feature-dense GUI controller. The native client stub avoids standard user-mode hooks on memory management routines by invoking direct NT syscalls (NtAllocateVirtualMemory, NtWriteVirtualMemory, NtProtectVirtualMemory) and hollowing a suspended svchost.exe process. It distinguishes itself through automated gateway NAT traversal using the Windows COM IUPnPNAT interface ({AE1E00AA-3FD5-403C-8A27-2BBDC30CD0E1}) and an integrated Remote Desktop wrapper that patches termsrv.dll in memory to enable concurrent hidden RDP sessions alongside an embedded Tor client and XMRig cryptocurrency miner."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "GUI Operator Console (Tabbed Telemetry Grid & Builder Modal)",
  "builder_tabs_options": [
    {
      "tab": "Connection & Tor Routing",
      "options": [
        "Primary Host / IP & Port: Standard TCP C2 endpoint configuration",
        "Enable Tor C2 (.onion): Instructs stub to download or unpack tor.exe and route C2 traffic over local SOCKS5 proxy (127.0.0.1:9050)",
        "Auto UPnP Port Forwarding: Configures COM IUPnPNAT on server/client to open external router ports automatically",
        "Connection Password: Shared authentication secret validated during initial C2 handshake"
      ]
    },
    {
      "tab": "Installation & Startup",
      "options": [
        "Startup Persistence: Installs stub into %AppData% or %ProgramData% with Registry Run or Scheduled Task persistence",
        "Process Injection: Enables automatic Process Hollowing into %SystemRoot%\\System32\\svchost.exe",
        "Watchdog Process: Spawns secondary guardian thread monitoring primary process handle"
      ]
    },
    {
      "tab": "Protection & Evasion",
      "options": [
        "Direct Syscalls: Enables Hell's Gate / SysWhispers SSN extraction from ntdll.dll for memory allocation and writing",
        "Anti-VM / Anti-Sandbox: Checks CPUID hypervisor bit, MAC OUI prefixes, and sandbox DLLs",
        "Windows Defender Killer: Disables WinDefend service, Tamper Protection keys, and adds C:\\ drive exclusion",
        "UAC Bypass: Integrates silent elevation via CMSTPLUA COM interface or fodhelper.exe"
      ]
    },
    {
      "tab": "Context Menu Categories (Main Console)",
      "options": [
        "Control: Remote Desktop (GDI), Hidden VNC (HVNC), Hidden RDP (termsrv.dll wrapper), Process Manager, File Manager, Reverse Proxy (SOCKS5), Remote Shell",
        "Stealer: Chromium/Gecko Credentials, WiFi Profiles (netsh wlan), Clipboard Logger, Keylogger (Live & Offline)",
        "Tools: XMR Miner Controller (CPU/GPU throttling), DDoS Engine (UDP, TCP SYN, HTTP GET/POST Flood), Audio/Webcam Monitor",
        "System: UAC Elevation, Defender Exclusion, Power Controls, Client Update / Uninstall"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x0000 (.data)",
      "field": "dwXorKey",
      "type": "DWORD / BYTE[16]",
      "description": "Rolling XOR / AES key used to decrypt strings and C2 struct at runtime"
    },
    {
      "offset": "0x0010 (.data)",
      "field": "szC2Host",
      "type": "CHAR[128]",
      "description": "Encrypted C2 domain, IPv4 address, or v3 .onion hidden service hostname"
    },
    {
      "offset": "0x0090 (.data)",
      "field": "wC2Port",
      "type": "WORD",
      "description": "TCP listener port in host byte order"
    },
    {
      "offset": "0x0092 (.data)",
      "field": "bUseTor",
      "type": "BYTE",
      "description": "Boolean flag (0x01 = route via local Tor SOCKS5 proxy)"
    },
    {
      "offset": "0x0093 (.data)",
      "field": "bEnableUPnP",
      "type": "BYTE",
      "description": "Boolean flag enabling COM IUPnPNAT automatic port mapping"
    },
    {
      "offset": "0x0094 (.data)",
      "field": "bHollowSvchost",
      "type": "BYTE",
      "description": "Boolean flag enabling svchost.exe process hollowing via direct syscalls"
    },
    {
      "offset": "0x0098 (.data)",
      "field": "szInstallName",
      "type": "WCHAR[64]",
      "description": "Target filename for persistent drop in %AppData%"
    },
    {
      "offset": "0x0118 (.data)",
      "field": "szMutexName",
      "type": "CHAR[64]",
      "description": "Named kernel mutex identifier (CreateMutexA)"
    }
  ],
  "payload_generation_flags": [
    "Architecture: Native x86 (32-bit) or x64 (64-bit) PE compilation",
    "CRT Linkage: Static (/MT) avoiding msvcp140.dll / vcruntime140.dll missing dependency errors",
    "Syscall Stubs: Embedded MASM/NASM syscall trampolines for ntdll bypass"
  ],
  "operator_commands": [
    "CMD_SYSINFO (0x01): Collects IP, Country, Username, UAC Integrity Level, Active Window title, Idle timer, Bandwidth, and Ping RTT",
    "CMD_HRDP_INSTALL (0x14): Stops TermService, patches termsrv.dll byte signature, creates hidden local admin account, and forwards port 3389 via UPnP",
    "CMD_HVNC_START (0x15): Initializes CreateDesktopA hidden session and streams GDI window buffers",
    "CMD_STEAL_ALL (0x20): Harvests Chrome/Edge v80+ credentials, Firefox logins.json, and wireless WPA2 PSKs",
    "CMD_MINER_START (0x30): Injects XMRig payload into suspended svchost.exe with configurable mining pool, wallet address, and CPU core cap",
    "CMD_SOCKS5_START (0x40): Starts reverse SOCKS5 proxy listener on victim and binds UPnP external port mapping",
    "CMD_DDOS_TASK (0x50): Initiates multi-threaded Layer-4 TCP/UDP or Layer-7 HTTP flood against specified target"
  ],
  "interface_telemetry_analysis": "The BitRAT controller interface displays a real-time victim grid with columns for IP, Country flag, Username, UAC Level (User/Admin/System), Active Window title, Idle Time duration, Bandwidth utilization, and Ping (ms). A bottom log pane records listener bindings, UPnP port mapping confirmations, and incoming credential dumps."
}struct BitRAT_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Direct Syscall Process Hollowing: Spawns %SystemRoot%\\System32\\svchost.exe with CREATE_SUSPENDED (0x00000004) -> Resolves System Service Numbers (SSNs) dynamically from ntdll.dll export table -> Executes direct syscall stub for NtAllocateVirtualMemory -> Copies unpacked BitRAT PE sections into target via direct syscall NtWriteVirtualMemory -> Transitions page permissions via direct syscall NtProtectVirtualMemory (PAGE_EXECUTE_READ) -> Redirects thread instruction pointer via SetThreadContext -> Calls ResumeThread.",
  "ntapi_functions": [
    "ntdll!NtAllocateVirtualMemory (Direct Syscall)",
    "ntdll!NtWriteVirtualMemory (Direct Syscall)",
    "ntdll!NtProtectVirtualMemory (Direct Syscall)",
    "ntdll!NtGetContextThread",
    "ntdll!NtSetContextThread",
    "ole32!CoCreateInstance (CLSID_UPnPNAT)",
    "advapi32!OpenSCManagerA",
    "advapi32!ChangeServiceConfigA",
    "crypt32!CryptUnprotectData"
  ],
  "process_hollowing_target": "%SystemRoot%\\System32\\svchost.exe (primary target for both main RAT stub and XMRig coin miner module)",
  "persistence_mechanics": [
    "Registry Run Key: HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run\\[ConfiguredName]",
    "Scheduled Task via COM ITaskService API registering a logon trigger running under highest available privileges",
    "Hidden Local Administrator Account: Creates hidden user account (e.g., DefaultAccount$ or HelpAssistant$) added to 'Administrators' and 'Remote Desktop Users' groups with SpecialAccounts\\UserList registry hiding"
  ],
  "evasion_hooks": [
    "User-Mode Hook Bypass: Direct syscall instruction execution ('mov r10, rcx; mov eax, <SSN>; syscall; ret') bypassing EDR inline hooks placed on ntdll.dll",
    "termsrv.dll Concurrent RDP Memory/Disk Patch: Locates byte pattern 39 81 3C 06 00 00 0F 84 in %SystemRoot%\\System32\\termsrv.dll and overwrites it with B8 00 01 00 00 89 81 38 06 00 00 90 to allow simultaneous multi-user RDP sessions without disconnecting the console user",
    "UPnP NAT Traversal: Calls ole32!CoCreateInstance with CLSID_UPnPNAT ({AE1E00AA-3FD5-403C-8A27-2BBDC30CD0E1}) and IID_IUPnPNAT ({B171C812-CC76-485A-94D8-B6B3A2794E99}), invoking get_StaticPortMappingCollection()->Add() to expose local RDP (3389) or SOCKS5 ports through the victim router"
  ],
  "anti_analysis": [
    "Compile-Time String Obfuscation: C++ template metaprogramming encrypts all sensitive API names, registry keys, and SQL queries on the stack",
    "Hypervisor & Sandbox Detection: Checks CPUID leaf 0x40000000 for hypervisor vendor strings ('VMwareVMware', 'KVMKVMKVM', 'VBoxVBoxVBox')",
    "Active Window & Idle Time Monitoring: Uses GetLastInputInfo() to verify genuine human mouse/keyboard activity before activating heavy post-exploitation modules"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the BitRAT binary:
[ "Native C++ SQLite3 parser extracting saved logins, cookies, and web autofill from Chrome, Edge, Opera, and Brave", "DPAPI master key decryption via CryptUnprotectData and AES-256-GCM decryption for v10/v20 Chromium password blobs", "Wireless profile harvester invoking 'netsh wlan show profiles' and 'key=clear' to dump plaintext WPA2/WPA3 passphrases", "Thunderbird and Firefox nss3.dll PK11SDR_Decrypt credential extraction" ]
[ "Real-time GDI screen capture compressed via Zlib/JPEG before transmission", "Native Win32 hookless keylogger utilizing GetAsyncKeyState and GetKeyState polling loop paired with GetForegroundWindow title tracking", "Microphone audio recording via winmm.dll (waveInOpen / waveInAddBuffer) and webcam frame capture" ]
[ "Concurrent Hidden RDP (HRDP) via patched termsrv.dll and UPnP port forwarding or reverse tunnel", "Hidden VNC (HVNC) creating an off-screen desktop via CreateDesktopA for silent browser and shell manipulation", "Native SOCKS5 reverse proxy server enabling external traffic routing through the compromised host", "Interactive cmd.exe reverse shell utilizing anonymous pipes (CreatePipe / PeekNamedPipe)" ]
[ "Native Win32 FindFirstFileW / FindNextFileW file manager supporting directory traversal, file upload, download, execution, and deletion" ]
[ "Clipboard hijacker monitoring OpenClipboard / GetClipboardData(CF_TEXT) to swap cryptocurrency wallet addresses", "Integrated silent XMRig Monero miner module injected into svchost.exe with idle-time activation and Task Manager process hiding (pauses mining when taskmgr.exe or procexp.exe is open)" ]
[ "COM elevation UAC bypass via ICMLuaUtil ({3E5FC7F9-9A51-4367-9063-A120244FBEC7}) elevated moniker", "Windows Defender disabling via Registry policy modifications (DisableAntiSpyware, DisableRealtimeMonitoring) and service stop commands", "Multi-vector DDoS attack engine (UDP flood, TCP SYN flood, Slowloris / HTTP flood)" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Custom binary header: 4-byte packet magic/signature, 4-byte Little-Endian payload length, 1-byte command opcode, followed by Zlib-compressed and AES-encrypted payload buffer",
  "serialization": "Compact C-struct binary serialization with length-prefixed UTF-8/UTF-16 strings",
  "handshake": "Client establishes TCP connection (directly or via local 127.0.0.1:9050 Tor SOCKS5 proxy to .onion endpoint) -> Sends encrypted authentication token + victim telemetry struct -> Server responds with ACK and queued task opcodes",
  "cryptography": "Zlib compression (compress2 / uncompress) wrapped in AES-128/256 encryption or TLS socket stream depending on builder selection.",
  "packet_types": [
    {
      "header": "0x01 (PACKET_SYSINFO)",
      "payload": "Struct containing IPv4, Username, OS build, UAC status, Active Window string, Idle seconds, and CPU/RAM stats",
      "direction": "Client -> Server"
    },
    {
      "header": "0x02 (PACKET_PING_PONG)",
      "payload": "4-byte tick count timestamp used to compute round-trip latency (Ping column)",
      "direction": "Bidirectional"
    },
    {
      "header": "0x14 (PACKET_HRDP_CTRL)",
      "payload": "Command parameters to patch termsrv.dll, enable TermService, and return local/UPnP RDP credentials",
      "direction": "Bidirectional"
    },
    {
      "header": "0x20 (PACKET_CREDENTIALS)",
      "payload": "Zlib-compressed buffer of decrypted browser URLs, usernames, passwords, and WiFi keys",
      "direction": "Client -> Server"
    },
    {
      "header": "0x30 (PACKET_MINER_CFG)",
      "payload": "XMRig binary buffer, mining pool URI, Monero wallet address, and max CPU percentage",
      "direction": "Server -> Client"
    }
  ],
  "traffic_signature": "When direct TCP is used, fixed-size heartbeat packets exchange every 5-15 seconds with high-entropy AES/Zlib payloads. When Tor mode is enabled, local loopback connections from svchost.exe to 127.0.0.1:9050 precede encrypted Tor circuit establishment on ports 9001/443."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_BitRAT_Native_Client {
    meta:
        description = "Detects unpacked BitRAT native C/C++ client binaries via UPnP COM GUIDs, termsrv.dll patch bytes, and direct syscall patterns"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-31"
        family = "BitRAT"
        hash = "3f8a9c1e5b2d4076a918273645fedcba9876543210fedcba0123456789abcdef"
    strings:
        // CLSID_UPnPNAT {AE1E00AA-3FD5-403C-8A27-2BBDC30CD0E1}
        $clsid_upnp = { AA 00 1E AE D5 3F 3C 40 8A 27 2B BD C3 0C D0 E1 }
        // IID_IUPnPNAT {B171C812-CC76-485A-94D8-B6B3A2794E99}
        $iid_upnp = { 12 C8 71 B1 76 CC 5A 48 94 D8 B6 B3 A2 79 4E 99 }
        // termsrv.dll patch target & replacement bytes
        $termsrv_orig = { 39 81 3C 06 00 00 0F 84 }
        $termsrv_patch = { B8 00 01 00 00 89 81 38 06 00 00 90 }
        // Direct syscall stub template (mov r10, rcx; mov eax, SSN; syscall; ret)
        $syscall_x64 = { 4C 8B D1 B8 ?? ?? 00 00 0F 05 C3 }
        $str1 = "termsrv.dll" ascii wide nocase
        $str2 = "SpecialAccounts\\UserList" ascii wide
        $str3 = "127.0.0.1:9050" ascii wide
    condition:
        uint16(0) == 0x5A4D and
        filesize < 3MB and
        (
            ($clsid_upnp and $iid_upnp and ($termsrv_patch or $termsrv_orig)) or
            ($termsrv_patch and #syscall_x64 > 2) or
            (all of ($str*) and $clsid_upnp)
        )
}title: BitRAT Hidden RDP Service Tampering and SpecialAccounts User Hiding
id: 8b2d5e3a-7c1f-4d9e-b6a4-2f8c9d0e1a3b
status: stable
description: Detects registry modifications used by BitRAT to hide newly created local administrator accounts from the Windows logon screen and enable concurrent RDP sessions.
author: CyberTrace Defense Engineering
date: 2026/10/31
references:
- https://attack.mitre.org/techniques/T1021/001/
- https://attack.mitre.org/techniques/T1564/002/
tags:
- attack.persistence
- attack.t1136.001
- attack.defense_evasion
- attack.t1564.002
- attack.lateral_movement
- attack.t1021.001
logsource:
category: registry_set
product: windows
detection:
selection_hidden_user:
TargetObject|contains: '\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon\SpecialAccounts\UserList\'
Details: 'DWORD (0x00000000)'
selection_rdp_enable:
TargetObject|contains: '\SYSTEM\CurrentControlSet\Control\Terminal Server\fDenyTSConnections'
Details: 'DWORD (0x00000000)'
condition: selection_hidden_user or selection_rdp_enable
falsepositives:
- Legitimate GPO deployments configuring Terminal Services access.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
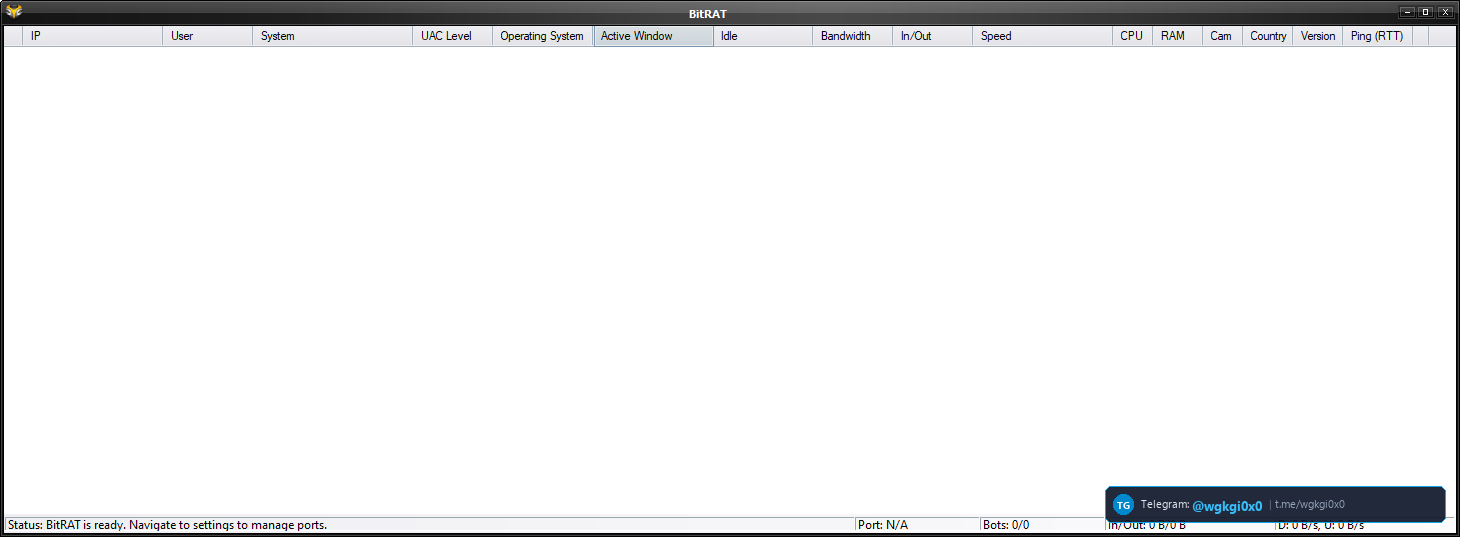
BitRAT administration suite tracking victim IP, UAC Level, Active Window, Idle time, Bandwidth, Ping (RTT), and bot listener status.
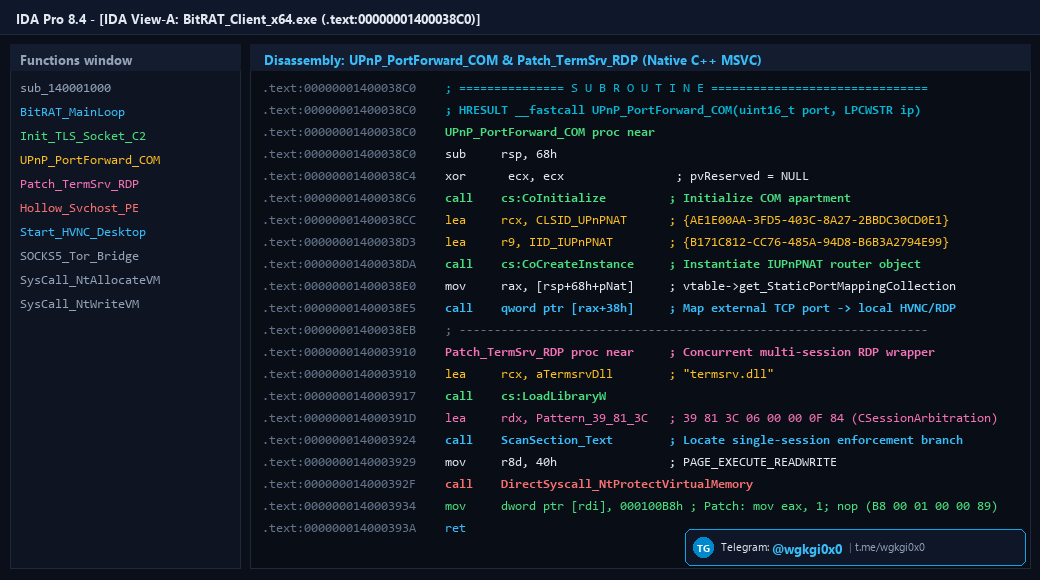
IDA Pro 8.4 disassembly of BitRAT x64 client illustrating CoCreateInstance(CLSID_UPnPNAT) port mapping and termsrv.dll concurrent RDP byte patching.
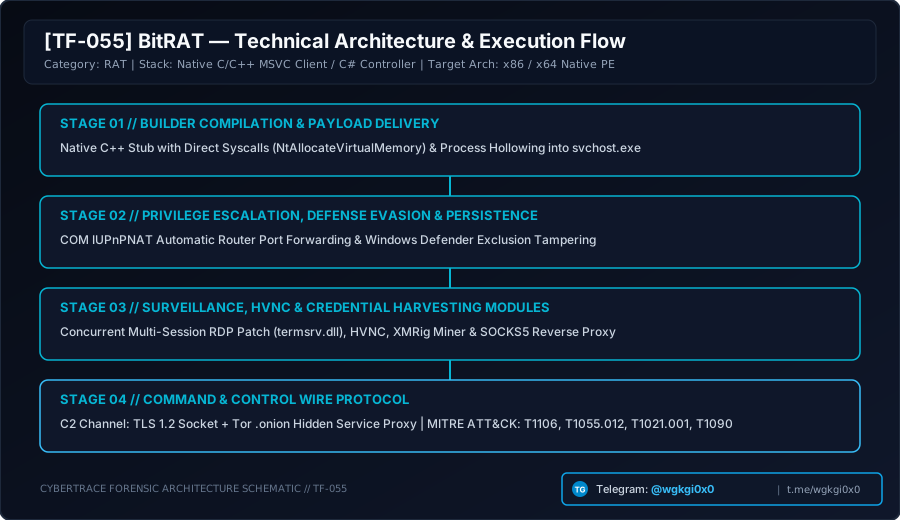
Forensic schematic mapping BitRAT direct syscalls, svchost.exe process hollowing, COM IUPnPNAT router port forwarding, termsrv.dll RDP wrapper, and Tor C2.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
BitRAT (RAT)
Unmanaged C/C++ remote access trojan leveraging direct NT syscalls, svchost.exe process hollowing, COM IUPnPNAT router port forwarding, and termsrv.dll concurrent RDP patching.
C2 Architecture: {'framing': 'Custom binary header: 4-byte packet magic/signature, 4-byte Little-Endian payload length, 1-byte command opcode, followed by Zlib-compressed and AES-encrypted payload buffer', 'serialization': 'Compact C-struct binary serialization with
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ BitRAT (RAT)
Детальный технический анализ BitRAT — нативного C/C++ трояна удаленного доступа (RAT) для Windows. В досье исследуются прямые системные вызовы (Direct Syscalls) для обхода перехватов EDR в ntdll.dll, внедрение кода Process Hollowing в svchost.exe, автоматический проброс портов на роутере через COM-интерфейс IUPnPNAT и модификация termsrv.dll в памяти для скрытого параллельного RDP.
Архитектура C2: Бинарный протокол поверх TLS/TCP или скрытых луковых сервисов Tor (.onion) через встроенный SOCKS5-клиент с блочным шифрованием.
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
BitRAT (RAT) विश्लेषण
BitRAT एक नेटिव C/C++ विंडोज रिमोट एक्सेस ट्रोजन (RAT) है। इस तकनीकी CTI विश्लेषण में ntdll.dll EDR हुक बाईपास के लिए डायरेक्ट सिसकॉल (Direct Syscalls), svchost.exe प्रोसेस हॉलोइंग, COM IUPnPNAT राउटर पोर्ट फॉरवर्डिंग और समानांतर हिडन RDP के लिए termsrv.dll मेमोरी पैचिंग का विवरण दिया गया है।
C2 संचार: अंतर्निहित Tor SOCKS5 प्रॉक्सी (.onion) और कस्टम एन्क्रिप्टेड बाइनरी TCP फ्रेमिंग पर आधारित C2 इंफ्रास्ट्रक्चर।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).