01 | Tool Specifications & Architectural Profile
BlackCat (ALPHV) is an advanced cross-platform ransomware framework developed in Rust. The platform targets both Windows and Linux/VMware ESXi hypervisors. Binaries utilize the Tokio multi-threaded asynchronous runtime, Clap CLI parser, Serde JSON configuration deserializer, and hardware-accelerated AES-NI / ChaCha20 cryptographic engines. The binary enforces an execution gating mechanism via the mandatory --access-token argument.
02 | Operator Interface & Configuration Struct Model
{
  "--access-token": "Mandatory 32-byte hexadecimal authorization token; execution aborts immediately without valid token string.",
  "--drag-and-drop": "Enables interactive file/folder drop handler for selective targeted encryption.",
  "--bypass-uac": "Executes programmatic auto-elevation routine via ICMLuaUtil COM interfaces.",
  "--safe-mode": "Configures BCD bootloader with safeboot network and registers persistence service for execution in Safe Mode.",
  "--no-wall": "Suppresses desktop wallpaper replacement routine.",
  "--no-prop-servers": "Suppresses scanning and lateral propagation against domain controllers and network servers.",
  "--no-prop-shares": "Disables enumeration and traversal of network SMB and NFS shares.",
  "--no-net-enum": "Disables local network ARP cache inspection and subnet ping sweeps.",
  "--extra-logging": "Enables detailed debug logging to stdout and designated log files.",
  "-p, --paths": "Specifies an array of explicit filesystem paths targeted for cryptographic operations."
}{
"description": "Embedded JSON document compressed and encrypted in binary, decrypted in memory using the supplied --access-token",
"fields": [
"public_key: 32-byte Base64-encoded public key (Curve25519 or RSA-4096)",
"extension: Custom 7-character file extension assigned to affiliate campaign",
"note_file_name: Name of dropped ransom note (e.g., RECOVER-[extension]-NOTES.txt)",
"note_full_text: Base64-encoded ransom note template including affiliate negotiation Tor URL",
"services: Array of service names targeted for termination (e.g., vss, sql, veeam, exchange, backup)",
"processes: Array of process names targeted for termination (e.g., sqlservr.exe, vmware.exe, postgres.exe)",
"white_list_strings: Array of directories and files excluded from encryption ($Recycle.Bin, Windows, boot)",
"encryption_mode: Configured encryption mode (Full, HeadOnly, Dot, Smart)",
"network_discovery: Boolean toggle governing ARP sweep and SMB share discovery"
]
}03 | Internal Binary & Memory Execution Mechanics
{
  "initialization": "Rust runtime initializes Tokio multi-threaded scheduler. Parses CLI switches via Clap. Decrypts internal JSON configuration using the mandatory --access-token.",
  "privilegeEscalation": "Evaluates token integrity level. If non-elevated and --bypass-uac is set, launches elevated COM task via ICMLuaUtil. Enables SeDebugPrivilege and SeBackupPrivilege.",
  "discoveryAndEnumeration": "Enumerates local logical drives, volume GUIDs, and network shares via WNetOpenEnumW unless --no-prop-shares is active. Scans ARP table via GetIpNetTable.",
  "serviceTermination": "Iterates through config.services array, calling OpenServiceW and ControlService(SERVICE_CONTROL_STOP). Iterates through config.processes, terminating matching PIDs via TerminateProcess.",
  "shadowCopyDestruction": "Windows: Executes vssadmin.exe delete shadows /all /quiet, wmic.exe shadowcopy delete, and bcdedit.exe /set {default} recoveryenabled No. ESXi: Invokes esxcli to force-kill VM worlds.",
  "cryptographicProcessing": "Tokio runtime spawns async worker tasks per logical core. Evaluates encryption_mode: Full, HeadOnly, Dot (stride skips), or Smart. Encrypts with ChaCha20 or AES-256-GCM, appends encrypted session key block, and renames file.",
  "ransomNotification": "Drops RECOVER-*-NOTES.txt in traversed directories. Updates desktop background image unless --no-wall is specified."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the BlackCat / ALPHV binary:
Unified Rust codebase compiled to native Windows PE32+ and Linux/ESXi ELF-64 binaries
Tokio async multi-threaded runtime with work-stealing queue optimization for ultra-high I/O throughput
Support for Full, HeadOnly, Dot (intermittent stride), and Smart extension-dependent encryption
Mandatory --access-token prevents dynamic sandbox execution; log purging via wevtutil and bcdedit manipulation
Native execution of esxcli and vim-cmd commands to kill virtual machines and encrypt .vmdk storage containers
05 | Wire Protocol & C2 Communication Framing
Commands and telemetry operate over Tor V3 Onion endpoints mediated via an embedded SOCKS5 proxy layer. Victim negotiation is facilitated through decentralized onion portals where victims authenticate using credentials embedded in dropped ransom notes. Operator communication interfaces with private REST API endpoints on hidden services.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_BlackCat_ALPHV_RustCore {
    meta:
        description = "Detects BlackCat (ALPHV) Rust-based ransomware binary, CLI flags, and Tokio runtime artifacts"
        author = "CyberTrace Intelligence (@wgkgi0x0)"
        reference = "TF-022"
        date = "2026-10-29"
        hash = "bd8b6b21900d8d47b59e358b5fa2f644e542e8f176b6b7a54460f9ef829e0cc1"
    strings:
        // BlackCat CLI flags
        $flag_token = "--access-token" ascii
        $flag_drop  = "--drag-and-drop" ascii
        $flag_safe  = "--safe-mode" ascii
        $flag_uac   = "--bypass-uac" ascii
        // Rust Tokio runtime strings
        $rust_tokio = "tokio-runtime-worker" ascii
        $rust_src   = "/cargo/registry/src/" ascii
        // Cryptographic mode strings from JSON config schema
        $mode_full  = "HeadOnly" ascii
        $mode_dot   = "Dot" ascii
        // Windows shadow deletion artifact
        $cmd_vss    = "vssadmin.exe delete shadows /all /quiet" wide ascii
    condition:
        (uint16(0) == 0x5A4D or uint32(0) == 0x464C457F) and
        ($flag_token and 2 of ($flag_*)) and
        ($rust_tokio or $rust_src) and
        (1 of ($mode_*) or $cmd_vss)
}title: BlackCat ALPHV Ransomware Execution and CLI Switches
id: 9a32c418-5f2b-4d7a-8b19-43c22076d022
status: stable
description: Detects command-line execution parameters characteristic of BlackCat (ALPHV) ransomware.
author: CyberTrace Intelligence (@wgkgi0x0)
date: 2026-10-29
logsource:
category: process_creation
product: windows
detection:
selection_token:
CommandLine|contains:
- "--access-token"
- "--bypass-uac"
- "--safe-mode"
selection_esxi:
Image|endswith:
- "/esxcli"
CommandLine|contains|all:
- "vm"
- "process"
- "kill"
condition:
selection_token or selection_esxi
falsepositives:
- Highly unlikely in production environments
level: critical
tags:
- attack.impact
- attack.t1486
- attack.t1070
- attack.t1562.00107 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
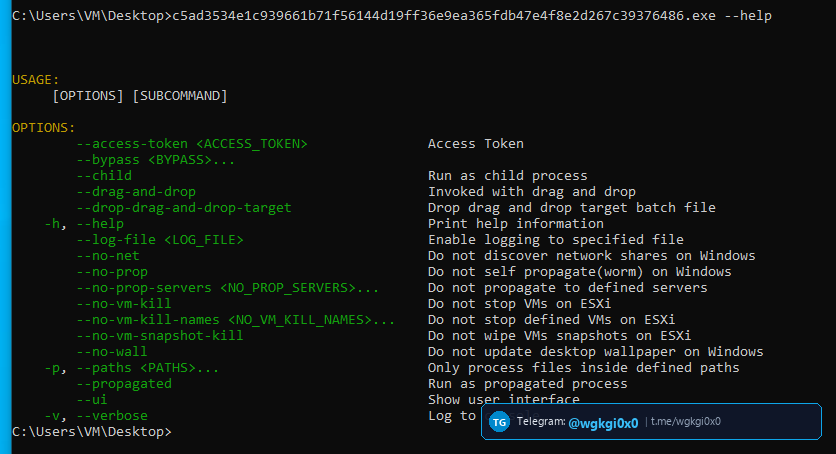
Forensic terminal capture displaying command-line switches for domain escalation, safemode reboot, and shadow wipe.
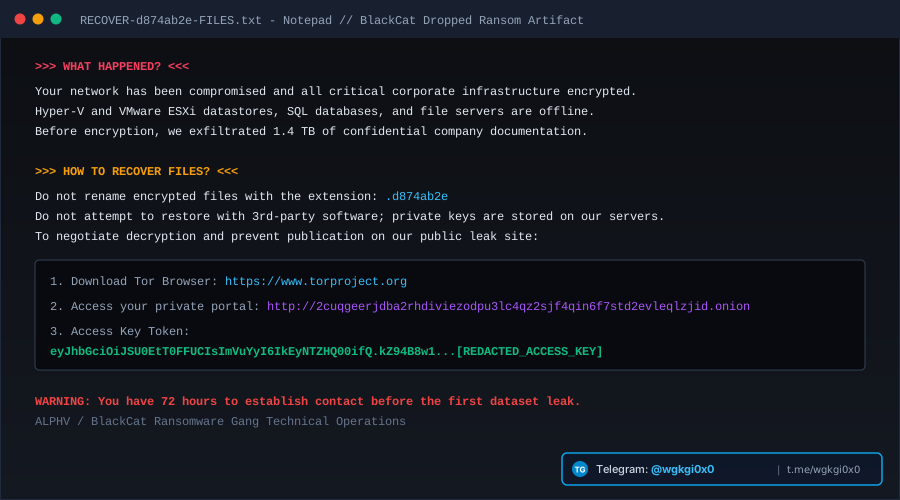
Generated ransom text note dropped on encrypted endpoints pointing to the ALPHV negotiation portal.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Tor Onion Nodes, REST API Command Channels command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
BlackCat / ALPHV (Ransomware)
Modular, cross-platform ransomware compiled in Rust with Tokio async concurrency, embedded JSON config parsing, and selectable ChaCha20-Poly1305 / AES-256-GCM encryption modes.
C2 Architecture: Commands and telemetry operate over Tor V3 Onion endpoints mediated via an embedded SOCKS5 proxy layer. Victim negotiation is facilitated through decentralized onion portals where victims authenticate using credentials embedded in dropped ransom note
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ BlackCat / ALPHV (Ransomware)
Детальный технический анализ BlackCat / ALPHV — это Программа-вымогатель (Шифровальщик), разработанный на стеке Rust compiler (rustc 1.6x+ / LLVM backend) with Cargo package manager. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Tor V3 Onion endpoints accessed through built-in SOCKS5 proxy layer and HTTPS REST endpoints) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Tor V3 Onion endpoints accessed through built-in SOCKS5 proxy layer and HTTPS REST endpoints, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
BlackCat / ALPHV (Ransomware) विश्लेषण
BlackCat / ALPHV एक परिष्कृत डेटा एन्क्रिप्ट करने वाला रैंसमवेयर है जिसे Rust compiler (rustc 1.6x+ / LLVM backend) with Cargo package manager का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Tor V3 Onion endpoints accessed through built-in SOCKS5 proxy layer and HTTPS REST endpoints) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Tor V3 Onion endpoints accessed through built-in SOCKS5 proxy layer and HTTPS REST endpoints आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).