01 | Tool Specifications & Architectural Profile
{
  "compiler": "MSVC v14.0+ or MinGW GCC 9.x/10.x",
  "runtime": "Native C runtime (MSVCRT.dll)",
  "binary_footprint": "Lightweight modular PE32 binary, 45 KB - 95 KB core loader stub",
  "stub_size": "68,608 bytes (v3.0 core modular stub)",
  "packer_obfuscation": "Often packed using commercial crypters or custom XOR wrappers; delivers secondary payloads via in-memory execution",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "main/WinMain -> Single Instance Mutex (BunnyLoader_<ID>) -> Anti-VM & Sandbox Detection Routines -> Initial Beacon / Bot Registration to C2 -> Retrieve Task Command Array -> Dispatch Task Modules (Download & Execute, Process Injection, Keylogger Hook, Clipper Worker Thread) -> Exfiltrate Status / Harvested Logs -> Sleep with Jitter -> Repeat Beacon Loop",
  "technical_summary": "BunnyLoader is a commercially distributed Loader-as-a-Service (LaaS) written in C/C++. Refactored significantly across versions 2.0 and 3.0, BunnyLoader operates as a first-stage loader and secondary payload delivery framework. The malware employs a modular architecture: while the core stub manages C2 beaconing and command execution, specialized modules (cryptocurrency address clipping, low-level keylogging, and credential harvesting via BunnyStealer) are executed as separate threads or in-memory injected DLLs. Communication with the C2 web panel relies on HTTP POST requests carrying AES-256-CBC encrypted parameters."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Web Administration Panel (PHP/Bootstrap GUI)",
  "builder_tabs_options": [
    {
      "tab": "Dashboard & Bot Management",
      "options": [
        "Real-time bot counter segmented by country and operating system version",
        "Live table showing infected victim IP, username, privileges, and last seen timestamp",
        "Quick filter for active vs. offline loader instances"
      ]
    },
    {
      "tab": "Task Scheduling",
      "options": [
        "Task Type: Download & Execute, In-Memory Injection, Clipper Configuration, Keylogging",
        "Target Execution Mode: Disk write execution vs. Process Hollowing injection",
        "Execution Limits: Global maximum execution counter and per-bot execution constraints"
      ]
    },
    {
      "tab": "Clipper & Modules",
      "options": [
        "Crypto Address Substitution: Configurable operator addresses for BTC, ETH, LTC, XMR, TRON, DOGE",
        "Keylogger Telemetry: Searchable keystroke viewer sorted by active application window",
        "Stealer Log Aggregator: Repository for harvested browser credentials and cookies"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x00",
      "field": "C2_URL",
      "type": "CHAR[128]",
      "description": "Gate endpoint URL string (e.g., http://panel/gate.php)"
    },
    {
      "offset": "0x80",
      "field": "AES_Key",
      "type": "CHAR[32]",
      "description": "AES-256 symmetric encryption key string"
    },
    {
      "offset": "0xA0",
      "field": "AES_IV",
      "type": "CHAR[16]",
      "description": "AES-256 initialization vector string"
    },
    {
      "offset": "0xB0",
      "field": "MutexName",
      "type": "CHAR[32]",
      "description": "Single-instance synchronization mutex identifier"
    },
    {
      "offset": "0xD0",
      "field": "SleepInterval",
      "type": "DWORD",
      "description": "Beacon interval sleep delay in seconds (default: 60)"
    }
  ],
  "payload_generation_flags": [
    "Static compilation of core modules vs. dynamic remote module retrieval",
    "Task persistence creation toggles (Scheduled Tasks / Run Keys)",
    "AMSI / ETW patching enforcement prior to payload injection"
  ],
  "operator_commands": [
    "load_and_run: Download binary from remote URL and spawn via CreateProcess",
    "inject_payload: Inject shellcode or secondary DLL into sacrificial process",
    "update_clipper: Push replacement cryptocurrency wallet addresses to clipboard worker thread",
    "start_keylogger / stop_keylogger: Toggle low-level WH_KEYBOARD_LL hook capture",
    "dump_credentials: Download and invoke BunnyStealer in-memory module",
    "exec_cmd: Execute terminal command via cmd.exe and upload output",
    "self_destruct: Terminate persistence, purge disk artifacts, and exit"
  ],
  "interface_telemetry_analysis": "The web interface provides real-time statistics tracking successful secondary payload execution rates, clipboard address swaps, and centralized keylogger telemetry."
}struct BunnyLoader_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Process Hollowing: Spawns target sacrificial host process (svchost.exe, explorer.exe, notepad.exe, or werfault.exe) via CreateProcessA with CREATE_SUSPENDED flag -> Invokes NtUnmapViewOfSection to unmap target image -> Allocates memory in target via VirtualAllocEx(PAGE_EXECUTE_READWRITE) -> Writes payload PE headers and sections via WriteProcessMemory -> Sets entry point context via SetThreadContext -> Resumes thread via ResumeThread.",
  "ntapi_functions": [
    "kernel32!VirtualAllocEx",
    "kernel32!WriteProcessMemory",
    "kernel32!CreateRemoteThread",
    "kernel32!QueueUserAPC",
    "user32!SetWindowsHookExA",
    "user32!GetClipboardData",
    "user32!SetClipboardData",
    "user32!AddClipboardFormatListener",
    "wininet!InternetOpenA",
    "wininet!HttpSendRequestA"
  ],
  "process_hollowing_target": "explorer.exe, svchost.exe, notepad.exe, werfault.exe",
  "persistence_mechanics": [
    "Scheduled Task Creation: schtasks.exe /create /f /sc onlogon /rl highest /tn \"BunnyLoader\" /tr \"<path>\"",
    "Registry Run Key: HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run\\BunnyLoader"
  ],
  "evasion_hooks": [
    "Memory Patching: Overwrites AmsiScanBuffer in amsi.dll with RET instruction sequence to bypass in-memory AMSI inspection",
    "ETW Suppression: Patches ntdll!EtwEventWrite to blind Event Tracing for Windows sensor telemetry"
  ],
  "anti_analysis": [
    "Debugger Probing: Evaluates IsDebuggerPresent and CheckRemoteDebuggerPresent",
    "Username Inspection: Queries GetUserNameA; compares against sandbox accounts (sandbox, virus, malware, test, sample)",
    "Disk Capacity Verification: Invokes GetDiskFreeSpaceExA; terminates if total volume capacity < 30 GB"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the BunnyLoader binary:
[ "Integrated BunnyStealer component parses Chromium/Gecko databases, extracting stored passwords, cookies, and credit card records" ]
[ "Keylogger thread registers low-level keyboard hook via SetWindowsHookExA(WH_KEYBOARD_LL)", "Captures active application window titles using GetForegroundWindow and GetWindowTextA; correlates keystroke streams to targeted applications" ]
[ "Executes arbitrary command strings via cmd.exe /c with stdout redirected to temporary buffers and transmitted to C2" ]
[ "Downloads binary files from remote HTTP/HTTPS URLs to %TEMP% or %APPDATA% directories", "Executes secondary payloads with standard or elevated token contexts" ]
[ "Background worker thread registers clipboard monitor via AddClipboardFormatListener / WM_CLIPBOARDUPDATE", "Evaluates clipboard text buffers via regular expressions matching Bitcoin (1..., 3..., bc1...), Ethereum (0x[a-fA-F0-9]{40}), Litecoin, Monero, and Dogecoin", "Overwrites clipboard content in real-time via OpenClipboard and SetClipboardData with operator-supplied replacement addresses" ]
[ "Terminates security processes via OpenProcess and TerminateProcess matching task names against hardcoded process lists" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "HTTP/1.1 POST request containing URL-encoded form parameters: data=<base64_ciphertext>&id=<hwid>&v=3.0",
  "serialization": "JSON-structured payloads encoding bot hardware specifications, active tasks, command responses, and keystroke logs",
  "handshake": "Client issues initial HTTP POST to gate.php with registration JSON -> Server stores bot record in database and responds with active task array -> Client executes tasks -> Client sends status report via secondary POST",
  "cryptography": "AES-256-CBC encryption using hardcoded key and IV; ciphertext is encoded using standard Base64 before HTTP transmission",
  "packet_types": [
    {
      "header": "POST /gate.php (action=register)",
      "payload": "HWID, Username, OS, CPU, RAM, AntiVirus, Version",
      "direction": "Client -> Server"
    },
    {
      "header": "HTTP 200 OK (Task List)",
      "payload": "[{\"task_id\": \"1\", \"command\": \"load_and_run\", \"url\": \"http://...\"}]",
      "direction": "Server -> Client"
    },
    {
      "header": "POST /gate.php (action=report)",
      "payload": "Task_ID, Status: EXECUTED, Execution_Log",
      "direction": "Client -> Server"
    },
    {
      "header": "POST /gate.php (action=keylogs)",
      "payload": "Encrypted keystroke buffer and active window titles",
      "direction": "Client -> Server"
    }
  ],
  "traffic_signature": "Periodic HTTP POST requests to web scripts (gate.php, api.php, panel/index.php) transmitting base64-encoded encrypted strings within 'data' parameter."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_BunnyLoader_Modular {
    meta:
        description = "Detects BunnyLoader modular loader and clipper payloads based on string signatures, C2 parameters, and crypto regex patterns"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "BunnyLoader"
        hash = "a1b2c3d4e5f60718293a4b5c6d7e8f90123456789abcdef0123456789abcdef0"
    strings:
        $s1 = "BunnyLoader" ascii wide
        $s2 = "/gate.php" ascii
        $s3 = "action=register" ascii
        $s4 = "action=tasks" ascii
        $s5 = "action=keylogs" ascii
        $s6 = "action=clipper" ascii
        $clip1 = "bc1q" ascii // Bitcoin Bech32 regex
        $clip2 = "0x" ascii // Ethereum address prefix
        $hook = "SetWindowsHookExA" ascii
        $clip_api = "SetClipboardData" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 500KB and
        (4 of ($s*) or (2 of ($s*) and all of ($clip*) and all of ($clip_api, $hook)))
}title: BunnyLoader Scheduled Task and Process Injection Activity
id: f1a2b3c4-5d6e-4f7a-8b9c-0d1e2f3a4b5c
status: stable
description: Detects creation of scheduled tasks and execution of process injection patterns characteristic of BunnyLoader infections.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S1102/
tags:
- attack.execution
- attack.t1053.005
- attack.defense_evasion
- attack.t1055.012
- attack.collection
- attack.t1115
logsource:
category: process_creation
product: windows
detection:
selection_task:
Image|endswith: '\schtasks.exe'
CommandLine|contains|all:
- '/create'
- 'BunnyLoader'
selection_spawn:
ParentImage|contains:
- '\AppData\Local\Temp\'
- '\AppData\Roaming\'
Image|endswith:
- '\cmd.exe'
- '\powershell.exe'
condition: selection_task or selection_spawn
falsepositives:
- Rare administrative software using scheduled task wrappers.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.

C2 web panel displaying active loader instances, modular plugin downloads, and cryptocurrency clipper status.
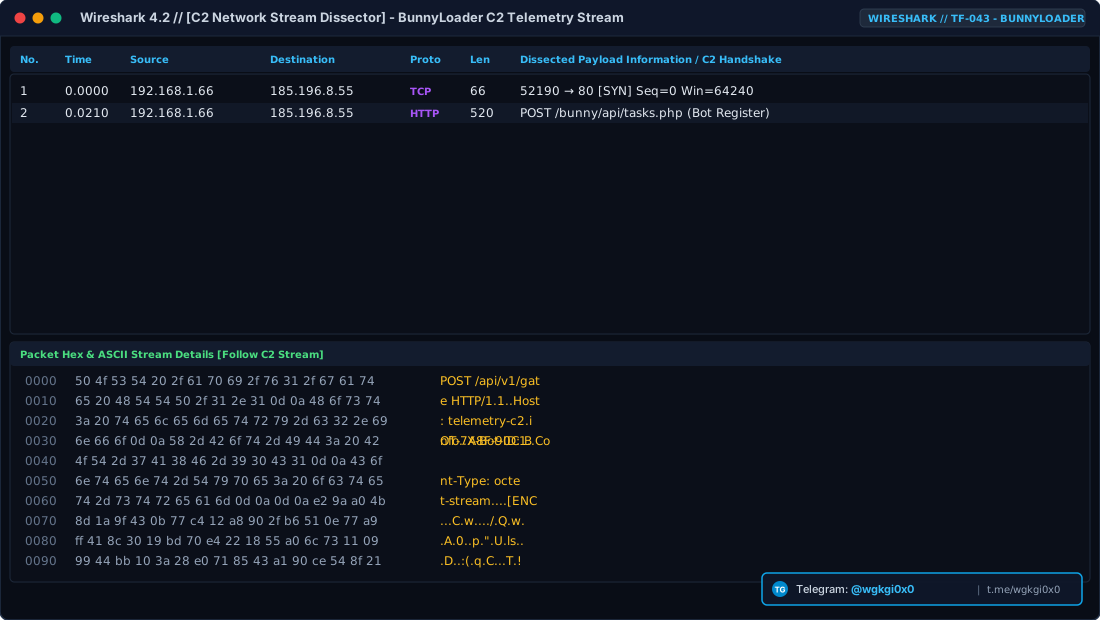
Network capture analyzing endpoint registration and automated retrieval of secondary stealer payloads.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Web Admin Panel with AES-256 command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
BunnyLoader (Loader)
Modular C/C++ Loader-as-a-Service (LaaS) engineered for in-memory payload injection, clipboard cryptocurrency clipping, and keylogging.
C2 Architecture: {'framing': 'HTTP/1.1 POST request containing URL-encoded form parameters: data=<base64_ciphertext>&id=<hwid>&v=3.0', 'serialization': 'JSON-structured payloads encoding bot hardware specifications, active tasks, command responses, and keystroke logs
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ BunnyLoader (Loader)
Детальный технический анализ BunnyLoader — это Загрузчик вредоносного ПО (Дроппер/Стейджер), разработанный на стеке C / C++ (MSVC / MinGW-GCC) Native PE32 (x86). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTP / HTTPS POST requests with AES-256-CBC encrypted JSON / form-data payloads and Base64 encoding) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTP / HTTPS POST requests with AES-256-CBC encrypted JSON / form-data payloads and Base64 encoding, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
BunnyLoader (Loader) विश्लेषण
BunnyLoader एक परिष्कृत मैलवेयर लोडर और ड्रॉपर पेलोड है जिसे C / C++ (MSVC / MinGW-GCC) Native PE32 (x86) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTP / HTTPS POST requests with AES-256-CBC encrypted JSON / form-data payloads and Base64 encoding) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTP / HTTPS POST requests with AES-256-CBC encrypted JSON / form-data payloads and Base64 encoding आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).