01 | Tool Specifications & Architectural Profile
{
  "compiler": "MinGW GCC / Microsoft Visual C++ (Beacon agent) and OpenJDK Java Compiler (TeamServer)",
  "runtime": "Native Win32/Win64 PE execution environment (Beacon); Java Virtual Machine 11+ (TeamServer)",
  "binary_footprint": "Reflective PE32 / PE32+ Dynamic Link Library (beacon.dll), typ. 180 KB - 320 KB uncompressed memory footprint",
  "stub_size": "212,992 bytes (typical x64 beacon.dll stageless payload); staged stagers measure 800 - 1,200 bytes",
  "packer_obfuscation": "Artifact Kit custom loaders, Sleep Mask obfuscation (v1-v4), Module Stomping, Process Mocking, and UDRL (User Defined Reflective Loaders)",
  "subsystem": "Windows GUI / Console (Subsystem 2 or 3 depending on staging wrapper)",
  "entry_point_flow": "ReflectiveLoader bootstrap -> PEB traversal & ROR-13 API hashing -> Memory allocation via VirtualAlloc -> Section mapping & Relocations -> DllMain(DLL_PROCESS_ATTACH) -> BeaconInit() -> Setting table XOR decoding -> Sleep & C2 check-in loop",
  "technical_summary": "Cobalt Strike is a modular, client-server adversary simulation framework centered on Beacon, a post-exploitation payload engineered for in-memory execution. Beacon employs Stephen Fewer-derived reflective DLL injection, highly malleable network communication profiles, timer-driven memory obfuscation (Sleep Mask), and nested lateral movement pivots through SMB named pipes."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Java Swing Desktop Client (cobaltstrike.jar)",
  "builder_tabs_options": [
    {
      "tab": "Listeners Configuration",
      "options": [
        "Payload Types: Beacon HTTP, Beacon HTTPS, Beacon DNS, Beacon SMB, Beacon TCP, External C2",
        "HTTP Hosts / Host Header / Port: Dynamic domain rotation and proxy authentication",
        "Malleable C2 Profile: Selection of customized C2 transformation profile (.profile)",
        "Guard Rails: Watermark validation, execution expiration date, and IP/range binding"
      ]
    },
    {
      "tab": "Payload Generation (Attacks -> Packages)",
      "options": [
        "Windows Executable (Stageless): Compiles full Beacon DLL wrapped in an executable or service binary",
        "Windows Executable (Staged): Emits raw shellcode stager pulling payload over configured listener",
        "Payload Generator: Exports raw shellcode, C, C#, Java, Perl, Python, PowerShell, or VBA arrays",
        "HTML Application (HTA) & Office Macro: Generates initial access payloads executing via mshta.exe or VBA"
      ]
    },
    {
      "tab": "Pivoting & Lateral Movement",
      "options": [
        "SOCKS4a / SOCKS5 Proxy: Spawns in-memory SOCKS server listening on operator client port",
        "Reverse Port Forwarding (rportfwd): Relays external TCP streams through compromised beacon session",
        "SMB Named Pipe Linking: 'link <target> <pipename>' establishes peer-to-peer parent-child C2 tree"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x0001",
      "type": "short",
      "field": "SETTING_BEACONTREE",
      "description": "Beacon communication protocol type (0x00=HTTP, 0x01=DNS, 0x02=SMB, 0x04=HTTPS, 0x08=TCP)"
    },
    {
      "offset": "0x0002",
      "type": "short",
      "field": "SETTING_PORT",
      "description": "C2 callback port integer (e.g., 80, 443, 8080)"
    },
    {
      "offset": "0x0003",
      "type": "int",
      "field": "SETTING_SLEEPTIME",
      "description": "Base callback sleep interval in milliseconds"
    },
    {
      "offset": "0x0004",
      "type": "int",
      "field": "SETTING_MAXGET",
      "description": "Maximum size of HTTP GET request payload frame"
    },
    {
      "offset": "0x0005",
      "type": "short",
      "field": "SETTING_JITTER",
      "description": "Percentage jitter applied to sleep intervals (0 - 99%)"
    },
    {
      "offset": "0x0006",
      "type": "short",
      "field": "SETTING_MAXDNS",
      "description": "Maximum length of DNS query strings"
    },
    {
      "offset": "0x0007",
      "type": "bytes",
      "field": "SETTING_PUBKEY",
      "description": "RSA public key in DER format used to encrypt session metadata"
    },
    {
      "offset": "0x0008",
      "type": "string",
      "field": "SETTING_DOMAINS",
      "description": "Comma-separated list of C2 callback hosts and URI paths"
    },
    {
      "offset": "0x0009",
      "type": "string",
      "field": "SETTING_USERAGENT",
      "description": "HTTP User-Agent header string configured in profile"
    },
    {
      "offset": "0x000a",
      "type": "string",
      "field": "SETTING_SUBMITURI",
      "description": "HTTP POST endpoint for task output transmission"
    },
    {
      "offset": "0x000e",
      "type": "string",
      "field": "SETTING_SPAWNTO_X86",
      "description": "Default target binary path for 32-bit process injection (e.g., %windir%\\syswow64\\rundll32.exe)"
    },
    {
      "offset": "0x000f",
      "type": "string",
      "field": "SETTING_SPAWNTO_X64",
      "description": "Default target binary path for 64-bit process injection (e.g., %windir%\\system32\\rundll32.exe)"
    },
    {
      "offset": "0x001d",
      "type": "short",
      "field": "SETTING_USESM",
      "description": "Boolean flag enabling Sleep Mask in-memory encryption stub"
    }
  ],
  "payload_generation_flags": [
    "stage.obfuscate: Strips PE header strings and masks import section during allocation",
    "stage.userwx: Controls whether in-memory allocations require PAGE_EXECUTE_READWRITE (false enforces RX)",
    "stage.cleanup: Automatically frees bootstrap reflective loader memory after PE initialization",
    "stage.sleep_mask: Injects Sleep Mask stub to XOR-encrypt payload memory pages during sleep cycle"
  ],
  "operator_commands": [
    "sleep <sec> <jitter>: Updates callback sleep interval and jitter percentage",
    "execute-assembly <path> <args>: Executes .NET assembly in-memory via sacrificial CLR host",
    "bof-execute <bof_path>: Executes unlinked Beacon Object File (BOF) directly in Beacon thread context",
    "shinject <pid> <arch> <path>: Injects raw position-independent shellcode into target process",
    "make_token <domain> <user> <pass>: Creates new logon session token using LogonUserW",
    "steal_token <pid>: Duplicates security token from specified process using OpenProcessToken / DuplicateTokenEx",
    "link <pipe_target>: Connects to SMB named pipe listener on internal pivot machine",
    "socks <port>: Launches SOCKS4a proxy routing local operator traffic through target Beacon"
  ],
  "interface_telemetry_analysis": "The operator UI provides complete session orchestration across heterogeneous network environments, displaying interactive process graphs, credential vaults, and multi-hop pivot links in real time."
}struct Cobalt_Strike_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Process Injection / Fork & Run: Beacon invokes CreateProcessW with CREATE_SUSPENDED (0x00000004) targeting the configured SpawnTo binary -> Allocates remote memory via VirtualAllocEx (PAGE_READWRITE) -> Writes shellcode or reflective payload via WriteProcessMemory -> Transitions page protection via VirtualProtectEx to PAGE_EXECUTE_READ -> Spawns execution via CreateRemoteThread, RtlCreateUserThread, or QueueUserAPC.",
  "ntapi_functions": [
    "ntdll!NtAllocateVirtualMemory",
    "ntdll!NtProtectVirtualMemory",
    "ntdll!NtWriteVirtualMemory",
    "ntdll!NtCreateThreadEx",
    "ntdll!NtQueueApcThread",
    "ntdll!NtWaitForSingleObject",
    "ntdll!NtDelayExecution"
  ],
  "reflective_loader": "UserDefinedReflectiveLoader (UDRL): Traverses the PEB to locate in-memory kernel32.dll -> Resolves LoadLibraryA, GetProcAddress, and VirtualAlloc via ROR-13 hashing -> Allocates memory base -> Maps PE sections to their relative virtual addresses (RVA) -> Applies base relocations -> Binds Import Address Table (IAT) descriptors -> Invokes DLL entry point with DLL_PROCESS_ATTACH.",
  "sleep_mask_evasion": "Sleep Mask Engine (v1 - v4): Intercepts the sleep cycle -> Identifies Beacon's base allocation via VirtualQuery -> Invokes VirtualProtect to change image sections from RX/RWX to RW -> XOR-encrypts text sections, data sections, and allocated heap with an ephemeral 13-byte or system-randomized key -> Invokes delay routine (NtDelayExecution or ROP-driven timer queues using CreateTimerQueueTimer / SetWaitableTimer) -> Decrypts memory space upon timer expiration -> Re-applies original memory permissions before processing tasks.",
  "named_pipe_pivoting": "SMB Pivot Architecture: Establishes named pipe listeners via CreateNamedPipeA using formatted strings (e.g., \\\\.\\pipe\\msagent_*). Child beacons connect to the parent pipe using CreateFileA and communicate using ReadFile / WriteFile. The parent Beacon serializes child frames into its primary C2 check-in stream, allowing fully isolated subnets to pivot without direct Internet routing.",
  "anti_analysis": "Module Stomping (overwriting benign DLL memory sections), Thread Stack Spoofing (fabricating legitimate call frames during sleep), Heap Encryption, and PE header wiping."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Cobalt Strike binary:
[ "In-memory execution of unmanaged .NET binaries via dynamic CLR initialization (execute-assembly)", "Execution of Beacon Object Files (BOF) compiled as small COFF objects linked dynamically in-memory", "Mimikatz integration executing logonpasswords, dcsync, and kerberos ticket harvesting", "Token manipulation enabling token theft, token creation, and privilege elevation via ImpersonateLoggedOnUser" ]
[ "Dynamic SOCKS4a and SOCKS5 proxy server hosting over C2 channel", "Reverse Port Forwarding (rportfwd) directing external traffic through target network", "SMB and TCP peer-to-peer Beacon chaining over named pipes and direct sockets" ]
[ "Desktop screen capture scraping GDI surfaces via GetDC / BitBlt", "Asynchronous keylogger hooking low-level Windows keyboard events", "Process browser, file browser, and port scanner with multi-threaded TCP scanning" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "HTTP GET / POST requests framed according to Malleable C2 grammar specifications. Tasks and metadata are length-prefixed with 4-byte big-endian integers.",
  "serialization": "Custom TLV (Type-Length-Value) packet structure encoding task IDs, command types, and serialized parameter buffers.",
  "handshake": "Beacon generates a 16-byte AES-256 session key and 16-byte HMAC key -> Encrypts keys along with system metadata (PID, user, hostname, IP) using TeamServer's RSA-1024 / RSA-2048 public key -> Transmits encrypted metadata block via HTTP GET cookie, header, or URI parameter.",
  "cryptography": "AES-256-CBC with PKCS7 padding for tasking and exfiltration streams; HMAC-SHA256 signature verification over every encrypted frame to ensure message integrity.",
  "packet_types": [
    "0x00: Check-in / Metadata frame containing encrypted session keys and host telemetry",
    "0x01: Command tasking frame containing serialized operator instructions",
    "0x02: Command output frame containing AES-encrypted command execution output"
  ],
  "traffic_signature": "User-defined malleable transformations allow complete emulation of legitimate REST APIs, CDN asset requests, and software update telemetry."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_CobaltStrike_Beacon_Signatures {
    meta:
        description = "Detects Cobalt Strike Beacon reflective DLL loader and configuration setting structures"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        reference = "TF-031"
    strings:
        $udrl_x64 = { 48 89 5C 24 08 57 48 83 EC 20 48 8B D9 48 8B 0D ?? ?? ?? ?? 48 85 C9 }
        $setting_decode = { 8A 04 0A 30 04 0A 41 83 C2 01 41 81 FA ?? ?? 00 00 72 EF }
        $pipe_pattern = "\\\\%s\\pipe\\msagent_%x"
        $default_uri = "/activity"
    condition:
        uint16(0) == 0x5A4D and (2 of them)
}title: Cobalt Strike Named Pipe Communication and Pivoting
id: a2b5c7e1-8894-4d2a-bc91-231a4f028b12
status: stable
description: Detects creation and connection to named pipes matching default or common Cobalt Strike pivot naming conventions.
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
product: windows
category: pipe_created
detection:
selection:
PipeName|contains:
- '\pipe\msagent_'
- '\pipe\status_'
- '\pipe\mojo.5688.8054.'
- '\pipe\spoolss_'
condition: selection
fields:
- ProcessId
- Image
- PipeName
falsepositives:
- Customized legitimate administrative tools using identical pipe strings
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
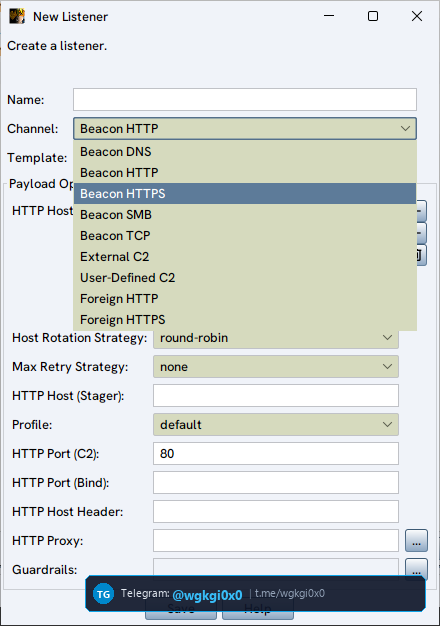
Operator interface configuring HTTP, HTTPS, and DNS malleable C2 listeners and tracking active Beacons.

Technical schematic showing Reflective DLL loading, sleep masking, and thread stack spoofing mechanisms.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Malleable C2, DNS/HTTPS/SMB Beacons command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Cobalt Strike (C2 Framework)
Industry-standard post-exploitation adversary simulation platform utilizing in-memory reflective Beacon agents, Malleable C2 network shaping, and Sleep Mask evasion.
C2 Architecture: {'framing': 'HTTP GET / POST requests framed according to Malleable C2 grammar specifications. Tasks and metadata are length-prefixed with 4-byte big-endian integers.', 'serialization': 'Custom TLV (Type-Length-Value) packet structure encoding task I
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Cobalt Strike (C2 Framework)
Детальный технический анализ Cobalt Strike — это Фреймворк командно-контрольного управления (C2), разработанный на стеке TeamServer: OpenJDK / Oracle JVM 11-17; Beacon Payload: MinGW / MSVC (C/Assembly x86 and x64). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Malleable HTTP/HTTPS (AES-256-CBC / HMAC-SHA256), DNS A/TXT/AAAA records, SMB Named Pipes (\\pipe\\*), Raw TCP) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Malleable HTTP/HTTPS (AES-256-CBC / HMAC-SHA256), DNS A/TXT/AAAA records, SMB Named Pipes (\\pipe\\*), Raw TCP, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Cobalt Strike (C2 Framework) विश्लेषण
Cobalt Strike एक परिष्कृत कमांड और कंट्रोल (C2) फ्रेमवर्क है जिसे TeamServer: OpenJDK / Oracle JVM 11-17; Beacon Payload: MinGW / MSVC (C/Assembly x86 and x64) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Malleable HTTP/HTTPS (AES-256-CBC / HMAC-SHA256), DNS A/TXT/AAAA records, SMB Named Pipes (\\pipe\\*), Raw TCP) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Malleable HTTP/HTTPS (AES-256-CBC / HMAC-SHA256), DNS A/TXT/AAAA records, SMB Named Pipes (\\pipe\\*), Raw TCP आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).