01 | Tool Specifications & Architectural Profile
{
  "compiler": "apktool + Smali/Baksmali + apksigner orchestrated by EVLF Dev .NET Framework 4.8 Builder",
  "runtime": "Android Runtime (ART) / Dalvik VM (DEX bytecode)",
  "binary_footprint": "Single or Multi-DEX APK package, typ. 1.2 MB - 4.8 MB standalone stub; 15 MB - 80 MB when bound to legitimate host APK",
  "stub_size": "1,450,000 bytes (unpacked template APK before CJK class renaming and junk Smali injection)",
  "packer_obfuscation": "Custom Smali class/method renaming using Unicode CJK ideographs, junk NOP/goto sled insertion, encrypted DEX payload loading via DexClassLoader, and manifest attribute tampering",
  "subsystem": "Android Application Framework (Background Service + AccessibilityService + SYSTEM_ALERT_WINDOW)",
  "entry_point_flow": "MainActivity / Dropper Activity -> Request AccessibilityService prompt loop -> Auto-grant runtime permissions via performAction(ACTION_CLICK) -> Start SensorRestarterBroadcastReceiver & Foreground Service -> Initialize TCP Socket loop to C2 Host/Port",
  "technical_summary": "Developed by EVLF Dev as a commercial successor to SpyNote and CypherRAT, CraxsRAT is an Android remote control and banking overlay framework controlled via a C# .NET WinForms console. Its core execution model centers on abusing Android's AccessibilityService API to automatically grant runtime permissions, capture UI view hierarchies (including OTPs and cryptocurrency seed phrases), inject automated touch/scroll gestures via Hidden VNC (HVNC), and prevent uninstallation through active Settings window termination."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "GUI Builder / Operator Console",
  "builder_tabs_options": [
    {
      "tab": "Connection",
      "options": [
        "Host / IP / DNS: Primary and fallback C2 domain or IPv4 addresses added to connection list",
        "Port: TCP listener port integer (e.g., 7771, 6666, 4444)",
        "Client Name: Identifier tag assigned to infected handsets in the operator grid",
        "Connection Key: Shared secret string authenticating client socket handshakes"
      ]
    },
    {
      "tab": "Options",
      "options": [
        "Hide Icon: Suppresses launcher activity alias after initial Accessibility grant",
        "Keep Screen On: Acquires PARTIAL_WAKE_LOCK andSCREEN_DIM_WAKE_LOCK to prevent Doze sleep",
        "Deactivate Doze Mode: Automates ACTION_REQUEST_IGNORE_BATTERY_OPTIMIZATIONS dialog approval",
        "Start On Boot: Registers RECEIVE_BOOT_COMPLETED broadcast receiver for reboot persistence"
      ]
    },
    {
      "tab": "information",
      "options": [
        "App Name: Display label injected into AndroidManifest.xml and strings.xml",
        "Package Name: Custom Java package namespace (e.g., com.google.service.update)",
        "Version Name / Code: Spoofed semantic version metadata",
        "App Icon: PNG icon replacement across mipmap-mdpi through mipmap-xxxhdpi directories"
      ]
    },
    {
      "tab": "Tools",
      "options": [
        "Draw Over Apps: Requests SYSTEM_ALERT_WINDOW for black-screen masking and WebView phishing overlays",
        "Offline Keylogger: Hooks TYPE_VIEW_TEXT_CHANGED and SimpleIME.class input events to local storage",
        "Anti-Emulator: Terminates execution if Build.FINGERPRINT, QEMU props, or goldfish hardware strings are detected",
        "Super Mod: Enables aggressive anti-deletion loop that forces HOME navigation whenever Settings or App Info opens",
        "Bind With Another APK: Merges malicious DEX and manifest components into a clean third-party APK"
      ]
    },
    {
      "tab": "Login",
      "options": [
        "Title / Discription: Custom prompt text shown on initial AccessibilityService permission lure screen",
        "Custom WebView URL: Loads fake carrier, banking, or Google Play verification page during setup"
      ]
    },
    {
      "tab": "Permissions",
      "options": [
        "Auto-Grant Runtime Permissions: Selecting Camera, Microphone, SMS, Contacts, Location, and External Storage for Accessibility auto-clicker approval"
      ]
    },
    {
      "tab": "Build",
      "options": [
        "Obfuscate Classes: Renames Smali classes and fields to non-ASCII CJK characters",
        "Anti-Kill / Protect APK: Corrupts ZIP Central Directory extra fields to break jadx and apktool decompilation",
        "Build APK: Compiles, aligns, and signs final APK with auto-generated V1/V2 keystore"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "ClientHost.HOST",
      "field": "Host",
      "type": "String (Base64)",
      "description": "Encoded C2 IP address or Dynamic DNS hostname"
    },
    {
      "offset": "ClientHost.PORT",
      "field": "Port",
      "type": "String (Base64)",
      "description": "Encoded C2 TCP destination port"
    },
    {
      "offset": "ClientHost.KEY",
      "field": "Key",
      "type": "String",
      "description": "Socket packet delimiter and authentication key"
    },
    {
      "offset": "ClientHost.NAM",
      "field": "ClientName",
      "type": "String",
      "description": "Campaign or victim group tag displayed in console"
    },
    {
      "offset": "Data.SUPER_MOD",
      "field": "SuperMod",
      "type": "Boolean / String",
      "description": "Flag enabling Settings crash loop and anti-uninstall protection"
    },
    {
      "offset": "Data.HIDE_ICON",
      "field": "HideIcon",
      "type": "Boolean / String",
      "description": "ComponentManager toggle disabling main launcher alias"
    }
  ],
  "payload_generation_flags": [
    "Smali Class Obfuscation: CJK Ideograph Dictionary",
    "Manifest Tampering: Bogus XML namespace attributes + ZIP Central Directory corruption",
    "APK Signature Scheme: v1 (JAR) + v2 (APK Signature Block)"
  ],
  "operator_commands": [
    "ScreenReader (HVNC): Streams live UI node tree or MediaProjection frames while dispatching remote gesture coordinates",
    "BlackScreen: Projects opaque SYSTEM_ALERT_WINDOW overlay with fake 'System Updating' spinner to hide operator actions",
    "Keylogger: Streams live Accessibility text input events and retrieves stored offline keystroke logs",
    "PermissionsManager: Triggers silent background permission elevation via Accessibility auto-clicker",
    "Injections: Displays HTML/WebView credential harvesting overlays atop targeted banking and crypto package names",
    "SMSManager: Reads inbox/outbox databases, intercepts incoming 2FA SMS, and dispatches outbound messages",
    "FileManager: Enumerates /sdcard/ directory trees, exfiltrates DCIM photos, and uploads secondary payloads",
    "CallForward: Executes USSD MMI codes (*21*number#) to redirect victim voice calls and voice OTPs"
  ],
  "interface_telemetry_analysis": "The CraxsRAT v7.x operator console is a dark-themed C# WinForms dashboard authored by EVLF Dev. Connected handsets populate a visual card or table grid displaying device wallpaper thumbnails, battery percentage, Wi-Fi/cellular signal state, Android version, device model, country flag, and active foreground application icon. A floating action menu exposes one-click triggers for Live Screen Control (HVNC), Hidden Camera, Microphone Listener, Keylogger, and APK Builder tabs."
}struct CraxsRAT_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "APK Dropper / Host App -> DexClassLoader loads encrypted secondary payload from assets/ -> AccessibilityService registered by user via deceptive lure -> onAccessibilityEvent(TYPE_WINDOW_STATE_CHANGED) monitors com.android.packageinstaller ->AccessibilityNodeInfo.findAccessibilityNodeInfosByText('Allow') -> performAction(ACTION_CLICK) auto-grants permissions -> WindowManager.addView(TYPE_APPLICATION_OVERLAY) projects black screen over live HVNC gesture automation.",
  "ntapi_functions": [
    "android.accessibilityservice.AccessibilityService!onAccessibilityEvent",
    "android.accessibilityservice.AccessibilityService!dispatchGesture",
    "android.accessibilityservice.AccessibilityService!performGlobalAction",
    "android.view.WindowManager!addView",
    "android.media.projection.MediaProjectionManager!createScreenCaptureIntent",
    "dalvik.system.DexClassLoader!loadClass",
    "android.app.admin.DevicePolicyManager!lockNow"
  ],
  "process_hollowing_target": "Host APK main process (when bound) or persistent background services masquerading as com.google.android.gms / system update services",
  "persistence_mechanics": [
    "AccessibilityService Bind: System-managed lifecycle restarts the service automatically whenever enabled in Settings -> Accessibility",
    "SensorRestarterBroadcastReceiver: Custom BroadcastReceiver triggered by Service.onDestroy() to immediately re-invoke startForegroundService()",
    "BOOT_COMPLETED & USER_PRESENT Receivers: Re-initializes socket worker threads upon device boot or screen unlock",
    "WakeLock & Battery Optimization Whitelist: Acquires PARTIAL_WAKE_LOCK and auto-clicks 'Allow' on REQUEST_IGNORE_BATTERY_OPTIMIZATIONS"
  ],
  "evasion_hooks": [
    "Super Mod Anti-Uninstall: Inspects getPackageName() and className in TYPE_WINDOW_STATE_CHANGED; if com.android.settings.SubSettings or InstalledAppDetails appears, immediately fires performGlobalAction(GLOBAL_ACTION_HOME) or GLOBAL_ACTION_BACK",
    "Black-Screen Curtain Overlay: Mounts a full-screen WindowManager.LayoutParams.TYPE_APPLICATION_OVERLAY view with FLAG_NOT_FOCUSABLE and FLAG_LAYOUT_IN_SCREEN at zero brightness while dispatching gestures underneath",
    "APK Zip Header Tampering: Modifies compression method flags and extra field lengths in the APK Central Directory to trigger parser exceptions in Apktool and JADX",
    "CJK Identifier Obfuscation: Replaces package hierarchies, class names, and method descriptors with repetitive Chinese/Japanese/Korean Unicode characters"
  ],
  "anti_analysis": [
    "Emulator Environment Checks: Inspects Build.FINGERPRINT, Build.MODEL, Build.HARDWARE ('goldfish', 'ranchu', 'vbox86'), and system properties (ro.kernel.qemu)",
    "Google Play Protect Evasion: Uses staged dropper APKs that load the core RAT DEX payload dynamically from encrypted asset blobs only after installation completes",
    "Dynamic Notification Suppression: Intercepts StatusBarNotification events via NotificationListenerService to cancel security warnings and banking transaction alerts"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the CraxsRAT binary:
[ "Accessibility UI Tree Scraping: Captures text from non-password and exposed EditText nodes, extracting cryptocurrency seed phrases and banking balances", "WebView Overlay Phishing: Monitors active foreground app package names and renders matching HTML/JS login forms over banking and financial apps", "Google Authenticator & 2FA Scraping: Reads com.google.android.apps.authenticator2 UI nodes in real time as OTP codes refresh", "Lockscreen PIN/Pattern Capture: Records coordinate trajectories and text inputs during keyguard unlock events", "SimpleIME Custom Input Method: Optional rogue soft keyboard component logging every character committed to InputConnection" ]
[ "Hidden VNC (HVNC) & Screen Streaming: Captures live display via MediaProjection API or reconstructs wireframes from AccessibilityNodeInfo coordinates", "Dual-Camera Surveillance: Silently initializes Camera / Camera2 APIs using a 1x1 pixel SurfaceView to stream front and rear video", "Live Microphone Recording: Streams PCM audio buffers captured via android.media.AudioRecord (MediaRecorder.AudioSource.MIC)", "Offline & Live Keylogger: Logs TYPE_VIEW_TEXT_CHANGED, TYPE_VIEW_FOCUSED, and clipboard change events with timestamps to local encrypted files", "GPS & Network Geolocation: Polls LocationManager (GPS_PROVIDER and NETWORK_PROVIDER) to report latitude, longitude, and speed" ]
[ "Automated Gesture Dispatch: Executes remote tap, double-tap, swipe, and pinch gestures via AccessibilityService.dispatchGesture(GestureDescription)", "Remote UI Navigation: Triggers GLOBAL_ACTION_BACK, GLOBAL_ACTION_HOME, GLOBAL_ACTION_RECENTS, and GLOBAL_ACTION_LOCK_SCREEN", "Interactive Shell Execution: Runs shell commands via Runtime.getRuntime().exec('sh') and returns stdout/stderr streams", "Application Manager: Enumerates installed packages, launches arbitrary activities, or initiates package installation/removal" ]
[ "Full Storage Browser: Traverses external storage (/storage/emulated/0/) and app-specific directories", "Automated Media & Document Exfiltration: Bulk downloads DCIM/Camera images, WhatsApp media databases, and PDF/DOCX files", "Arbitrary File Upload & Execution: Pushes secondary APK or DEX modules to local storage and triggers silent installation via Accessibility" ]
[ "Clipboard Manager Listener: Registers OnPrimaryClipChangedListener to inspect copied strings in real time", "Wallet Address Substitution: Replaces copied BTC, ETH, ERC-20, and TRC-20 USDT destination addresses with operator-controlled wallets", "Automated Crypto Wallet Drain: Uses HVNC gesture sequences to open Trust Wallet, MetaMask, or Binance, paste operator addresses, and confirm transfers under a black screen overlay" ]
[ "Device Lock / Ransomware Overlay: Forces DevicePolicyManager.lockNow() or displays persistent full-screen HTML lock overlays demanding payment", "Call Forwarding Manipulation: Dials USSD forwarding strings via ACTION_CALL to divert incoming verification calls", "Audio Ringer Suppression: Sets AudioManager ringer and notification streams to RINGER_MODE_SILENT during unauthorized transactions" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Custom delimiter-separated TCP stream using a configurable split token (e.g., '8888' or '<EOF>') combined with length headers and GZIP payload compression",
  "serialization": "String-delimited command tokens paired with Base64-encoded or raw byte arrays for binary media chunks (JPEG screen frames, PCM audio, file buffers)",
  "handshake": "Client opens raw TCP socket to C2 Host:Port -> Sends initial registration packet containing Connection Key, Device UUID, Model, Android API Version, Country, Battery Level, and Accessibility status -> Server acknowledges and begins heartbeat polling",
  "cryptography": "Application-layer payload obfuscation using GZIP compression wrapped in static-key AES-128-CBC or multi-byte XOR + Base64 encoding defined during APK compilation",
  "packet_types": [
    {
      "header": "info / pong",
      "payload": "Device Model, OS Version, Battery %, Active Foreground Package, Wi-Fi Status, Screen State",
      "direction": "Client -> Server"
    },
    {
      "header": "scr / hvnc",
      "payload": "GZIP-compressed JPEG frame buffer or serialized AccessibilityNodeInfo coordinate tree",
      "direction": "Client -> Server"
    },
    {
      "header": "clk / mov",
      "payload": "X/Y touch coordinates, swipe vector duration, or GlobalAction integer ID",
      "direction": "Server -> Client"
    },
    {
      "header": "key / log",
      "payload": "Base64-encoded keystroke buffer with package name and timestamp metadata",
      "direction": "Client -> Server"
    },
    {
      "header": "cam / mic",
      "payload": "Chunked H.264/JPEG camera frame or raw PCM audio stream buffer",
      "direction": "Client -> Server"
    }
  ],
  "traffic_signature": "Persistent non-TLS TCP flows over non-standard high ports (commonly 7771, 7772, 6666) exhibiting periodic keep-alive heartbeats and GZIP magic headers (0x1F 0x8B 0x08) separated by recurring ASCII delimiter strings."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_CraxsRAT_APK_DEX {
    meta:
        description = "Detects CraxsRAT Android DEX payloads via EVLF Dev service markers, Accessibility hooks, and persistence receivers"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-30"
        family = "CraxsRAT"
        platform = "Android"
    strings:
        $dex = { 64 65 78 0A 30 33 ?? 00 }
        $s1 = "SensorRestarterBroadcastReceiver" ascii
        $s2 = "SimpleIME" ascii
        $s3 = "CraxsRat" ascii nocase
        $s4 = "EVLF" ascii
        $s5 = "ClientHost" ascii
        $a1 = "android.accessibilityservice.AccessibilityService" ascii
        $a2 = "dispatchGesture" ascii
        $a3 = "performGlobalAction" ascii
        $a4 = "TYPE_APPLICATION_OVERLAY" ascii
    condition:
        $dex at 0 and
        (2 of ($s*) and 2 of ($a*))
}title: CraxsRAT C2 Listener and APK Builder Execution on Operator Host
id: 4f8a2b1c-9d3e-4f5a-8b7c-1e2d3f4a5b6c
status: stable
description: Detects execution of the CraxsRAT .NET operator console and its child Java/Apktool APK compilation toolchain on Windows hosts.
author: CyberTrace Defense Engineering
date: 2026/10/30
references:
- https://attack.mitre.org/Mobile/techniques/T1453/
tags:
- attack.execution
- attack.command_and_control
- attack.t1071
logsource:
category: process_creation
product: windows
detection:
selection_builder:
ParentImage|endswith:
- '\CraxsRat.exe'
- '\Craxs.exe'
Image|endswith:
- '\java.exe'
- '\javaw.exe'
CommandLine|contains:
- 'apktool'
- 'signapk'
- 'apksigner'
- 'zipalign'
condition: selection_builder
falsepositives:
- None expected for processes spawned directly by CraxsRat binaries.
level: critical07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
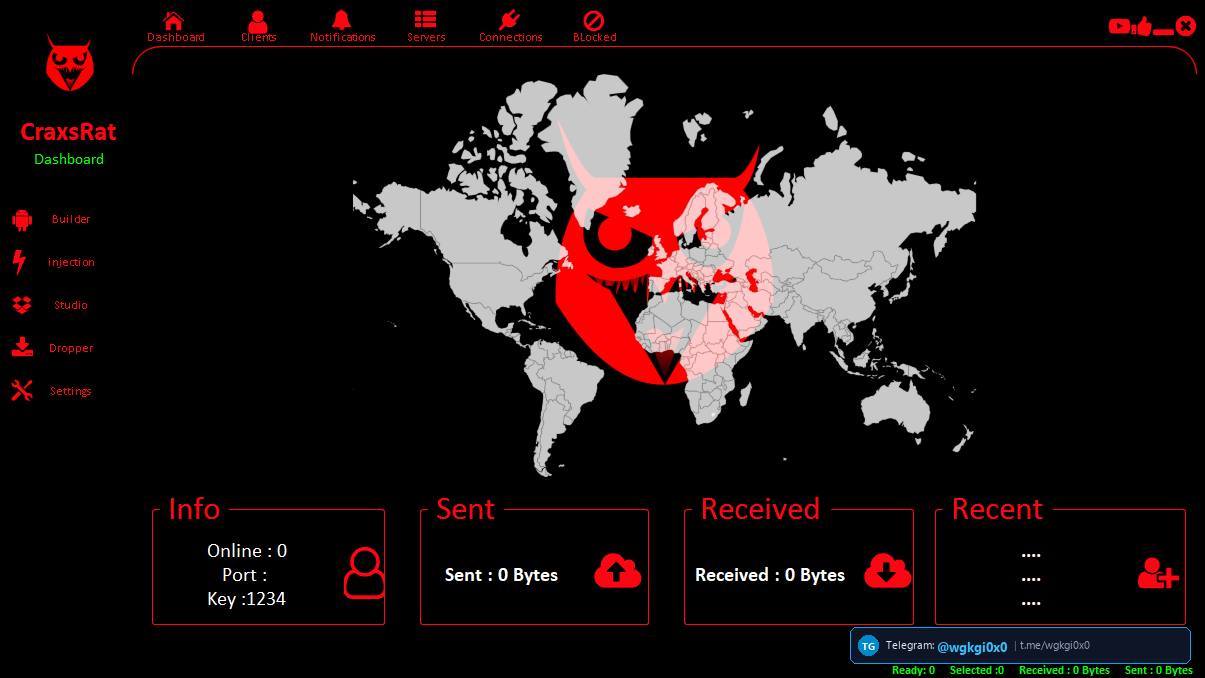
EVLF Dev C# .NET WinForms operator dashboard displaying client telemetry, port listener status, and APK builder navigation.
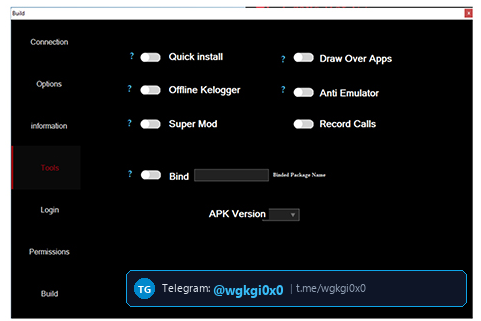
Authentic CraxsRAT Builder Tools tab configuring Draw Over Apps, Offline Keylogger, Anti-Emulator, Super Mod anti-deletion, and APK Binding.
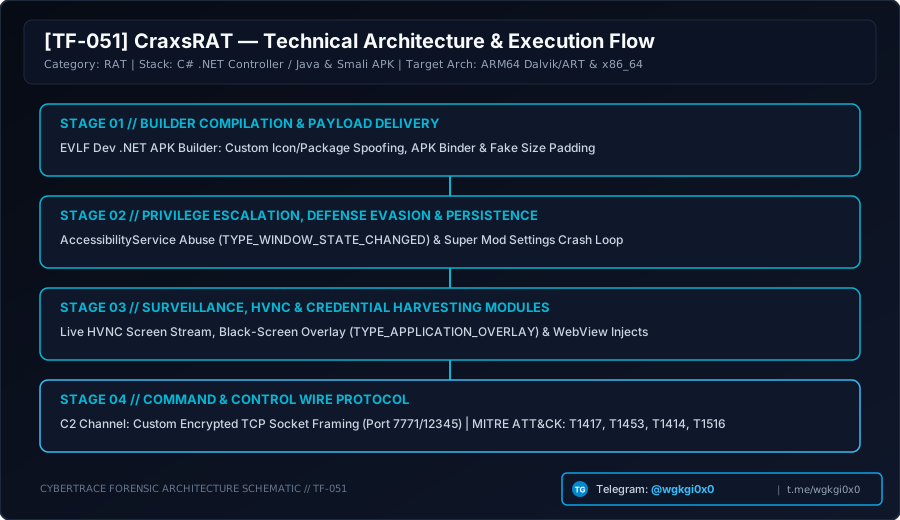
Forensic architecture schematic detailing EVLF Dev APK compilation, AccessibilityService gesture dispatch, HVNC screen streaming, and encrypted TCP socket framing.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
CraxsRAT (RAT)
Commercial Android RAT authored by EVLF Dev featuring AccessibilityService privilege escalation, live HVNC gesture control, black-screen overlays, and CJK bytecode obfuscation.
C2 Architecture: {'framing': "Custom delimiter-separated TCP stream using a configurable split token (e.g., '8888' or '<EOF>') combined with length headers and GZIP payload compression", 'serialization': 'String-delimited command tokens paired with Base64-encoded or
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ CraxsRAT (RAT)
Детальный технический анализ CraxsRAT (v7.6, EVLF Dev) — коммерческого Android-трояна удаленного доступа (RAT) с серверной панелью на C# .NET WinForms. В отчете исследуются механизмы злоупотребления Android AccessibilityService, скрытая трансляция экрана (HVNC), перехват криптокошельков через WebView-оверлеи, обход ограничений Google Play Protect и защита от удаления (Super Mod).
Архитектура C2: Зашифрованный протокол поверх сырых TCP-сокетов с GZip-сжатием, префиксами длины пакетов и туннелированием через Cloudflare/Ngrok.
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
CraxsRAT (RAT) विश्लेषण
CraxsRAT (v7.6, EVLF Dev) एक उन्नत Android रिमोट एक्सेस ट्रोजन (RAT) है जिसका ऑपरेटर कंसोल C# .NET WinForms में निर्मित है। इस तकनीकी CTI विश्लेषण में Android AccessibilityService का दुरुपयोग, मोबाइल HVNC स्क्रीन स्ट्रीमिंग, क्रिप्टो वॉलेट WebView ओवरले इंजेक्शन और Super Mod एंटी-डिलीशन तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: GZip संपीड़न और कस्टम बाइनरी लंबाई-प्रीफ़िक्स फ्रेमिंग के साथ एन्क्रिप्टेड कच्चे TCP सॉकेट C2 प्रोटोकॉल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).