01 | Tool Specifications & Architectural Profile
Constructed primarily in Embarcadero Delphi, resulting in substantial PE files characterized by Borland Delphi runtime signatures, Visual Component Library (VCL) metadata, and extensive RTTI tables. Delivery relies on multi-stage modular execution pipelines: typically an initial Windows Installer (.msi) package, VBScript, or PDF lure extracts a legitimate compiled AutoIt3.exe executable alongside an heavily obfuscated AutoIt script (.au3 or .a3x). The script performs in-memory shellcode reconstruction and injects the core Delphi PE into user-mode processes.
02 | Operator Interface & Configuration Struct Model
DarkGate is managed through a closed-access web management dashboard rented as Malware-as-a-Service (MaaS). Configuration settings are embedded in the compiled Delphi binary within an obfuscated string block. The configuration parser decrypts this block using a unique 64-character custom Base64 alphabet (substituting the standard RFC 4648 character set with a pseudo-random permutation, e.g., 'zLAxuU0kMmrs...') followed by a multi-byte XOR key. Decrypted configuration flags: Index 0: C2 Server URL list; Index 1: Ping/Heartbeat interval (seconds); Index 2: Anti-Analysis and Anti-VM toggle; Index 3: Embedded Cryptominer flag; Index 4: Registry Run Key persistence string; Index 5: XOR Encryption Key for C2 communications; Index 6: Campaign Identifier; Index 7: Botnet Group Tag.
struct DarkGate_Loader_Config {
    uint32_t magic;
    char c2_host[128];
    uint16_t port;
    char install_path[260];
    char mutex[64];
    uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
The AutoIt staging script allocates heap memory via kernel32.dll!VirtualAlloc(PAGE_EXECUTE_READWRITE) and invokes shellcode using CallWindowProc or DllCallAddress. The shellcode serves as a custom reflective loader: it parses its own embedded DarkGate Delphi payload, allocates virtual memory, manually resolves imports via API hashing (hashing Win32 API names with a modified ROR-13 algorithm), and applies base relocations. DarkGate incorporates NTAPI direct syscall stagers to bypass user-mode API hooking installed by EDR products on ntdll.dll (e.g., NtAllocateVirtualMemory, NtWriteVirtualMemory, NtProtectVirtualMemory). It performs aggressive anti-VM verification: queries CPUID hypervisor bit, inspects disk drive strings for 'VMware', 'VBOX', 'QEMU', measures Sleep execution timing against GetTickCount64, and enumerates installed software checking for analysis tools (Wireshark, Process Hacker, x64dbg).
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the DarkGate Loader binary:
Dynamically fetches and executes secondary payloads from the C2 server, supporting DLL reflection, raw shellcode execution, and executable drops.
High-performance Hidden Virtual Network Computing engine built using Delphi VCL graphics primitives. Spawns an isolated desktop, intercepts window messaging, and streams compressed desktop frames.
Extracts credentials, autofill forms, credit cards, and session cookies from Chromium browsers (decrypting DPAPI and App-Bound Encryption tokens) and Gecko-based profiles.
Integrates an obfuscated XMRig cryptocurrency miner module configured to mine Monero (XMR). Implements dynamic CPU throttling: suspends mining threads immediately when Task Manager or Process Hacker processes are spawned.
Scans Local Storage leveldb folders in %APPDATA%\discord and %APPDATA%\Telegram Desktop for active session tokens.
Deploys an in-memory reverse proxy client allowing operators to route traffic through the infected machine.
05 | Wire Protocol & C2 Communication Framing
Communication utilizes HTTP/HTTPS POST requests over custom TCP ports (e.g., 80, 443, 2355, 9999). Message bodies are encrypted using the custom Base64 alphabet and XOR key extracted from the configuration. Request structure: HTTP POST /<random_string> HTTP/1.1; Host: <C2_IP>; User-Agent: <Custom_or_Mozilla>; Content-Type: application/x-www-form-urlencoded. Request body payload contains key-value pairs formatted as: 'id=<Victim_ID>&data=<Encrypted_Blob>'. The C2 server returns an encrypted task string parsed by the client dispatch loop into numerical task codes: Code 1: Download and execute secondary binary; Code 2: Execute shell command via cmd.exe; Code 3: Activate HVNC module; Code 4: Start/Stop Cryptominer; Code 5: Terminate and self-delete.
06 | Verified Detection Signatures (YARA & Sigma)
rule Mal_Win_DarkGate_Delphi_Core {
    meta:
        description = "Detects DarkGate Delphi core payload and custom Base64 alphabet"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        hash = "46a7be755be888e2c050e0bc324f4e2f896b054238e55e884ecb2cbbab793a38"
        threat_id = "TF-009"
    strings:
        $delphi1 = "Borland\\Delphi\\RTL" ascii
        $delphi2 = "SOFTWARE\\Borland\\Delphi" ascii
        $str_c2 = "DarkGate" ascii wide
        $autoit_ref = "AutoIt3.exe" ascii wide
        $xor_loop = { 8A 14 0A 32 14 0B 88 14 0A 41 3B CA 72 F2 } // Typical Delphi XOR decryption loop
        $b64_custom = /[a-zA-Z0-9+\/]{64}/ ascii
    condition:
        uint16(0) == 0x5A4D and
        ( (2 of ($delphi*) and $str_c2) or ($autoit_ref and $xor_loop) or (all of ($delphi*) and $xor_loop) )
}title: DarkGate AutoIt Execution from Suspicious Directory
id: f3849c20-e234-4a21-9556-44d86f02e009
status: production
description: Detects execution of AutoIt3 interpreter from non-standard staging directories (ProgramData, Temp, AppData) typical of DarkGate stagers.
references:
- https://cybertrace.io/threats/darkgate-whitepaper.html
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
category: process_creation
product: windows
detection:
selection:
Image|endswith:
- '\autoit3.exe'
- '\AutoIt3_x64.exe'
CommandLine|contains:
- 'C:\ProgramData\'
- '\AppData\Local\Temp\'
- '\AppData\Roaming\'
selection_flags:
CommandLine|contains:
- '.au3'
- '.a3x'
condition: selection and selection_flags
falsepositives:
- Legitimate internal enterprise administrative automation scripts utilizing AutoIt
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
46a7be755be888e2c050e0bc324f4e2f896b054238e55e884ecb2cbbab793a38
9c824c1e13aa4db3dc8808dcfa7ae293b679bf448cc40e5318db49b5c2d338fb
2d338fbf5bc4727142b78119ce06259f63f59db5a3e8a2b53f65cd600b343867
185.234.247[.]119:2355
45.130.138[.]168:80
darkgate-panel[.]top:443
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\DarkGate
HKCU\Software\DarkGate
C:\ProgramData\autoit3.exe
C:\ProgramData\test.au3
%TEMP%\darkgate_payload.dll
DarkGate_V5_Mutex
DG_Instance_Lock_01
08 | Forensic Visual Evidence & Disassembly Artifacts (4 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
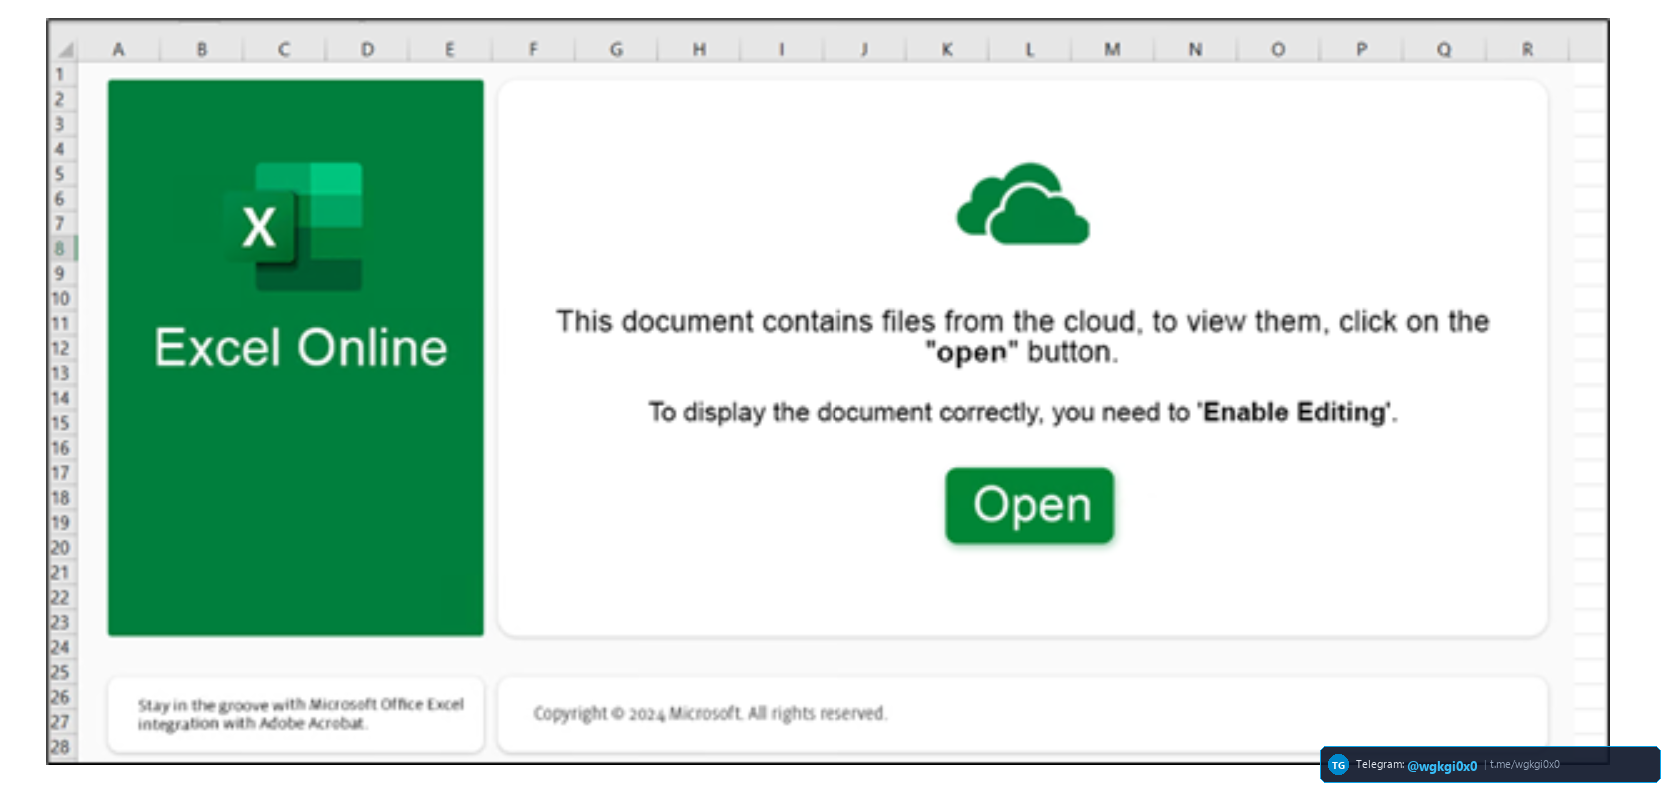
Malwarebytes forensic capture showing rogue MSI installer dropping obfuscated AutoIt interpreter script stubs.
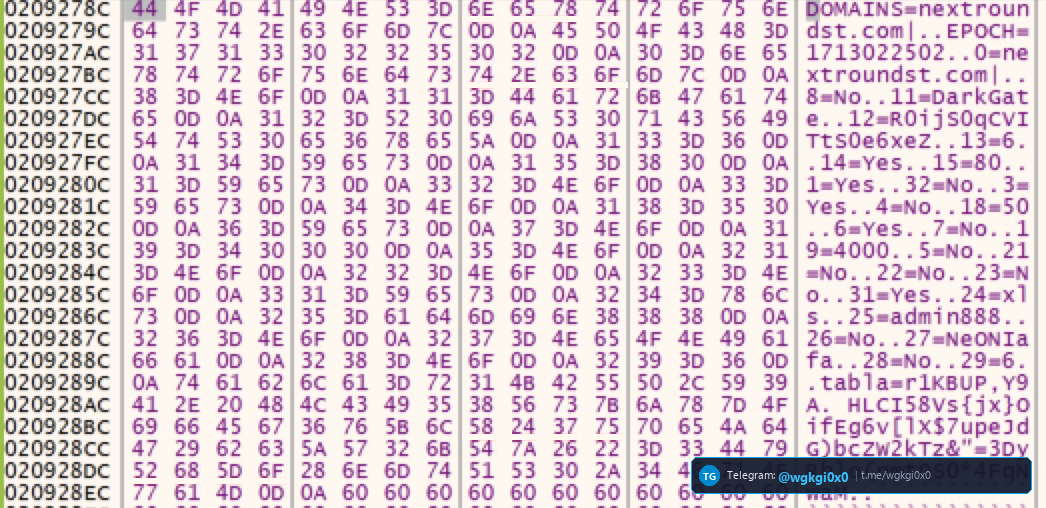
Automated extractor output displaying AES-encrypted C2 servers, botnet flags, and evasion switches.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Custom HTTP Encryption, Obfuscated Query Params command infrastructure.
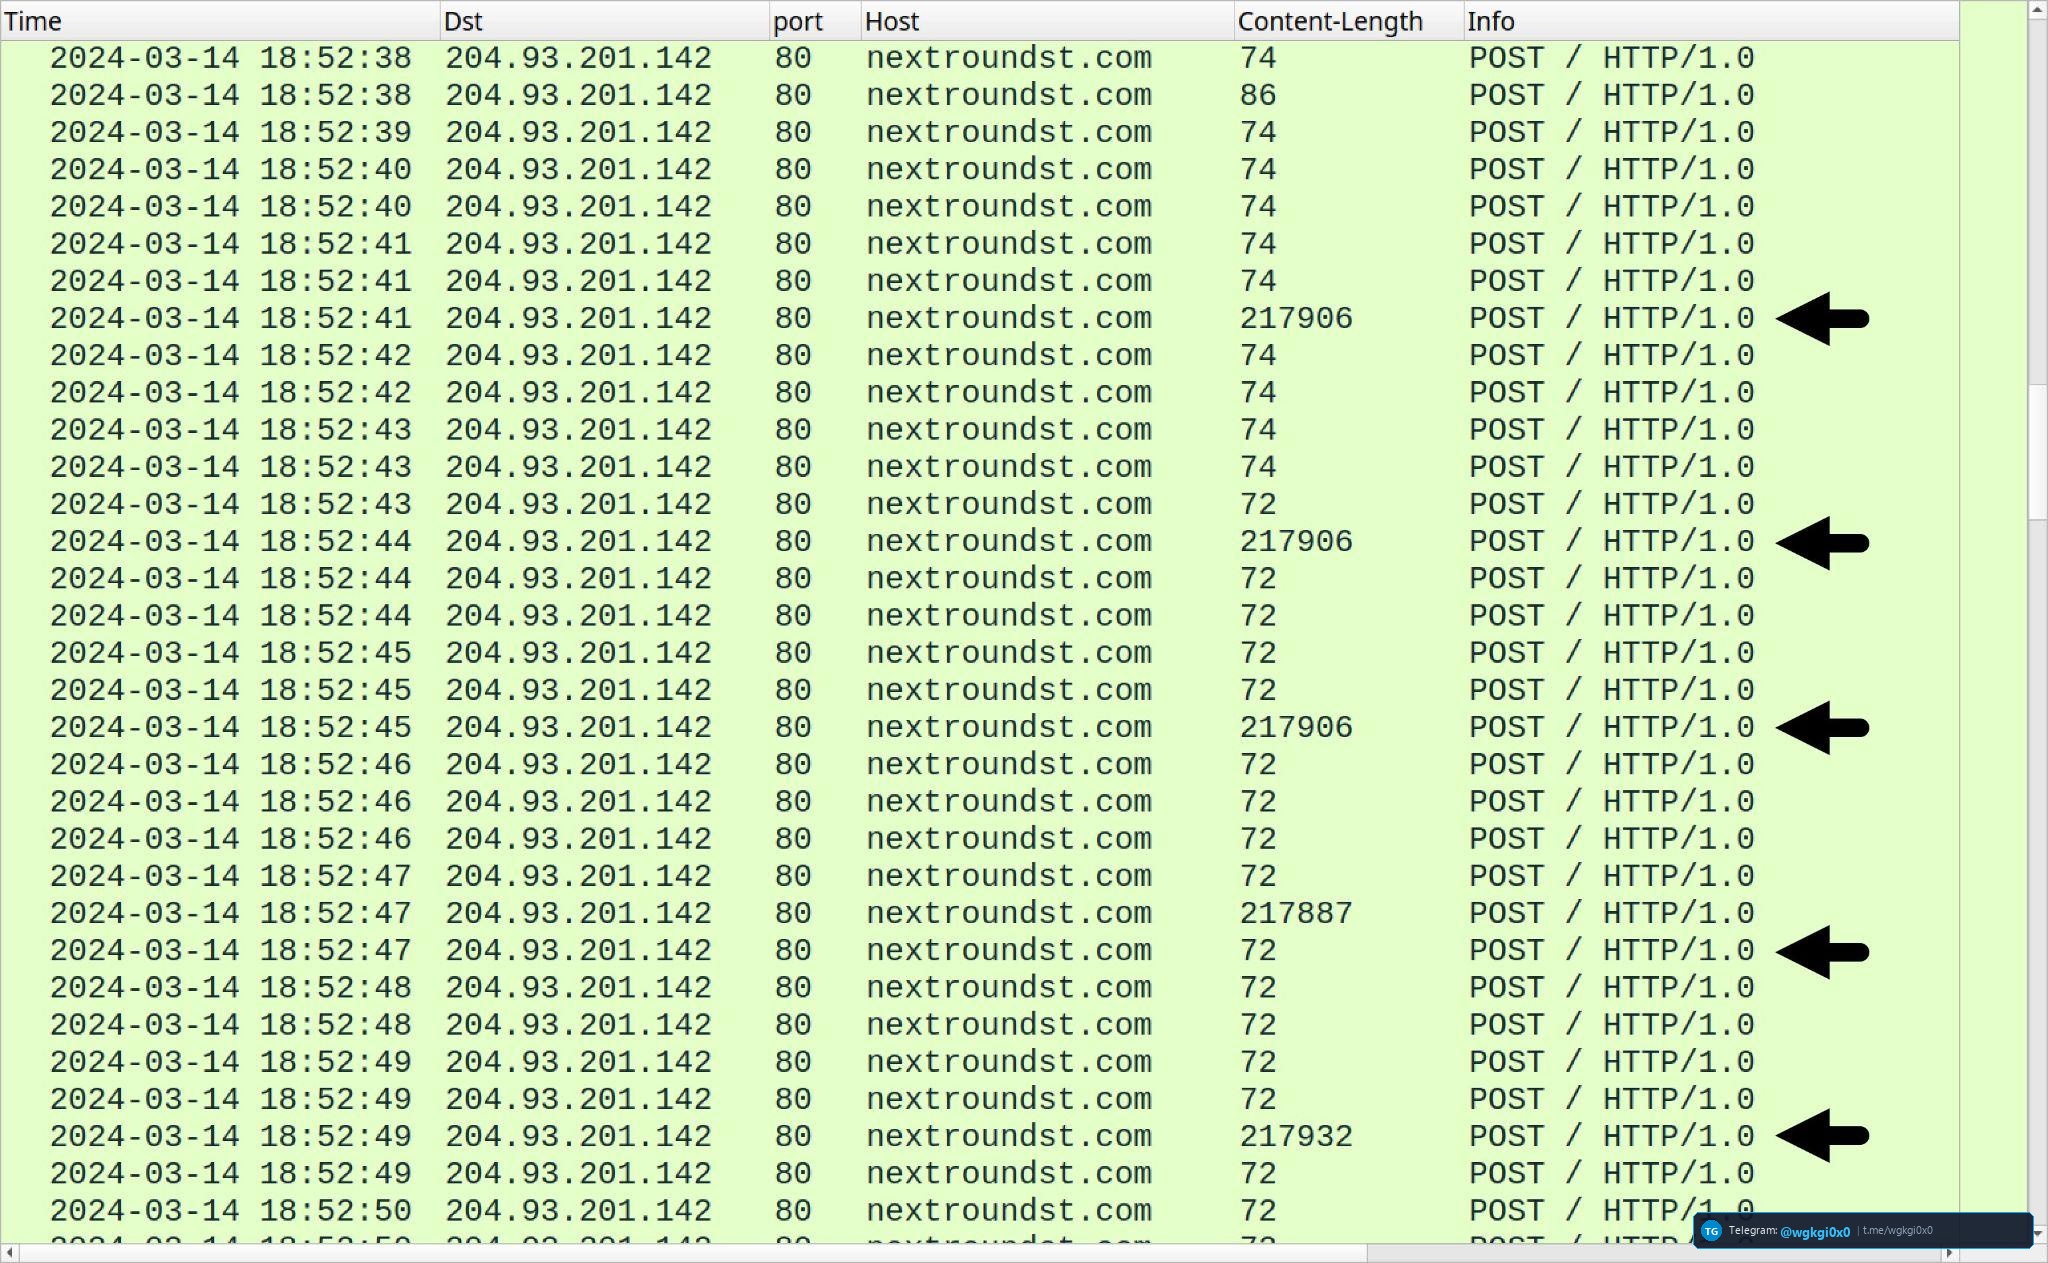
Raw packet inspection showing HTTP POST parameters and custom User-Agent beacons.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
DarkGate Loader (Loader)
High-complexity Delphi modular loader featuring multi-stage AutoIt scripting stagers, custom Base64 alphabet C2 encryption, direct NTAPI syscalls, and in-memory payload execution.
C2 Architecture: Communication utilizes HTTP/HTTPS POST requests over custom TCP ports (e.g., 80, 443, 2355, 9999). Message bodies are encrypted using the custom Base64 alphabet and XOR key extracted from the configuration. Request structure: HTTP POST /<random_strin
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ DarkGate Loader (Loader)
Детальный технический анализ DarkGate Loader — это Загрузчик вредоносного ПО (Дроппер/Стейджер), разработанный на стеке Embarcadero Delphi 10/11 (Native x86/x64) with AutoIt v3 Stagers. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTP/HTTPS with Custom Base64 Character Set Substitution & Rotating XOR Keys) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTP/HTTPS with Custom Base64 Character Set Substitution & Rotating XOR Keys, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
DarkGate Loader (Loader) विश्लेषण
DarkGate Loader एक परिष्कृत मैलवेयर लोडर और ड्रॉपर पेलोड है जिसे Embarcadero Delphi 10/11 (Native x86/x64) with AutoIt v3 Stagers का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTP/HTTPS with Custom Base64 Character Set Substitution & Rotating XOR Keys) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTP/HTTPS with Custom Base64 Character Set Substitution & Rotating XOR Keys आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).