01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Roslyn C# Compiler (csc.exe)",
  "runtime": ".NET Common Language Runtime (CLR 4.0.30319)",
  "binary_footprint": "Ultra-lightweight core PE32 (.NET assembly), typ. 30 KB - 65 KB uncompressed stub",
  "stub_size": "45,056 bytes (vanilla core stub without embedded plugins)",
  "packer_obfuscation": "ConfuserEx, KoiVM, proprietary DCRat Crypter, or layered PowerShell/batch loaders",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "Program.Main() -> Decrypt internal configuration strings -> Mutex initialization -> Anti-Analysis & Anti-CIS verification -> Persistence installation -> Dynamic Plugin Manager check-in loop -> Fetch and in-memory load of plugins via Assembly.Load(byte[])",
  "technical_summary": "DCRat (DarkCrystal RAT) is an affordable, highly modular commercial Remote Access Trojan written in C# (.NET). Operating on a modular micro-kernel architecture, the core client remains extremely lightweight (~40 KB) and downloads task-specific pre-compiled .NET assembly plugins dynamically from a PHP web backend. Plugins execute entirely in memory via reflection, delivering capabilities ranging from credential stealing (Chromium, Gecko, crypto wallets) and HVNC to crypto clipping, keylogging, and DDoS attacks."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "DarkCrystal Studio Desktop Application & PHP Web Admin Panel",
  "builder_tabs_options": [
    {
      "tab": "C2 & Network Settings",
      "options": [
        "C2 URL: Endpoint URL pointing to gate.php on the operator's PHP web server",
        "Encryption Key: Pre-shared passphrase string deriving the AES encryption key",
        "Campaign Tag: Identification string grouping bots inside the web administration dashboard",
        "Connection Delay: Sleep interval (seconds) before first network beacon to defeat sandbox timeouts"
      ]
    },
    {
      "tab": "Plugin Selection & Bundling",
      "options": [
        "Stealer.dll: Extracts browser passwords, cookies, credit cards, Discord tokens, and crypto wallets",
        "Surveillance.dll: Desktop screen streaming, webcam recorder, and low-level keylogger",
        "Clipper.dll: Memory and clipboard monitor replacing cryptocurrency addresses via regex matching",
        "HVNC.dll: Spawns hidden virtual desktop session for covert browser navigation"
      ]
    },
    {
      "tab": "Evasion & Persistence",
      "options": [
        "Anti-CIS: Checks system keyboard layout and language; terminates if Russian/CIS locales are detected",
        "Anti-Analysis: Detects VMware, VirtualBox, QEMU, debuggers, and sandbox environments",
        "Process Protection: P/Invokes RtlSetProcessIsCritical to prevent termination via Task Manager",
        "Startup Persistence: Configures Task Scheduler jobs (/create) or CurrentVersion\\Run registry entries"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "Index 0",
      "type": "string",
      "field": "Config[0]",
      "description": "Gate URL (e.g., https://example.com/gate.php)"
    },
    {
      "offset": "Index 1",
      "type": "string",
      "field": "Config[1]",
      "description": "Pre-shared encryption key used in PBKDF2 key derivation"
    },
    {
      "offset": "Index 2",
      "type": "string",
      "field": "Config[2]",
      "description": "Campaign identification tag"
    },
    {
      "offset": "Index 3",
      "type": "string",
      "field": "Config[3]",
      "description": "Mutex string identifier"
    },
    {
      "offset": "Index 4",
      "type": "int",
      "field": "Config[4]",
      "description": "Initial execution delay in seconds"
    },
    {
      "offset": "Index 5",
      "type": "bool",
      "field": "Config[5]",
      "description": "Anti-CIS execution guard toggle"
    },
    {
      "offset": "Index 6",
      "type": "bool",
      "field": "Config[6]",
      "description": "Process protection watchdog toggle"
    }
  ],
  "payload_generation_flags": [
    "Obfuscation: Integrated string encryption and control flow flattening via Roslyn compiler integration",
    "Icon & Assembly Cloning: Clones PE version headers, company name, copyright, and icon from legitimate software",
    "Plugin Inlining: Allows operator to either embed selected plugins inside the core stub or fetch them dynamically"
  ],
  "operator_commands": [
    "load_plugin <url>: Instructs core to download and dynamically reflectively load a .NET plugin assembly",
    "steal_credentials: Triggers Stealer plugin to harvest browser databases and wallet files",
    "start_stream: Launches real-time screen capture stream via HTTP POST or WebSocket",
    "clip_address <regex> <addr>: Configures clipboard cryptocurrency replacer parameters",
    "open_hvnc: Initiates Hidden Virtual Network Computing session on secondary desktop",
    "shell_exec <cmd>: Executes shell command through hidden cmd.exe or powershell.exe process"
  ],
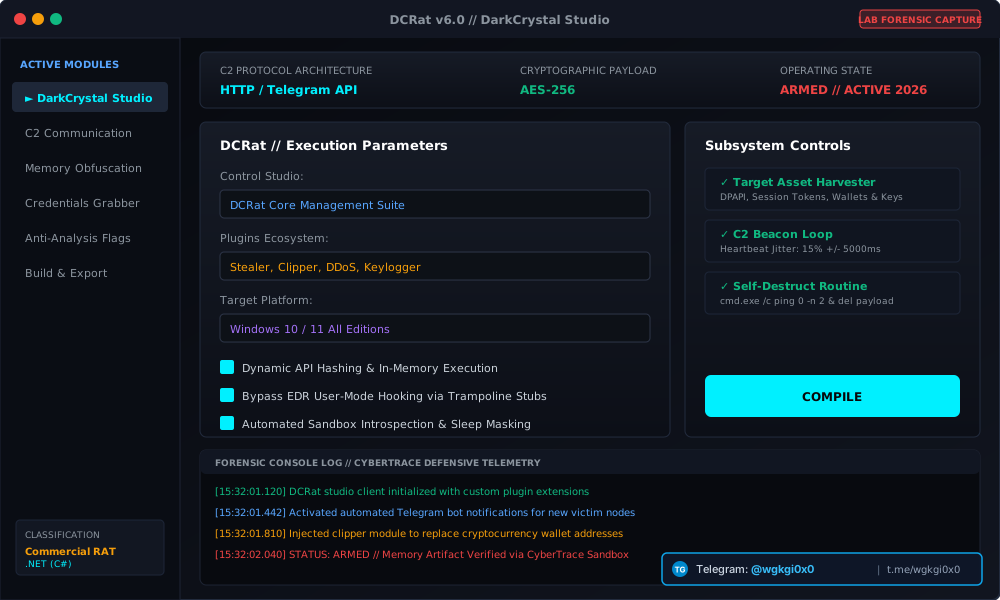
  "interface_telemetry_analysis": "DarkCrystal Studio provides a centralized workbench featuring an integrated plugin marketplace, builder configurator, victim management table, and log viewing modules."
}struct DCRat_(DarkCrystal_RAT)_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Modular Reflection & In-Memory Plugin Loading: Core executable drops and installs persistence -> Connects to gate.php -> Receives tasking array containing encrypted plugin binaries -> Core decrypts payload into raw byte[] array -> Invokes System.Reflection.Assembly.Load(byte[]) -> Discovers module entry point via reflection -> Instantiates and invokes plugin methods without writing DLLs to the filesystem.",
  "ntapi_functions": [
    "ntdll!RtlSetProcessIsCritical",
    "kernel32!VirtualAlloc",
    "user32!OpenDesktopA",
    "user32!CreateDesktopA",
    "user32!SwitchDesktop",
    "user32!SetWindowsHookExW"
  ],
  "plugin_manager": "Dynamic Assembly Architecture: The DCRat core maintains an internal registry of loaded modules (Dictionary<string, object>). When the C2 tasks the agent with a specific operation (e.g., stealing browser cookies or launching HVNC), the core checks if the corresponding plugin assembly is already present in memory. If absent, it issues an HTTP GET request to download the encrypted assembly bytes, decrypts them with AES-CBC, and executes Assembly.Load(). This allows the base payload to maintain a minimal detection footprint.",
  "anti_cis_mechanics": "Geographic Evasion: Checks system locale and active keyboard layout using InputLanguage.CurrentInputLanguage.Culture. If culture identifiers match Russian (ru-RU), Belarusian (be-BY), Ukrainian (uk-UA), or Kazakh (kk-KZ), the client immediately self-terminates and removes its dropped binary, avoiding scrutiny from CIS law enforcement.",
  "anti_analysis": "Inspects process names against analysis tools (x64dbg, dnSpy, Fiddler, Wireshark, ProcessHacker); checks WMI Win32_ComputerSystem for virtualization strings (VMware, VirtualBox, KVM).",
  "persistence_mechanics": "Executes schtasks.exe /create /tn \"SecurityUpdate\" /tr <path> /sc onlogon /rl highest, or writes to HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the DCRat (DarkCrystal RAT) binary:
[ "Stealer.dll: Chromium and Gecko browser credential extraction, DPAPI master key decryption, cryptocurrency wallet harvesting", "Surveillance.dll: Desktop screen capture streaming, microphone recording, webcam capture, low-level keylogger", "Clipper.dll: Memory and clipboard monitor replacing cryptocurrency addresses (BTC, ETH, LTC, Monero, TON)", "HVNC.dll: Hidden Desktop session (CreateDesktopA) enabling covert browser navigation and session hijacking", "ProcessManager.dll: Viewing, suspending, terminating processes and file system exploration" ]
[ "HTTP / HTTPS POST requests to PHP backend (gate.php) disguised as web analytics", "AES-128-CBC / AES-256-CBC encrypted communication payloads encoded in Base64", "WebSocket persistent bi-directional communication channels for low-latency streaming" ]
[ "Anti-CIS localization checks aborting execution on Russian/CIS systems", "Critical process watchdog (RtlSetProcessIsCritical) forcing BSOD on termination", "In-memory dynamic assembly loading with zero disk footprint for operational plugins" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "HTTP POST requests directed to /gate.php carrying urlencoded or raw data parameters. Response bodies contain JSON structured task arrays.",
  "serialization": "JSON serialized task and telemetry objects encrypted with AES-CBC and encoded via Base64.",
  "handshake": "Client gathers hardware ID (HWID), computer name, OS, and active plugins -> Encrypts JSON string with AES-CBC using session key -> Submits HTTP POST to gate.php -> Server validates parameters and returns task list.",
  "cryptography": "AES-128-CBC or AES-256-CBC with PKCS7 padding; encryption key derived from pre-shared string via PBKDF2 or SHA256 hashing.",
  "packet_types": [
    "gate.php?action=check: Initial check-in and bot status update",
    "gate.php?action=get_tasks: Command polling frame querying server queue",
    "gate.php?action=response: Exfiltration frame transmitting command output or stolen credential archives"
  ],
  "traffic_signature": "HTTP POST traffic with application/x-www-form-urlencoded payloads containing large Base64 strings sent to PHP endpoints."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_DCRat_DarkCrystal_Core {
    meta:
        description = "Detects DCRat (DarkCrystal) core client stubs, plugin manager reflection patterns, and configuration decryptors"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        reference = "TF-035"
    strings:
        $plugin_load = "Assembly.Load"
        $dcrat_str1 = "DarkCrystal"
        $dcrat_str2 = "DCRat"
        $gate_param = "gate.php"
        $anti_cis = "InputLanguage"
    condition:
        uint16(0) == 0x5A4D and ($plugin_load and ($dcrat_str1 or $dcrat_str2 or $gate_param) and $anti_cis)
}title: DCRat HTTP Gate Communication to PHP Backend
id: 3c2e1a9b-4819-4f2a-8c19-5a5e01b23847
status: stable
description: Detects suspicious HTTP POST requests directed to gate.php endpoints carrying Base64 encoded payload parameters.
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
product: zeek
service: http
detection:
selection:
method: 'POST'
uri|endswith: '/gate.php'
condition: selection
fields:
- id.orig_h
- id.resp_h
- uri
- user_agent
falsepositives:
- Legitimate administrative applications with identically named gate scripts
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
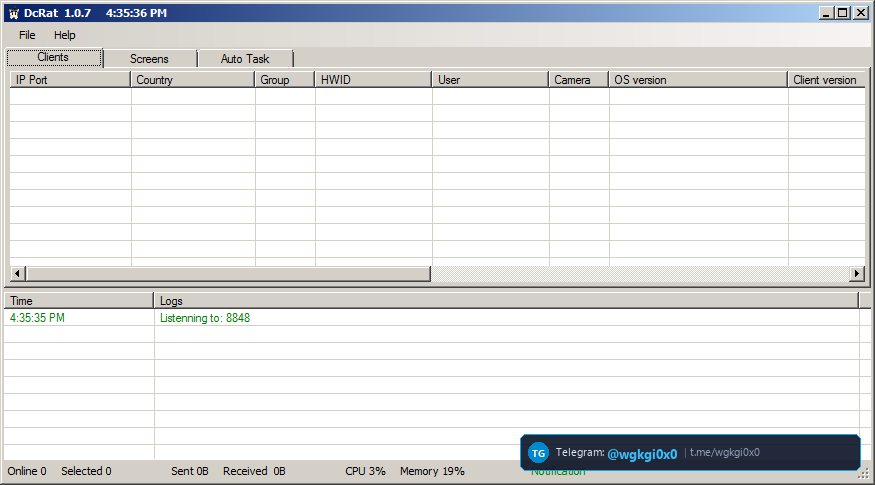
Modern builder interface displaying modular plugin selections, stealer configurations, and obfuscation options.
Web-based administration console tracking active victim nodes, geolocations, and extracted credentials.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and HTTP / Web Panel via PHP Backend command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
DCRat (DarkCrystal RAT) (RAT)
Modular .NET commercial Remote Access Trojan featuring a lightweight core micro-kernel, in-memory plugin reflection, and PHP web backend C2.
C2 Architecture: {'framing': 'HTTP POST requests directed to /gate.php carrying urlencoded or raw data parameters. Response bodies contain JSON structured task arrays.', 'serialization': 'JSON serialized task and telemetry objects encrypted with AES-CBC and encoded v
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ DCRat (DarkCrystal RAT) (RAT)
Детальный технический анализ DCRat (DarkCrystal RAT) — это Троян удаленного доступа (RAT), разработанный на стеке Roslyn C# Compiler targeting .NET Framework 4.5 or 4.8. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTP / HTTPS POST with AES-128-CBC or AES-256-CBC and Base64 encoding; optional WebSocket persistent connection) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTP / HTTPS POST with AES-128-CBC or AES-256-CBC and Base64 encoding; optional WebSocket persistent connection, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
DCRat (DarkCrystal RAT) (RAT) विश्लेषण
DCRat (DarkCrystal RAT) एक परिष्कृत रिमोट एक्सेस ट्रोजन (RAT) है जिसे Roslyn C# Compiler targeting .NET Framework 4.5 or 4.8 का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTP / HTTPS POST with AES-128-CBC or AES-256-CBC and Base64 encoding; optional WebSocket persistent connection) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTP / HTTPS POST with AES-128-CBC or AES-256-CBC and Base64 encoding; optional WebSocket persistent connection आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).