01 | Tool Specifications & Architectural Profile
{
  "compiler": "C# .NET Builder orchestrating apktool, baksmali/smali, zipalign, and apksigner with custom DEX crypter modules",
  "runtime": "Android Runtime (ART) / Dalvik VM",
  "binary_footprint": "Staged APK Dropper (800 KB - 2 MB) unpacking a core RAT DEX/APK payload (1.5 MB - 5 MB)",
  "stub_size": "1,620,000 bytes (core payload APK before dropper wrapping and asset encryption)",
  "packer_obfuscation": "Staged APK Dropper architecture (bypassing Android 13+ Restricted Settings via session-based PackageInstaller or DexClassLoader), string encryption, and manifest attribute obfuscation",
  "subsystem": "Android Application Framework (AccessibilityService + SYSTEM_ALERT_WINDOW + NotificationListenerService)",
  "entry_point_flow": "Dropper Activity -> Unpacks & loads encrypted payload from assets/ -> Prompts for AccessibilityService -> Auto-grants SYSTEM_ALERT_WINDOW, SMS, and Storage permissions -> Starts foreground service -> Establishes dual TCP connections to C2 Ports 7771 and 7772",
  "technical_summary": "EagleSpy (circulating in V3 Ultimate and V4 releases) is a specialized Android RAT and financial fraud suite heavily adapted from the CraxsRAT/SpyMax lineage. Engineered with a modern C# WinForms dashboard, EagleSpy integrates native modules specifically tailored for cryptocurrency theft and banking takeover: an automated seed-phrase overlay injector targeting MetaMask, Trust Wallet, and Binance; a dedicated Google Authenticator 2FA token scraper (G-Auth Stealer); a multi-chain clipboard clipper; and a staged APK Dropper builder designed to bypass Google Play Protect and Android 13/14 security restrictions."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "GUI Builder / Operator Console",
  "builder_tabs_options": [
    {
      "tab": "Home & Quick Option",
      "options": [
        "Live Client Grid: Displays connected devices with real-time screen preview thumbnails",
        "Quick Option Tiles: One-click triggers for Screen Control, Live Screen, Keylogger, Lock Screen, Screen Reader, Browser Monitor, File Manager, and SMS Manager",
        "Banking / Crypto Injection: Instant deployment of phishing overlays for banking apps and cryptocurrency wallets",
        "G-Auth Stealer: Dedicated extraction trigger for Google Authenticator 2FA codes"
      ]
    },
    {
      "tab": "Build (APK Builder)",
      "options": [
        "Host IP / DNS & Dual Ports: Configures primary C2 address and dual TCP ports (default 7771 and 7772)",
        "App Identity: Custom App Name, Package Name, Version, and Icon",
        "Telegram Bot Bridge: Optional Telegram Bot Token and Chat ID for instant new-victim and seed-phrase alerts",
        "Anti-Delete / Super Protection: Enables Accessibility-based Settings blocking and icon hiding"
      ]
    },
    {
      "tab": "Dropper (APK Dropper)",
      "options": [
        "Generate Staged Dropper: Wraps the compiled EagleSpy APK inside a clean loader APK to evade static AV and Android 13 Restricted Settings",
        "Lure Template: Selects fake update UI (Google Play, Chrome, System Update) displayed while installing the secondary payload"
      ]
    },
    {
      "tab": "Tools / Clipper / Injector",
      "options": [
        "Crypto Clipper Addresses: Pre-loads operator BTC, ETH, TRC-20 USDT, BNB, and SOL wallet addresses for automatic clipboard replacement",
        "Target Wallet Overlays: Selects HTML/WebView seed-phrase phishing screens for Trust Wallet, MetaMask, Phantom, and Binance",
        "Lockscreen Phishing: Configures custom PIN/Pattern/Password lockscreen overlay"
      ]
    },
    {
      "tab": "Encrypt",
      "options": [
        "APK Crypter: Applies DEX class encryption, random Smali junk code insertion, and ZIP structure manipulation"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "Config.HOST",
      "field": "Host",
      "type": "String (Encrypted)",
      "description": "Primary C2 IP address or domain name"
    },
    {
      "offset": "Config.PORT_CMD",
      "field": "CommandPort",
      "type": "String / Int",
      "description": "Primary command and control TCP port (default 7771)"
    },
    {
      "offset": "Config.PORT_MEDIA",
      "field": "StreamPort",
      "type": "String / Int",
      "description": "High-throughput media and screen streaming TCP port (default 7772)"
    },
    {
      "offset": "Config.TG_TOKEN",
      "field": "TelegramToken",
      "type": "String",
      "description": "Telegram Bot API token for out-of-band victim notifications"
    },
    {
      "offset": "Config.CLIPPER_WALLETS",
      "field": "ClipperMap",
      "type": "JSON / String Array",
      "description": "Configured cryptocurrency replacement addresses (BTC, ETH, USDT-TRC20)"
    }
  ],
  "payload_generation_flags": [
    "Dual-Socket Mode: Port 7771 (Control) + Port 7772 (HVNC/Camera/Audio Stream)",
    "Dropper Staging: Session-based PackageInstaller or DexClassLoader asset unpacking",
    "Overlay Assets: Bundled HTML/CSS/JS banking and crypto wallet templates"
  ],
  "operator_commands": [
    "ScreenControl / ScreenReader: Initiates HVNC live screen streaming and remote Accessibility gesture injection",
    "CryptoInjection: Triggers immediate WebView overlay requesting 12/24-word recovery seed phrases on target wallet apps",
    "BankingInjection: Deploys targeted credential harvesting overlay matching installed mobile banking packages",
    "GAuthSteal: Launches or monitors com.google.android.apps.authenticator2 and scrapes active TOTP codes via AccessibilityNodeInfo",
    "LockScreenOverlay: Projects full-screen PIN/Pattern capture view to harvest device unlock credentials",
    "ClipperToggle: Activates or updates background regex clipboard replacement for cryptocurrency addresses",
    "FileManager / SMSManager: Full filesystem access and real-time SMS OTP interception",
    "AdminRight / DozeOff: Forces DeviceAdmin activation and battery optimization whitelisting"
  ],
  "interface_telemetry_analysis": "The EagleSpy V4 operator console features a left-hand navigation sidebar (Home, Logs, Build, Dropper, Tools, Encrypt, Injector, Settings) and a central 'Quick Option' dashboard equipped with 24 action tiles. A bottom status bar tracks connected client counts, active dual-port listeners ('Port: 7771, 7772'), and real-time upload/download throughput ('Sent / Received'). Selecting a connected handset opens a side-by-side live phone bezel preview with interactive remote touch controls."
}struct EagleSpy_(V3_Ultimate_/_V4)_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Staged Dropper APK installed -> Uses PackageInstaller.Session (setting InstallScenario) or DexClassLoader to deploy core payload -> AccessibilityService enabled via social engineering prompt -> Auto-clicks runtime permissions and SYSTEM_ALERT_WINDOW -> Foreground window monitor detects io.metamask or com.wallet.crypto.trustapp -> Injects WebView overlay or scrapes AccessibilityNodeInfo text trees -> Exfiltrates over TCP Port 7771/7772 and Telegram Bot API.",
  "ntapi_functions": [
    "android.accessibilityservice.AccessibilityService!onAccessibilityEvent",
    "android.accessibilityservice.AccessibilityService!dispatchGesture",
    "android.view.WindowManager!addView",
    "android.webkit.WebView!addJavascriptInterface",
    "android.content.ClipboardManager!addPrimaryClipChangedListener",
    "android.content.pm.PackageInstaller!createSession",
    "android.media.projection.MediaProjection!createVirtualDisplay"
  ],
  "process_hollowing_target": "Dropper host process or persistent foreground service masquerading as Google Play Services / System UI",
  "persistence_mechanics": [
    "AccessibilityService Lifecycle Binding: System automatically maintains and restarts the bound Accessibility service",
    "BroadcastReceiver Resurrection: Hooks BOOT_COMPLETED, USER_PRESENT, and custom restart intents fired on Service.onDestroy()",
    "Battery Optimization Exemption: Programmatically requests and auto-approves ACTION_REQUEST_IGNORE_BATTERY_OPTIMIZATIONS",
    "Anti-Uninstall Watchdog: Monitors Settings activities via Accessibility events and immediately navigates away when App Info or Device Admin revocation screens are detected"
  ],
  "evasion_hooks": [
    "Session-Based Dropper Installation: Uses PackageInstaller.SessionParams to bypass Android 13/14 'Restricted Settings' blocks on AccessibilityService for sideloaded APKs",
    "Black-Screen Curtain: Covers the physical display with an opaque SYSTEM_ALERT_WINDOW view while performing automated wallet transfers in the background",
    "Notification Suppression: Uses NotificationListenerService to intercept and dismiss incoming bank transfer alerts and security notifications"
  ],
  "anti_analysis": [
    "Emulator & Sandbox Fingerprinting: Checks Build.HARDWARE, Build.PRODUCT, sensor availability, and QEMU system properties",
    "Encrypted Asset Staging: Stores the functional RAT DEX and HTML injection templates as AES/XOR-encrypted blobs inside the assets/ directory",
    "ZIP & Manifest Structure Tampering: Injects malformed resource IDs and corrupted ZIP header flags to hinder static analysis in JADX and Apktool"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the EagleSpy (V3 Ultimate / V4) binary:
[ "Crypto Seed Phrase Overlay Injection: Renders pixel-accurate WebView overlays over Trust Wallet, MetaMask, Binance, and Phantom demanding 12/24-word mnemonic phrases", "Banking Credential Overlays: Dynamically loads HTML login forms paired with JavascriptInterface bridges to capture mobile banking usernames, passwords, and PINs", "G-Auth Stealer (Google Authenticator Scraper): Traverses AccessibilityNodeInfo trees inside com.google.android.apps.authenticator2 to exfiltrate 6-digit TOTP codes in real time", "Device Lockscreen Harvester: Projects a deceptive lockscreen overlay capturing numerical PINs, alphanumeric passwords, or unlock pattern sequences", "Browser & Social Media Scraping: Monitors Chrome, WebView, and social apps via Accessibility text extraction" ]
[ "Dual-Mode Screen Capture: Supports both pixel-based MediaProjection streaming and tree-based Accessibility Screen Reader reconstruction", "Offline & Live Keylogger: Records all text inputs, focused package names, and clipboard additions", "Stealth Camera & Microphone Streaming: Captures live front/back camera video and ambient microphone audio over dedicated TCP Port 7772", "SMS & Call Log Monitoring: Intercepts incoming SMS messages and queries call history databases" ]
[ "HVNC Interactive Remote Control: Translates operator mouse clicks and drags on the desktop phone preview into dispatchGesture() calls on the victim handset", "Global Navigation Control: Remotely triggers Home, Back, Recents, Notifications, and Quick Settings actions", "Remote App Launcher: Enumerates installed applications and forces target banking or crypto apps to the foreground" ]
[ "Remote File Explorer: Full directory traversal, file download, upload, and deletion across internal and external storage", "Gallery & Screenshot Harvester: Exfiltrates stored screenshots (frequently containing saved recovery phrases or QR codes)" ]
[ "Multi-Chain Clipboard Clipper: Monitors ClipboardManager and substitutes wallet addresses matching Bitcoin, Ethereum (0x...), TRON/USDT (T...), and BNB patterns" ]
[ "Remote Screen Lock & Blackout: Locks the handset screen or displays a fake system update overlay to block user intervention during fraud", "Ringer & Notification Muting: Silences device audio streams to hide transaction confirmation chimes" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Dual-socket TCP framing: Port 7771 carries delimiter-framed, GZIP-compressed command/response packets; Port 7772 streams length-prefixed binary media and HVNC screen frames",
  "serialization": "Custom string-delimited key-value tokens with Base64-encoded JSON/binary payloads and out-of-band HTTPS POST webhook notifications to api.telegram.org",
  "handshake": "Stub connects to TCP Port 7771 -> Transmits encrypted client registration packet (HWID, Model, OS, Country, Installed Crypto/Bank Apps list) -> Opens secondary stream socket on TCP Port 7772 when live screen, camera, or audio modules are invoked",
  "cryptography": "GZIP compression combined with static-key AES-CBC or XOR obfuscation on TCP socket streams; TLS 1.2/1.3 for optional Telegram Bot API exfiltration",
  "packet_types": [
    {
      "header": "CMD_INFO / PING",
      "payload": "Device telemetry, active foreground package, battery state, and installed target wallet flags",
      "direction": "Client -> Server (Port 7771)"
    },
    {
      "header": "INJ_CRYPTO / INJ_BANK",
      "payload": "Target package identifier, HTML overlay template bytes, or captured seed phrase / login credentials",
      "direction": "Bidirectional (Port 7771)"
    },
    {
      "header": "GAUTH_DUMP",
      "payload": "Scraped Google Authenticator account labels and current 6-digit TOTP tokens",
      "direction": "Client -> Server (Port 7771)"
    },
    {
      "header": "STREAM_SCR / HVNC",
      "payload": "Compressed JPEG screen frames or serialized UI node coordinates",
      "direction": "Client -> Server (Port 7772)"
    },
    {
      "header": "GESTURE_CMD",
      "payload": "Touch X/Y coordinates, swipe vectors, or text injection strings",
      "direction": "Server -> Client (Port 7771)"
    }
  ],
  "traffic_signature": "Simultaneous outbound TCP connections from a single Android handset to the same remote IP on adjacent ports 7771 and 7772, often accompanied by HTTPS requests to api.telegram.org/bot<token>/sendMessage."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_EagleSpy_APK_DEX {
    meta:
        description = "Detects EagleSpy V3/V4 Android RAT payloads and staged droppers via overlay injection, clipper, and G-Auth scraper markers"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-30"
        family = "EagleSpy"
        platform = "Android"
    strings:
        $dex = { 64 65 78 0A 30 33 ?? 00 }
        $s1 = "EagleSpy" ascii nocase
        $s2 = "com.google.android.apps.authenticator2" ascii
        $s3 = "io.metamask" ascii
        $s4 = "com.wallet.crypto.trustapp" ascii
        $a1 = "addPrimaryClipChangedListener" ascii
        $a2 = "dispatchGesture" ascii
        $a3 = "addJavascriptInterface" ascii
        $a4 = "TYPE_APPLICATION_OVERLAY" ascii
    condition:
        $dex at 0 and
        (($s1 and 2 of ($a*)) or (2 of ($s2, $s3, $s4) and 3 of ($a*)))
}title: EagleSpy Dual-Port Listener and APK Dropper Builder Execution
id: 5e6f7a8b-1c2d-4e3f-9a8b-7c6d5e4f3a2b
status: stable
description: Identifies execution of the EagleSpy Windows operator console or its child APK compilation processes.
author: CyberTrace Defense Engineering
date: 2026/10/30
references:
- https://attack.mitre.org/Mobile/techniques/T1516/
tags:
- attack.execution
- attack.command_and_control
- attack.t1071
logsource:
category: process_creation
product: windows
detection:
selection_binary:
Image|endswith:
- '\EagleSpy.exe'
- '\EagleSpyV4.exe'
- '\EagleSpy_V3.exe'
selection_child:
ParentImage|endswith:
- '\EagleSpy.exe'
- '\EagleSpyV4.exe'
Image|endswith:
- '\java.exe'
- '\apktool.exe'
condition: selection_binary or selection_child
falsepositives:
- Malware analysis sandboxes detonating EagleSpy builder packages.
level: critical07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
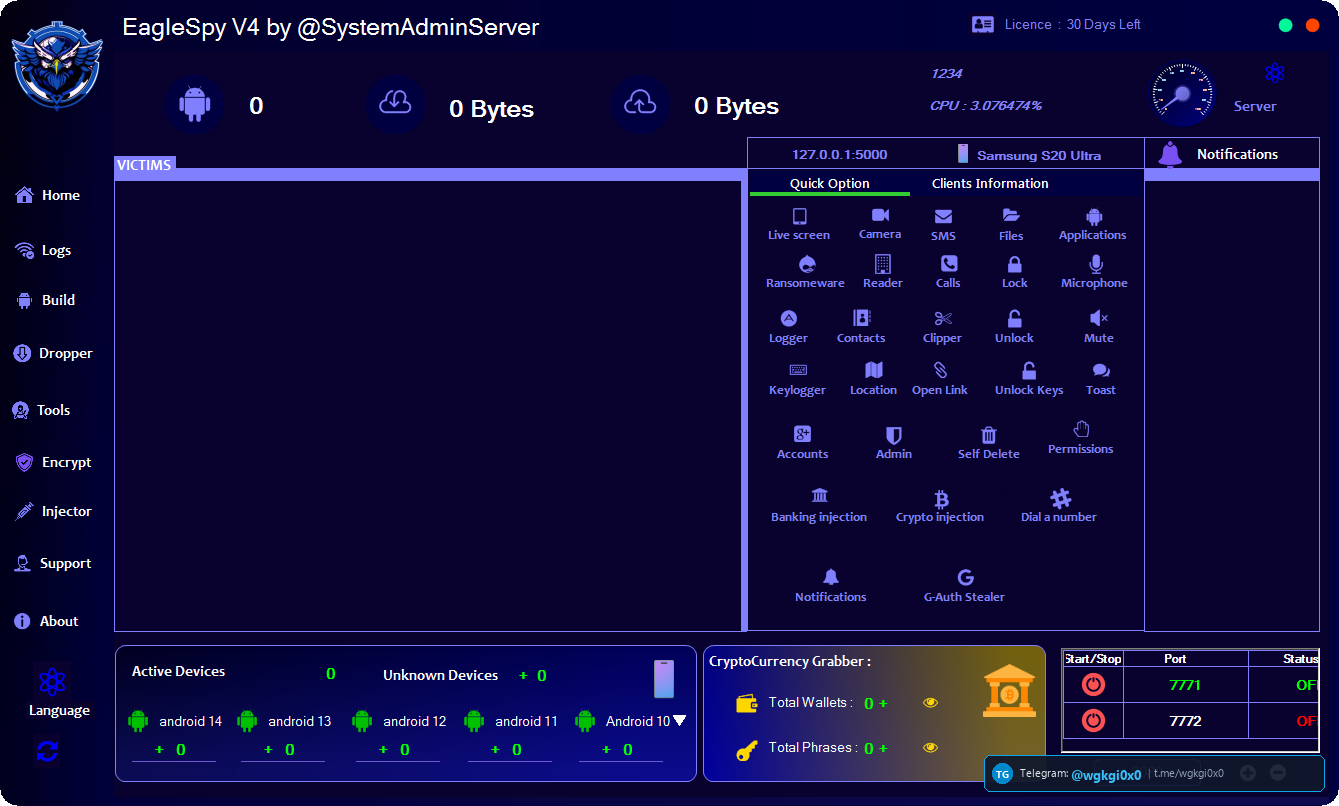
EagleSpy V4 WinForms controller featuring Quick Option surveillance grid, Banking/Crypto injection triggers, G-Auth Stealer, and dual-port listener (7771/7772).
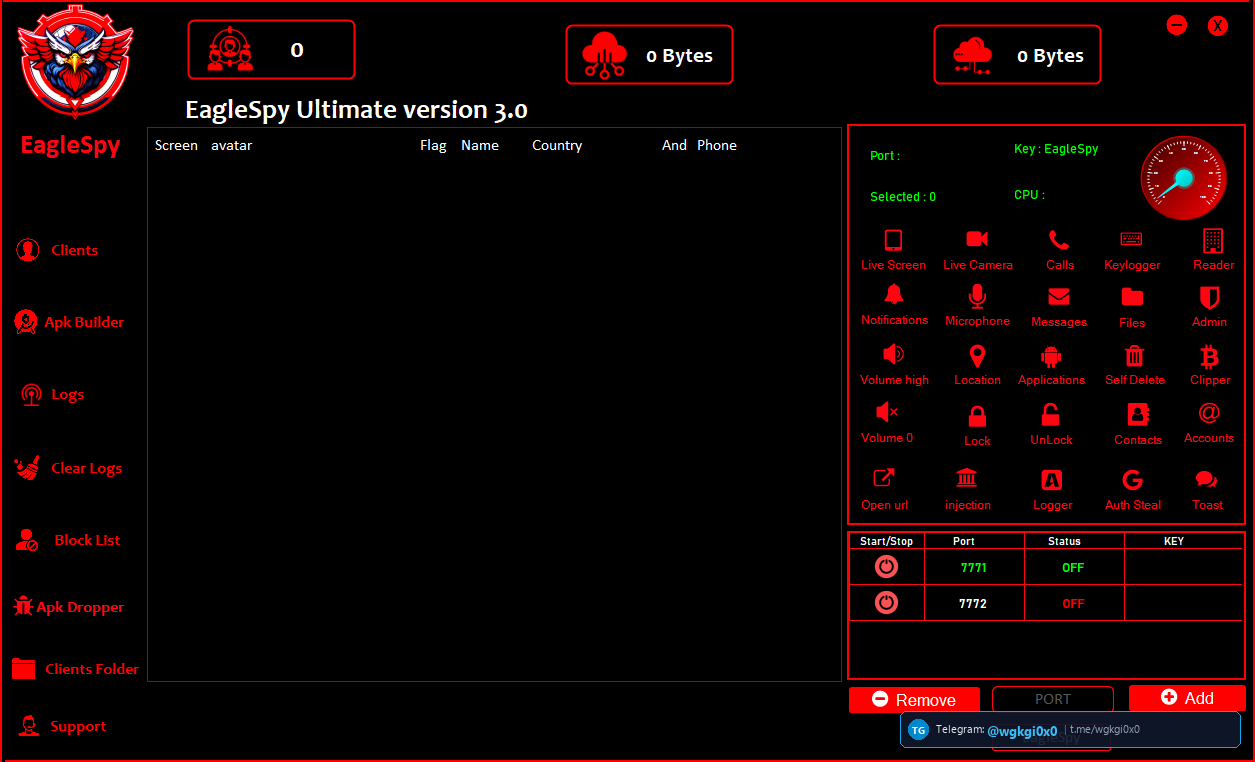
EagleSpy v3.0 operator console showing APK Builder, APK Dropper, Clipper, Auth Steal, and live device management.
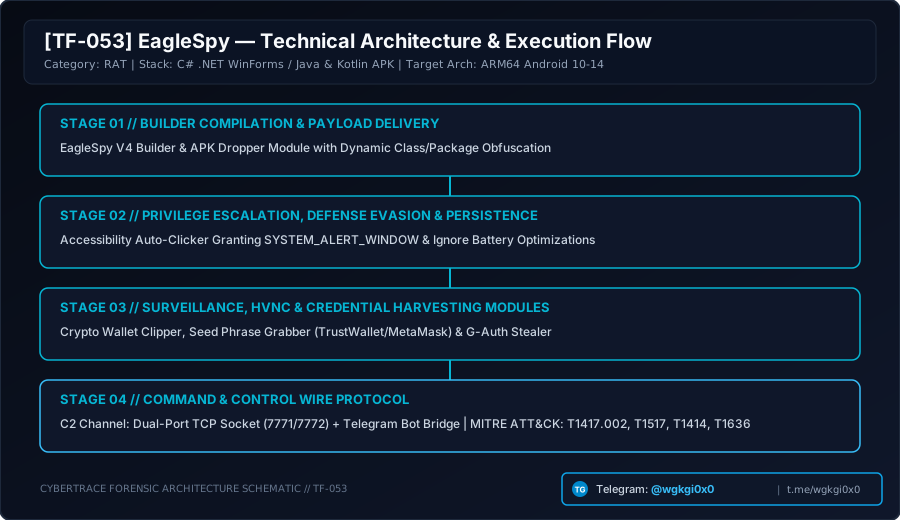
Forensic schematic mapping EagleSpy V4 dropper staging, Accessibility auto-clicker permission escalation, crypto wallet overlay injection, and dual-port TCP C2.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
EagleSpy (V3 Ultimate / V4) (RAT)
Commercial Android RAT and financial fraud framework featuring a dual-port (7771/7772) C# console, staged APK dropper builder, crypto seed-phrase overlay injector, and Google Authenticator scraper.
C2 Architecture: {'framing': 'Dual-socket TCP framing: Port 7771 carries delimiter-framed, GZIP-compressed command/response packets; Port 7772 streams length-prefixed binary media and HVNC screen frames', 'serialization': 'Custom string-delimited key-value tokens wit
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ EagleSpy (V3 Ultimate / V4) (RAT)
Детальный технический анализ EagleSpy (V4 / Ultimate v3.0) — Android-трояна удаленного доступа (RAT) и крипто-стилера. В отчете исследуются архитектура двухэтапного APK-дроппера, автоматическое предоставление разрешений через Accessibility auto-clicker, кража сид-фраз из MetaMask, TrustWallet и Binance с помощью фишинговых оверлеев, а также перехват кодов Google Authenticator.
Архитектура C2: Двухканальный TCP-протокол (порты 7771 для команд и 7772 для потокового видео/HVNC) с шифрованием и сжатием пакетов.
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
EagleSpy (V3 Ultimate / V4) (RAT) विश्लेषण
EagleSpy (V4 / Ultimate v3.0) एक उन्नत Android रिमोट एक्सेस ट्रोजन (RAT) और क्रिप्टोकरेंसी स्टीलर है। इस तकनीकी विश्लेषण में APK ड्रॉपर स्टेजिंग, Accessibility ऑटो-क्लिकर विशेषाधिकार वृद्धि, क्रिप्टो वॉलेट सीड-फ्रेज़ ओवरले इंजेक्शन और Google Authenticator 2FA चोरी तंत्र का विवरण दिया गया है।
C2 संचार: कमांड डिस्पैच (पोर्ट 7771) और लाइव HVNC/कैमरा स्ट्रीमिंग (पोर्ट 7772) के लिए डुअल-पोर्ट TCP सॉकेट C2 प्रोटोकॉल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).