01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C++ (MSVC x86, CRT-less /NODEFAULTLIB)",
  "runtime": "Native Win32 subsystem executing direct NTAPI syscalls",
  "binary_footprint": "Single PE32 executable, typ. 28 KB - 48 KB unpacked core payload",
  "stub_size": "34,816 bytes (unpacked core), delivered via 250 KB - 900 KB multi-stage crypters (NSIS, VB6, or .NET)",
  "packer_obfuscation": "Custom polymorphic crypter stagers, string hashing (DJB2/CRC32), encrypted imports, and self-modifying code stubs",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "Crypter stager -> Decrypts Stage 2 shellcode -> Shellcode maps clean ntdll.dll from \\KnownDlls\\ntdll.dll -> Overwrites .text section to strip EDR hooks -> Injects into 32-bit intermediate process -> Spawns target host (svchost.exe / explorer.exe) -> Installs API hooks in browser memory -> Initiates decoy HTTP beaconing loop",
  "technical_summary": "Formbook (and its successor XLoader) is an advanced C/Assembly information stealer engineered specifically for form grabbing, keystroke interception, and credential harvesting. It executes without standard C runtime libraries, directly resolving Win32 APIs via PEB traversal and export table hashing. Formbook's evasion architecture includes reading a clean ntdll.dll copy from disk to unhook user-mode monitoring agents, performing nested multi-process injection, and cloaking its real C2 traffic beneath bursts of HTTP requests sent to dozens of legitimate decoy domains."
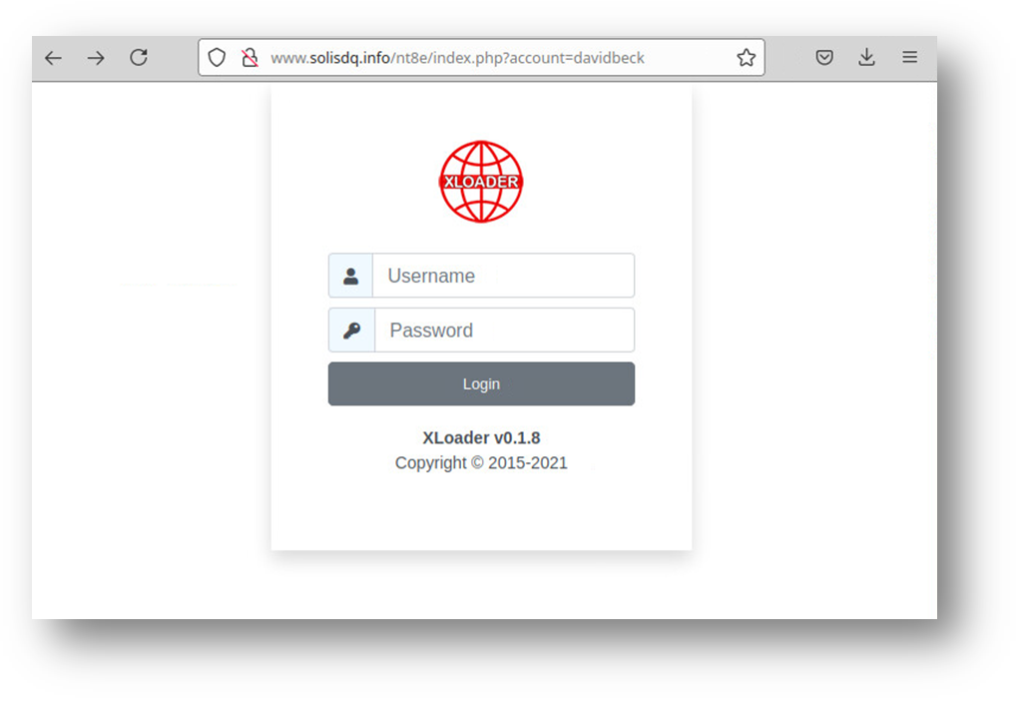
}02 | Operator Interface & Configuration Struct Model
{
  "type": "Web Management Panel (PHP/MySQL) & Windows Payload Builder",
  "builder_tabs": [
    "Server Settings (Decoy domain list, real C2 URL, campaign identifier)",
    "Installation Options (Persistence registry keys, dropped file paths, run triggers)",
    "Stealer Modules (Browser hook enablement, clipboard monitoring, keylogger toggles)",
    "Network & Evasion (Decoy request count, sleep intervals, process injection targets)"
  ],
  "config_fields": [
    {
      "offset": "0x0010",
      "field": "CampaignID",
      "type": "ASCII String",
      "description": "Operator campaign tag identifier"
    },
    {
      "offset": "0x0030",
      "field": "DecoyCount",
      "type": "DWORD",
      "description": "Number of decoy domains generated per cycle (typically 64 or 128)"
    },
    {
      "offset": "0x0034",
      "field": "DecoyDomains",
      "type": "Encrypted String Array",
      "description": "List of decoy domain names used to mask C2 traffic"
    },
    {
      "offset": "0x0180",
      "field": "RealC2Index",
      "type": "DWORD",
      "description": "Zero-based index of the authentic C2 server within the domain array"
    },
    {
      "offset": "0x0184",
      "field": "RC4KeySalt",
      "type": "Byte Array (16 bytes)",
      "description": "Salt parameter used for key derivation in network encryption"
    },
    {
      "offset": "0x01A0",
      "field": "SleepInterval",
      "type": "DWORD",
      "description": "Beaconing interval in seconds between exfiltration cycles"
    }
  ],
  "payload_generation_flags": [
    "Target Subsystem: Win32 GUI",
    "Unhooking Mode: Active (\\KnownDlls\\ntdll.dll replacement)",
    "Form Grabber Target Matrix: Chromium, Gecko, WebKit, WinINet",
    "Traffic Cloaking: 64 Decoy Requests per Exfiltration Burst"
  ],
  "operator_commands": [
    "cmd /c: Executes arbitrary shell commands via cmd.exe pipe",
    "download: Fetches secondary binary from operator URL and executes",
    "run: Launches executable file on target endpoint",
    "reboot: Triggers immediate Windows system reboot",
    "shutdown: Initiates machine shutdown",
    "uninstall: Unhooks API intercepts, removes persistence keys, and wipes binary footprint"
  ],
  "interface_telemetry_analysis": "The operator interface is hosted on a LAMP stack (Linux/Apache/MySQL/PHP). The administration dashboard provides real-time geographic telemetry of compromised endpoints, organized by country code, IP address, bot ID, operating system build, and harvested credential categories. Harvested web form credentials, browser autofill entries, and keystroke logs are aggregated into relational SQL tables, allowing operators to filter submissions by targeted financial, corporate, and email domains."
}struct Formbook_/_XLoader_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Nested Process Injection: The unpacked Formbook stub maps a clean copy of ntdll.dll to unhook API intercepts -> Spawns an intermediate 32-bit Windows system binary (e.g., explorer.exe or svchost.exe) in suspended state (CREATE_SUSPENDED) -> Writes secondary shellcode via NtAllocateVirtualMemory and NtWriteVirtualMemory -> Executes intermediate thread via NtResumeThread -> Intermediate process spawns final worker process (default browser, msiexec.exe, or cmd.exe) -> Injects core stealer routine and installs inline API hooks.",
  "ntapi_functions": [
    "ntdll!NtOpenSection",
    "ntdll!NtMapViewOfSection",
    "ntdll!NtUnmapViewOfSection",
    "ntdll!NtProtectVirtualMemory",
    "ntdll!NtAllocateVirtualMemory",
    "ntdll!NtWriteVirtualMemory",
    "ntdll!NtCreateThreadEx",
    "ntdll!NtResumeThread",
    "ntdll!NtQueryInformationProcess"
  ],
  "process_hollowing_target": "explorer.exe, svchost.exe, msiexec.exe, or default web browser executable",
  "persistence_mechanics": [
    "Registry Run Key: HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run\\[RandomID]",
    "Startup Folder: %APPDATA%\\Microsoft\\Windows\\Start Menu\\Programs\\Startup\\[RandomName].lnk",
    "Scheduled Task: schtasks.exe /create /tn \"WindowsUpdate_[RandomID]\" /tr \"[DroppedPath]\" /sc onlogon"
  ],
  "evasion_hooks": [
    "NTDLL Unhooking: Opens \\KnownDlls\\ntdll.dll via NtOpenSection, maps section, sets memory protection to PAGE_EXECUTE_READWRITE on local ntdll.dll .text section, and overwrites hooked syscall wrappers with clean opcodes",
    "Heaven's Gate: Executes far jmp 0x33:Offset to switch processor from 32-bit compatibility mode to 64-bit mode on WoW64 systems, bypassing 32-bit user-mode API monitoring hooks",
    "Inline API Hooking: Patches browser networking functions (HttpSendRequestW, PR_Write) with 5-byte JMP stubs to redirect form data to internal buffers"
  ],
  "anti_analysis": [
    "PEB!BeingDebugged and NtGlobalFlag checking to detect attached debugger instances",
    "Hardware breakpoint detection via GetThreadContext inspecting DR0-DR3 registers",
    "Blacklisted module enumeration: Checks for sbiedll.dll, dbghelp.dll, api_log.dll, dir_watch.dll",
    "RDTSC instruction delta loops measuring execution latency across basic blocks to detect hypervisor virtualization"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Formbook / XLoader binary:
[ "Browser web form grabbing intercepting user inputs prior to TLS encryption", "Chromium-based browser SQLite database extraction (Login Data, Web Data, Cookies)", "Mozilla Firefox password database parsing (logins.json, key4.db) via nss3.dll API hooking", "Windows Vault and Credential Manager credential recovery", "FTP client credential recovery (FileZilla, WinSCP, Total Commander)", "Email client credential theft (Microsoft Outlook, Mozilla Thunderbird)" ]
[ "Low-level keyboard hook intercepting keystrokes and mapping them to active window titles", "Clipboard content monitor capturing text buffers on change notifications", "Desktop screenshot capture rendered via GDI BitBlt routines", "Local system metadata enumeration (OS version, architecture, privileges, installed AV)" ]
[ "Arbitrary command execution via cmd.exe process spawning with redirected standard streams", "Secondary executable downloading and in-memory execution" ]
[ "File search and grabber engine matching patterns (*.txt, *.doc, *.docx, *.pdf, *.kdbx)", "Endpoint file tree enumeration across local and removable storage drives" ]
[ "Regex-based clipboard scanning for cryptocurrency addresses (BTC, ETH, LTC)", "Dynamic replacement of cryptocurrency addresses in the Windows clipboard buffer" ]
[ "Forced system restart and shutdown via ExitWindowsEx / InitiateSystemShutdownEx", "Self-termination and registry artifact wiping upon uninstall instruction" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "HTTP POST requests directed to root URI or random pseudo-static paths (e.g., /index.php, /[random_path]/). Requests are distributed across 64-128 decoy domains, with only 1 authentic C2 domain receiving active data.",
  "serialization": "URL-encoded key-value pairs containing multi-round encrypted binary payloads formatted in custom Base64",
  "handshake": "Client generates registration payload containing unique Bot HWID (derived from volume serial number and CPUID) -> Encrypts payload with RC4 and custom Base64 -> Transmits HTTP POST to decoy array -> Real C2 responds with HTTP 200 containing RC4-encrypted command structure",
  "cryptography": "Layered RC4 and rolling XOR. The encryption key is dynamically derived using SHA-1 applied to the Bot HWID combined with the static configuration salt. The encrypted buffer undergoes bitwise transposition followed by encoding with a custom 64-character alphabet.",
  "packet_types": [
    {
      "header": "POST /<path>/ (type=0)",
      "payload": "Host registration packet containing HWID, OS build, computer name, and campaign ID",
      "direction": "Client -> Server"
    },
    {
      "header": "POST /<path>/ (type=1)",
      "payload": "Exfiltration packet containing intercepted web form fields, login credentials, and target URLs",
      "direction": "Client -> Server"
    },
    {
      "header": "POST /<path>/ (type=2)",
      "payload": "Exfiltration packet containing chronological keystroke logs and clipboard text entries",
      "direction": "Client -> Server"
    },
    {
      "header": "HTTP 200 OK",
      "payload": "Encrypted command packet containing task instructions (download, execute, update, sleep)",
      "direction": "Server -> Client"
    }
  ],
  "traffic_signature": "High volume of outbound HTTP POST requests to multiple distinct, seemingly unrelated top-level domains within short time intervals. POST bodies contain high-entropy base64-like alphanumeric strings with custom padding, lacking standard MIME boundary structures."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_FormBook_Core_Payload {
    meta:
        description = "Detects unpacked Formbook and XLoader core payloads based on ntdll unhooking logic, RC4 crypto routines, and injection signatures"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "Formbook"
        hash = "f1a2b3c4d5e6f7a8b9c0d1e2f3a4b5c6d7e8f9a0b1c2d3e4f5a6b7c8d9e0f1a2"
    strings:
        $unhook1 = "\KnownDlls\ntdll.dll" wide
        $unhook2 = "ntdll.dll" ascii
        $api1 = "NtOpenSection" ascii
        $api2 = "NtMapViewOfSection" ascii
        $api3 = "NtProtectVirtualMemory" ascii
        $crypto_loop = { 8A 04 0A 88 04 0E 88 0C 0A 01 C3 81 E3 FF 00 00 00 }
        $custom_b64 = "ABCDEFGHIJKLMNOPQRSTUVWXYZabcdefghijklmnopqrstuvwxyz0123456789+/" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 200KB and
        ($unhook1 or ($unhook2 and 2 of ($api*))) and
        ($crypto_loop or $custom_b64)
}title: Formbook Multi-Process Injection and Decoy HTTP Telemetry
id: e4f1b2c3-9a8d-4e7b-8c0a-1f2e3d4c5b6a
status: stable
description: Detects process injection into system binaries and subsequent bursts of HTTP POST requests across uncorrelated domains characteristic of Formbook/XLoader infections.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S0218/
tags:
- attack.execution
- attack.t1059.003
- attack.defense_evasion
- attack.t1055.001
- attack.credential_access
- attack.t1056.001
logsource:
category: process_creation
product: windows
detection:
selection_intermediate:
ParentImage|endswith:
- '\powershell.exe'
- '\cmd.exe'
- '\wscript.exe'
Image|endswith:
- '\explorer.exe'
- '\svchost.exe'
- '\msiexec.exe'
selection_flags:
CommandLine|contains: 'CREATE_SUSPENDED'
condition: selection_intermediate and selection_flags
falsepositives:
- Highly customized administrative provisioning scripts.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
ANY.RUN technical diagram illustrating payload decryption and nested thread injection into system binaries.
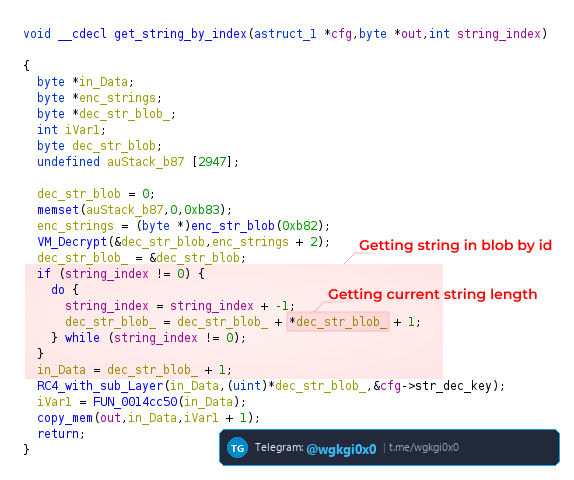
Forensic memory trace detailing base64 and RC4 decoding of command-and-control responses.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Decoy Domains, HTTP POST with Layered Encryption command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Formbook / XLoader (InfoStealer)
C-native information stealer and form grabber employing NTDLL unhooking and massive decoy HTTP traffic.
C2 Architecture: {'framing': 'HTTP POST requests directed to root URI or random pseudo-static paths (e.g., /index.php, /[random_path]/). Requests are distributed across 64-128 decoy domains, with only 1 authentic C2 domain receiving active data.', 'serialization': 'U
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Formbook / XLoader (InfoStealer)
Детальный технический анализ Formbook / XLoader — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Custom C / MASM x86 (MSVC compiler without C Runtime / CRT). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTP POST buried in 64-128 decoy domains; RC4 + rolling byte substitution + custom Base64 alphabet) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTP POST buried in 64-128 decoy domains; RC4 + rolling byte substitution + custom Base64 alphabet, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Formbook / XLoader (InfoStealer) विश्लेषण
Formbook / XLoader एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Custom C / MASM x86 (MSVC compiler without C Runtime / CRT) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTP POST buried in 64-128 decoy domains; RC4 + rolling byte substitution + custom Base64 alphabet) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTP POST buried in 64-128 decoy domains; RC4 + rolling byte substitution + custom Base64 alphabet आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).