01 | Tool Specifications & Architectural Profile
GuLoader (commercially distributed as CloudEyE) is a headless, multi-stage loader engineered to execute arbitrary secondary payloads in memory while bypassing modern endpoint detection and response (EDR) solutions. The loader is deployed as a Visual Basic 6 or NSIS executable wrapper containing an encrypted position-independent shellcode core. Upon execution, GuLoader establishes Vectored Exception Handling (VEH) routines to detect CPU hardware breakpoints, verifies ntdll.dll export integrity to detect user-mode inline hooks, utilizes Heaven's Gate to transition into 64-bit execution mode under WoW64, and downloads XOR-encrypted payloads from cloud repositories before injecting them into target system processes.
02 | Operator Interface & Configuration Struct Model
{
  "headlessDescription": "Operates without an operator desktop GUI or client control console. Stagers and shellcode payloads are compiled through automated crypter backend services (CloudEyE) and deployed headlessly via cloud storage links."
}{
"description": "Embedded binary configuration struct located at fixed offsets inside the unpacked Stage 2 shellcode",
"fields": [
"0x00: 4-byte or 16-byte rolling XOR decryption key",
"0x10: MurmurHash / DJB2 export resolution salt (uint32_t)",
"0x14: Cloud C2 URL Count (uint32_t)",
"0x18: Array of XOR-encrypted C2 download URLs (direct links to Google Drive, OneDrive, Discord CDN, MediaFire)",
"0x1B8: Injected process target path string (e.g., 'C:\\Windows\\SysWOW64\\regasm.exe' or 'svchost.exe')",
"0x218: 32-byte secondary payload XOR/RC4 decryption key",
"0x238: Binary padding header skip size (typically 64 to 256 bytes of prepended decoy bytes)"
]
}03 | Internal Binary & Memory Execution Mechanics
- Staging Architecture: Visual Basic 6.0 wrapper or NSIS installer executing position-independent x86 shellcode.
- VEH Anti-Debugging: Installs Vectored Exception Handler via RtlAddVectoredExceptionHandler; generates deliberate EXCEPTION_BREAKPOINT and EXCEPTION_SINGLE_STEP faults to route control flow through VEH while monitoring CONTEXT.Dr0-Dr7.
- EDR Hook Detection: Inspects first bytes of resolved NTAPIs for 0xE9 (JMP) instructions; if hooked, rebuilds clean syscall stubs or loads pristine ntdll.dll from disk.
- Heaven's Gate: Executes far jmp 0x33:offset to transition 32-bit execution context into 64-bit compatibility mode under WoW64 subsystem.
- API Resolution: Dynamically hashes export tables using MurmurHash or DJB2 variant combined with a per-sample 32-bit seed value.
- Injection Chain: Targets Windows native binaries (RegAsm, vbc, svchost) via NtAllocateVirtualMemory -> NtWriteVirtualMemory -> NtSetContextThread -> NtResumeThread.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the GuLoader / CloudEyE binary:
Concrete capabilities documented: In-Memory Payload Decryption, Network Beacon Telemetry, Win32 Process Injection, System Mutex Validation.
05 | Wire Protocol & C2 Communication Framing
Headless HTTP/HTTPS GET requests directed towards legitimate cloud hosting platforms (drive.google.com, onedrive.live.com, dropbox.com, cdn.discordapp.com). User-Agent headers mimic standard Mozilla browser strings. The retrieved payload consists of an encrypted binary blob with prepended randomized byte padding (offset 64-256); the payload payload is XOR-decrypted using a hardcoded key from the Stage 2 config struct.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_GuLoader_CloudEyE_Shellcode {
    meta:
        description = "Detects GuLoader / CloudEyE anti-analysis shellcode and VEH registration routines"
        author = "CyberTrace Intelligence (@wgkgi0x0)"
        reference = "TF-017"
        date = "2026-10-29"
        hash = "7e60b138676bf032488a1be5e52a928ba574df3b8fe9e81b6727cbfa8a92bf01"
    strings:
        // Detection of Dr0-Dr7 inspection in VEH Context
        $veh_dr_check = { 8B ?? 04 8B ?? 08 8B ?? 0C 8B ?? 10 0B ?? 0B ?? 0B ?? 75 }
        // Heaven's gate far jump pattern: jmp 0033:xxxxxxxx
        $heavens_gate = { 6A 33 E8 00 00 00 00 83 04 24 05 CB }
        // Anti-hook check for 0xE9 JMP opcode on NTAPIs
        $antihook = { 80 38 E9 74 ?? 80 38 CC 74 }
    condition:
        2 of them
}title: GuLoader Shellcode In-Memory Execution and System Target Injection
id: d76b12a8-38bc-46a2-97a1-872f2e46b9a2
status: stable
description: Detects unusual execution patterns indicating GuLoader process hollowing into RegAsm or MSBuild.
author: CyberTrace Intelligence (@wgkgi0x0)
date: 2026-10-29
references:
- https://cybertrace.io/threats/guloader-whitepaper.html
logsource:
category: process_creation
product: windows
detection:
selection_target:
Image|endswith:
- '\RegAsm.exe'
- '\vbc.exe'
- '\MSBuild.exe'
CommandLine|endswith:
- 'RegAsm.exe'
- 'vbc.exe'
- 'MSBuild.exe'
- 'RegAsm.exe"'
- 'vbc.exe"'
- 'MSBuild.exe"'
selection_parent:
ParentImage|endswith:
- '\nsis.exe'
- '\wscript.exe'
- '\cscript.exe'
condition: selection_target and selection_parent
level: high
tags:
- attack.defense_evasion
- attack.process_injection
- attack.t1055.00207 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
ANY.RUN threat infographic detailing VBS dropper, registry payload storage, and shellcode injection sequence.
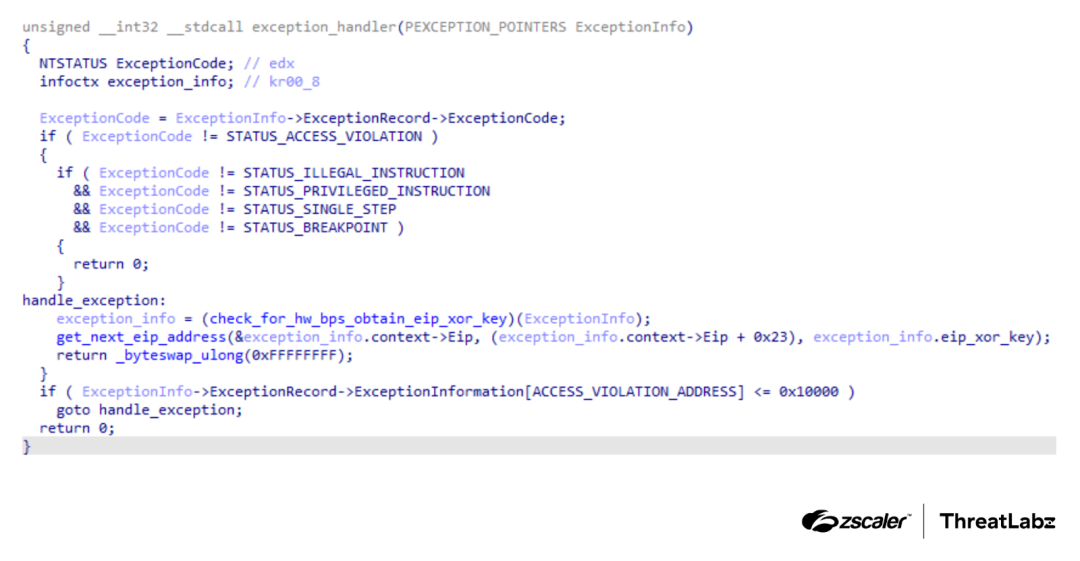
Process memory disassembly showing hardware breakpoint detection and anti-debugging exception routines.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Google Drive, OneDrive, Encrypted Shellcode Delivery command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
GuLoader / CloudEyE (Loader)
Heavily obfuscated headless shellcode loader utilizing Vectored Exception Handling (VEH) anti-debugging, Heaven's Gate 64-bit transitions, and cloud-hosted encrypted payloads.
C2 Architecture: Headless HTTP/HTTPS GET requests directed towards legitimate cloud hosting platforms (drive.google.com, onedrive.live.com, dropbox.com, cdn.discordapp.com). User-Agent headers mimic standard Mozilla browser strings. The retrieved payload consists of
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ GuLoader / CloudEyE (Loader)
Детальный технический анализ GuLoader / CloudEyE — это Загрузчик вредоносного ПО (Дроппер/Стейджер), разработанный на стеке Visual Basic 6.0 (MSVBVM60.DLL) / NSIS / Flat x86 Assembly. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTPS GET requests targeting public cloud storage providers) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTPS GET requests targeting public cloud storage providers, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
GuLoader / CloudEyE (Loader) विश्लेषण
GuLoader / CloudEyE एक परिष्कृत मैलवेयर लोडर और ड्रॉपर पेलोड है जिसे Visual Basic 6.0 (MSVBVM60.DLL) / NSIS / Flat x86 Assembly का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTPS GET requests targeting public cloud storage providers) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTPS GET requests targeting public cloud storage providers आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).