01 | Tool Specifications & Architectural Profile
Havoc is an advanced command-and-control framework architected as an alternative to proprietary platforms like Cobalt Strike. Its core implant, termed 'Demon', is written in pure C and assembly, delivering enterprise-grade evasions. Demon features native indirect syscall resolution (Halo's Gate / RecycledGate), call stack spoofing, hardware breakpoint AMSI/ETW patching, and in-memory heap encryption during sleep intervals via the Ekko technique. The teamserver is developed in Go with high-concurrency channel pipelines, while operators interact through a native Qt6 desktop client.
02 | Operator Interface & Configuration Struct Model
Detailed reverse-engineering specifications archived in laboratory telemetry.
{
  "structureType": "Embedded Binary Struct (DEMON_CONFIG) & YAOTL Profile Model",
  "decryptionRoutine": "Demon payload initial stage resolves key via pre-configured XOR or AES-256-CBC envelope; runtime configuration resides in unbacked or allocated memory pages with dynamic masking.",
  "inMemoryLayout": "typedef struct {\n    ULONG   Magic;              // Offset 0x00: 0xDEADBEEF\n    ULONG   SleepTime;          // Offset 0x04: Beacon sleep interval in seconds\n    ULONG   SleepJitter;        // Offset 0x08: Randomization percentage (0-100)\n    ULONG   KillDate;           // Offset 0x0C: Unix epoch timestamp for termination\n    ULONG   WorkingHours;       // Offset 0x10: Allowed operational timeframe bitmask\n    BYTE    AmsiEtwPatch;       // Offset 0x14: 0x01 (Patch) | 0x02 (Hardware Breakpoints)\n    BYTE    SyscallMethod;      // Offset 0x15: 0x00 (Win32), 0x01 (Direct), 0x02 (Indirect/Halo's Gate)\n    BYTE    SleepTechnique;     // Offset 0x16: 0x00 (None), 0x01 (Ekko), 0x02 (Foliage), 0x03 (Zsk)\n    BYTE    ProxyType;          // Offset 0x17: 0x00 (Direct), 0x01 (SOCKS5), 0x02 (HTTP Connect)\n    CHAR    Hosts[3][256];      // Offset 0x18: Up to 3 primary and failover C2 domain endpoints\n    BYTE    AesKey[32];         // Offset 0x318: Negotiated 256-bit AES session key\n    BYTE    AesIv[16];          // Offset 0x338: 128-bit initialization vector\n} DEMON_CONFIG;",
  "panelConfigOptions": "Demon Builder GUI allows selection of: Target Arch (x64/x86), Output Format (Windows Shellcode, DLL, Exe, Service Exe), Sleep Obfuscation Method (Ekko, Foliage, TimerQueue), Syscall Engine (Direct Syscalls, Indirect Syscalls), Call Stack Spoofing toggle, AMSI/ETW Patching method, and Malleable HTTP listener headers."
}03 | Internal Binary & Memory Execution Mechanics
{
  "apiResolution": "Demon implements custom hashing (DJB2 with randomized seeds) across PEB InLoadOrderModuleList to locate ntdll.dll and kernel32.dll exports without invoking GetProcAddress.",
  "indirectSyscalls": "Integrates RecycledGate and Halo's Gate mechanics. Evaluates ntdll.dll Export Address Table in memory, computes System Service Numbers (SSN), detects inline hooks (0xE9 JMP), traverses adjacent stubs to extract true SSN, and executes 'syscall ; ret' instructions directly from clean memory offsets inside ntdll.dll.",
  "sleepObfuscation": "Employs the Ekko / Foliage sleep evasion technique. Utilizes CreateTimerQueueTimer or NtSetTimer2 combined with NtContinue contexts. While transitioning to sleep, it invokes SystemFunction032 (RC4) to encrypt the heap and Demon memory image, modifies page protections from PAGE_EXECUTE_READ to PAGE_NOACCESS or PAGE_READWRITE, sleeps for the jittered duration, and restores PAGE_EXECUTE_READ prior to code resumption.",
  "stackSpoofing": "Synthetic stack frame spoofing rewrites thread CONTEXT structures to emulate legitimate execution call stacks (e.g., ntdll!RtlUserThreadStart -> kernel32!BaseThreadInitThunk) masking unbacked thread call graphs from security scanners."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Havoc Post-Exploitation Framework binary:
{'module': 'Indirect Syscall Dispatcher', 'description': 'Executes NTAPI system calls via ntdll.dll trampolines avoiding EDR userland API hooks.', 'apis': 'NtAllocateVirtualMemory, NtProtectVirtualMemory, NtWriteVirtualMemory, NtCreateThreadEx'}
{'module': 'COFF / BOF In-Memory Loader', 'description': 'Parses and executes unlinked Common Object File Format (COFF) objects directly in memory, resolving internal dynamic symbols.', 'apis': 'BeaconDataParse, BeaconPrintf, Internal Symbol Linker'}
{'module': 'Token Impersonation & Manipulation', 'description': 'Steals, duplicates, and impersonates security tokens from target processes to achieve privilege escalation or lateral movement.', 'apis': 'OpenProcess, OpenProcessToken, DuplicateTokenEx, ImpersonateLoggedOnUser'}
{'module': 'Process Injection Engine', 'description': 'Injects arbitrary shellcode into remote processes using Early Cascade, QueueUserAPC, or thread hijacking techniques.', 'apis': 'NtOpenProcess, NtAllocateVirtualMemory, NtQueueApcThread, NtResumeThread'}
{'module': 'SMB Named Pipe Pivot', 'description': 'Enables peer-to-peer agent mesh networking across air-gapped or restricted network segments using Windows Named Pipes.', 'apis': 'CreateNamedPipeA, ConnectNamedPipe, ReadFile, WriteFile'}
05 | Wire Protocol & C2 Communication Framing
Havoc Demon utilizes a binary packet framing protocol over malleable HTTP/HTTPS or SMB Named Pipes. Each packet consists of: [ 4-byte Magic (0xDEADBEEF) ] [ 4-byte Agent ID ] [ 4-byte Command ID ] [ 4-byte Data Length ] [ Encrypted Body (AES-256-CBC or AES-256-GCM) ] [ 16-byte HMAC/Tag ]. Initial registration uses RSA-2048 to negotiate a unique AES-256 session key. In HTTP mode, packets are embedded in custom HTTP headers, base64-encoded cookie fields, or simulated image uploads matching the configured YAOTL malleable profile. In SMB mode, packets traverse named pipes matching configurable path masks (e.g., \\.\pipe\demon-*).
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Havoc_Demon_Agent {
    meta:
        description = "Detects Havoc C2 Demon implant binary footprints and memory artifacts"
        author = "CyberTrace CTI Operations"
        date = "2026-10-29"
        hash = "8a3d5e2781b0a9b6c167c6999b78ff342468383c0f49c0ea45dbf6828a1c97a5"
        category = "C2_FRAMEWORK"
    strings:
        $magic = { EF BE AD DE } // 0xDEADBEEF Demon Magic
        $djb2_seed = { B8 05 15 00 00 } // 5381 DJB2 seed constant
        $ekko_rop1 = "SystemFunction032" ascii
        $ekko_rop2 = "NtContinue" ascii
        // Indirect syscall trampoline byte sequence
        $indirect_gate = { 4C 8B D1 B8 ?? ?? 00 00 0F 05 C3 }
    condition:
        uint16(0) == 0x5A4D and
        ( ( $magic and 2 of ($ekko*) ) or ( $indirect_gate and $djb2_seed ) )
}title: Havoc C2 Demon Named Pipe or Network Activity
id: 7e4b2d18-5f9a-41c3-8820-2c7b4e9a1d3f
status: stable
description: Detects pipe creation and process execution patterns characteristic of Havoc Demon post-exploitation activities.
author: CyberTrace Defensive Engineering
date: 2026-10-29
logsource:
category: pipe_created
product: windows
detection:
selection:
PipeName|startswith: '\demon-'
condition: selection
fields:
- ProcessId
- Image
- PipeName
falsepositives:
- Unknown third-party software with coincidental pipe naming (unlikely)
level: high
tags:
- attack.execution
- attack.defense_evasion
- attack.t1055.001
- attack.t1573.00207 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
Decompiled Disassembly & Reverse-Engineering Strings
// Decompiled Havoc Demon Indirect Syscall and Ekko Sleep Dispatch
NTSTATUS DemonSyscallInvoke(DWORD ssn, PVOID syscallTrampoline, PVOID args) {
    // SSN loaded into EAX, indirect jump executed to 'syscall; ret' inside clean ntdll address
    __asm {
        mov r10, rcx
        mov eax, ssn
        jmp syscallTrampoline
    }
}

VOID DemonEkkoSleep(DWORD sleepMs) {
    CONTEXT ctxThread, ctxRop;
    HANDLE hTimerQueue = CreateTimerQueue();
    HANDLE hTimer = NULL;
    // Set timer callbacks to SystemFunction032 (RC4 mask), NtProtectVirtualMemory (PAGE_NOACCESS),
    // WaitForSingleObject, and NtProtectVirtualMemory (PAGE_EXECUTE_READ)
    CreateTimerQueueTimer(&hTimer, hTimerQueue, (WAITORTIMERCALLBACK)NtContinue, &ctxRop, sleepMs, 0, WT_EXECUTEINTIMERTHREAD);
    WaitForSingleObject(hTimer, sleepMs);
}
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
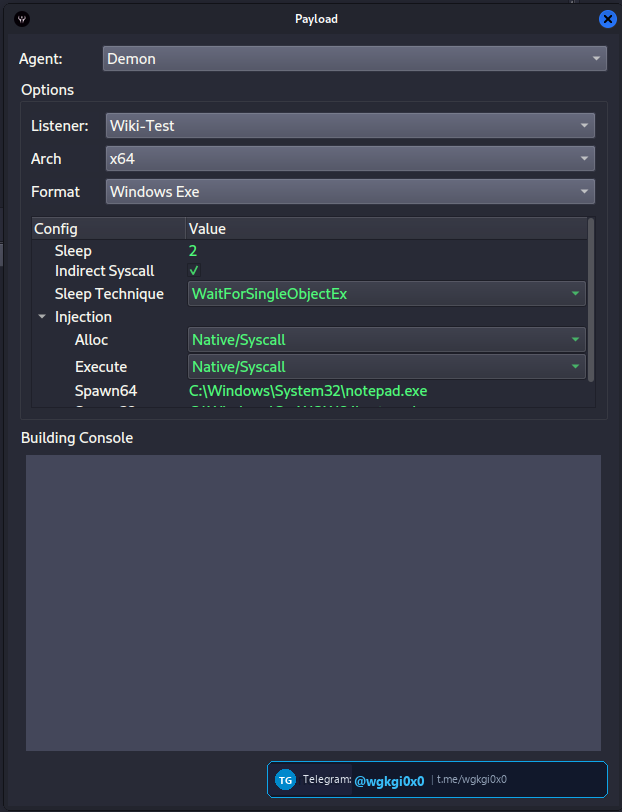
Official Havoc client UI configuring Demon agent sleep obfuscation, indirect syscalls, and x64 shellcode injection stubs.
Operator UI managing compromised enterprise hosts, active Demon beacons, and lateral movement listeners.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Demon Agent, Malleable HTTP/HTTPS, SMB Pipes command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Havoc Post-Exploitation Framework (C2 Framework)
Modern open-source post-exploitation C2 framework featuring a native C agent ('Demon') equipped with indirect syscalls, Ekko sleep obfuscation, and malleable communication transports.
C2 Architecture: Havoc Demon utilizes a binary packet framing protocol over malleable HTTP/HTTPS or SMB Named Pipes. Each packet consists of: [ 4-byte Magic (0xDEADBEEF) ] [ 4-byte Agent ID ] [ 4-byte Command ID ] [ 4-byte Data Length ] [ Encrypted Body (AES-256-CBC
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Havoc Post-Exploitation Framework (C2 Framework)
Детальный технический анализ Havoc Post-Exploitation Framework — это Фреймворк командно-контрольного управления (C2), разработанный на стеке Demon: C/ASM (MinGW/Clang); Server: Go; Client: C++/Qt6. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Malleable HTTP/HTTPS, SMB Named Pipes) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Malleable HTTP/HTTPS, SMB Named Pipes, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Havoc Post-Exploitation Framework (C2 Framework) विश्लेषण
Havoc Post-Exploitation Framework एक परिष्कृत कमांड और कंट्रोल (C2) फ्रेमवर्क है जिसे Demon: C/ASM (MinGW/Clang); Server: Go; Client: C++/Qt6 का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Malleable HTTP/HTTPS, SMB Named Pipes) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Malleable HTTP/HTTPS, SMB Named Pipes आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).