01 | Tool Specifications & Architectural Profile
LockBit 3.0 (internal project designation LockBit Black) is a modular ransomware platform written in C and assembly. The architecture incorporates code elements from BlackMatter and DarkSide, utilizing runtime API hash resolution, a mandatory command-line decryption passkey (-pass) to decrypt in-memory code sections, an asynchronous multi-threaded IOCP file processing engine, and dual cryptographic algorithms (ChaCha20/AES-GCM with Curve25519/RSA-4096).
02 | Operator Interface & Configuration Struct Model
{
  "-pass": "Mandatory 32-character hexadecimal key used to decrypt code segments and configuration table in memory. Execution terminates if omitted.",
  "-k": "Path to local key escrow file containing session encryption keys.",
  "-path": "Directs encryption strictly to the designated folder path, suppressing full-drive traversal.",
  "-p": "Alternative parameter syntax to target a single directory or network mount.",
  "-n": "Disables network share discovery and enumeration via WNetOpenEnumW and NetShareEnum.",
  "-log": "Directs forensic execution trace and encrypted file paths to a local log file.",
  "-safe": "Configures bcdedit safeboot network and schedules service to execute payload upon Safe Mode reboot.",
  "-silent": "Runs headless without console output or UI dialog allocations."
}{
"description": "Encrypted binary structure within .data section, decrypted via custom XOR/RC4 loop keyed by -pass parameter",
"fields": [
"0x00: 4-byte CRC32 checksum of decrypted configuration data",
"0x04: 32-byte master Curve25519 public key (or 512-byte RSA-4096 public key modulus)",
"0x24: 16-byte unique affiliate identification token",
"0x34: Boolean flags bitmap (enable_network_shares, enable_safe_mode, kill_processes, kill_services, wipe_shadows)",
"0x38: Offset to null-delimited process termination blacklist (sqlservr.exe, excel.exe, winword.exe, etc.)",
"0x3C: Offset to null-delimited service termination blacklist (vss, msexchange, sql, veeam, sophos, backup)",
"0x40: Offset to directory exclusion list (Windows, ProgramData, System Volume Information, $Recycle.Bin)",
"0x44: Offset to file extension exclusion list (.exe, .dll, .sys, .lnk, .lockbit)",
"0x48: Offset to ransom note template string (incorporating dynamic affiliate Tor URL and personal ID)",
"0x4C: Desktop wallpaper BMP payload byte stream"
]
}03 | Internal Binary & Memory Execution Mechanics
{
  "initialization": "Validates command-line arguments. Locates -pass flag and derives runtime decryption key. Decrypts internal API resolution hashes and executes dynamic PE loader.",
  "antiAnalysis": "Executes CPUID instruction to detect hypervisor bit. Invokes NtSetInformationThread(ThreadHideFromDebugger). Checks PEB.BeingDebugged and performs timing verification via rdtsc.",
  "tokenElevation": "Invokes OpenProcessToken to acquire SeDebugPrivilege, SeTakeOwnershipPrivilege, and SeBackupPrivilege. If running with unprivileged token, spawns ICMLuaUtil COM elevation helper.",
  "serviceAndProcessSweeper": "Iterates through Service Control Manager using EnumServicesStatusExW; calls ControlService(SERVICE_CONTROL_STOP) on identified backup/security services. Uses CreateToolhelp32Snapshot to identify and TerminateProcess file-locking processes.",
  "shadowCopyPurge": "Invokes IVssBackupComponents COM interface to locate and delete all active volume shadow copies. Executes fallback shell commands: vssadmin delete shadows /all /quiet and bcdedit /set {default} recoveryenabled no.",
  "encryptionPipeline": "Initializes Windows I/O Completion Port (IOCP). Traverses drive volumes and network shares. Workers pop file paths, generate 256-bit ChaCha20 session keys, perform full or intermittent stride encryption, append Curve25519-wrapped key header, and rename file to .[random_affiliate_id].",
  "ransomDelivery": "Drops ransom note README.txt across all traversed directories. Writes BMP wallpaper to %TEMP% and updates desktop via SystemParametersInfoW(SPI_SETDESKWALLPAPER). Triggers network printer spooling via EnumPrintersW and StartDocPrinterW."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the LockBit 3.0 binary:
ChaCha20-Poly1305 / AES-256-GCM hardware-accelerated stream cipher with Curve25519 ECDH key wrapping
Windows I/O Completion Ports (IOCP) multithreaded architecture scaled to hardware thread availability
API hashing via custom ROR13, code segment encryption, debugger evasion via NtSetInformationThread, process token elevation
Safe Mode reboot persistence via bcdedit /set {current} safeboot network and RunOnce service keys
WNetOpenEnumW and NetShareEnum network discovery with multi-threaded SMB directory crawling
COM-based VSS purge coupled with vssadmin and WMI Win32_ShadowCopy command execution
05 | Wire Protocol & C2 Communication Framing
Decentralized command infrastructure operating over Tor V3 Onion hidden services. Communication routing occurs via embedded SOCKS5 proxy components connecting to preconfigured Tor gateway nodes. Operators interact with affiliates via Tox decentralized protocol IDs embedded within the configuration structure. Negotiation and ransom verification proceed through dedicated per-victim Tor Onion portals authenticated via unique victim identification tokens.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_LockBit_3.0_Core {
    meta:
        description = "Detects LockBit 3.0 (Black) ransomware payload, command-line parameter parsing, and IOCP encryption routines"
        author = "CyberTrace Intelligence (@wgkgi0x0)"
        reference = "TF-021"
        date = "2026-10-29"
        hash = "c18be50db1f7131b7829774505c86c1236814b62dbd11158b0f8d95180cb9e28"
    strings:
        // LockBit 3.0 command-line parsing switches
        $flag_pass = "-pass" wide ascii
        $flag_path = "-path" wide ascii
        $flag_safe = "-safe" wide ascii
        $flag_log  = "-log" wide ascii
        // ChaCha20 constant matrix: "expand 32-byte k"
        $chacha_const = { 65 78 70 61 6E 64 20 33 32 2D 62 79 74 65 20 6B }
        // API hashing and IOCP invocation sequence
        $iocp_call = { FF 15 ?? ?? ?? ?? 85 C0 74 ?? 6A 00 6A 00 56 FF 15 }
        // Shadow copy deletion command
        $vss_cmd = "vssadmin delete shadows /all /quiet" wide ascii
        $bcd_cmd = "bcdedit /set {default} recoveryenabled no" wide ascii
    condition:
        uint16(0) == 0x5A4D and
        ($chacha_const or ($flag_pass and 2 of ($flag_*))) and
        ($vss_cmd or $bcd_cmd or $iocp_call)
}title: LockBit 3.0 Ransomware Execution and Shadow Copy Purge
id: 4e82b719-7d1a-4c92-9381-8b201476d021
status: stable
description: Detects command-line parameters and process execution patterns characteristic of LockBit 3.0 (LockBit Black).
author: CyberTrace Intelligence (@wgkgi0x0)
date: 2026-10-29
logsource:
category: process_creation
product: windows
detection:
selection_flags:
CommandLine|contains:
- "-pass "
- "-safe "
selection_vss:
CommandLine|contains|all:
- "vssadmin"
- "delete"
- "shadows"
- "/quiet"
selection_bcd:
CommandLine|contains|all:
- "bcdedit"
- "recoveryenabled"
- "no"
condition:
selection_flags or (selection_vss and selection_bcd)
falsepositives:
- Administrative backup management scripts using vssadmin (distinguished by absence of -pass flag)
level: critical
tags:
- attack.impact
- attack.t1486
- attack.t1490
- attack.t1059.00307 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
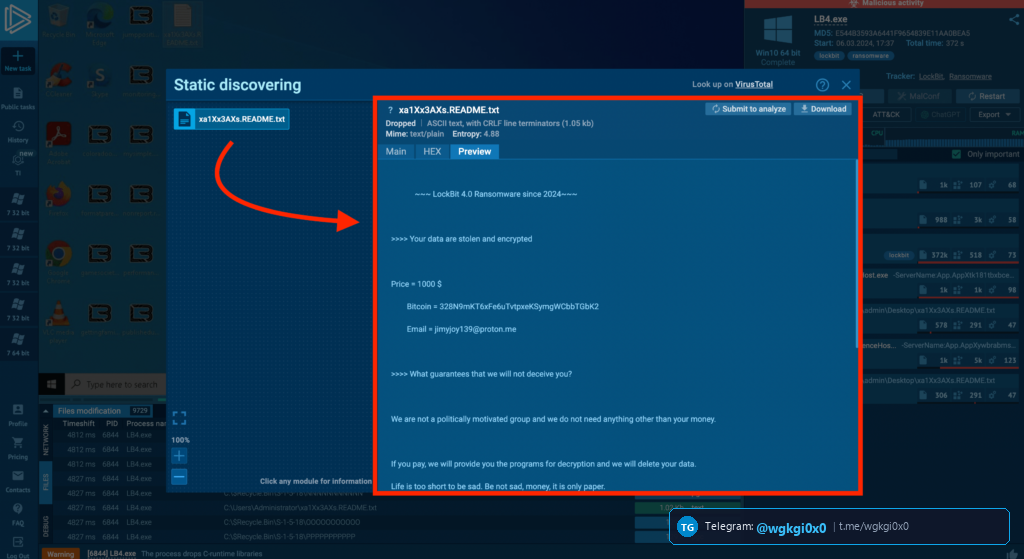
ANY.RUN sandbox capture showing service termination, shadow copy deletion, and high-speed file encryption.
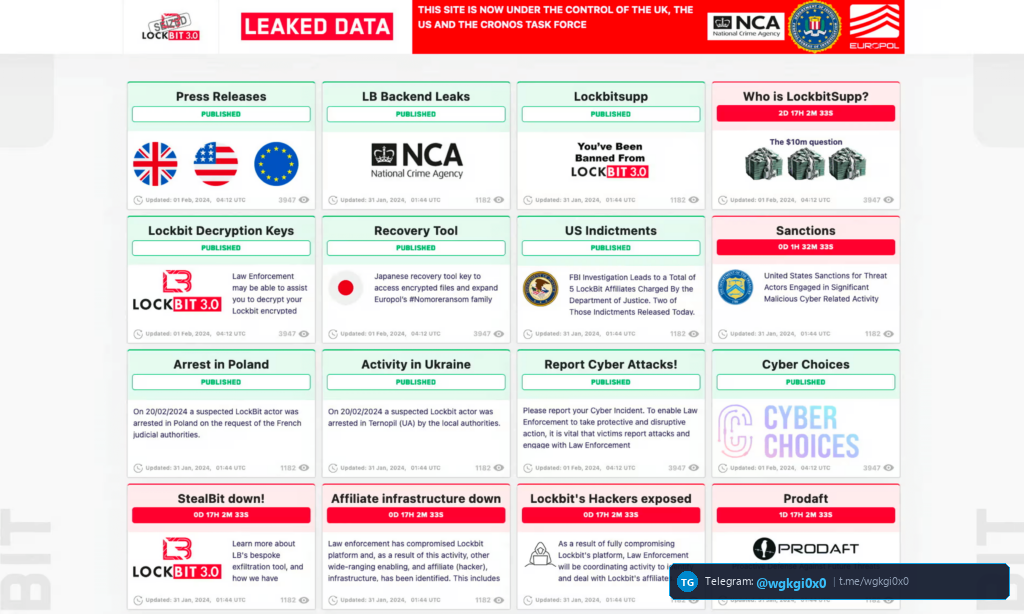
Onion portal interface detailing ransom demands, countdown timers, and stolen proof-of-concept data archives.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Tor Hidden Services, Decentralized Leaks Portals command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
LockBit 3.0 (Ransomware)
Statically compiled C/assembly ransomware framework engineered with Windows I/O Completion Port multithreading, modular code section encryption, and dual Curve25519/ChaCha20 cryptographic engines.
C2 Architecture: Decentralized command infrastructure operating over Tor V3 Onion hidden services. Communication routing occurs via embedded SOCKS5 proxy components connecting to preconfigured Tor gateway nodes. Operators interact with affiliates via Tox decentralize
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ LockBit 3.0 (Ransomware)
Детальный технический анализ LockBit 3.0 — это Программа-вымогатель (Шифровальщик), разработанный на стеке Microsoft Visual C++ (MSVC) / x86 Assembly (PE32 / PE32+). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Tor V3 Onion Services via embedded SOCKS5 proxy routing and Tox messaging protocol) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Tor V3 Onion Services via embedded SOCKS5 proxy routing and Tox messaging protocol, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
LockBit 3.0 (Ransomware) विश्लेषण
LockBit 3.0 एक परिष्कृत डेटा एन्क्रिप्ट करने वाला रैंसमवेयर है जिसे Microsoft Visual C++ (MSVC) / x86 Assembly (PE32 / PE32+) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Tor V3 Onion Services via embedded SOCKS5 proxy routing and Tox messaging protocol) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Tor V3 Onion Services via embedded SOCKS5 proxy routing and Tox messaging protocol आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).