01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C/C++ (MSVC) optimized for size (/O1 or /Os)",
  "runtime": "Win32 C Runtime with direct NTAPI syscalls",
  "binary_footprint": "Single PE32 executable, typically 120 KB - 280 KB uncompressed",
  "stub_size": "184,320 bytes (typical unpacked sample)",
  "packer_obfuscation": "Intense control-flow flattening (CFF), opaque predicate insertion, Heaven's Gate execution transitions under WOW64, dynamic string decoding",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "Entry -> Anti-Analysis & Mouse Position Differential Check -> Heaven's Gate WOW64 transition -> Dynamic Syscall Resolution -> Resolve C2 Domain Array -> Retrieve Target Config -> Execute Stealer Modules -> Dispatch Payload -> Terminate",
  "technical_summary": "Lumma Stealer (LummaC2) is a sophisticated Malware-as-a-Service information stealer written in C. It employs aggressive defense evasion, including mouse movement trajectory validation, Heaven's Gate execution transitions to bypass WOW64 hooks, and indirect syscalls. Its C2 infrastructure utilizes fast-flux domain networks across low-cost TLDs (.pw, .shop, .top) fronted by Cloudflare CDN edge nodes."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "MaaS Web Panel / Operator Dashboard",
  "builder_tabs_options": [
    {
      "tab": "Affiliate Dashboard",
      "options": [
        "Real-time log ingestion stream showing victim IP, country, and stolen asset counters",
        "Automated wallet sorter filtering by token balance and blockchain address activity",
        "Cookie format validator converting raw sqlite exports into Netscape format"
      ]
    },
    {
      "tab": "Payload Configuration",
      "options": [
        "Affiliate Tag: Unique string assigned to operator (e.g., 'aff_7812')",
        "Domain Array: Entry of 9-10 rotating C2 endpoint domains",
        "File Grabber Config: Regular expressions defining file extensions, directory depths, and size caps (default < 10MB)",
        "Loader Integration: Configuration of secondary executable download URL and execution conditions"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x0000",
      "field": "BuildId",
      "type": "char[32]",
      "description": "Affiliate identification string"
    },
    {
      "offset": "0x0020",
      "field": "C2DomainCount",
      "type": "uint32",
      "description": "Number of embedded active C2 domains"
    },
    {
      "offset": "0x0024",
      "field": "C2DomainPointers",
      "type": "uint32[10]",
      "description": "Offsets to XOR-obfuscated domain strings"
    },
    {
      "offset": "0x004C",
      "field": "XorSeed",
      "type": "uint32",
      "description": "Seed value for PRNG-based string decryption"
    },
    {
      "offset": "0x0050",
      "field": "GrabberRules",
      "type": "char[256]",
      "description": "Semicolon-delimited target file extension patterns"
    }
  ],
  "payload_generation_flags": [
    "Target Subsystem: Win32 GUI",
    "Control Flow Flattening: Enabled",
    "Indirect Syscalls: Native x64 WOW64 Gate"
  ],
  "operator_commands": [
    "TASK_DOWNLOAD_EXEC: Downloads binary from specified URL and invokes via CreateProcessW",
    "TASK_UPDATE_DOMAINS: Updates active internal C2 domain array in memory",
    "TASK_SLEEP: Adjusts beacon frequency interval",
    "TASK_KILL: Erases memory buffers and issues immediate process termination"
  ],
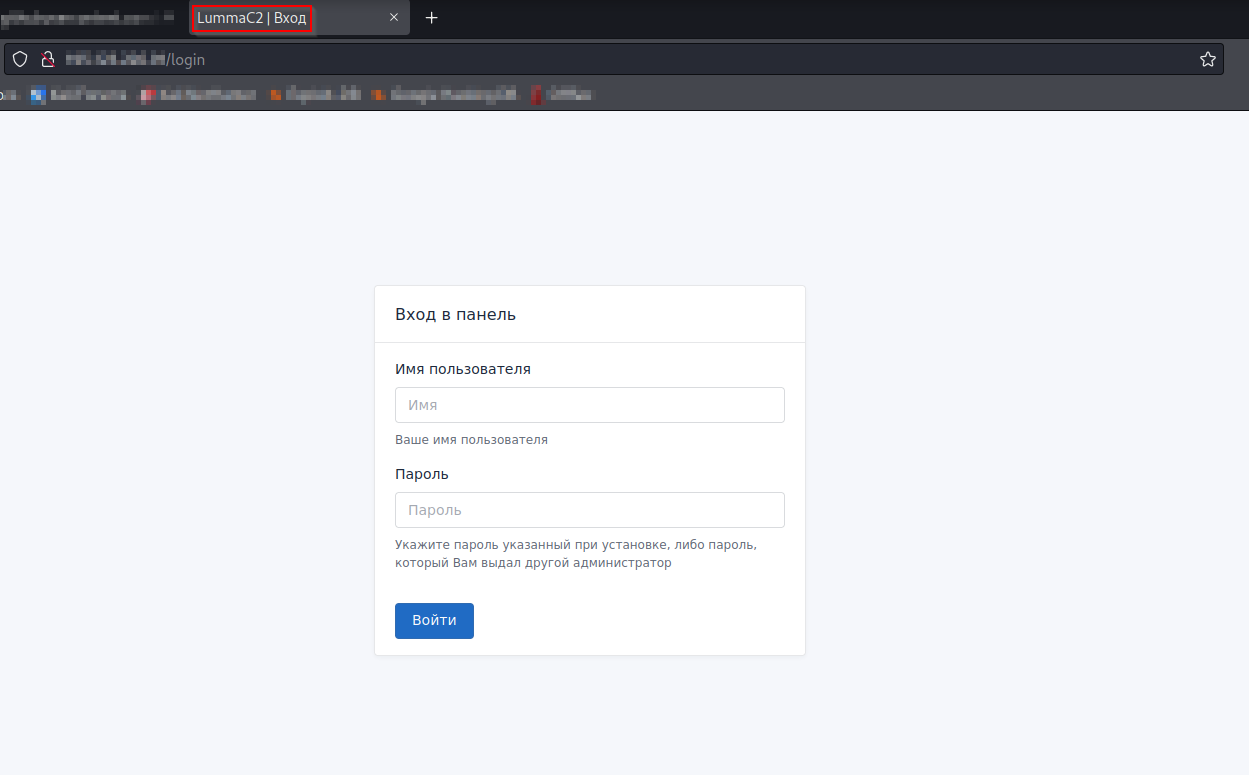
  "interface_telemetry_analysis": "The LummaC2 operator interface is accessible via private Tor hidden services or authenticated clearnet web portals. It features analytics detailing infection counts by country, top victim operating systems, total cryptocurrency wallets discovered, and automated filters for high-value banking and enterprise credentials."
}struct Lumma_Stealer_(LummaC2)_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Under WOW64 on 64-bit Windows, Lumma executes Heaven's Gate: issues a far jump (jmp 0x33:Offset) to transition the CPU from 32-bit compatibility mode into 64-bit long mode, executing 64-bit indirect syscalls directly and evading 32-bit userland API hooks installed by security products in ntdll.dll.",
  "ntapi_functions": [
    "ntdll!NtAllocateVirtualMemory",
    "ntdll!NtProtectVirtualMemory",
    "ntdll!NtWriteVirtualMemory",
    "ntdll!NtCreateThreadEx",
    "ntdll!NtResumeThread"
  ],
  "process_hollowing_target": "N/A (Executes primarily within initial process context or hollows into clean system utilities like svchost.exe / msiexec.exe)",
  "persistence_mechanics": [
    "Does not establish native persistence by default; functions as an ephemeral harvesting agent or downloads persistent secondary payloads via tasking"
  ],
  "evasion_hooks": [
    "Heaven's Gate 32-to-64 bit execution mode transition",
    "Dynamic runtime hashing of API strings using custom ROR13-based algorithms",
    "Hardware breakpoint detection inspecting DR0-DR7 debug registers via GetThreadContext"
  ],
  "anti_analysis": [
    "Human interaction heuristic: queries GetCursorPos across time intervals, computing Euclidean vector distance; halts execution if mouse cursor does not move continuously in a non-linear path",
    "Timing check via rdtsc and QueryPerformanceCounter detecting virtual machine instruction execution latency",
    "Blacklist validation of BIOS serials, disk model names (checking for 'VBOX', 'VMWARE', 'QEMU'), and sandbox DLL modules"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Lumma Stealer (LummaC2) binary:
[ "Chromium v10/v20 App-Bound Encryption bypass via elevated DPAPI decryption loops", "Targeted extraction of Login Data, Web Data, Cookies, and History SQLite tables", "Gecko profiles extraction targeting logins.json and key4.db master passwords", "Extraction of 90+ Web3 cryptocurrency extension profiles (MetaMask, Phantom, TronLink, Binance, Coinbase)" ]
[ "System profile collection: OS version, system architecture, CPU info, GPU description, screen dimensions, keyboard layout" ]
[ "Second-stage loader module: downloads and executes secondary binaries, loaders, or ransomware payloads on demand" ]
[ "File grabber module targeting user profile folders for files matching .txt, .pdf, .doc, .docx, .kdbx, .wallet", "Telegram Desktop session directory (tdata) collection", "Discord client token extraction from local LevelDB databases" ]
[ "N/A (Focuses on direct wallet file and extension vault extraction rather than persistent clipboard monitoring)" ]
[ "Memory scrubbing: overwrites harvested credential buffers with zeros immediately prior to freeing heap space" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "HTTP/1.1 POST transactions with URI paths structured as randomized alphanumeric strings or /api endpoint paths",
  "serialization": "Base64-encoded compressed binary stream containing a 32-byte header followed by zlib-deflated JSON data",
  "handshake": "Client issues DNS queries against fast-flux domain array -> Establishes TCP connection to port 80/443 -> Dispatches initial check-in beacon containing hardware UUID and affiliate tag -> C2 returns encrypted tasking directives and target list",
  "cryptography": "Custom rolling XOR algorithm utilizing a 16-byte key derived from the build timestamp, combined with SSL/TLS transport layer encryption when routed through Cloudflare CDN proxies",
  "packet_types": [
    {
      "header": "POST /api",
      "payload": "Encrypted check-in beacon: HWID, OS, BuildTag",
      "direction": "Client -> C2"
    },
    {
      "header": "HTTP 200 OK",
      "payload": "Tasking response: active grabber rules, secondary download URLs",
      "direction": "C2 -> Client"
    },
    {
      "header": "POST /api/upload",
      "payload": "Multipart stream: Harvested archive data",
      "direction": "Client -> C2"
    }
  ],
  "traffic_signature": "Rapid outbound HTTP/HTTPS beaconing to high-entropy domains under .pw, .shop, .top, or .click TLDs, transmitting POST requests with User-Agent strings mimicking recent Chrome/Edge browser releases."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_LummaStealer_Native {
    meta:
        description = "Detects unpacked LummaC2 native executables based on control flow deobfuscation loops, Heaven's Gate transitions, and unique string patterns"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "LummaStealer"
        hash = "8b64e082e6d6e7bf7f6e0c1f513a9686e0882e9b0151f7bb8a2c2627d3b5b19f"
    strings:
        $hg_wow64 = { 6A 33 E8 00 00 00 00 83 04 24 05 CB } // Heaven's Gate far jump sequence
        $mouse_check = { FF 15 ?? ?? ?? ?? 8B ?? ?? 8B ?? ?? 2B ?? 0F AF ?? } // Cursor delta vector calculation
        $s1 = "LummaC2" ascii
        $s2 = "aff_id=" ascii
        $s3 = "c2_gate" ascii
        $s4 = "\Local State" ascii
        $s5 = "\key4.db" ascii
        $s6 = "tdata" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 500KB and
        ($hg_wow64 or $mouse_check or 3 of ($s*))
}title: LummaC2 Fast-Flux Network Activity and Heaven's Gate Execution
id: 3c2d1e0f-9a8b-4c7d-8e6f-5a4b3c2d1e0f
status: stable
description: Detects process execution exhibiting WOW64 Heaven's Gate transitions followed by HTTP POST connections to low-reputation top-level domains.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S1133/
tags:
- attack.execution
- attack.t1106
- attack.defense_evasion
- attack.t1027
- attack.command_and_control
- attack.t1071.001
logsource:
category: process_creation
product: windows
detection:
selection_process:
Image|endswith:
- '\AppData\Local\Temp\*.exe'
- '\AppData\Roaming\*.exe'
- '\Users\Public\*.exe'
selection_network:
DestinationHostname|endswith:
- '.pw'
- '.shop'
- '.top'
- '.click'
- '.site'
condition: selection_process and selection_network
falsepositives:
- Unlikely in enterprise environments; monitor for developer testing.
level: critical07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
ANY.RUN sandbox telemetry displaying multi-stage process injection, anti-analysis loops, and credential harvesting routines.
Encrypted HTTP C2 beaconing protocol showing dynamic domain resolution and target configuration retrieval.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Fast-Flux Domains, Cloudflare Proxies, Multi-tier C2 command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Lumma Stealer (LummaC2) (InfoStealer)
High-velocity C native info stealer with Heaven's Gate WOW64 evasion and fast-flux C2 infrastructure.
C2 Architecture: {'framing': 'HTTP/1.1 POST transactions with URI paths structured as randomized alphanumeric strings or /api endpoint paths', 'serialization': 'Base64-encoded compressed binary stream containing a 32-byte header followed by zlib-deflated JSON data',
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Lumma Stealer (LummaC2) (InfoStealer)
Детальный технический анализ Lumma Stealer (LummaC2) — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Native C compiled with Microsoft Visual C/C++ (MSVC), stripped PE32 binary. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTP/1.1 and HTTPS via Fast-Flux rotating domain infrastructure with custom XOR/RC4 session encryption) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTP/1.1 and HTTPS via Fast-Flux rotating domain infrastructure with custom XOR/RC4 session encryption, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Lumma Stealer (LummaC2) (InfoStealer) विश्लेषण
Lumma Stealer (LummaC2) एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Native C compiled with Microsoft Visual C/C++ (MSVC), stripped PE32 binary का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTP/1.1 and HTTPS via Fast-Flux rotating domain infrastructure with custom XOR/RC4 session encryption) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTP/1.1 and HTTPS via Fast-Flux rotating domain infrastructure with custom XOR/RC4 session encryption आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).