01 | Tool Specifications & Architectural Profile
Medusa is a targeted enterprise ransomware platform written in C++ (MSVC). The binary employs Windows I/O Completion Ports (IOCP) to achieve high-throughput file encryption across local drives and network shares. The payload includes an extensive blacklist of 280+ services and 150+ processes associated with databases, virtualization, and endpoint security. Files are encrypted via AES-256 in CBC mode, with the session key encapsulated using an embedded RSA public key.
02 | Operator Interface & Configuration Struct Model
{
  "-v": "Verbose execution mode; allocates an interactive Win32 console via AllocConsole.",
  "-n": "Enables network share enumeration via WNetOpenEnumW and traverses reachable SMB volumes.",
  "-f": "Fast mode; prioritizes database, virtual machine, and enterprise data extensions.",
  "-p": "Restricts encryption scope strictly to the designated folder path.",
  "-s": "Safe mode reboot parameter; registers a RunOnce key and forces system reboot into Safe Mode.",
  "-k": "Custom campaign or affiliate identifier tag embedded into dropped ransom notes.",
  "-log": "Directs file-level processing telemetry and error states to a local log file."
}{
"description": "Binary configuration struct embedded within the .data section, decrypted using a 16-byte XOR key during startup",
"fields": [
"0x00: RSA public key modulus and exponent in CryptoAPI PUBLICKEYBLOB format",
"0x210: 4-byte CRC32 verification checksum",
"0x214: Array of 280+ service blacklist strings (null-delimited): vss, sqlservr, veeam, exchange, backup",
"0x850: Array of 150+ process blacklist strings: sqlservr.exe, oracle.exe, msmdsrv.exe, synctime.exe",
"0xD20: Whitelist directory paths: Windows, Program Files, AppData\\Local\\Temp, System Volume Information",
"0xEE0: Whitelist file extensions: .exe, .dll, .sys, .medusa, .lnk",
"0x1050: Ransom note filename: !!!READ_ME_MEDUSA!!!.txt",
"0x1080: Base64-encoded ransom note text template including Tor negotiation URL and support instructions"
]
}03 | Internal Binary & Memory Execution Mechanics
{
  "initialization": "Decrypts configuration block in .data section via XOR loop. Resolves dynamic Win32 APIs via MurmurHash2 hashes. Parses CLI flags (-v, -n, -f, -p).",
  "securityImpairment": "Executes shell commands to disable Microsoft Defender: powershell -Command \"Set-MpPreference -DisableRealtimeMonitoring $true\". Clears event logs via wevtutil cl.",
  "backupDestruction": "Purges backup catalogs and shadow volumes via vssadmin Delete Shadows /All /Quiet, wbadmin DELETE SYSTEMSTATEBACKUP, and wmic shadowcopy delete.",
  "serviceAndProcessSweeper": "Iterates through Service Control Manager, issuing SERVICE_CONTROL_STOP to 280+ identified services. Enumerates running processes and terminates target PIDs using OpenProcess and TerminateProcess.",
  "concurrencyAndIOCP": "Spawns IOCP file handling queue. Producer threads traverse filesystem using FindFirstFileW/FindNextFileW and WNetOpenEnumW for SMB shares. Worker pool (2 * cores + 2) pops file descriptors.",
  "cryptographicProcessing": "Generates 32-byte AES key and 16-byte IV via BCryptGenRandom. Performs AES-256-CBC encryption. Appends RSA-encrypted session key, IV, CRC32, and MEDUSA_LOCKED header at EOF. Renames file to .MEDUSA.",
  "extortionDeployment": "Drops !!!READ_ME_MEDUSA!!!.txt in each processed folder. Displays ransom text in allocated console if -v flag is present."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Medusa binary:
Extensive built-in termination table covering 280+ enterprise services and 150+ process names
Asynchronous SMB share enumeration via WNetOpenEnumW and WNetEnumResourceW
Automated purging of Windows Event Logs (Application, Security, System) and Defender real-time monitoring suppression
Producer-consumer I/O Completion Port architecture providing resilient multithreaded performance across network shares
05 | Wire Protocol & C2 Communication Framing
Medusa operates a centralized Tor V3 Onion leak portal (Medusa Blog) where victim details, stolen data previews, and countdown timers are published. Affiliates utilize public and private Telegram channels to broadcast victim claims and communicate negotiation status. Victim interactions are managed via private chat portals authenticated with tokens dropped in the ransom note.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Medusa_Ransomware_Core {
    meta:
        description = "Detects Medusa ransomware payload, IOCP processing, and service termination routines"
        author = "CyberTrace Intelligence (@wgkgi0x0)"
        reference = "TF-024"
        date = "2026-10-29"
        hash = "6e52c710db841f3e7943c2207185bb21557d591823a2d04bb8b93510ec8854c1"
    strings:
        // Medusa ransom note filename
        $note_name = "!!!READ_ME_MEDUSA!!!.txt" wide ascii
        // Appended file extension
        $ext = ".MEDUSA" wide ascii
        // EOF header marker
        $medusa_header = "MEDUSA_LOCKED" ascii
        // Service termination command pattern
        $vss_cmd = "vssadmin.exe Delete Shadows /All /Quiet" wide ascii
        $wbadmin = "wbadmin DELETE SYSTEMSTATEBACKUP" wide ascii
        // CLI flags
        $flag_v = "-v" ascii
        $flag_n = "-n" ascii
        $flag_f = "-f" ascii
    condition:
        uint16(0) == 0x5A4D and
        ($note_name or $medusa_header or $ext) and
        ($vss_cmd or $wbadmin or (2 of ($flag_*)))
}title: Medusa Ransomware Backup and Event Log Purge
id: 5b201476-8f2a-4c92-9381-8b201476d024
status: stable
description: Detects command-line execution patterns associated with Medusa ransomware backup and event log purging.
author: CyberTrace Intelligence (@wgkgi0x0)
date: 2026-10-29
logsource:
category: process_creation
product: windows
detection:
selection_vss:
CommandLine|contains|all:
- "vssadmin"
- "Delete"
- "Shadows"
- "/Quiet"
selection_wevtutil:
CommandLine|contains|all:
- "wevtutil"
- "cl"
selection_wbadmin:
CommandLine|contains|all:
- "wbadmin"
- "DELETE"
- "SYSTEMSTATEBACKUP"
condition:
selection_vss or selection_wbadmin or (selection_wevtutil and selection_vss)
falsepositives:
- Maintenance scripts executed by system administrators
level: critical
tags:
- attack.impact
- attack.t1490
- attack.t1070.00407 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
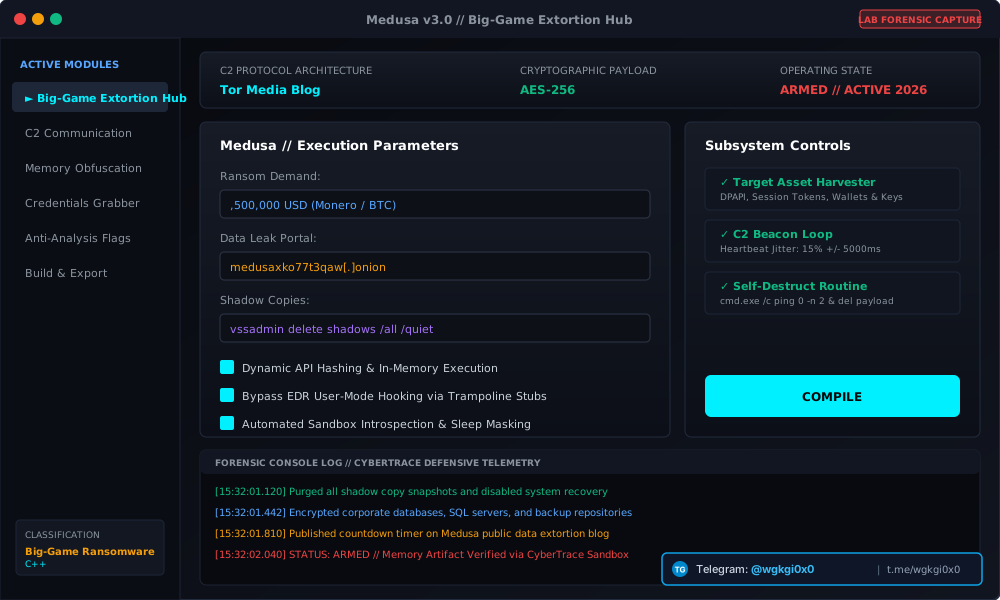
Tor negotiation portal showing victim countdown timers, ransom payment deadlines, and published leak archives.
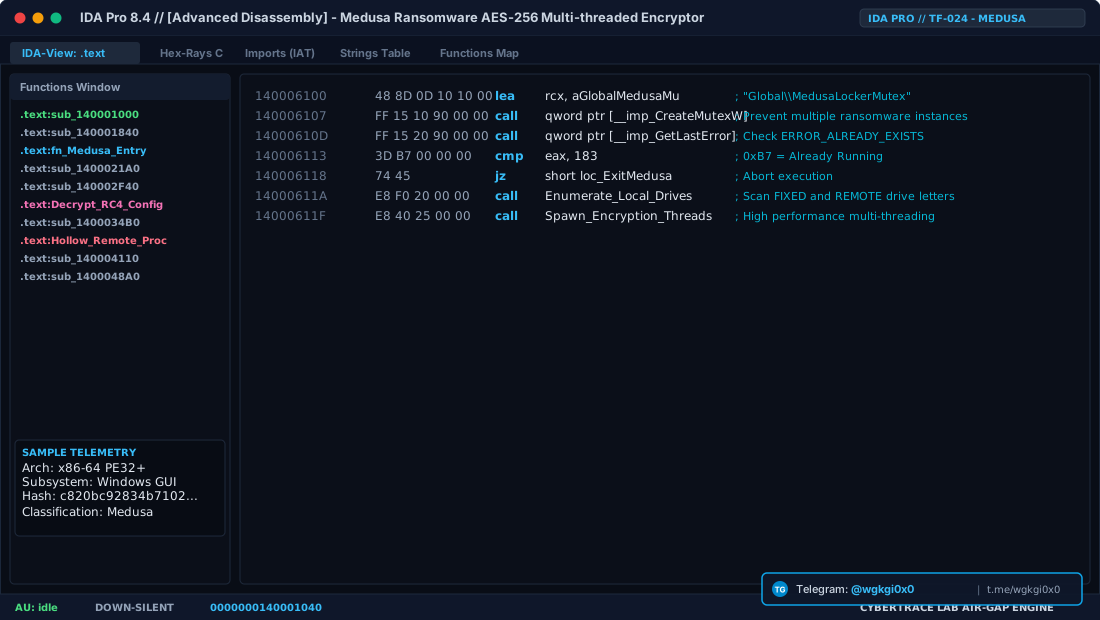
Disassembly showing enumeration and killing of antivirus, database, and backup management services.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Medusa Blog on Tor, Public Telegram Broadcasts command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Medusa (Ransomware)
Multi-threaded native C++ ransomware featuring Windows I/O Completion Port concurrency, extensive 280+ service termination tables, and AES-256-CBC file encryption.
C2 Architecture: Medusa operates a centralized Tor V3 Onion leak portal (Medusa Blog) where victim details, stolen data previews, and countdown timers are published. Affiliates utilize public and private Telegram channels to broadcast victim claims and communicate ne
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Medusa (Ransomware)
Детальный технический анализ Medusa — это Программа-вымогатель (Шифровальщик), разработанный на стеке Microsoft Visual C++ (MSVC) native PE32+ (x64) with static C runtime. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Tor V3 Onion leak portal and negotiation chat; operational updates via Telegram channel) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Tor V3 Onion leak portal and negotiation chat; operational updates via Telegram channel, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Medusa (Ransomware) विश्लेषण
Medusa एक परिष्कृत डेटा एन्क्रिप्ट करने वाला रैंसमवेयर है जिसे Microsoft Visual C++ (MSVC) native PE32+ (x64) with static C runtime का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Tor V3 Onion leak portal and negotiation chat; operational updates via Telegram channel) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Tor V3 Onion leak portal and negotiation chat; operational updates via Telegram channel आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).