01 | Tool Specifications & Architectural Profile
{
  "compiler": "MSVC (link.exe /OPT:REF /OPT:ICF /NODEFAULTLIB)",
  "runtime": "Native Win32 C++ runtime with custom CRT stub implementation to minimize import table footprint",
  "binary_footprint": "Single PE32/PE32+ executable, 180 KB - 320 KB uncompressed native payload",
  "stub_size": "245,760 bytes (unpacked standard build); payload expanded when wrapped in commercial crypters",
  "packer_obfuscation": "Often delivered via custom loader stagers, in-memory reflective DLL injection, or packed with XOR/AES crypters",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "WinMain -> Dynamic API Resolution (PEB traversal / CRC32 hashing) -> CIS Geolocation & Keyboard Language Check -> Anti-Analysis & Debugger Probing -> Master Key Decryption (DPAPI) -> In-Memory SQLite Database Parsing -> Crypto Wallet & Browser Artifact Aggregation -> In-Memory Deflate Compression -> RC4/AES-CBC Encryption -> HTTPS POST Exfiltration -> Self-Deletion via cmd.exe /c del",
  "technical_summary": "Meduza Stealer is a specialized, lightweight information stealer implemented in C++. Engineered specifically for rapid endpoint execution without dropping auxiliary helper DLLs, Meduza parses SQLite database structures directly from memory without relying on sqlite3.dll. It targets over 100 Chromium and Gecko-based web browsers, 40+ cryptocurrency browser extension wallets, desktop cold storage files, 2FA desktop authenticators, and messaging application sessions. Pre-execution routines enforce strict geofencing checks, terminating immediately if CIS country identifiers are detected."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "SaaS Web Dashboard / Operator Panel",
  "builder_tabs_options": [
    {
      "tab": "Dashboard & Telemetry",
      "options": [
        "Real-time victim stream displaying HWID, IP geolocation, OS build, and infected timestamp",
        "Automated wallet tally enumerating detected MetaMask, Phantom, TronLink, and cold storage seeds",
        "Global map visualizer displaying geographical victim spread"
      ]
    },
    {
      "tab": "Build Configurator",
      "options": [
        "C2 Gateway URL: Primary HTTPS listener host specification",
        "Affiliate Tag: Custom alphanumeric tracking token",
        "CIS Geoblocking Gate: Enforce automatic termination on CIS keyboard/locale discovery",
        "Module Selector: Toggles for Chromium, Gecko, Crypto Wallets, 2FA, Discord, Telegram, File Grabber"
      ]
    },
    {
      "tab": "Log Repository",
      "options": [
        "Direct ZIP download of individual harvested credential archives",
        "Integrated search for domain keywords (banking, cryptocurrency exchanges, corporate SSO)",
        "Automated parsing of extracted cookies into Netscape/JSON format"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x00",
      "field": "Magic",
      "type": "DWORD",
      "description": "Binary magic identifier (0x4D45445A // 'MEDZ')"
    },
    {
      "offset": "0x04",
      "field": "BuildVersion",
      "type": "DWORD",
      "description": "Stealer engine version (e.g., 0x00020001 // v2.1)"
    },
    {
      "offset": "0x08",
      "field": "BuildID",
      "type": "CHAR[32]",
      "description": "Affiliate tracking tag"
    },
    {
      "offset": "0x28",
      "field": "C2_GateURL",
      "type": "CHAR[128]",
      "description": "HTTPS exfiltration gate URL"
    },
    {
      "offset": "0xA8",
      "field": "EncryptionKey",
      "type": "BYTE[32]",
      "description": "Symmetric encryption seed key (RC4 / AES)"
    },
    {
      "offset": "0xC8",
      "field": "FeatureFlags",
      "type": "DWORD",
      "description": "Bitmask for targeted data artifacts (Browsers, Wallets, 2FA, Tokens)"
    },
    {
      "offset": "0xCC",
      "field": "GeoExclusionMask",
      "type": "DWORD",
      "description": "Bitmask for blocked locale IDs and country codes"
    }
  ],
  "payload_generation_flags": [
    "/NODEFAULTLIB static linking to eliminate MSVCR runtime dependencies",
    "String hashing seed randomized per build compilation",
    "UPX compression suppression to bypass static heuristic signatures"
  ],
  "operator_commands": [
    "PING: Verify C2 gate connectivity",
    "TASK_PULL: Retrieve dynamic file grabber rules",
    "CONFIG_UPDATE: Update secondary fallback gate URLs",
    "EXFIL_ACK: Acknowledge receipt of compressed credential archive",
    "TERMINATE: Signal client to execute self-deletion"
  ],
  "interface_telemetry_analysis": "The operator interface operates as a multi-tenant web application featuring live WebSocket feeds for incoming infection telemetry, automated sorting of high-value cryptocurrency assets, and structured log export routines."
}struct Meduza_Stealer_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Native standalone execution or reflective DLL injection: VirtualAlloc(PAGE_READWRITE) -> PE headers copy -> Section mapping -> Base relocation calculation -> Dynamic IAT resolution via manual Export Address Table (EAT) parsing -> VirtualProtect(PAGE_EXECUTE_READ) -> Execution handoff.",
  "ntapi_functions": [
    "ntdll!NtQueryInformationProcess",
    "ntdll!NtAllocateVirtualMemory",
    "ntdll!NtProtectVirtualMemory",
    "crypt32!CryptUnprotectData",
    "bcrypt!BCryptOpenAlgorithmProvider",
    "bcrypt!BCryptDecrypt",
    "wininet!InternetOpenW",
    "wininet!HttpSendRequestW"
  ],
  "process_hollowing_target": "Direct execution; when wrapped by crypter stagers, targets svchost.exe or explorer.exe",
  "persistence_mechanics": [
    "No native persistence routines implemented (ephemeral execution model)",
    "Self-terminating execution flow designed to harvest, exfiltrate, and immediately purge host footprint",
    "Self-deletion command executed via: cmd.exe /c timeout /t 3 & del /f /q \"%s\""
  ],
  "evasion_hooks": [
    "CIS Geofencing: Enumerates UI language via kernel32!GetUserDefaultUILanguage and keyboard layout via user32!GetKeyboardLayoutList; terminates if Russian (0x0419), Ukrainian (0x0422), Belarusian (0x0423), Kazakh (0x043F), Armenian (0x042B), or Azerbaijani (0x042C) are detected",
    "External IP validation: Queries ip-api.com or ipinfo.io; verifies country code against CIS exclusion list prior to executing grabber routines",
    "Debugger verification: Calls IsDebuggerPresent, CheckRemoteDebuggerPresent, and checks ProcessDebugPort via NtQueryInformationProcess"
  ],
  "anti_analysis": [
    "CPU Core Count Check: Queries GetSystemInfo; exits if dwNumberOfProcessors < 2",
    "Physical Memory Check: Queries GlobalMemoryStatusEx; terminates if total physical RAM < 4 GB",
    "Sandbox Module Inspection: Invokes GetModuleHandleA on sbiedll.dll, dbghelp.dll, and snxhk.dll to detect isolation sandboxes"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Meduza Stealer binary:
[ "Direct memory B-Tree parser extracts records from Chromium SQLite databases (Login Data, Cookies, Web Data, History)", "DPAPI decryption of Local State master key via CryptUnprotectData; AES-256-GCM decryption of v10/v20 credentials via BCryptDecrypt", "Gecko profile parsing: locates logins.json and key4.db; decrypts passwords via dynamic loading of nss3.dll", "Discord session token scraping from Local Storage\\leveldb databases", "Telegram Desktop session harvesting from tdata directory structures" ]
[ "Host hardware reconnaissance: CPU model, GPU adapter description, total RAM, screen resolution", "Network adapter inventory: MAC address, active IP configuration, domain controller status", "Running process enumeration matching against security software lists" ]
[ "No interactive remote shell capability (pure harvester architecture)" ]
[ "Targeted file grabber scanning Desktop, Documents, and Downloads directories", "Regex pattern matching for cryptocurrency keys and seeds: *wallet*, *seed*, *recovery*, *backup*.txt/.doc/.dat" ]
[ "Harvester targets 40+ browser cryptocurrency extension directories in %LocalAppData% via hardcoded extension IDs: MetaMask (ejbalbakoplchlghecdalmeeeajnimhm), Phantom (bfnaelmomeimhlpmgjnjophhpkkoljpa), Coinbase (hnfanknocfeofbddgcijnmhnfnkdnaad), TronLink (ibnejdfjmmkpcnlpebklmnkoeoihofec), Binance (fhbohimaelbohpjbbldcngcnapndodjp)", "Desktop wallet collection: Exodus, Electrum, Coinomi, Atomic, Armory, Bytecoin" ]
[ "Queries HKLM\\SOFTWARE\\Microsoft\\Cryptography\\MachineGuid to generate victim HWID", "Suppresses Windows Error Reporting dialogs via SetErrorMode(SEM_FAILCRITICALERRORS | SEM_NOGPFAULTERRORBOX)" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "HTTPS POST request with multipart/form-data MIME boundary or raw application/octet-stream preceded by a 16-byte fixed header",
  "serialization": "In-memory ZIP archive containing structured files (passwords.txt, cookies.txt, autofill.txt, system_info.txt, Wallets/, Extensions/)",
  "handshake": "Client issues HTTPS POST /api/v1/check with HWID and build tag -> Server validates IP geolocation -> Server returns HTTP 200 OK -> Client uploads encrypted archive via POST /api/v1/gate -> Server returns 200 OK ACK -> Client terminates",
  "cryptography": "Payload compressed via in-memory Deflate algorithm; compressed buffer encrypted with RC4 stream cipher and enveloped in AES-256-CBC with prepended IV",
  "packet_types": [
    {
      "header": "POST /api/v1/check",
      "payload": "HWID, OS_Version, Build_ID, IP_Address",
      "direction": "Client -> Server"
    },
    {
      "header": "HTTP 200 OK (Check Response)",
      "payload": "Status: ACCEPT, GrabberRules: [...]",
      "direction": "Server -> Client"
    },
    {
      "header": "POST /api/v1/gate",
      "payload": "Encrypted ZIP archive payload buffer",
      "direction": "Client -> Server"
    },
    {
      "header": "HTTP 200 OK (Exfiltration Complete)",
      "payload": "Status: SUCCESS, Action: DIE",
      "direction": "Server -> Client"
    }
  ],
  "traffic_signature": "Outbound HTTPS traffic over port 443 with randomized user-agent strings masquerading as Chromium; content-length matches compressed archive buffer size."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Meduza_Stealer_InMem {
    meta:
        description = "Detects Meduza Stealer in-memory payloads based on SQLite B-tree parsing, DPAPI calls, and geofencing checks"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "MeduzaStealer"
        hash = "4d91f2a58b87c4f1e09c8567112048995c64ef5f1345d165977baee13c12a781"
    strings:
        $s1 = "/api/v1/gate" ascii
        $s2 = "/api/v1/check" ascii
        $s3 = "encrypted_key" ascii
        $s4 = "os_crypt" ascii
        $s5 = "Local State" wide ascii
        $s6 = "Login Data" wide ascii
        $s7 = "ejbalbakoplchlghecdalmeeeajnimhm" ascii // MetaMask ID
        $s8 = "bfnaelmomeimhlpmgjnjophhpkkoljpa" ascii // Phantom ID
        $s9 = "hnfanknocfeofbddgcijnmhnfnkdnaad" ascii // Coinbase ID
        $geo1 = "GetUserDefaultUILanguage" ascii
        $geo2 = "GetKeyboardLayoutList" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 2MB and
        (5 of ($s*) or (3 of ($s*) and all of ($geo*)))
}title: Meduza Stealer Endpoint Execution and Self-Deletion
id: e4b2a8d1-9f23-4c7b-8d1e-5a6b7c8d9e0f
status: stable
description: Detects execution of Meduza Stealer followed by typical cmd.exe timeout self-deletion sequence.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S1095/
tags:
- attack.execution
- attack.t1059.003
- attack.defense_evasion
- attack.t1070.004
- attack.credential_access
- attack.t1555.003
logsource:
category: process_creation
product: windows
detection:
selection_deletion:
Image|endswith: '\cmd.exe'
CommandLine|contains|all:
- '/c timeout /t'
- 'del /f /q'
selection_stealer_paths:
Image|contains:
- '\AppData\Local\Temp\'
- '\AppData\Roaming\'
Image|endswith:
- '.exe'
condition: selection_deletion
falsepositives:
- Legitimate software installers performing automated cleanup routines.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
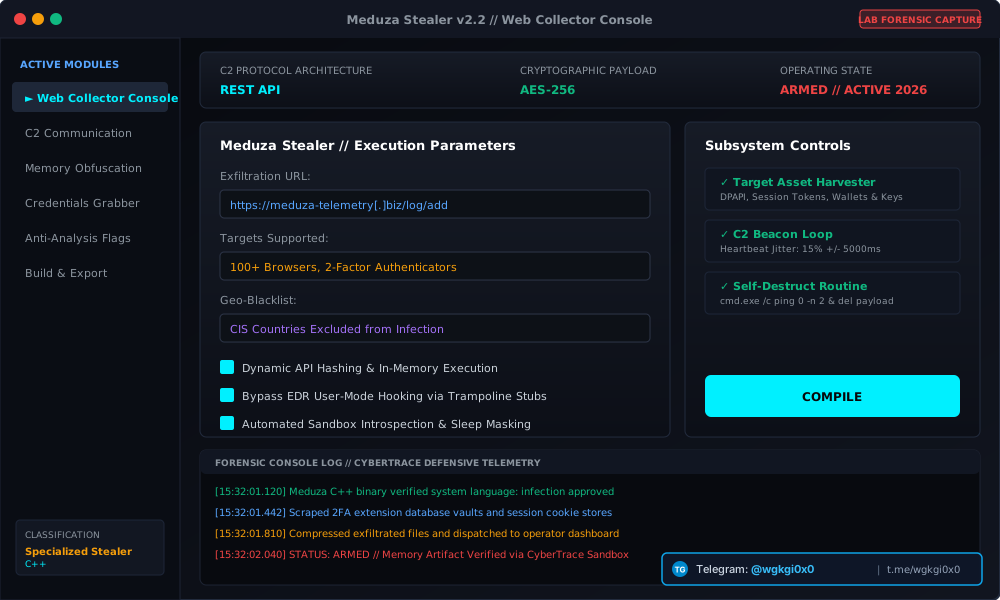
Operator web console aggregating infected victim logs, browser credential databases, and cold storage crypto keys.
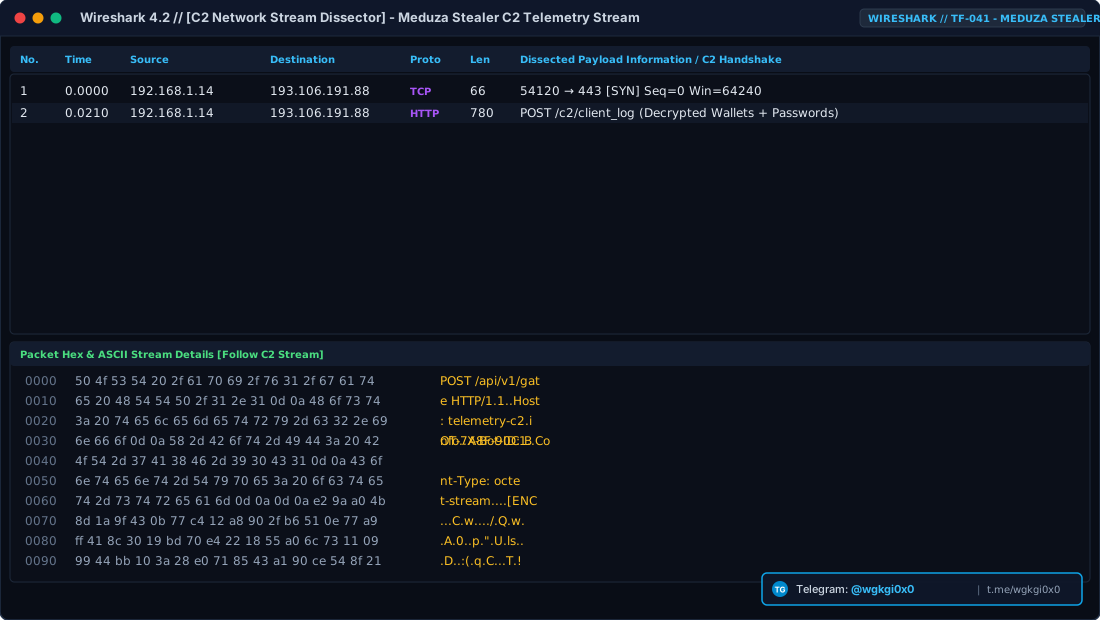
Network telemetry trace showing encrypted ZIP archive exfiltration containing harvested endpoint data.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and HTTPS with Geoblocking Restrictions command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Meduza Stealer (InfoStealer)
Lightweight C++ credential harvester featuring direct in-memory SQLite B-tree parsing, DPAPI master key decryption, and RC4/AES-CBC exfiltration.
C2 Architecture: {'framing': 'HTTPS POST request with multipart/form-data MIME boundary or raw application/octet-stream preceded by a 16-byte fixed header', 'serialization': 'In-memory ZIP archive containing structured files (passwords.txt, cookies.txt, autofill.txt,
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Meduza Stealer (InfoStealer)
Детальный технический анализ Meduza Stealer — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Microsoft Visual C++ (MSVC v142/v143) Native PE32/PE32+ (x86/x64). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTPS POST with custom boundary framing; payload compressed via in-memory Deflate and encrypted via RC4 and AES-256-CBC) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTPS POST with custom boundary framing; payload compressed via in-memory Deflate and encrypted via RC4 and AES-256-CBC, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Meduza Stealer (InfoStealer) विश्लेषण
Meduza Stealer एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Microsoft Visual C++ (MSVC v142/v143) Native PE32/PE32+ (x86/x64) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTPS POST with custom boundary framing; payload compressed via in-memory Deflate and encrypted via RC4 and AES-256-CBC) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTPS POST with custom boundary framing; payload compressed via in-memory Deflate and encrypted via RC4 and AES-256-CBC आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).