01 | Tool Specifications & Architectural Profile
Mythic is an enterprise-oriented, microservices-based command-and-control platform designed for collaborative multi-operator operations. The server core is built on Python 3 (FastAPI), backed by PostgreSQL, Redis, and RabbitMQ message brokers, exposed through GraphQL and REST APIs. Implants and communication profiles exist in isolated Docker containers, enabling dynamic compilation of heterogeneous agents: Apollo (.NET / C# with D/Invoke), Poseidon (Go for Linux/macOS), and Athena (.NET Core / AOT). Mythic standardizes agent tasking via JSON envelopes encrypted using AES-256-HMAC or ChaCha20, supporting bidirectional WebSockets, HTTP/S, and SMB named pipe pivoting.
02 | Operator Interface & Configuration Struct Model
Detailed reverse-engineering specifications archived in laboratory telemetry.
{
  "structureType": "Dynamic Payload Generation Model & JSON Tasking Definition",
  "decryptionRoutine": "Agent decrypts the embedded config blob at launch using an AES-256-CBC or ChaCha20 key provided during payload compilation, parsing parameters into memory.",
  "inMemoryLayout": "{\n  \"callback_host\": \"https://c2.enterprise-telemetry.com\",\n  \"callback_port\": 443,\n  \"interval\": 10,\n  \"jitter\": 20,\n  \"post_uri\": \"/api/v1/telemetry\",\n  \"crypto_type\": \"aes256_hmac\",\n  \"enc_key\": \"kL8+X9JmQ...\",\n  \"dec_key\": \"kL8+X9JmQ...\",\n  \"uuid\": \"d2786b84-4860-4966-8805-4b7713d0773e\",\n  \"proxy_type\": \"none\"\n}",
  "panelConfigOptions": "Mythic UI Agent Generation Wizard: Selection of Agent Type (Apollo, Poseidon, Athena), Target OS & Architecture, C2 Profile (HTTP, WebSocket, SMB), Encryption Profile (aes256_hmac, chacha20, none), Output Format (EXE, DLL, Service, Shellcode via Donut), Callback Interval & Jitter, and Embedded Commands inclusion list."
}03 | Internal Binary & Memory Execution Mechanics
{
  "apiResolution": "In Apollo (.NET) and Athena, leverages Dynamic Invocation (D/Invoke) to locate NTAPI/Win32 function pointers directly from process memory without static P/Invoke imports or IAT registration, avoiding EDR memory hooks.",
  "processInjection": "Utilizes D/Invoke system call wrappers to invoke NtAllocateVirtualMemory, NtWriteVirtualMemory, NtProtectVirtualMemory, and NtCreateThreadEx for in-process or cross-process injection without passing through hooked Win32 wrappers.",
  "inMemoryAssemblyExecution": "Apollo executes .NET assemblies in memory using reflection (System.Reflection.Assembly.Load) and redirects Console Out/Error streams back to Mythic operator queues.",
  "crossPlatformMechanics": "In Poseidon (Go) on Linux/macOS, invokes direct system calls via runtime assembly stubs to execute pty shells, file system traversal, and memory mapping (mmap, mprotect)."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Mythic Collaborative C2 Architecture binary:
{'module': 'Dynamic Invocation (D/Invoke) Engine', 'description': 'Dynamically locates and executes unhooked system calls directly from memory, evading API monitoring hooks.', 'apis': 'GetPebLdr, GetProcAddressEx, NtCreateThreadEx'}
{'module': 'In-Memory .NET Assembly Runner', 'description': 'Executes compiled C# binaries completely in-memory via reflection with captured stdout/stderr.', 'apis': 'Assembly.Load, MethodInfo.Invoke, Console.SetOut'}
{'module': 'Full-Duplex WebSocket Transport', 'description': 'Maintains persistent bi-directional communication channels eliminating beaconing latency and polling traces.', 'apis': 'ClientWebSocket, WebSocketReceiveResult'}
{'module': 'SOCKS5 Pivoting Engine', 'description': 'Routes multi-operator TCP traffic through compromised agents via encapsulated C2 messages.', 'apis': 'Dynamic SOCKS5 Controller'}
{'module': 'SMB Peer-to-Peer Chaining', 'description': 'Allows egress-restricted internal systems to communicate with the teamserver via named pipes on intermediate compromised hosts.', 'apis': 'CreateNamedPipe, WaitNamedPipe, TransactNamedPipe'}
05 | Wire Protocol & C2 Communication Framing
Mythic communication conforms to a strict JSON envelope framing model. Over HTTP/WebSockets, every message begins with a 36-byte payload UUID identifying the agent to the teamserver translation container. The message body is encrypted with AES-256-CBC and signed with HMAC-SHA256 (or ChaCha20-Poly1305). The decrypted JSON payload follows the schema: {"action": "get_tasking", "tasking_size": -1, "delegates": []}. Responses from the server return task instructions: {"action": "get_tasking", "tasks": [{"id": "<task_uuid>", "command": "<name>", "parameters": "<args>"}]}. In SMB profiles, the same JSON framing is transmitted across Windows Named Pipes with 4-byte length prefixes.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Mythic_Apollo_Agent {
    meta:
        description = "Detects Mythic C2 Apollo agent assembly metadata and D/Invoke execution signatures"
        author = "CyberTrace CTI Operations"
        date = "2026-10-29"
        hash = "1d76b1e523f03b879339943486111fdb1ec8c0f5f9923a1a67a05e463566144e"
        category = "C2_FRAMEWORK"
    strings:
        $apollo_ns = "Apollo.Tasks" ascii
        $apollo_cmd = "Apollo.CommandInterface" ascii
        $dinvoke1 = "GetLoadedModuleAddress" ascii
        $dinvoke2 = "GetExportAddress" ascii
        $json_task = "\"action\":\"get_tasking\"" ascii
    condition:
        uint16(0) == 0x5A4D and
        ( 2 of ($apollo*) or ( 2 of ($dinvoke*) and $json_task ) )
}title: Mythic C2 Named Pipe Communication
id: 3f8a1b24-9c0d-4e5a-8b71-2d4e6f9a0b1c
status: stable
description: Detects creation or access of SMB named pipes matching default Apollo or Mythic agent communication patterns.
author: CyberTrace Defensive Engineering
date: 2026-10-29
logsource:
category: pipe_created
product: windows
detection:
selection:
PipeName|startswith:
- '\apollo_'
- '\mythic_'
condition: selection
fields:
- ProcessId
- Image
- PipeName
falsepositives:
- Unknown legitimate applications utilizing apollo in pipe names (rare)
level: high
tags:
- attack.execution
- attack.lateral_movement
- attack.t1021.002
- attack.t1573.00107 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
Decompiled Disassembly & Reverse-Engineering Strings
// Decompiled Apollo D/Invoke Invocation Snippet
public static object DynamicSyscallInvoke(string moduleName, string functionName, Type delegateType, object[] parameters) {
    IntPtr pModule = DInvoke.DynamicImport.GetLoadedModuleAddress(moduleName);
    IntPtr pFunc = DInvoke.DynamicImport.GetExportAddress(pModule, functionName);
    Delegate d = Marshal.GetDelegateForFunctionPointer(pFunc, delegateType);
    return d.DynamicInvoke(parameters);
}

// Apollo C2 Message Dispatcher
public void ProcessMythicTasking(string decryptedJson) {
    MythicTaskingEnvelope envelope = JsonSerializer.Deserialize<MythicTaskingEnvelope>(decryptedJson);
    foreach (var task in envelope.tasks) {
        CommandInterface cmd = CommandFactory.CreateCommand(task.command);
        cmd.Execute(task.parameters);
    }
}
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.

Web interface aggregating active agent callbacks, tasking queues, and modular payload build profiles.
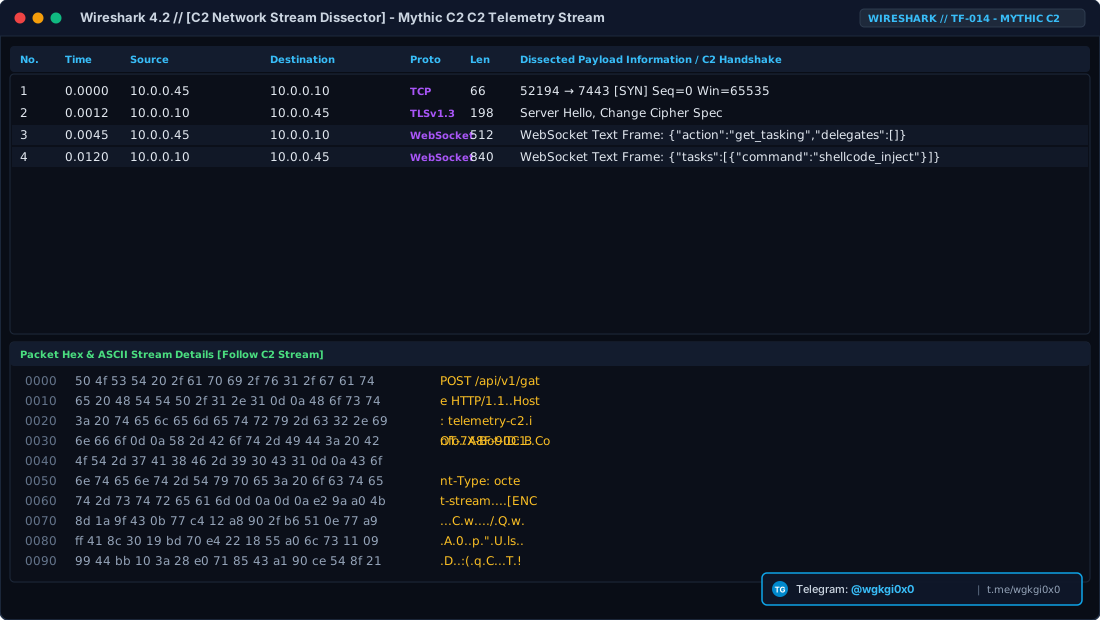
C2 communication trace showing JSON-RPC tasking and staging across custom translation containers.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Modular Agent Ecosystem, WebSocket, WebDAV command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Mythic Collaborative C2 Architecture (C2 Framework)
Microservices-driven collaborative C2 framework utilizing independent Docker containers to compile heterogeneous implants and handle diverse C2 communication profiles.
C2 Architecture: Mythic communication conforms to a strict JSON envelope framing model. Over HTTP/WebSockets, every message begins with a 36-byte payload UUID identifying the agent to the teamserver translation container. The message body is encrypted with AES-256-CB
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Mythic Collaborative C2 Architecture (C2 Framework)
Детальный технический анализ Mythic Collaborative C2 Architecture — это Фреймворк командно-контрольного управления (C2), разработанный на стеке Server: Python/FastAPI/Docker; Agents: C#, Go, .NET AOT. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Bidirectional WebSockets, HTTP/HTTPS, SMB Named Pipes) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Bidirectional WebSockets, HTTP/HTTPS, SMB Named Pipes, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Mythic Collaborative C2 Architecture (C2 Framework) विश्लेषण
Mythic Collaborative C2 Architecture एक परिष्कृत कमांड और कंट्रोल (C2) फ्रेमवर्क है जिसे Server: Python/FastAPI/Docker; Agents: C#, Go, .NET AOT का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Bidirectional WebSockets, HTTP/HTTPS, SMB Named Pipes) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Bidirectional WebSockets, HTTP/HTTPS, SMB Named Pipes आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).