01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C++ (MSVC 2010 - 2019)",
  "runtime": "Win32 C Runtime (MSVCR100.dll / VCRUNTIME140.dll) and Windows Subsystem API",
  "binary_footprint": "Digitally signed multi-binary commercial application suite (client32.exe, w95hook.dll, TCBIC.DLL, PCICHEK.DLL), totaling 12 MB - 25 MB on disk",
  "stub_size": "890,880 bytes (client32.exe typical binary footprint)",
  "packer_obfuscation": "Commercial binaries are uncompressed; delivery containers utilize obfuscated JavaScript (SocGholish / FakeUpdates), PowerShell stagers, or BAT wrappers",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "Delivery script drops full NetSupport application directory -> Script writes customized client32.ini configuration -> Execution of client32.exe -> Loading of hook DLLs (w95hook.dll) -> Config integrity checksum verification -> Silent reverse connection initiation to operator Gateway server",
  "technical_summary": "NetSupport RAT is the malicious deployment of the legitimate, commercially available NetSupport Manager remote administration software. Threat actors weaponize authentic, digitally signed client32.exe executables by pairing them with covert configuration files (client32.ini / pcap.ini) that enforce silent execution, suppress user notifications, hide system tray icons, and route remote control sessions to actor-controlled NetSupport Gateway servers."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "NetSupport Manager Control Console (Commercial Win32 GUI)",
  "builder_tabs_options": [
    {
      "tab": "Gateway Configuration",
      "options": [
        "Gateway Address: Hostname or IP address of the NetSupport Gateway server",
        "Gateway Port: TCP listening port (default: 3085, or mapped to 80/443)",
        "Gateway Key: Pre-shared authentication passphrase string",
        "Secondary Gateway: Failover IP address for redundant communication"
      ]
    },
    {
      "tab": "Client Stealth Settings (client32.ini)",
      "options": [
        "QuietMode: Set to 1 to suppress balloon notifications and alert messages",
        "HideIcon: Set to 1 to remove the client icon from the Windows system tray",
        "DisableChat: Set to 1 to block victim-facing chat dialog windows",
        "NoConfirm: Set to 1 to automatically allow remote operator connections without victim approval"
      ]
    },
    {
      "tab": "Deployment Automation",
      "options": [
        "Scripted Stager: JavaScript / VBScript unpacking NetSupport archive to %APPDATA%",
        "Persistence Hook: Creation of Windows shortcut (.lnk) in Startup folder or Registry Run key",
        "Process Renaming: Renaming client32.exe to benign process names (dwm.exe, svchost.exe, curl.exe)"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "INI Header",
      "type": "string",
      "field": "[Client]",
      "description": "Client profile parameters"
    },
    {
      "offset": "INI Field",
      "type": "int",
      "field": "ClientType=1",
      "description": "Defines standalone workstation client mode"
    },
    {
      "offset": "INI Header",
      "type": "string",
      "field": "[Gateway]",
      "description": "Gateway connection directives"
    },
    {
      "offset": "INI Field",
      "type": "string",
      "field": "GatewayAddress=<IP>",
      "description": "C2 Gateway server IP or domain address"
    },
    {
      "offset": "INI Field",
      "type": "int",
      "field": "GatewayPort=443",
      "description": "C2 Gateway listening port"
    },
    {
      "offset": "INI Field",
      "type": "string",
      "field": "GatewayKey=<HASH>",
      "description": "Encrypted pre-shared key for Gateway authentication"
    },
    {
      "offset": "INI Header",
      "type": "string",
      "field": "[Security]",
      "description": "Stealth and security toggles"
    },
    {
      "offset": "INI Field",
      "type": "int",
      "field": "QuietMode=1",
      "description": "Suppresses client balloon popups and warning dialogues"
    },
    {
      "offset": "INI Field",
      "type": "int",
      "field": "HideIcon=1",
      "description": "Suppresses system tray icon in explorer.exe notification area"
    },
    {
      "offset": "INI Field",
      "type": "string",
      "field": "CheckSum=<HEX>",
      "description": "Integrity checksum protecting INI contents from tampering"
    }
  ],
  "payload_generation_flags": [
    "Delivery Mechanism: SocGholish / FakeUpdates drive-by compromise presenting fake browser update ZIP",
    "Script Extraction: Obfuscated JS extracts bundled client32.exe, w95hook.dll, and configuration to %APPDATA%",
    "Persistence Execution: Creates scheduled task or Run registry entry launching client32.exe silently"
  ],
  "operator_commands": [
    "View / Remote Control: Interactive desktop capture and virtual mouse/keyboard input injection",
    "File Transfer: Bi-directional file upload and download across client and operator machines",
    "Inventory Explorer: Gathers hardware configuration, installed software list, and network adapter details",
    "Remote Execute: Spawns arbitrary processes and shell commands under the client user context",
    "Audio Monitoring: Streams victim microphone input to operator console"
  ],
  "interface_telemetry_analysis": "The operator interface utilizes the fully featured NetSupport Control GUI, providing interactive remote desktop viewing, multi-client thumbnail grids, file system browsing, and inventory reporting without requiring custom malware panel development."
}struct NetSupport_RAT_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Execution via Living-off-the-Land (LotL): Malicious delivery script (JS/PowerShell) writes the complete legitimate NetSupport directory into %APPDATA%\\NetSupport or %TEMP% -> Creates configured client32.ini -> Spawns client32.exe using WScript.Shell.Run or Start-Process -> client32.exe dynamically loads hook libraries (w95hook.dll) -> Connects to Gateway.",
  "ntapi_functions": [
    "kernel32!CreateProcessW",
    "kernel32!LoadLibraryA",
    "user32!SetWindowsHookExW",
    "user32!GetDC",
    "gdi32!CreateCompatibleBitmap",
    "gdi32!BitBlt",
    "ws2_32!connect",
    "ws2_32!send"
  ],
  "ini_checksum_validation": "Configuration Integrity Check: NetSupport Manager includes an internal checksum calculation mechanism protecting client32.ini. The client computes a CRC32 / proprietary byte hash of specified INI fields combined with a static internal salt. If the configuration is manually altered without recalculating the valid CheckSum value (or configuring pcap.ini correctly), client32.exe detects configuration corruption and refuses to start. Threat actors utilize custom keygen scripts to compute valid checksums when building deployment packages.",
  "remote_desktop_hooks": "Screen Capture & Input Injection: Screen capture is performed using Win32 GDI calls (GetDC, CreateCompatibleDC, BitBlt), capturing frame differentials and compressing bitmaps via proprietary RLE / JPEG algorithms. Keystroke logging and input handling are implemented via w95hook.dll, which installs global keyboard and message hooks (WH_KEYBOARD and WH_GETMESSAGE) via SetWindowsHookExW to record user input and inject remote operator keystrokes.",
  "anti_analysis": "Relying on legitimate, digitally signed binaries defeats standard file reputation and code signing heuristics; stealth configuration flags prevent end-user notification."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the NetSupport RAT binary:
[ "Full-motion remote desktop streaming with interactive mouse and keyboard virtualization", "Low-level keyboard hook (w95hook.dll) capturing global keystrokes and application titles", "Real-time audio monitoring capturing endpoint microphone streams", "Webcam capture and screen thumbnail broadcasting to NetSupport Control" ]
[ "Remote file management: upload, download, file execution, and deletion", "Process manager: viewing, suspending, and killing active processes", "Registry editor: remote inspection and modification of Windows registry keys", "Command execution: spawning interactive command-line sessions and scripts" ]
[ "Execution of authentic, validly signed binaries from NetSupport Ltd.", "Suppression of system tray notification icons via HideIcon=1 configuration directive", "Suppression of warning dialogs and connection alerts via QuietMode=1", "Renaming of client32.exe to common Windows system process names" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Proprietary binary packet framing or HTTP POST encapsulation routed through the NetSupport Gateway server on TCP port 443, 80, or 3085.",
  "serialization": "Proprietary structured binary protocol encoding command identifiers, screen coordinates, compressed bitmap deltas, and keystroke codes.",
  "handshake": "Client initiates TCP connection to Gateway -> Sends client registration header containing machine name, MAC address, and GatewayKey hash -> Gateway validates key and assigns client session ID -> Session routed to operator Control console.",
  "cryptography": "Proprietary encryption utilizing DES or Blowfish algorithms keyed with the pre-shared GatewayKey and SecurityKey strings configured in client32.ini.",
  "packet_types": [
    "0x50: Protocol initiation and client registration handshake",
    "0x52: Remote desktop display delta packet containing compressed tile updates",
    "0x53: Input event packet containing virtual key codes and mouse coordinates",
    "0x54: File transfer block packet carrying chunked binary data"
  ],
  "traffic_signature": "Initial HTTP POST request to /scripts/gateway.dll?cmd=register or raw TCP connection presenting proprietary NetSupport magic bytes."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_NetSupport_Weaponized_Config {
    meta:
        description = "Detects weaponized NetSupport Manager configuration files and stealth parameters"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        reference = "TF-033"
    strings:
        $ini_header = "[Client]"
        $gateway_tag = "GatewayAddress="
        $quiet_mode = "QuietMode=1"
        $hide_icon = "HideIcon=1"
        $dll_marker = "w95hook.dll"
    condition:
        ($ini_header and $gateway_tag and ($quiet_mode or $hide_icon)) or ($dll_marker and $quiet_mode)
}title: Weaponized NetSupport Client Execution from Suspicious Directory
id: 4d2e1a9b-3847-4f12-9c1a-8294a5e01b23
status: stable
description: Detects execution of NetSupport client32.exe from non-standard user profile directories associated with malware stagers.
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
product: windows
category: process_creation
detection:
selection:
Image|endswith:
- '\client32.exe'
Image|contains:
- '\AppData\'
- '\Temp\'
- '\Users\Public\'
condition: selection
fields:
- Image
- CommandLine
- ParentImage
falsepositives:
- Legitimate non-standard administrative installations of NetSupport Manager
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
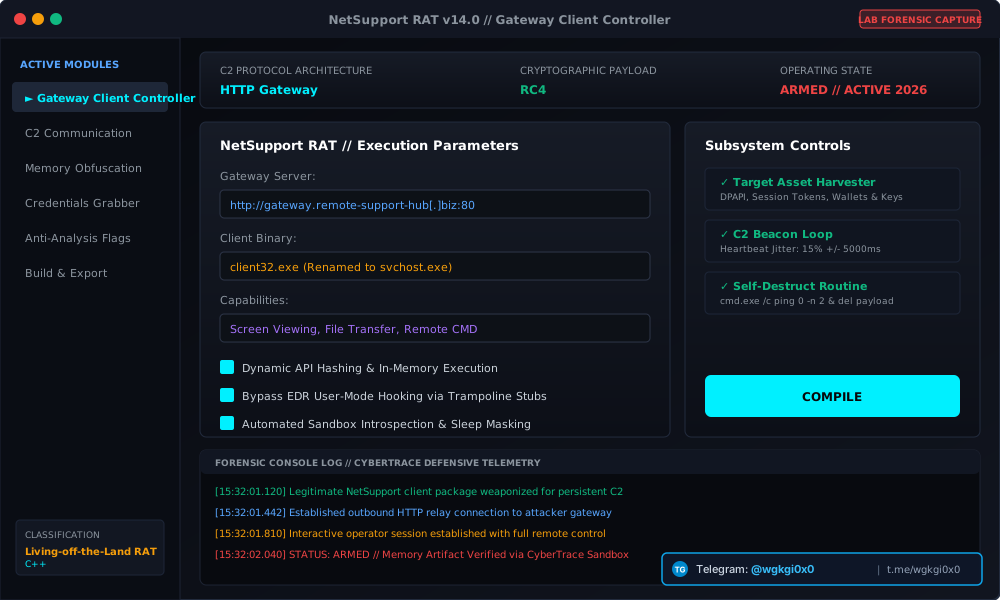
Forensic analysis of client32.ini configuration parameters establishing covert gateway reverse connections.

Disassembly tracking surveillance API hooks capturing remote desktop buffers and operator commands.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and HTTP Gateway, Client-Server Sockets command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
NetSupport RAT (RAT)
Legitimate commercial NetSupport Manager software weaponized through covert client configuration files (client32.ini), suppressed UI notifications, and reverse Gateway proxies.
C2 Architecture: {'framing': 'Proprietary binary packet framing or HTTP POST encapsulation routed through the NetSupport Gateway server on TCP port 443, 80, or 3085.', 'serialization': 'Proprietary structured binary protocol encoding command identifiers, screen coord
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ NetSupport RAT (RAT)
Детальный технический анализ NetSupport RAT — это Троян удаленного доступа (RAT), разработанный на стеке Microsoft Visual C++ (Win32 PE32 GUI/Service application). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Proprietary HTTP Gateway protocol (Port 443 / 80 / 3085) with custom DES / Blowfish encryption and configuration checksum validation) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Proprietary HTTP Gateway protocol (Port 443 / 80 / 3085) with custom DES / Blowfish encryption and configuration checksum validation, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
NetSupport RAT (RAT) विश्लेषण
NetSupport RAT एक परिष्कृत रिमोट एक्सेस ट्रोजन (RAT) है जिसे Microsoft Visual C++ (Win32 PE32 GUI/Service application) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Proprietary HTTP Gateway protocol (Port 443 / 80 / 3085) with custom DES / Blowfish encryption and configuration checksum validation) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Proprietary HTTP Gateway protocol (Port 443 / 80 / 3085) with custom DES / Blowfish encryption and configuration checksum validation आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).