01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual Basic .NET Compiler (vbc.exe) / Roslyn",
  "runtime": ".NET Common Language Runtime (CLR 2.0.50727 or 4.0.30319)",
  "binary_footprint": "Single executable PE32 (.NET assembly), typ. 25 KB - 85 KB uncompressed stub",
  "stub_size": "49,152 bytes (vanilla v0.7d stub payload)",
  "packer_obfuscation": "ConfuserEx, DeepSea, .NET Reactor, or bundled inside multi-stage AutoIt / VBScript / PowerShell loaders",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "Main() in module A or OK -> Mutex check (avoid duplicate instances) -> Unpack internal settings -> Copy self to drop directory (%TEMP% or %APPDATA%) -> Registry Run key persistence installation -> Critical process watchdog activation (RtlSetProcessIsCritical) -> Connect() raw TCP socket loop to configured C2",
  "technical_summary": "NjRAT (also known as Bladabindi) is a legacy commodity Remote Access Trojan authored in Visual Basic .NET. Renowned for its ubiquity across cybercrime forums, the malware utilizes an unencrypted, pipe-delimited raw TCP socket protocol separating command tokens with the literal string \"|'|'|\". Operational capabilities include remote desktop streaming, microphone and webcam surveillance, keystroke logging, registry manipulation, USB drive worm propagation, and system watchdog protection enforcing BSOD on termination."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "WinForms Desktop GUI Operator Application (njRAT v0.7d / Golden Edition)",
  "builder_tabs_options": [
    {
      "tab": "Connection Configuration",
      "options": [
        "Host: Dynamic DNS hostname (e.g., duckdns.org, no-ip.biz) or static IP address",
        "Port: TCP listening port (default: 5552, 1177)",
        "Victim Name (VN): Identifier string assigned to infected endpoints (e.g., 'HacKeD')",
        "Version (VR): Hardcoded campaign/version string (e.g., 'njRAT 0.7d')"
      ]
    },
    {
      "tab": "Installation & Persistence",
      "options": [
        "Install Dir: Drop directory selection (%TEMP%, %APPDATA%, %PROGRAMFILES%)",
        "Exe Name: Executable filename dropped on disk (e.g., server.exe, svchost.exe)",
        "Registry Key: Subkey name written into CurrentVersion\\Run",
        "Copy to Startup: Boolean toggle copying executable directly into Windows Startup folder"
      ]
    },
    {
      "tab": "Defense & Propagation Toggles",
      "options": [
        "Protect Process (BD): Invokes RtlSetProcessIsCritical to trigger BSOD if process is killed",
        "USB Spread: Enables background monitoring of WM_DEVICECHANGE to copy payload and autorun.inf to flash drives",
        "Anti-Process: Terminates taskmgr.exe, regedit.exe, and Wireshark if detected"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "Field HH",
      "type": "string",
      "field": "OK.HH",
      "description": "C2 server hostname or IP address"
    },
    {
      "offset": "Field PO",
      "type": "int",
      "field": "OK.PO",
      "description": "C2 server listening port number"
    },
    {
      "offset": "Field VN",
      "type": "string",
      "field": "OK.VN",
      "description": "Victim identifier / campaign name"
    },
    {
      "offset": "Field VR",
      "type": "string",
      "field": "OK.VR",
      "description": "Client version string (e.g., 'njRAT 0.7d')"
    },
    {
      "offset": "Field RG",
      "type": "string",
      "field": "OK.RG",
      "description": "Registry subkey name for persistence"
    },
    {
      "offset": "Field DR",
      "type": "string",
      "field": "OK.DR",
      "description": "Drop directory environment variable name"
    },
    {
      "offset": "Field EXE",
      "type": "string",
      "field": "OK.EXE",
      "description": "Dropped executable filename"
    },
    {
      "offset": "Field BD",
      "type": "bool",
      "field": "OK.BD",
      "description": "Process protection boolean (True enables critical process watchdog)"
    }
  ],
  "payload_generation_flags": [
    "Compiler: Invokes in-memory CodeDOM compiler (Microsoft.VisualBasic.VBCodeProvider)",
    "Assembly Information Spoofing: Clones title, company, product, and version metadata from benign executables",
    "Icon Changer: Extracts and embeds custom icon resources into compiled stub"
  ],
  "operator_commands": [
    "ll: Initial registration beacon sending victim telemetry",
    "inf: Retrieves expanded system hardware, operating system, and uptime information",
    "kl: Synchronizes offline keystroke log buffer stored in memory or temp file",
    "rn: Downloads and executes payload from external URL or disk path",
    "up: Uploads binary file to victim filesystem",
    "dw: Downloads remote file from victim filesystem to operator console",
    "pr: Process manager command list (kill, suspend, refresh active tasks)",
    "CAP: Remote desktop capture request invoking GDI screen scrape",
    "un: Uninstalls client stub and deletes persistence registry keys"
  ],
  "interface_telemetry_analysis": "The operator interface provides an intuitive table view displaying connected bot nodes, geolocation flags, OS version, active window titles, and real-time screen capture feeds."
}struct NjRAT_(Bladabindi)_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Native .NET Execution / Dropper: Executes dropped stub -> Copies payload to %TEMP%\\<EXE>.exe -> Creates registry Run entry -> P/Invokes ntdll!RtlSetProcessIsCritical(1, NULL, 0) -> Enters asynchronous TCP socket loop using System.Net.Sockets.TcpClient.",
  "ntapi_functions": [
    "ntdll!RtlSetProcessIsCritical",
    "user32!GetForegroundWindow",
    "user32!GetWindowTextA",
    "user32!GetAsyncKeyState",
    "user32!SetWindowsHookExW"
  ],
  "delimiter_protocol": "Pipe Delimiter Communication: Unlike modern structured serialization formats (MsgPack/JSON), NjRAT relies on raw string concatenation. The protocol uses the signature delimiter string \"|'|'|\" (hex: 7C 27 7C 27 7C). Parameter values (computer name, user name, OS, active window title) are individual Base64-encoded strings joined by this delimiter. Packets begin with an ASCII integer length prefix followed by a null byte (0x00).",
  "process_protection_watchdog": "Critical Process Protection: If the builder option 'BD' (Break Death) is enabled, the client imports ntdll.dll via P/Invoke and calls RtlSetProcessIsCritical(1, 0, 0). This marks the malware process as a critical system component. If an analyst or user terminates the process via Task Manager or taskkill, the Windows kernel triggers BugCheck 0xEF (CRITICAL_PROCESS_DIED), immediately crashing the operating system.",
  "usb_propagation_engine": "Removable Drive Worm: Implements a background thread listening for the Windows message WM_DEVICECHANGE (0x0219). When a removable volume (DBT_DEVICEARRIVAL) is mounted, NjRAT copies its executable to the root directory, marks it with hidden/system file attributes (attrib +h +s), and creates an autorun.inf file or disguised Windows shortcuts (.lnk) pointing to the dropped payload.",
  "anti_analysis": "Basic process scanner scanning running processes against hardcoded blacklists (taskmgr, wireshark, processhacker)."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the NjRAT (Bladabindi) binary:
[ "Keystroke logging: Tracks global keystrokes and records active foreground window titles", "Remote desktop streaming: Captures desktop surfaces using Graphics.CopyFromScreen", "Webcam capture: Intercepts DirectShow / video capture device streams", "Microphone recording: Captures audio buffer feeds via mciSendStringA" ]
[ "Remote process manager: Enumerates, suspends, and terminates running system processes", "Remote file explorer: Browses local drives, uploads, downloads, and executes files", "Remote registry editor: Queries, adds, and modifies registry keys and values", "Remote command prompt: Spawns hidden cmd.exe session with redirected standard I/O" ]
[ "Persistence via CurrentVersion\\Run registry keys and Startup folder drops", "Process protection via ntdll!RtlSetProcessIsCritical forcing system crash on termination", "USB drive infection creating hidden executables and autorun configurations" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Packets are framed as: <length_in_ascii>\\x00<command>|'|'|<param1>|'|'|<param2>|'|'|...",
  "serialization": "String concatenation of Base64-encoded tokens separated by the literal delimiter |'|'|.",
  "handshake": "Client establishes raw TCP socket connection -> Sends registration packet: '<len>\\x00ll|'|'|<HWID_b64>|'|'|<User_b64>|'|'|<PC_b64>|'|'|<OS_b64>|'|'|<Cam_b64>|'|'|<VR_b64>|'|'|..' -> Server responds with commands.",
  "cryptography": "Unencrypted plaintext ASCII or trivial Base64 parameter encoding (no TLS or AES by default).",
  "packet_types": [
    "ll: Initial beacon and system identification frame",
    "inf: System hardware, uptime, and network interface summary",
    "kl: Keystroke log synchronization packet",
    "CAP: Compressed desktop screen capture image buffer"
  ],
  "traffic_signature": "Easily identifiable raw TCP traffic containing high recurrence of ASCII string |'|'| (7C 27 7C 27 7C)."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_NjRAT_Bladabindi_Protocol {
    meta:
        description = "Detects NjRAT / Bladabindi .NET payload stubs and pipe delimiter wire protocol strings"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        reference = "TF-034"
    strings:
        $delimiter = "|'|'|"
        $cmd_ll = "ll|'|'|"
        $cmd_inf = "inf|'|'|"
        $cmd_kl = "kl|'|'|"
        $bsod_func = "RtlSetProcessIsCritical"
        $vb_net = "Microsoft.VisualBasic"
    condition:
        uint16(0) == 0x5A4D and $delimiter and ($cmd_ll or $cmd_inf or $cmd_kl) and ($bsod_func or $vb_net)
}title: NjRAT Pipe-Delimited Network Traffic Pattern
id: 9b2e1a3c-5829-4d1a-8c19-4a5e01b23847
status: stable
description: Detects network communication containing NjRAT signature delimiter sequence over unencrypted TCP sockets.
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
product: zeek
service: raw
detection:
selection:
Payload|contains: "|'|'|"
condition: selection
fields:
- id.orig_h
- id.resp_h
- id.resp_p
falsepositives:
- Extremely rare proprietary applications utilizing identical string delimiters
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
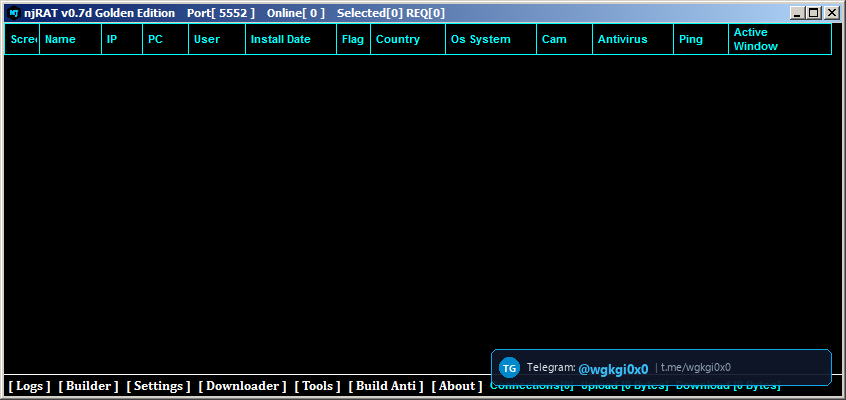
Visual Basic .NET builder configuring payload persistence, dynamic DNS connection strings, and mutex flags.

Operator UI managing connected victim bots, remote desktop viewing, and live microphone capture streams.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Direct TCP Sockets with Delimited Strings command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
NjRAT (Bladabindi) (RAT)
Classic Visual Basic .NET commodity Remote Access Trojan utilizing pipe-delimited unencrypted TCP sockets and critical process watchdog protection.
C2 Architecture: {'framing': "Packets are framed as: <length_in_ascii>\\x00<command>|'|'|<param1>|'|'|<param2>|'|'|...", 'serialization': "String concatenation of Base64-encoded tokens separated by the literal delimiter |'|'|.", 'handshake': "Client establishes raw T
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ NjRAT (Bladabindi) (RAT)
Детальный технический анализ NjRAT (Bladabindi) — это Троян удаленного доступа (RAT), разработанный на стеке Microsoft Visual Basic .NET Compiler (vbc.exe) targeting .NET Framework 2.0 / 3.5 / 4.0. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Unencrypted or Lightly Obfuscated Raw TCP Sockets delimited by |'|'| separator string with Base64 parameters) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Unencrypted or Lightly Obfuscated Raw TCP Sockets delimited by |'|'| separator string with Base64 parameters, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
NjRAT (Bladabindi) (RAT) विश्लेषण
NjRAT (Bladabindi) एक परिष्कृत रिमोट एक्सेस ट्रोजन (RAT) है जिसे Microsoft Visual Basic .NET Compiler (vbc.exe) targeting .NET Framework 2.0 / 3.5 / 4.0 का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Unencrypted or Lightly Obfuscated Raw TCP Sockets delimited by |'|'| separator string with Base64 parameters) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Unencrypted or Lightly Obfuscated Raw TCP Sockets delimited by |'|'| separator string with Base64 parameters आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).