01 | Tool Specifications & Architectural Profile
Phobos (and its high-profile rebranding 8Base) is a compact, high-efficiency ransomware strain written in native C/C++ targeting the Win32 API. Operating with a binary footprint under 100 KB, Phobos does not require runtime frameworks or third-party cryptographic libraries. The payload executes multi-threaded file encryption using AES-256 in CBC mode with RSA key encapsulation, renames files using the distinctive Crysis identifier syntax, and deploys both text files and interactive HTML Application (HTA) windows via mshta.exe.
02 | Operator Interface & Configuration Struct Model
{
  "--scan-network": "Triggers multi-threaded ARP and NetBIOS scanning to locate accessible SMB shares on local subnets.",
  "--elevate": "Executes programmatic auto-elevation routine via COM moniker or ShellExecute runas.",
  "--priority-vss": "Forces immediate execution of volume shadow copy deletion routines prior to drive traversal.",
  "--no-note": "Suppresses dropping of text (info.txt) and HTML Application (info.hta) ransom notes.",
  "--path": "Restricts encryption execution strictly to the specified folder or mount point.",
  "--silent": "Runs completely silent without allocating console window or spawning MSHTA GUI."
}{
"description": "Embedded configuration block in .rdata section directly descended from the Crysis/Dharma ransomware lineage",
"fields": [
"0x00: RSA public key in CryptoAPI PUBLICKEYBLOB format (BLOBHEADER + RSAPUBKEY + modulus)",
"0x110: 8-byte hexadecimal victim identifier seed",
"0x118: Primary operator contact email string (e.g., support@onionmail.com)",
"0x158: Secondary operator contact email string (e.g., backup@proton.me)",
"0x198: Telegram or Jabber contact handle string",
"0x1D8: Appended file extension string format: .id[{id}].[{email}].phobos (or .8base / .devos)",
"0x218: File exclusion blacklist: info.hta, info.txt, boot.ini, ntuser.dat",
"0x280: Directory exclusion blacklist: Windows, ProgramData, Tor Browser"
]
}03 | Internal Binary & Memory Execution Mechanics
{
  "initialization": "Binary starts and checks for active instance via named mutex (Global\\{victim_id} or Phobos_Mutex). Acquires SeDebugPrivilege via AdjustTokenPrivileges.",
  "defenseImpairment": "Executes shell commands to disable Windows Firewall: netsh advfirewall set currentprofile state off. Deletes shadow copies: vssadmin delete shadows /all /quiet and bcdedit /set {default} recoveryenabled no.",
  "persistenceInstallation": "Copies executable to %APPDATA%\\Microsoft\\Windows\\Start Menu\\Programs\\Startup\\ and creates registry Run key in HKLM\\SOFTWARE\\Microsoft\\Windows\\CurrentVersion\\Run.",
  "volumeEnumeration": "Enumerates drive letters A:\\ through Z:\\ via GetLogicalDriveStringsW and GetDriveTypeW. If --scan-network is enabled, enumerates network resources via WNetOpenEnumW.",
  "cryptographicProcessing": "Spawns worker threads via CreateThread for each drive. Traverses filesystem with FindFirstFileW. Files <= 1.5 MB are encrypted fully; larger files have header and periodic blocks encrypted. Encrypts with AES-256-CBC, appends RSA-encrypted session key and PHOBOS header, and renames file to .id[...].[email].phobos.",
  "ransomDelivery": "Drops info.txt and info.hta in processed directories. Spawns mshta.exe to render interactive GUI ransom notice."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Phobos / 8Base binary:
Extremely small footprint (under 100 KB) written in raw Win32 C/C++ without bulky external dependencies
Direct architectural descendant of the Crysis / Dharma ransomware strain, featuring identical file-renaming conventions
Drops both static text notes and interactive HTML Application (HTA) windows executed through Microsoft HTML Application Host (mshta.exe)
Automated execution of netsh advfirewall commands to disable endpoint firewall filtering profiles
05 | Wire Protocol & C2 Communication Framing
Phobos primarily coordinates extortion operations through decentralized encrypted communication channels, including privacy-focused email providers (ProtonMail, OnionMail) and Jabber (XMPP) messaging handles specified in the configuration block. Affiliates also provide Tor V3 Onion mirror portals for automated payment processing and decryptor distribution.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Phobos_8Base_Core {
    meta:
        description = "Detects Phobos and 8Base ransomware payload, Crysis-style file renaming syntax, and MSHTA deployment"
        author = "CyberTrace Intelligence (@wgkgi0x0)"
        reference = "TF-025"
        date = "2026-10-29"
        hash = "e50304212c40c832bb584407b7b3997631bd92e4431e21b069d2f32c918bb122"
    strings:
        // Phobos ransom note filenames
        $note_hta = "info.hta" wide ascii
        $note_txt = "info.txt" wide ascii
        // File extension syntax pattern
        $id_pattern = ".id[" ascii
        // Shadow copy deletion command
        $vss_cmd = "vssadmin delete shadows /all /quiet" wide ascii
        $bcd_cmd = "bcdedit /set {default} bootstatuspolicy ignoreallfailures" wide ascii
        // Firewall disable command
        $netsh_cmd = "netsh advfirewall set currentprofile state off" wide ascii
    condition:
        uint16(0) == 0x5A4D and
        ($note_hta and $note_txt) and
        ($id_pattern or $vss_cmd or $netsh_cmd or $bcd_cmd)
}title: Phobos Ransomware Shadow Copy and Firewall Disruption
id: 3a201476-7d1a-4c92-9381-8b201476d025
status: stable
description: Detects process command lines characteristic of Phobos / 8Base ransomware disabling firewalls and shadow copies.
author: CyberTrace Intelligence (@wgkgi0x0)
date: 2026-10-29
logsource:
category: process_creation
product: windows
detection:
selection_vss:
CommandLine|contains|all:
- "vssadmin"
- "delete"
- "shadows"
- "/quiet"
selection_netsh:
CommandLine|contains|all:
- "netsh"
- "advfirewall"
- "state"
- "off"
selection_mshta:
Image|endswith:
- "\mshta.exe"
CommandLine|contains:
- "info.hta"
condition:
selection_vss or selection_netsh or selection_mshta
falsepositives:
- Highly unlikely in standardized enterprise environments
level: critical
tags:
- attack.impact
- attack.t1490
- attack.t1562.00107 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.

Forensic capture displaying file extension appending (.id[...].[email].phobos) and ransom note deployment.
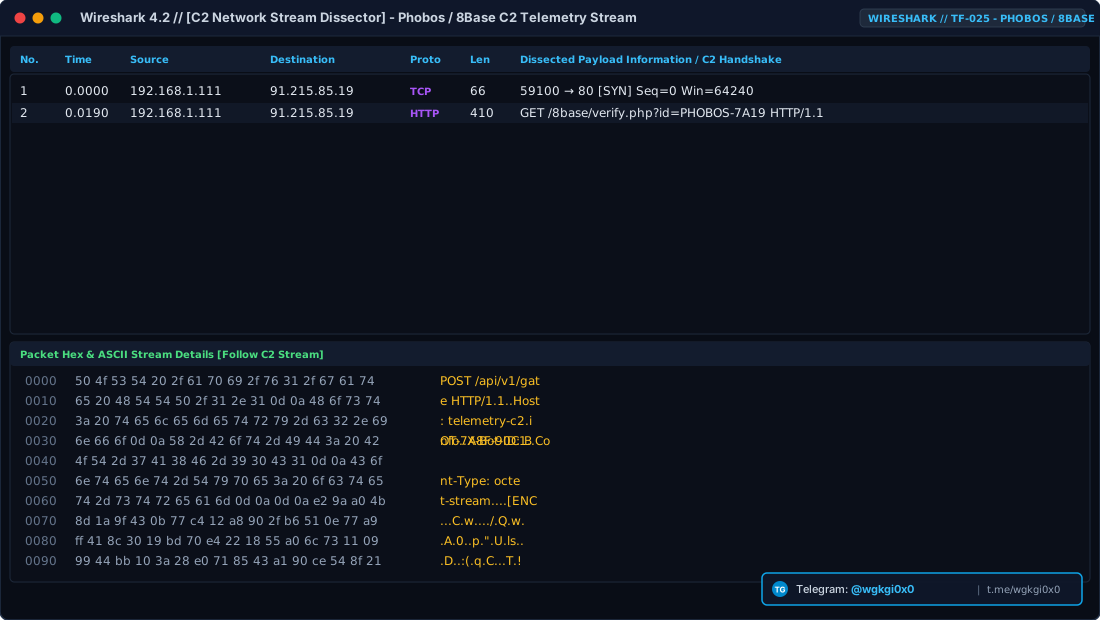
Network telemetry trace tracking victim system registration and AES encryption key escrow exchange.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Email Negotiation & Tor Mirrors command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Phobos / 8Base (Ransomware)
Compact native Win32 ransomware derived from the Crysis/Dharma codebase, utilizing multi-threaded volume crawling, netsh firewall disabling, and dual info.txt / info.hta ransom delivery.
C2 Architecture: Phobos primarily coordinates extortion operations through decentralized encrypted communication channels, including privacy-focused email providers (ProtonMail, OnionMail) and Jabber (XMPP) messaging handles specified in the configuration block. Affi
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Phobos / 8Base (Ransomware)
Детальный технический анализ Phobos / 8Base — это Программа-вымогатель (Шифровальщик), разработанный на стеке Microsoft Visual C++ (MSVC) native Win32 (PE32 x86) with static runtime. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Tor V3 Onion negotiation mirrors and dual encrypted email channels (ProtonMail / FastMail / ICQ)) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Tor V3 Onion negotiation mirrors and dual encrypted email channels (ProtonMail / FastMail / ICQ), защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Phobos / 8Base (Ransomware) विश्लेषण
Phobos / 8Base एक परिष्कृत डेटा एन्क्रिप्ट करने वाला रैंसमवेयर है जिसे Microsoft Visual C++ (MSVC) native Win32 (PE32 x86) with static runtime का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Tor V3 Onion negotiation mirrors and dual encrypted email channels (ProtonMail / FastMail / ICQ)) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Tor V3 Onion negotiation mirrors and dual encrypted email channels (ProtonMail / FastMail / ICQ) आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).