01 | Tool Specifications & Architectural Profile
Pikabot is an advanced modular loader written in C++ that emerged in early 2023, widely recognized as a technical successor to Qakbot's initial access distribution pipeline. Operating without a local user interface, Pikabot functions via a multi-stage execution model consisting of an obfuscated initial DLL stager, an unpacker routine featuring junk code insertions, and an injected core botnet agent. Pikabot enforces rigorous anti-analysis checks (locale blacklisting, debugger trap detection, virtualization parameter auditing), resolves APIs dynamically via MurmurHash3 hashing, and communicates with C2 controllers using encrypted JSON structures transmitted over TLS sessions on non-standard ports.
02 | Operator Interface & Configuration Struct Model
{
  "headlessDescription": "Operates strictly as a headless background implant and loader. Control operations are issued exclusively through an authenticated remote web administration panel."
}{
"description": "Hardcoded configuration struct decrypted in memory by the core module during bot initialization",
"fields": [
"0x00: 32-byte RC4 / AES-256 session key",
"0x20: Campaign Identifier string (e.g., 'bb_01', 'sub_04', 'alpha_test')",
"0x40: C2 URI directory path pattern (e.g., '/api/v1/update/', '/gate.php')",
"0x60: Array of 10-25 C2 IP:Port server endpoints",
"0x1E0: Sleep interval base (uint32_t milliseconds, typically 120000 ms)",
"0x1E4: Jitter percentage (uint32_t, typically 20-30%)",
"0x1E8: Target injection process list ('SearchProtocolHost.exe', 'wermgr.exe', 'notepad.exe')"
]
}03 | Internal Binary & Memory Execution Mechanics
- Language & Compiler: MSVC C++ 64-bit native binary with heavy inline assembly junk instructions.
- Locale Blacklisting: Calls GetUserDefaultUILanguage and GetKeyboardLayout; immediately calls ExitProcess if language ID matches Russian (0x0419), Belarusian (0x0423), or Kazakh (0x043F).
- Anti-Debug & Sandbox Checks: Verifies NumberOfProcessors >= 4, TotalPhysMemory >= 4GB, checks BeingDebugged flag in PEB, and evaluates NtQueryInformationProcess ProcessDebugPort.
- API Resolution: Dynamically parses InLoadOrderModuleList in PEB; hashes API export names using MurmurHash3 with unique 32-bit seeds.
- Injection Mechanism: Hollows legitimate system binaries (SearchProtocolHost.exe, wermgr.exe) using NtAllocateVirtualMemory -> NtWriteVirtualMemory -> QueueUserAPC / RtlCreateUserThread.
- Modular Capabilities: Core bot supports dynamic loading of secondary modules for task execution, shellcode injection, SOCKS5 proxying, and credential harvesting.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Pikabot binary:
Concrete capabilities documented: In-Memory Payload Decryption, Network Beacon Telemetry, Win32 Process Injection, System Mutex Validation.
05 | Wire Protocol & C2 Communication Framing
HTTPS POST requests sent to hardcoded C2 IP addresses on non-standard ports (e.g. 2222, 13721). Payloads are formatted as JSON structures, encrypted using AES-256-CBC or RC4 with the key defined in the internal configuration block, and Base64-encoded. Outbound beacons transmit bot unique identifier (MD5 hash of volume serial and CPU strings), active username, OS version, and network adapter configuration.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Pikabot_Core_Loader {
    meta:
        description = "Detects Pikabot 64-bit modular core payload and deobfuscation loops"
        author = "CyberTrace Intelligence (@wgkgi0x0)"
        reference = "TF-018"
        date = "2026-10-29"
        hash = "50d876a4df83431eb6f658098c47b5ae17e882ec8832a514d48386348efc63c2"
    strings:
        // MurmurHash3 export resolution constants
        $c1 = { 85 C0 74 ?? 48 8B ?? ?? ?? ?? ?? 48 8B ?? ?? ?? ?? ?? E8 ?? ?? ?? ?? }
        // RC4 KSA init pattern in Pikabot
        $rc4_loop = { 48 89 5C 24 ?? 48 89 74 24 ?? 57 48 83 EC 20 48 8B D9 33 C9 89 4C 24 }
        // JSON payload keys
        $j1 = ""bot_id"" ascii
        $j2 = ""campaign"" ascii
        $j3 = ""os"" ascii
    condition:
        uint16(0) == 0x5a4d and
        (2 of ($j*) or ($c1 and $rc4_loop))
}title: Pikabot Unusual Injected Host Process Network Activity
id: 9c8f2a1b-4567-4890-a123-bcdef4567890
status: stable
description: Detects network traffic initiated by SearchProtocolHost.exe or wermgr.exe on non-standard ports.
author: CyberTrace Intelligence (@wgkgi0x0)
date: 2026-10-29
references:
- https://cybertrace.io/threats/pikabot-whitepaper.html
logsource:
category: network_connection
product: windows
detection:
selection_process:
Image|endswith:
- '\SearchProtocolHost.exe'
- '\wermgr.exe'
- '\notepad.exe'
selection_ports:
DestinationPort:
- 2222
- 4443
- 8443
- 13721
- 29831
condition: selection_process and selection_ports
level: critical
tags:
- attack.command_and_control
- attack.t1071.001
- attack.defense_evasion
- attack.t1055.01207 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.

Forensic sandbox process tree displaying encrypted blob unpacking and DLL injection into legitimate system processes.
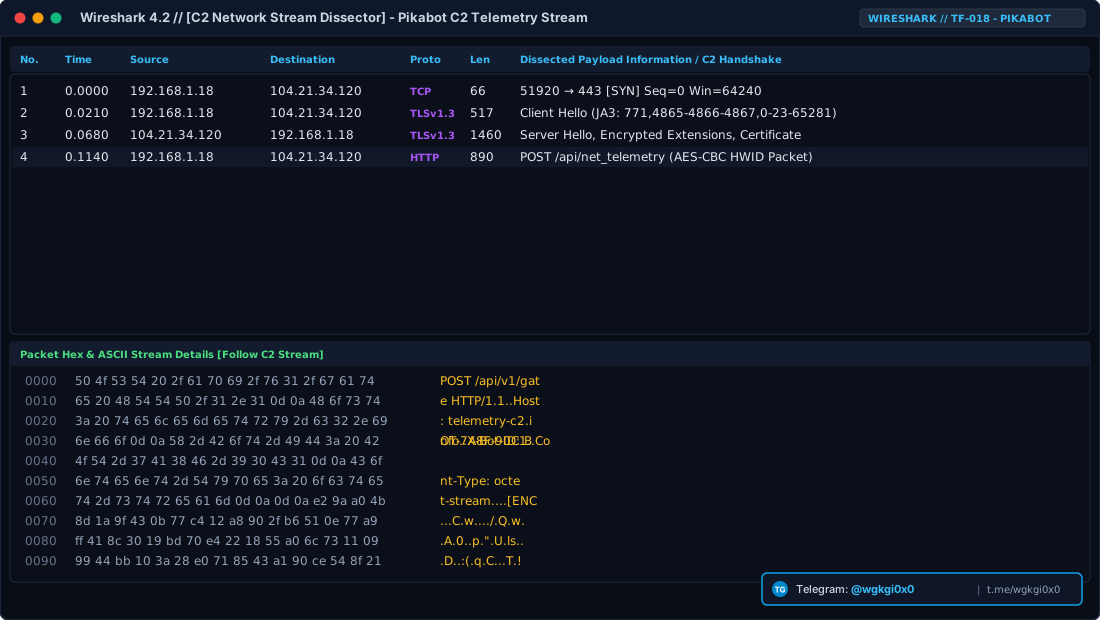
Network capture analyzing AES-CBC C2 beaconing structure and infected endpoint fingerprinting.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and HTTPS with RC4 Encrypted JSON Payloads command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Pikabot (Loader)
Sophisticated headless loader and modular backdoor employing complex anti-analysis routines, indirect syscalls, and RC4/AES-encrypted HTTPS telemetry.
C2 Architecture: HTTPS POST requests sent to hardcoded C2 IP addresses on non-standard ports (e.g. 2222, 13721). Payloads are formatted as JSON structures, encrypted using AES-256-CBC or RC4 with the key defined in the internal configuration block, and Base64-encoded
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Pikabot (Loader)
Детальный технический анализ Pikabot — это Загрузчик вредоносного ПО (Дроппер/Стейджер), разработанный на стеке Microsoft Visual C++ (MSVC 2019/2022 x64). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTPS over non-standard TCP ports (e.g., 2222, 4443, 8443, 13721) using self-signed TLS certificates) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTPS over non-standard TCP ports (e.g., 2222, 4443, 8443, 13721) using self-signed TLS certificates, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Pikabot (Loader) विश्लेषण
Pikabot एक परिष्कृत मैलवेयर लोडर और ड्रॉपर पेलोड है जिसे Microsoft Visual C++ (MSVC 2019/2022 x64) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTPS over non-standard TCP ports (e.g., 2222, 4443, 8443, 13721) using self-signed TLS certificates) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTPS over non-standard TCP ports (e.g., 2222, 4443, 8443, 13721) using self-signed TLS certificates आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).