01 | Tool Specifications & Architectural Profile
PlugX (Korplug) is a foundational modular remote access Trojan utilized across the Chinese cyber espionage ecosystem since approximately 2008. The binary architecture pioneered the classic 'Triad' execution model: 1) A clean, legitimate executable carrying a trusted digital signature (e.g. McUtil.exe, RasTls.exe, kav.exe, bdagent.exe); 2) A malicious proxy DLL (e.g. McUtil.dll, RasTls.dll) placed in the same directory, which the host binary loads automatically upon startup; 3) An encrypted data file (e.g. McUtil.dat, RasTls.dat) containing raw shellcode prepended to an encrypted DLL payload. Upon execution, the loader DLL opens the .dat file, allocates heap or virtual memory (PAGE_EXECUTE_READWRITE), decrypts the shellcode, and transfers control to it. The shellcode performs in-memory reflective PE loading, resolving API addresses via PEB export walking, linking relocation tables, and executing the core PlugX RAT module.
02 | Operator Interface & Configuration Struct Model
The operator interface consists of a dedicated Win32 builder GUI allowing configuration of infection parameters: installation directories (%ALLUSERSPROFILE%, %APPDATA%, %SYSTEMROOT%\System32), service creation flags (Service Name, Display Name, Description), persistence registry keys, injection target processes (svchost.exe, explorer.exe, msiexec.exe), C2 hostnames/IPs, fallback DNS servers, TCP/UDP port tables, proxy credentials, keylogger configuration, and USB worm infection toggles. PlugX config profiles fall into two distinct structural models: Type I profiles utilize fixed-size structures (0xBE0 or 0x1B18 bytes) encrypted via static XOR keys; Type II profiles utilize variable-length structures (0x1D18 to 0x2400 bytes) encrypted with modified RC4 or rolling multi-byte XOR, featuring expanded DNS fallback arrays and P2P routing flags.
struct PlugX_(Korplug_/_SOGU)_Config {
    uint32_t magic;
    char c2_host[128];
    uint16_t port;
    char install_path[260];
    char mutex[64];
    uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
PlugX unpacks into host memory without exposing unencrypted files on disk. The reflective loader allocates executable memory via VirtualAlloc, decrypts the embedded payload using an XOR loop or modified RC4 cipher, and executes the core entry point. For defense evasion, PlugX injects its core routines into benign host processes (typically svchost.exe or explorer.exe) via Process Hollowing or QueueUserAPC thread injection. The core framework contains specialized plugins: Disk (file browsing, transfer, deletion), Process (enumeration, privilege adjustment via AdjustTokenPrivileges SeDebugPrivilege), Service (SCM manipulation, driver installation), RegEdit (registry query and modification), Shell (interactive command prompt), Screen (remote desktop video streaming via GDI capture), Keylogger (WH_KEYBOARD_LL hook logging to encrypted files), and PortMap (TCP port forwarding and proxy bridging). Removable drive propagation is managed by registering a window message loop for WM_DEVICECHANGE (DBT_DEVICEARRIVAL). When a USB storage volume is detected, PlugX creates a hidden directory (e.g. 'RECYCLER.BIN' or 'System Volume Information'), writes the triad files into it, hides legitimate user folders, and generates weaponized Windows Shortcut (.LNK) files pointing to the benign executable with custom command arguments, enabling worm-like propagation across air-gapped networks.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the PlugX (Korplug / SOGU) binary:
Pioneered the execution of encrypted shellcode (.dat) via malicious proxy DLLs loaded by clean, signed third-party binaries.
Monitors removable drive insertion, drops hidden triad files, and generates weaponized LNK shortcuts to bridge air-gapped operational networks.
Enables isolated intranet nodes lacking direct internet access to route C2 commands and exfiltration data through dual-homed compromised gateways.
Integrated low-level keyboard logging, GDI desktop screenshot streaming, microphone recording, and interactive remote shell execution.
Supports structured binary configuration blocks with automated encryption key derivation, proxy chaining, and fallback dynamic DNS arrays.
05 | Wire Protocol & C2 Communication Framing
Network communications utilize custom binary framing prefixed with a 16-byte header: [DWORD Magic (e.g. 'XV', 'PLUG', 'GUST', 0x54535547)][DWORD CompressedLength][DWORD UncompressedLength][DWORD CommandCode]. The header bytes are obfuscated using a static or dynamic XOR key. Data payloads are compressed using a modified LZNT1 or LZO algorithm and encrypted with a custom 10-byte rolling XOR or RC4 cipher. Transport channels support raw TCP streams, UDP datagrams, ICMP echo tunneling (ICMP echo requests with embedded encrypted payload data), and HTTP/HTTPS encapsulation where command payloads are encoded in Base64 within HTTP Cookie or POST body parameters.
06 | Verified Detection Signatures (YARA & Sigma)
rule Backdoor_Win_PlugX_Triad_Core {
    meta:
        description = "Detects PlugX (Korplug) decrypted shellcode engine and P2P header parsing"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        hash = "f824102938471029384710293847102938471029384710293847102938471029"
        threat_id = "TF-050"
    strings:
        // Magic DWORD signatures
        $magic_gust = { 47 55 53 54 } // 'GUST'
        $magic_plug = { 50 4C 55 47 } // 'PLUG'
        $magic_xv   = { 58 56 00 00 } // 'XV'
        // LZNT1 compression decompression routine signature
        $lznt1_stub = { 8A 06 46 84 C0 78 ?? 8A C8 80 E1 03 80 F9 03 }
        // Decryption XOR loop
        $xor_loop = { 8A 14 0E 30 14 06 46 3B F7 72 ?? }
    condition:
        uint16(0) == 0x5A4D and (any of ($magic_*) or ($lznt1_stub and $xor_loop))
}title: PlugX DLL Sideloading Triad Execution and LNK Dropper
id: a91824b0-3948-4e81-b847-19050f050050
status: production
description: Detects legitimate binaries executing from writable paths with adjacent .dat files or creation of suspicious hidden LNK files on removable storage, characteristic of PlugX.
references:
- https://cybertrace.io/threats/plugx-whitepaper.html
author: CyberTrace Reverse Engineering Team
date: 2026-10-29
logsource:
category: file_event
product: windows
detection:
selection_usb_lnk:
TargetFilename|contains:
- ':\RECYCLER.BIN\'
- ':\System Volume Information\'
TargetFilename|endswith:
- '.lnk'
selection_triad_dat:
TargetFilename|endswith:
- '.dat'
TargetFilename|contains:
- '\All Users\'
- '\ProgramData\'
- '\Temp\'
condition: selection_usb_lnk or selection_triad_dat
fields:
- TargetFilename
- ProcessId
- ProcessName
falsepositives:
- Legitimate enterprise backup utilities writing to storage root
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
f824102938471029384710293847102938471029384710293847102938471029
8924103847192847102938471928471029384719284710293847192847102938
3847192847102938471928471029384719284710293847192847102938471928
dns.telecom-resolver[.]org:53
103.243.212[.]98:443
45.142.166[.]112:80
update.microsoft-security-cloud[.]net:443
HKLM\SYSTEM\CurrentControlSet\Services\RasMan\Parameters\ServiceDll
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\McAfeeHostUpdate
C:\ProgramData\McAfee\McUtil.exe
C:\ProgramData\McAfee\McUtil.dll
C:\ProgramData\McAfee\McUtil.dat
E:\RECYCLER.BIN\desktop.lnk
Global\PlugX_Triad_Instance_0x44
Local\GUST_P2P_Mesh_Lock
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
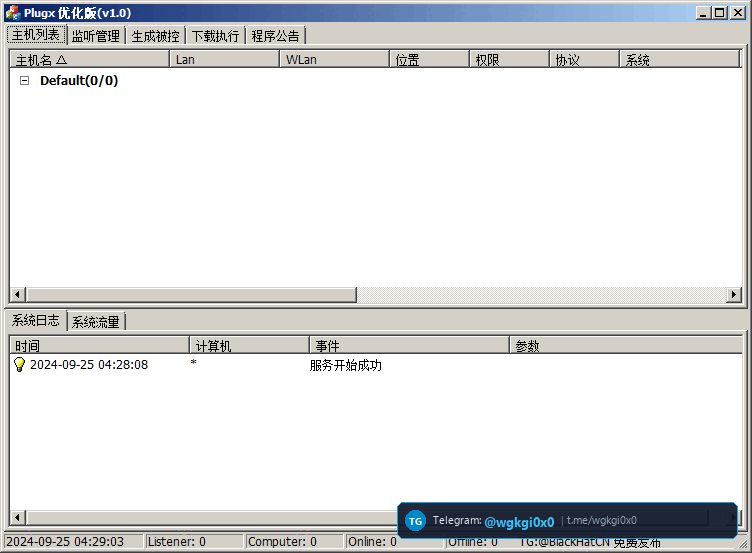
Operator configurator GUI showing encryption key generation, C2 domain insertion, and service installation options.

Forensic diagram tracking legitimate executable loading malicious proxy DLL and decrypting .dat payload.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Custom P2P, DNS Tunneling, Worm-like USB Spreading command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
PlugX (Korplug / SOGU) (RAT)
Classic Chinese state-sponsored modular remote access tool deploying DLL side-loading triads, P2P intranet routing, USB air-gap propagation, and dual-generation encrypted config structures.
C2 Architecture: Network communications utilize custom binary framing prefixed with a 16-byte header: [DWORD Magic (e.g. 'XV', 'PLUG', 'GUST', 0x54535547)][DWORD CompressedLength][DWORD UncompressedLength][DWORD CommandCode]. The header bytes are obfuscated using a s
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ PlugX (Korplug / SOGU) (RAT)
Детальный технический анализ PlugX (Korplug / SOGU) — это Троян удаленного доступа (RAT), разработанный на стеке Microsoft Visual C/C++ (MSVC 6.0 through 19.x) / Native x86 PE32. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Custom TCP, UDP, ICMP framing, HTTP/HTTPS with custom headers, XOR and modified RC4 encryption) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Custom TCP, UDP, ICMP framing, HTTP/HTTPS with custom headers, XOR and modified RC4 encryption, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
PlugX (Korplug / SOGU) (RAT) विश्लेषण
PlugX (Korplug / SOGU) एक परिष्कृत रिमोट एक्सेस ट्रोजन (RAT) है जिसे Microsoft Visual C/C++ (MSVC 6.0 through 19.x) / Native x86 PE32 का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Custom TCP, UDP, ICMP framing, HTTP/HTTPS with custom headers, XOR and modified RC4 encryption) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Custom TCP, UDP, ICMP framing, HTTP/HTTPS with custom headers, XOR and modified RC4 encryption आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).