01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C++ Compiler (cl.exe)",
  "runtime": "Native Windows Win32 API with statically linked Microsoft C Runtime (MSVCRT)",
  "binary_footprint": "Single PE32 executable without external runtime dependencies (file size: ~320 KB - 580 KB)",
  "stub_size": "327,680 bytes typical base compilation footprint",
  "packer_obfuscation": "Custom packing layers, section re-alignment, junk code insertion, API hashing via custom DJB2/ROR-13 algorithm",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "mainCRTStartup -> Anti-Analysis & Sandbox checks -> Collect Host Fingerprint (GUID) -> Initial HTTP POST beacon -> Parse JSON task queue -> Loop: Download encrypted payload -> Decrypt with RC4 -> Execute binary -> Post completion telemetry",
  "technical_summary": "PrivateLoader is a high-volume C++ Pay-Per-Install (PPI) downloader engineered to deliver diverse secondary malware payloads (e.g. RedLine, Vidar, Lumma Stealer, Djvu ransomware, GootLoader) to infected targets. It features an automated multi-task download engine, RC4 payload decryption, dynamic API resolution to bypass static IAT inspection, and persistent execution status reporting over custom HTTP C2 channels."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Centralized Web-based PPI Administration Panel",
  "builder_tabs_options": [
    {
      "tab": "Campaign Management",
      "options": [
        "Affiliate ID Assignment: Multi-tenant operator tracking per distribution campaign",
        "Geo-IP Targeting: Whitelist/blacklist filtering based on target country codes (excluding CIS regions)",
        "Payload Weighting: Distribution percentage allotment across competing buyer payloads"
      ]
    },
    {
      "tab": "Payload Queue",
      "options": [
        "Payload Upload: Direct hosting of secondary binaries (EXE, DLL, MSI)",
        "Encryption Passphrase: Sets per-payload RC4 key for on-wire decryption",
        "Execution Mode: ShellExecuteExW (direct execution) or Rundll32 invocation for DLL modules"
      ]
    },
    {
      "tab": "Telemetry Dashboard",
      "options": [
        "Live Installs Counter: Displays real-time infection counts per affiliate and geographical region",
        "Execution Success Rate: Aggregates return codes from endpoints (Success, Download Error, Execution Error)",
        "Endpoint Environmental Analytics: Summarizes AV distributions and Windows OS builds"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x00",
      "field": "c2_gate_urls",
      "type": "Null-terminated String Array",
      "description": "Primary and backup HTTP C2 endpoints for beaconing and task retrieval"
    },
    {
      "offset": "0x80",
      "field": "rc4_master_key",
      "type": "Char Array [32]",
      "description": "RC4 symmetric key used to decrypt on-wire task payloads and URL strings"
    },
    {
      "offset": "0xA0",
      "field": "affiliate_id",
      "type": "uint32_t",
      "description": "Identifier associating the infected endpoint with a specific distribution partner"
    },
    {
      "offset": "0xA4",
      "field": "campaign_tag",
      "type": "Char Array [16]",
      "description": "Tag identifying infection source (e.g., 'crack_iso', 'torrent_bundle')"
    },
    {
      "offset": "0xB4",
      "field": "sleep_delay",
      "type": "uint32_t",
      "description": "Interval in milliseconds between task execution and status beaconing"
    }
  ],
  "payload_generation_flags": [
    "Target Subsystem: Windows GUI (Silent)",
    "CRT Linkage: Static (/MT)",
    "IAT Obfuscation: API Hashing Enabled",
    "Payload Decryption: RC4 Stream Cipher"
  ],
  "operator_commands": [
    "TASK_DOWNLOAD_EXEC: Download binary from specified URL, decrypt with key, and execute",
    "TASK_UPDATE_CLIENT: Download new PrivateLoader binary, replace current file, and restart",
    "TASK_SYSTEM_INFO: Execute deep host enumeration and report active processes and hardware specs",
    "TASK_SLEEP: Pause network beaconing for specified second interval"
  ],
  "interface_telemetry_analysis": "The operator interface is accessed via an underground web panel. Operators manage customer campaigns, configure Geo-IP filtering rules, assign priority weights to different payload drops, and view real-time graphs of execution completions reported by the headless C++ clients."
}struct PrivateLoader_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Execution via direct process creation: Downloads encrypted file into %TEMP% or %APPDATA% via URLDownloadToFileW or WinINet InternetReadFile -> Decrypts buffer in-memory via RC4 -> Writes plaintext binary to disk with masqueraded name -> Invokes ShellExecuteExW or CreateProcessW with CREATE_NEW_PROCESS_GROUP flag -> Periodically executes DLLs using rundll32.exe <path>,#1.",
  "ntapi_functions": [
    "kernel32!CreateProcessW",
    "shell32!ShellExecuteExW",
    "urlmon!URLDownloadToFileW",
    "wininet!InternetOpenW",
    "wininet!InternetOpenUrlW",
    "wininet!InternetReadFile",
    "wininet!InternetCloseHandle",
    "advapi32!GetUserNameW",
    "kernel32!GetComputerNameW",
    "kernel32!GetVolumeInformationW"
  ],
  "process_hollowing_target": "None (relies on direct execution of dropped secondary payloads via ShellExecuteExW or rundll32.exe)",
  "persistence_mechanics": [
    "Scheduled Task: schtasks.exe /create /tn \"ServiceUpdate\" /tr \"<Path_To_PrivateLoader>\" /sc minute /mo 30",
    "Registry Run Key: HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run\\PrivateLoader",
    "Startup Folder LNK: Masqueraded Windows shortcut placed in %AppData%\\Microsoft\\Windows\\Start Menu\\Programs\\Startup"
  ],
  "evasion_hooks": [
    "API Hashing: Resolves functions dynamically by computing ROR-13 hashes of exported symbols in kernel32.dll and wininet.dll, bypassing static import table inspections.",
    "In-Memory Decryption: Payloads transmitted over HTTP are encrypted with RC4 and decrypted strictly in memory prior to staging on disk.",
    "Anti-Analysis Delay: Implements user activity verification loops querying GetCursorPos over several seconds before initiating C2 beaconing."
  ],
  "anti_analysis": [
    "Debugger Check: kernel32!IsDebuggerPresent() and NtQueryInformationProcess with ProcessDebugPort flag.",
    "Sandbox Inspection: Evaluates system uptime via GetTickCount() (exits if < 20 minutes) and disk capacity via GetDiskFreeSpaceExW (exits if < 40 GB).",
    "Process Blacklist: Iterates process snapshots checking for wireshark.exe, procmon.exe, x64dbg.exe, pestudio.exe, and fiddler.exe."
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the PrivateLoader binary:
[ "Not natively implemented (delegates credential theft to secondary payloads such as RedLine, Vidar, or Lumma Stealer)" ]
[ "Host hardware and software telemetry enumeration (OS version, architecture, CPU model, GPU vendor, active antivirus suite)" ]
[ "Modular task dispatch queue executing arbitrary remote executables, DLLs, and batch scripts" ]
[ "Download and write arbitrary files into %TEMP% and %APPDATA% directories", "Execute and delete staging files upon execution completion" ]
[ "Downloads and executes external clipper modules on high-priority targets" ]
[ "Scheduled task creation for automated continuous execution", "Secondary payload installation across administrative and standard user contexts" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "HTTP POST protocol over custom TCP ports with Base64-encoded parameters and RC4-encrypted body payloads",
  "serialization": "Key-value URL-encoded strings and JSON-formatted task lists",
  "handshake": "Client issues HTTP POST request containing Base64-encoded host identification string -> Server responds with HTTP 200 containing RC4-encrypted JSON array of assigned tasks",
  "cryptography": "RC4 stream cipher with static key embedded in binary; Base64 encoding applied to host telemetry parameters",
  "packet_types": [
    {
      "header": "POST /api/check_in.php HTTP/1.1",
      "payload": "guid=<HWID>&ver=2.4&os=<OS>&affiliate=<ID>&av=<AV_NAME>",
      "direction": "Client -> Server"
    },
    {
      "header": "HTTP/1.1 200 OK",
      "payload": "RC4_Ciphertext({tasks:[{id:101, url:'http://...', key:'...', type:'exe'}]})",
      "direction": "Server -> Client"
    },
    {
      "header": "POST /api/report_status.php HTTP/1.1",
      "payload": "guid=<HWID>&task_id=101&status=SUCCESS&err_code=0",
      "direction": "Client -> Server"
    }
  ],
  "traffic_signature": "Outbound HTTP POST requests characterized by custom User-Agent strings, high-numbered ports (e.g. 8080, 8000, 3128), and high-entropy base64/hex request bodies."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_PrivateLoader_Core {
    meta:
        description = "Detects PrivateLoader C++ downloader based on RC4 decryption loops, API hashing, and telemetry formatting"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "PrivateLoader"
        hash = "e159a647d9b0a7e6b09386d3b38c2c8f61e7a4b872f2e52b82142e88a08182b3"
    strings:
        $rc4_init = { 33 C0 89 44 24 ?? 88 84 04 ?? ?? 00 00 40 3D 00 01 00 00 7C }
        $s1 = "/api/check_in.php" ascii
        $s2 = "/api/report_status.php" ascii
        $s3 = "guid=" ascii
        $s4 = "affiliate=" ascii
        $s5 = "URLDownloadToFileW" ascii
        $s6 = "ShellExecuteExW" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 1MB and
        ($rc4_init or (3 of ($s*)))
}title: PrivateLoader Suspicious Download and Execution from Temp Directory
id: 4b2c1d3e-5f6a-4e7b-8c9d-0a1b2c3d4e5f
status: stable
description: Detects repetitive process creation patterns originating from %TEMP% or %APPDATA% directory triggered by unverified native binaries.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S1066/
tags:
- attack.execution
- attack.t1105
- attack.t1059
logsource:
category: process_creation
product: windows
detection:
selection:
ParentImage|contains:
- '\AppData\Local\Temp\'
- '\AppData\Roaming\'
Image|contains:
- '\AppData\Local\Temp\'
- '\AppData\Roaming\'
CommandLine|contains:
- '.exe'
- 'rundll32.exe'
filter_legit:
ParentImage|endswith:
- '\msiexec.exe'
- '\TrustedInstaller.exe'
condition: selection and not filter_legit
falsepositives:
- Software setup installers launching unpacked sub-installers from Temp
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
ANY.RUN technical diagram detailing corporate endpoint compromise via Pay-Per-Install malware distribution channels.
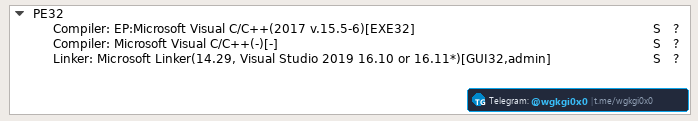
Process memory capture showing secondary payload downloading, decryption, and execution validation.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and HTTP POST over Custom Encrypted Ports command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
PrivateLoader (Loader)
Modular C++ Pay-Per-Install loader utilizing RC4 payload decryption, dynamic API resolving, and serialized HTTP task queue execution.
C2 Architecture: {'framing': 'HTTP POST protocol over custom TCP ports with Base64-encoded parameters and RC4-encrypted body payloads', 'serialization': 'Key-value URL-encoded strings and JSON-formatted task lists', 'handshake': 'Client issues HTTP POST request conta
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ PrivateLoader (Loader)
Детальный технический анализ PrivateLoader — это Загрузчик вредоносного ПО (Дроппер/Стейджер), разработанный на стеке Microsoft Visual C++ (MSVC 2017/2019/2022) with statically linked CRT (MT); native x86 PE32. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTP POST over TCP 80/8080/443; RC4 stream cipher encryption with embedded custom key; Base64 encoding) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTP POST over TCP 80/8080/443; RC4 stream cipher encryption with embedded custom key; Base64 encoding, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
PrivateLoader (Loader) विश्लेषण
PrivateLoader एक परिष्कृत मैलवेयर लोडर और ड्रॉपर पेलोड है जिसे Microsoft Visual C++ (MSVC 2017/2019/2022) with statically linked CRT (MT); native x86 PE32 का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTP POST over TCP 80/8080/443; RC4 stream cipher encryption with embedded custom key; Base64 encoding) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTP POST over TCP 80/8080/443; RC4 stream cipher encryption with embedded custom key; Base64 encoding आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).