01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C# Compiler (csc.exe)",
  "runtime": ".NET Common Language Runtime (CLR) 2.0.50727 or 4.0.30319",
  "binary_footprint": "PE32 .NET executable, typically 150 KB - 350 KB uncompressed",
  "stub_size": "262,144 bytes (vanilla stub), expanding up to 5 MB when wrapped in multi-stage packers or Lua loaders",
  "packer_obfuscation": "SmartAssembly, ConfuserEx, DotNetPusher, or packed within Lua bytecode interpreters executing native loaders",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "Entry -> Decrypt Config (IP, ID, Key) -> Establish WCF Channel -> Call TryGetArgs() -> Parse ScanSettings -> Enumerate Browsers/Wallets/VPNs -> Construct User Data Contract -> Call SendHit() / SaveResult() -> Terminate",
  "technical_summary": "RedLine Stealer is a commercial information stealer coded in C#. It distinguishes itself by leveraging the Windows Communication Foundation (WCF) framework over raw TCP sockets (net.tcp protocol) or HTTP bindings to exchange structured DataContract objects with the C2 server. Its modular architecture dynamically retrieves scanning parameters from the C2 server before initiating harvesting routines."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Desktop Operator Client & Web Panel",
  "builder_tabs_options": [
    {
      "tab": "Builder Configuration",
      "options": [
        "IP / Port: Target C2 endpoint address and listener port (e.g., 194.26.29.112:4125)",
        "Build ID: Operator tracking tag (e.g., 'red_campaign_01')",
        "Encryption Key: String key used for XOR configuration obfuscation"
      ]
    },
    {
      "tab": "Scan Rules (Arguments)",
      "options": [
        "ScanBrowsers: Toggles extraction of Chrome, Edge, Brave, Opera, Firefox credentials",
        "ScanFiles: Enables desktop and documents file grabber with custom extension list",
        "ScanFTP: Toggles extraction of saved credentials from FileZilla and WinSCP",
        "ScanWallets: Activates scanning for Armory, Atomic, Electrum, Ethereum, Exodus, Coinomi",
        "ScanTelegram / ScanDiscord: Toggles session token extraction",
        "ScanVPN: Extracts configurations from NordVPN, OpenVPN, and ProtonVPN"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "Arguments.IP",
      "field": "C2Address",
      "type": "String",
      "description": "XOR-encrypted C2 IP address or domain"
    },
    {
      "offset": "Arguments.ID",
      "field": "BuildId",
      "type": "String",
      "description": "Campaign identification identifier"
    },
    {
      "offset": "Arguments.Key",
      "field": "EncryptionKey",
      "type": "String",
      "description": "XOR passphrase string"
    },
    {
      "offset": "Arguments.Message",
      "field": "StatusMessage",
      "type": "String",
      "description": "Operational status tracking string"
    }
  ],
  "payload_generation_flags": [
    "Target CLR: AnyCPU",
    "String Encryption: Single-byte or multi-byte XOR with Base64",
    "WCF Binding: NetTcpBinding (SecurityMode.None)"
  ],
  "operator_commands": [
    "TryGetArgs: Invoked by client to obtain active scanning directives from C2",
    "SendHit: Invoked by client to transmit gathered credentials and hardware profile",
    "DownloadAndExecute: Instructs client to download external payload and execute via Process.Start"
  ],
  "interface_telemetry_analysis": "The RedLine management console provides operators with real-time log ingestion, filtering capabilities across harvested credentials, an integrated file viewer for grabber outputs, and detailed hardware telemetries including CPU architecture, installed anti-virus solutions, and UAC elevation states."
}struct RedLine_Stealer_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Often delivered via multi-stage loaders utilizing Lua scripts or native shellcode stagers that inject the unpacked .NET assembly into target host processes (e.g., msbuild.exe, cvtres.exe, or AddInProcess.exe) via VirtualAllocEx and WriteProcessMemory.",
  "ntapi_functions": [
    "kernel32!VirtualAllocEx",
    "kernel32!WriteProcessMemory",
    "kernel32!SetThreadContext",
    "kernel32!ResumeThread",
    "crypt32!CryptUnprotectData"
  ],
  "process_hollowing_target": "msbuild.exe, cvtres.exe, or explorer.exe",
  "persistence_mechanics": [
    "Typically executed without persistence (single-run harvesting mission)",
    "When configured for persistence: Creates Run registry entry under HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run"
  ],
  "evasion_hooks": [
    "Obfuscation of .NET metadata tokens and control-flow mangling via commercial protectors",
    "Dynamic runtime loading of assemblies via Assembly.Load(byte[])"
  ],
  "anti_analysis": [
    "WMI queries checking for virtual machine indicators: 'SELECT * FROM Win32_VideoController' evaluating Name for 'VirtualBox Graphics Adapter' or 'VMware SVGA'",
    "Evaluation of total physical memory (< 2GB) and CPU cores (< 2)",
    "Process enumeration checking for active monitoring tools (Wireshark, Fiddler, Process Hacker)"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the RedLine Stealer binary:
[ "Chromium browser password, cookie, and autofill harvesting using DPAPI CryptUnprotectData and AES-GCM master key decryption", "Gecko browser parsing extracting credentials from logins.json and key4.db", "FTP client credential recovery (FileZilla sitemanager.xml and recentservers.xml)", "VPN client configuration and credential recovery (NordVPN, OpenVPN, ProtonVPN)", "Cryptocurrency wallet vault theft across desktop clients (Electrum, Exodus, Atomic, Bitcoin Core) and 40+ browser extension IDs" ]
[ "System profiling: Operating system version, active user name, domain role, BIOS serial, monitor resolution, GPU model, active process list, installed software list" ]
[ "Task execution engine supporting secondary payload download and execution (DownloadAndExecute directive)" ]
[ "Configurable file grabber recursively scanning Desktop, Documents, and Downloads based on C2-supplied path and extension filters" ]
[ "N/A (Primarily relies on static wallet vault grabbing rather than dynamic clipboard modification)" ]
[ "N/A (Operates in user-mode space without kernel-level driver tampering)" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "WCF .NET binary framing or SOAP XML structure transmitted over raw TCP sockets",
  "serialization": ".NET DataContractSerializer encoding strongly-typed objects (ScanSettings, User, Result)",
  "handshake": "Client opens raw TCP connection to C2 port -> Transmits WCF framing preamble (0x00, 0x01, 0x00, 0x01, 0x02, 0x02) -> Initiates NetTcpBinding session -> Invokes TryGetArgs service method -> C2 returns XML/Binary serialized settings -> Client processes harvest and invokes SendHit",
  "cryptography": "Transport layer operates over plain TCP (SecurityMode.None) or TLS depending on builder selection. Payload data fields are obfuscated using multi-byte XOR combined with Base64 encoding.",
  "packet_types": [
    {
      "header": "WCF Action: TryGetArgs",
      "payload": "Client HWID, Campaign ID string",
      "direction": "Client -> C2"
    },
    {
      "header": "WCF Response: TryGetArgsResponse",
      "payload": "Serialized ScanSettings DataContract (boolean flags, file grabber rules)",
      "direction": "C2 -> Client"
    },
    {
      "header": "WCF Action: SendHit / SaveResult",
      "payload": "Serialized User DataContract (credentials, cookies, system info, wallet archives)",
      "direction": "Client -> C2"
    }
  ],
  "traffic_signature": "Outbound TCP connections to high-order ports (typ. 10000 - 50000) displaying WCF net.tcp stream preamble bytes (0x00, 0x01) followed by string references to 'http://tempuri.org/Entity/TryGetArgs'."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_RedLine_Stealer {
    meta:
        description = "Detects RedLine Stealer .NET binaries based on WCF service contracts, data members, and configuration routines"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "RedLine"
        hash = "f3a2c589710b14ef98e09f8c62b9a1249b5c3d2e1f08964728512ddb191c96da"
    strings:
        $wcf1 = "http://tempuri.org/Entity/TryGetArgs" ascii wide
        $wcf2 = "http://tempuri.org/Entity/SaveResult" ascii wide
        $wcf3 = "TryGetArgs" ascii
        $wcf4 = "ScanBrowsers" ascii
        $wcf5 = "ScanFiles" ascii
        $wcf6 = "ScanWallets" ascii
        $wcf7 = "ScanFTP" ascii
        $s1 = "Arguments" ascii
        $s2 = "Local State" ascii wide
        $s3 = "os_crypt" ascii
        $s4 = "encrypted_key" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 2MB and
        (3 of ($wcf*) and 2 of ($s*))
}title: RedLine Stealer WCF Network Connection and Credential Access
id: 8f7e6d5c-4b3a-2109-8765-43210fedcba9
status: stable
description: Detects executable processes establishing outbound TCP connections to high-order ports accompanied by rapid access to browser Local State and SQLite databases.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S0640/
tags:
- attack.collection
- attack.t1555
- attack.command_and_control
- attack.t1071
logsource:
category: process_creation
product: windows
detection:
selection_loader:
Image|endswith:
- '\cvtres.exe'
- '\msbuild.exe'
- '\AddInProcess.exe'
selection_cmdline:
CommandLine|contains:
- 'AppData\Local\Temp'
- 'Users\Public'
condition: selection_loader and selection_cmdline
falsepositives:
- Software build systems executing compilers in developer environments.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
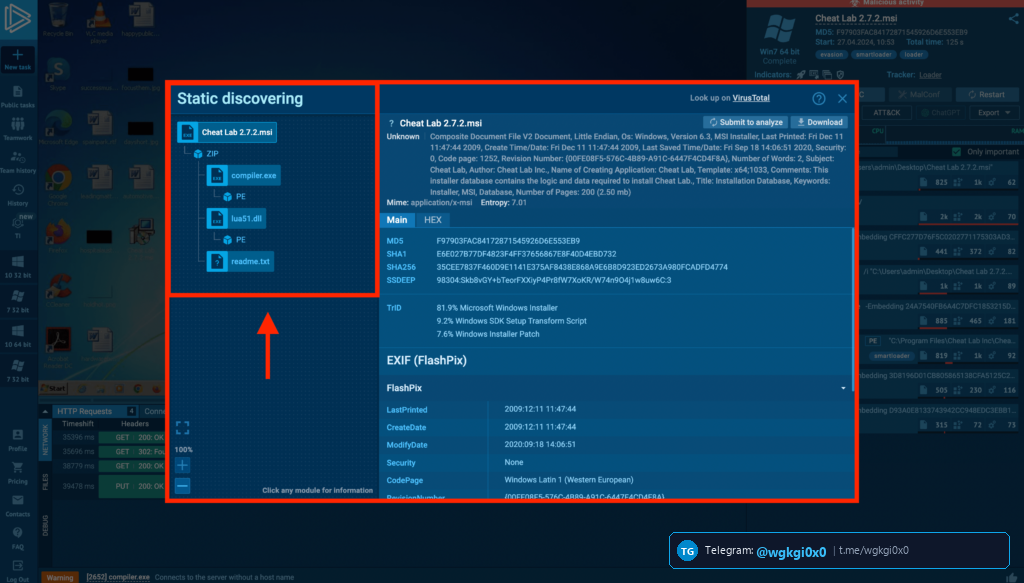
ANY.RUN sandbox capture showing Lua bytecode decompression and process hollowing into legitimate Windows processes.
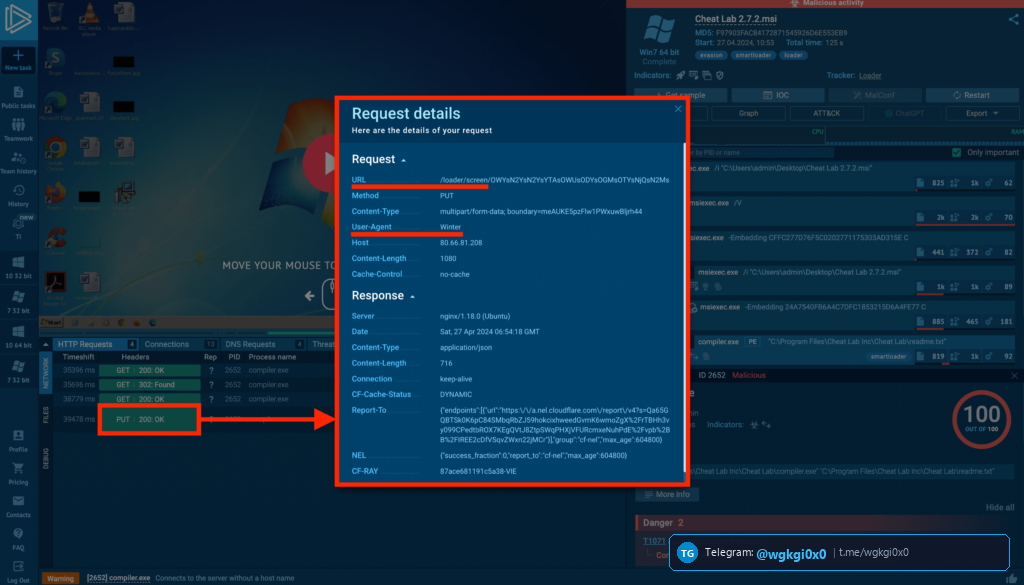
Forensic memory trace extracting DPAPI-protected credentials, session cookies, and cryptocurrency wallets.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Direct TCP, WCF Endpoints, Telegram Exfiltration command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
RedLine Stealer (InfoStealer)
C# information stealer utilizing Windows Communication Foundation (WCF) net.tcp framing for configuration exchange and credential exfiltration.
C2 Architecture: {'framing': 'WCF .NET binary framing or SOAP XML structure transmitted over raw TCP sockets', 'serialization': '.NET DataContractSerializer encoding strongly-typed objects (ScanSettings, User, Result)', 'handshake': 'Client opens raw TCP connection t
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ RedLine Stealer (InfoStealer)
Детальный технический анализ RedLine Stealer — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Microsoft C# Compiler (Roslyn) targeting .NET Framework 3.5 / 4.0. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Windows Communication Foundation (WCF) net.tcp / SOAP XML over raw TCP with XOR-Base64 encryption) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Windows Communication Foundation (WCF) net.tcp / SOAP XML over raw TCP with XOR-Base64 encryption, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
RedLine Stealer (InfoStealer) विश्लेषण
RedLine Stealer एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Microsoft C# Compiler (Roslyn) targeting .NET Framework 3.5 / 4.0 का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Windows Communication Foundation (WCF) net.tcp / SOAP XML over raw TCP with XOR-Base64 encryption) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Windows Communication Foundation (WCF) net.tcp / SOAP XML over raw TCP with XOR-Base64 encryption आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).