01 | Tool Specifications & Architectural Profile
Constructed entirely in C++ and MASM, linking directly against native Win32/NT subsystem libraries (kernel32.dll, user32.dll, advapi32.dll, ws2_32.dll). Does not depend on the .NET CLR or external runtimes. The binary relies on custom runtime dynamic linking: API function pointers are resolved dynamically via custom DJB2/ROR13 hash comparisons against export directories to suppress Import Address Table (IAT) indicators. The executable embeds a proprietary watchdog architecture and process injection module.
02 | Operator Interface & Configuration Struct Model
Remcos Professional incorporates a Win32 GUI client builder and real-time remote operations console. Builder configuration tabs include: 1) Connection: Primary/Fallback C2 Hosts, Port numbers, Keep-Alive ping frequency, Dynamic DNS update strings, and Master Password. 2) Installation: File path targets (%AppData%, %Temp%, %ProgramFiles%), randomized payload filename, Hidden and System file attribute switches, and Process Watchdog toggles. 3) Persistence: Registry Run keys (HKCU/HKLM), Winlogon Userinit hooks, and Scheduled Tasks. 4) Stealth: Target injection process list (explorer.exe, svchost.exe), Anti-VM checks (VMware, VirtualBox, QEMU, Sandboxie), and UAC elevation exploits (fodhelper.exe, eventvwr.exe). Config data is stored within the PE resource section (.rsrc) under resource type RT_RCDATA named 'SETTINGS'. The resource blob begins with a 32-byte RC4 initialization key followed by the encrypted configuration string.
struct Remcos_RAT_(Remote_Control_&_Surveillance)_Config {
    uint32_t magic;
    char c2_host[128];
    uint16_t port;
    char install_path[260];
    char mutex[64];
    uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
Execution begins by parsing its own PE resource directory via FindResourceA, LoadResource, and LockResource to retrieve the SETTINGS payload. It extracts the 32-byte key and decrypts the config buffer via standard RC4. If stealth mode is configured, Remcos spawns or targets an existing instance of explorer.exe or svchost.exe: 1) Obtains a process handle using OpenProcess(PROCESS_ALL_ACCESS). 2) Allocates virtual memory in the remote target using VirtualAllocEx(MEM_COMMIT | MEM_RESERVE, PAGE_EXECUTE_READWRITE). 3) Writes the decrypted payload and bootstrap shellcode via WriteProcessMemory. 4) Executes the injected code via CreateRemoteThread or NtQueueApcThread. Persistence is reinforced via a separate Watchdog process: both binaries monitor mutually held named Mutexes (e.g., 'Remcos-XXXXXX'); termination of one process causes the other to immediately respawn it.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Remcos RAT (Remote Control & Surveillance) binary:
Direct Win32 anonymous pipe redirection (CreatePipe, DuplicateHandle) linking cmd.exe or powershell.exe standard I/O streams to the C2 network socket.
Hidden Desktop Architecture: Invokes CreateDesktopA and OpenDesktopA to initialize an independent, isolated desktop session. Launches browsers (Chrome, Firefox, Edge) inside the hidden session, intercepting mouse and keyboard input without disrupting the active physical user desktop.
Integrates an asynchronous SOCKS5 proxy engine allowing operators to pivot interactive traffic through the victim host into internal enterprise subnets.
Implements an offline keylogger using SetWindowsHookExA(WH_KEYBOARD_LL). Encrypts keystrokes via RC4 and flushes them to a local hidden file (%APPDATA%\remcos\logs.dat). Also captures clipboard contents and window focus changes.
DirectShow API video frame grabbing from local webcams; audio stream recording via Windows WaveIn / Core Audio APIs; multi-monitor desktop capture and real-time screen streaming via GDI bitblt.
Extracts stored passwords and session cookies from Chromium, Firefox, Thunderbird, Outlook, WinSCP, FileZilla, and Windows Credential Manager.
05 | Wire Protocol & C2 Communication Framing
Communication operates over raw TCP sockets. The session is initialized via a symmetric RC4 cipher or optional TLS wrapper. Wire packet structure: [4 Bytes Little-Endian Length Prefix] [1 Byte Packet Type] [Command Delimiter '|remcos|'] [Variable Length Command & Arguments]. Handshake sequence: 1) Client initiates socket connection to configured C2:Port. 2) Client transmits encrypted Identification Beacon: 'remcos|version|OS|ComputerName|UserName|RAM|PrivilegeLevel(Admin/User)|CamAvailable|MicAvailable'. 3) C2 server returns tasking command strings (e.g., 'start_hvnc', 'get_passwords', 'start_socks:1080'). 4) Heartbeat packets: Client sends periodic 4-byte ping headers at operator-configured intervals to keep socket state alive through NAT firewalls.
06 | Verified Detection Signatures (YARA & Sigma)
rule Mal_Win_Remcos_Core {
    meta:
        description = "Detects native Remcos RAT binary, decrypted command strings, and RC4 resource parser"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        hash = "3d66fc88c224eb9a94191d81db09bfd3ca9762198038d7285dc327429158434a"
        threat_id = "TF-007"
    strings:
        $res = "SETTINGS" ascii wide fullword
        $cmd1 = "Remcos restarted by Watchdog" ascii
        $cmd2 = "\AppData\Roaming\remcos\logs.dat" ascii
        $cmd3 = "[Following opened window: " ascii
        $cmd4 = "Breaking-Security" ascii wide
        $cmd5 = "\connector.exe" ascii
        $delimit = "|remcos|" ascii
        $rc4_init = { 8A 04 0B 88 04 0A 88 0C 0B } // RC4 swap instruction sequence
    condition:
        uint16(0) == 0x5A4D and
        ( ($res and 2 of ($cmd*)) or ($delimit and 1 of ($cmd*)) or $rc4_init )
}title: Remcos RAT Registry Persistence and Process Injection
id: e9476b10-d021-4b11-9a44-22b64d02e007
status: production
description: Detects Remcos RAT execution patterns, including Run key additions from AppData and injection into explorer.exe.
references:
- https://cybertrace.io/threats/remcos-whitepaper.html
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
category: process_creation
product: windows
detection:
selection_img:
Image|endswith:
- '\AppData\Roaming\remcos\remcos.exe'
- '\AppData\Local\Temp\remcos.exe'
selection_injection:
TargetImage|endswith: '\explorer.exe'
SourceImage|contains: '\AppData\'
GrantedAccess: '0x1F0FFF'
condition: selection_img or selection_injection
falsepositives:
- None observed in standard enterprise environments
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
3d66fc88c224eb9a94191d81db09bfd3ca9762198038d7285dc327429158434a
8a2b53f65cd600b3438676a6ceb52f50567dc8ef58c73c8808dcfa7ae293b679
bf448cc40e5318db49b5c2d338fbf5bc4727142b78119ce06259f63f59db5a3e
185.143.223[.]12:2404
remcos-c2.ddns[.]net:1153
94.156.65[.]88:5050
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\Remcos
HKCU\Software\Remcos-Professional
%APPDATA%\remcos\logs.dat
%APPDATA%\remcos\remcos.exe
%TEMP%\connector.exe
Remcos-0198AB
Remcos_Watchdog_Mutex
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
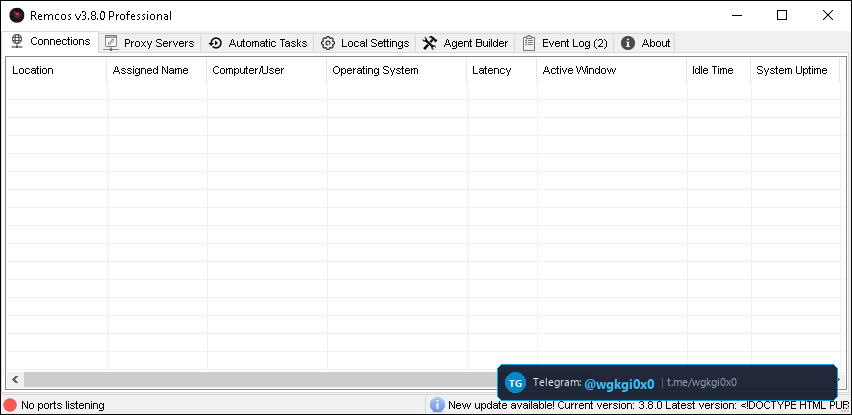
Builder interface displaying TLS encryption parameters, rootkit cloaking, watchdog persistence, and anti-analysis options.

Management console monitoring connected remote bots, system telemetry, and active surveillance streams.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Direct Encrypted TLS, Dynamic DNS, SOCKS5 Proxy command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Remcos RAT (Remote Control & Surveillance) (RAT)
Commercial-grade native C++ remote access tool abused for enterprise intrusion, incorporating SOCKS5 pivoting, HVNC desktop isolation, and RC4 packet streaming.
C2 Architecture: Communication operates over raw TCP sockets. The session is initialized via a symmetric RC4 cipher or optional TLS wrapper. Wire packet structure: [4 Bytes Little-Endian Length Prefix] [1 Byte Packet Type] [Command Delimiter '|remcos|'] [Variable Len
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Remcos RAT (Remote Control & Surveillance) (RAT)
Детальный технический анализ Remcos RAT (Remote Control & Surveillance) — это Троян удаленного доступа (RAT), разработанный на стеке Microsoft Visual C++ / Native Win32 PE (x86/x64). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Custom RC4 Stream Cipher / TLS-Wrapped TCP Socket) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Custom RC4 Stream Cipher / TLS-Wrapped TCP Socket, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Remcos RAT (Remote Control & Surveillance) (RAT) विश्लेषण
Remcos RAT (Remote Control & Surveillance) एक परिष्कृत रिमोट एक्सेस ट्रोजन (RAT) है जिसे Microsoft Visual C++ / Native Win32 PE (x86/x64) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Custom RC4 Stream Cipher / TLS-Wrapped TCP Socket) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Custom RC4 Stream Cipher / TLS-Wrapped TCP Socket आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).