01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual Basic / C# .NET Compiler via System.CodeDom.Compiler",
  "runtime": ".NET Common Language Runtime (CLR) v2.0.50727 / v4.0.30319",
  "binary_footprint": "Ultra-compact PE32 .NET CIL stub, typically 16 KB - 32 KB unpacked",
  "stub_size": "20,480 bytes (vanilla Lime stub), frequently wrapped in 60 KB - 300 KB VBS/JScript/PowerShell CodeDom stagers",
  "packer_obfuscation": "SmartAssembly, ConfuserEx, CryptoObfuscator, or fileless PowerShell/VBS stagers invoking CodeDomProvider.CompileAssemblyFromSource and InstallUtil.exe",
  "subsystem": "Windows GUI (IMAGE_SUBSYSTEM_WINDOWS_GUI = 2)",
  "entry_point_flow": "Lime.Program.Main() -> Settings.Initialize() -> Helper.CreateMutex() -> IdGenerator.InitializeProfiling() -> Client.BeginConnect() -> Client.TcpReceive() -> Client.PacketFixer() -> Packets.Read()",
  "technical_summary": "RevengeRAT (v0.3) is a lightweight .NET remote access trojan authored by EvilCoder and later maintained/forked by NYAN-x-CAT under the internal 'Lime' namespace architecture (Lime.Connection, Lime.Helper, Lime.NativeMethods, Lime.Packets, Lime.Settings). Designed with a minimal 20 KB core stub, RevengeRAT offloads post-exploitation functionality into modular .NET plugins transmitted over the C2 channel and executed in memory via Assembly.Load. In the wild, it is predominantly deployed through multi-stage VBS or PowerShell scripts that dynamically compile a C# wrapper using CodeDomProvider.CompileAssemblyFromSource and abuse the signed Microsoft binary InstallUtil.exe to inject the Lime stub into legitimate processes."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "GUI Builder / Operator Console (Revenge-RAT v0.3)",
  "builder_tabs_options": [
    {
      "tab": "Main Navigation Sidebar",
      "options": [
        "Clients: Live grid of connected victims displaying Country, IP, ID/HWID, Username, OS, Antivirus, CPU, RAM, and Active Window",
        "Thumbnails: Continuous tile view of desktop screenshots across active bots",
        "Clients Map: Geographic world map plotting victim IP geolocation coordinates",
        "Ports & Logs: Listener port configuration and real-time connection/plugin event log",
        "Client Builder: Multi-step stub compiler configuring Hosts, Pastebin dead-drop, Persistence, and Assembly metadata",
        "Plugins Control & On-Connect: Manages server-side plugin DLLs and configures automatic execution triggers upon initial bot check-in"
      ]
    },
    {
      "tab": "Client Builder - Network & Dead-Drop",
      "options": [
        "Host / IP List: Primary C2 domains or IP addresses with round-robin reconnection",
        "Port Array: Listener TCP ports (default: 4488, 1177, 5552)",
        "Splitter Key: Custom packet delimiter token (default: 'SPL-R-DATA' or '|-|')",
        "Pastebin Resolver: Raw Pastebin URL returning 'Host:Port' string dynamically before socket initialization"
      ]
    },
    {
      "tab": "Client Builder - Installation & Persistence",
      "options": [
        "Drop & Install: Copies binary to %AppData%, %Temp%, or %UserProfile% with optional hidden/system attributes",
        "Startup Methods: Registry HKCU\\...\\Run, Startup Folder LNK/copy, and schtasks.exe logon trigger",
        "Mutex String: Custom mutex token (e.g., RV_MUTEX_*)"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "Lime.Settings.Host",
      "field": "Host",
      "type": "List<string> / String",
      "description": "Configured C2 hostnames or IPv4 addresses"
    },
    {
      "offset": "Lime.Settings.Port",
      "field": "Port",
      "type": "List<int> / String",
      "description": "Configured C2 TCP ports"
    },
    {
      "offset": "Lime.Settings.SPL",
      "field": "SPL",
      "type": "String",
      "description": "Packet field and frame delimiter string (default: 'SPL-R-DATA')"
    },
    {
      "offset": "Lime.Settings.KEY",
      "field": "KEY",
      "type": "String",
      "description": "Stream end-of-packet marker and authentication token"
    },
    {
      "offset": "Lime.Settings.ID",
      "field": "ID",
      "type": "String",
      "description": "Base64-encoded campaign identifier tag"
    },
    {
      "offset": "Lime.Settings.Mutex",
      "field": "Mutex",
      "type": "String",
      "description": "Single-instance mutex string passed to System.Threading.Mutex"
    },
    {
      "offset": "Lime.Settings.Pastebin",
      "field": "Pastebin",
      "type": "String",
      "description": "Optional dead-drop URL queried via System.Net.WebClient.DownloadString"
    }
  ],
  "payload_generation_flags": [
    "Target Platform: x86 (32-bit required for RunPE / process hollowing compatibility)",
    "Target CLR: .NET Framework v2.0 / v4.0",
    "Compiler Engine: CodeDom / Mono.Cecil stub patching"
  ],
  "operator_commands": [
    "INF / SendInfo: Transmits hardware and OS fingerprint assembled by IdGenerator class",
    "PLG / Plugin: Loads GZip-decompressed .NET DLL via Assembly.Load and invokes its entry method",
    "PNG / Ping: Measures round-trip socket latency and updates Active Window title via GetActiveWindow()",
    "RD / RemoteDesktop: Streams GDI screen captures via dedicated plugin channel",
    "FM / FileManager: Enumerates logical drives, directories, and files",
    "KL / Keylogger: Captures keystrokes via SetWindowsHookEx or GetAsyncKeyState plugin",
    "UN / Uninstall: Removes persistence entries and terminates client process"
  ],
  "interface_telemetry_analysis": "The RevengeRAT v0.3 console features a clean flat-UI sidebar providing instant switching between Clients, Thumbnails, Clients Map, Ports, Client Builder, Logs, Plugins Control, and On-Connect automation. Right-clicking any client opens a modular context menu where every action dynamically dispatches the corresponding .NET plugin DLL from the server's 'Plugins' directory."
}struct RevengeRAT_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "CodeDom + InstallUtil LOLBin Execution & RunPE: Obfuscated VBS/PowerShell stager invokes System.CodeDom.Compiler.CodeDomProvider.CompileAssemblyFromSource to compile a temporary C# loader DLL containing a [System.ComponentModel.RunInstaller(true)] class override -> Spawns %Windir%\\Microsoft.NET\\Framework\\v4.0.30319\\InstallUtil.exe /logfile= /LogToConsole=false /U <TempDLL> -> Inside Uninstall() override, executes RunPE (CreateProcessA suspended -> NtUnmapViewOfSection -> VirtualAllocEx -> WriteProcessMemory -> SetThreadContext -> ResumeThread) injecting the unpacked RevengeRAT Lime stub into RegAsm.exe or vbc.exe.",
  "ntapi_functions": [
    "user32!GetForegroundWindow",
    "user32!GetWindowTextA",
    "kernel32!GetVolumeInformationA",
    "iphlpapi!GetExtendedTcpTable",
    "ntdll!NtUnmapViewOfSection",
    "kernel32!VirtualAllocEx",
    "kernel32!WriteProcessMemory",
    "kernel32!SetThreadContext"
  ],
  "process_hollowing_target": "InstallUtil.exe (parent LOLBin), injecting into RegAsm.exe, vbc.exe, AppLaunch.exe, or MSBuild.exe",
  "persistence_mechanics": [
    "Scheduled Task: schtasks /create /sc minute /mo 1 /tn \"UpdateService\" /tr \"wscript.exe //B '%AppData%\\stager.vbs'\"",
    "Registry Run Key: HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run\\[MutexOrName]",
    "Startup Folder LNK: Creates Windows Script Host WshShell shortcut in %AppData%\\Microsoft\\Windows\\Start Menu\\Programs\\Startup"
  ],
  "evasion_hooks": [
    "LOLBin Proxy Execution: Executes inside trusted Microsoft-signed InstallUtil.exe to bypass application whitelisting (AppLocker)",
    "Firewall Rule Injection: Executes netsh advfirewall firewall add rule name=\"System\" dir=in action=allow program=\"<StubPath>\" enable=yes",
    "Reflective Plugin Architecture: Core stub contains zero credential theft or surveillance code on disk; all modules execute from volatile memory via Assembly.Load"
  ],
  "anti_analysis": [
    "WMI SecurityCenter2 Enumeration: IdGenerator.GetAV() queries root\\SecurityCenter2 (or root\\SecurityCenter on legacy OS) 'SELECT * FROM AntivirusProduct' to report installed EDR/AV products",
    "Volume Serial Fingerprinting: IdGenerator.GetHardDiskSerialNumber() invokes ManagementObject('Win32_LogicalDisk.DeviceID=\"C:\"') or kernel32!GetVolumeInformationA to derive a deterministic Victim HWID"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the RevengeRAT binary:
[ "Reflectively loaded Password Recovery plugin harvesting saved credentials from Chrome, Firefox, Edge, Opera, FileZilla, and Outlook", "VaultCli.dll Windows Credential Manager enumeration", "Product key extractor recovering Windows and Microsoft Office license keys from DigitalProductId registry values" ]
[ "Active window title tracker in IdGenerator.GetActiveWindow() calling user32!GetForegroundWindow and GetWindowText", "Remote Desktop streaming plugin using JPEG-compressed GDI screen captures", "Webcam and Microphone streaming plugins utilizing DirectShow / waveIn APIs", "Keystroke and clipboard logging plugin storing offline logs or streaming live to operator console" ]
[ "Remote Shell plugin redirecting cmd.exe and powershell.exe standard I/O streams", "TCP Connections Manager plugin enumerating active sockets via iphlpapi!GetExtendedTcpTable and allowing remote connection termination", "Process Manager, Service Manager, and Registry Editor plugins providing full administrative control" ]
[ "Interactive File Manager plugin supporting thumbnail image previews, archive zipping/unzipping, download, upload, and execution" ]
[ "Optional On-Connect Clipper plugin monitoring clipboard buffer for BTC and ETH wallet strings" ]
[ "Hosts file editor plugin modifying %SystemRoot%\\System32\\drivers\\etc\\hosts", "System power control, BSOD trigger, and client self-updater" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Delimiter-based stream framing handled by Client.PacketFixer(byte[] bytesArray, string splitter). Packets consist of UTF-8 strings separated by Lime.Settings.SPL (default 'SPL-R-DATA' or '|-|') and terminated by Lime.Settings.KEY.",
  "serialization": "Plaintext UTF-8 string tokens separated by the configured splitter string, with binary payloads (screenshots, plugins, files) GZip-compressed and Base64-encoded or separated by raw byte delimiters.",
  "handshake": "Optional HTTP GET to Pastebin raw URL to resolve C2 Host:Port -> TCP Socket Connect -> Client invokes IdGenerator.SendInfo() -> Transmits 'INF' + SPL + Base64(ID) + SPL + HWID + SPL + Username + SPL + OS + SPL + AV + SPL + CPU + SPL + RAM + SPL + ActiveWindow + KEY",
  "cryptography": "No native transport encryption (plaintext TCP stream with Base64 and GZip encoding for binary blobs), making wire traffic directly inspectable for splitter tokens.",
  "packet_types": [
    {
      "header": "INF (IdGenerator.SendInfo)",
      "payload": "SPL-delimited array: Campaign ID, Volume Serial HWID, Username, OS Name, Antivirus (GetAV), CPU Name (GetCpu), RAM capacity, Active Window title",
      "direction": "Client -> Server"
    },
    {
      "header": "PLG (Plugin Dispatch)",
      "payload": "SPL-delimited plugin type identifier, GZip-compressed .NET assembly bytes, and execution arguments",
      "direction": "Server -> Client"
    },
    {
      "header": "PNG (Heartbeat & Window Update)",
      "payload": "Current foreground window title retrieved by IdGenerator.GetActiveWindow() and latency ping check",
      "direction": "Bidirectional"
    },
    {
      "header": "CAP (Thumbnail Preview)",
      "payload": "Low-resolution JPEG thumbnail bytes for the main console Thumbnails tab",
      "direction": "Client -> Server"
    }
  ],
  "traffic_signature": "Plaintext TCP stream containing repeating ASCII delimiter strings such as 'SPL-R-DATA', '|-|', or 'Revenge-RAT' interspersed with Base64 strings and GZip headers (H4sIAAAAAAA in Base64 or 1F 8B 08 in raw bytes)."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_RevengeRAT_Lime_Stub {
    meta:
        description = "Detects RevengeRAT .NET client stubs via Lime namespace classes, IdGenerator methods, and SPL-R-DATA framing strings"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-31"
        family = "RevengeRAT"
        hash = "6a1d8c3e9f2b4075a8123948576bcdef0123456789abcdef0123456789abcdef"
    strings:
        $ns1 = "Lime.Connection" ascii
        $ns2 = "Lime.Helper" ascii
        $ns3 = "Lime.Packets" ascii
        $ns4 = "Lime.Settings" ascii
        $m1 = "IdGenerator" ascii
        $m2 = "PacketFixer" ascii
        $m3 = "GetHardDiskSerialNumber" ascii
        $m4 = "SendInfo" ascii
        $spl1 = "SPL-R-DATA" ascii wide
        $spl2 = "Revenge-RAT" ascii wide nocase
        $wmi1 = "win32_logicaldisk.deviceid=" ascii wide nocase
        $wmi2 = "SELECT * FROM AntivirusProduct" ascii wide nocase
    condition:
        uint16(0) == 0x5A4D and
        filesize < 1MB and
        (
            (3 of ($ns*)) or
            (3 of ($m*) and ($wmi1 or $wmi2)) or
            ($spl1 and 1 of ($m*)) or
            ($spl2 and 2 of ($m*))
        )
}title: RevengeRAT CodeDom Stager and InstallUtil LOLBin Execution
id: 7c3e9a1b-4d2f-4e8a-9b5c-3e1f2a4b6c8d
status: stable
description: Detects execution of Microsoft InstallUtil.exe with uninstall flags (/U) spawned by script interpreters (wscript, cscript, powershell), a primary staging chain for RevengeRAT.
author: CyberTrace Defense Engineering
date: 2026/10/31
references:
- https://attack.mitre.org/techniques/T1218/004/
- https://attack.mitre.org/software/S0379/
tags:
- attack.defense_evasion
- attack.t1218.004
- attack.execution
- attack.t1059.005
logsource:
category: process_creation
product: windows
detection:
selection_parent:
ParentImage|endswith:
- '\wscript.exe'
- '\cscript.exe'
- '\powershell.exe'
- '\mshta.exe'
selection_installutil:
Image|endswith: '\InstallUtil.exe'
CommandLine|contains:
- '/U'
- '/logfile='
- '/LogToConsole=false'
condition: selection_parent and selection_installutil
falsepositives:
- Rare administrative scripts invoking InstallUtil.exe from WSH or PowerShell.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
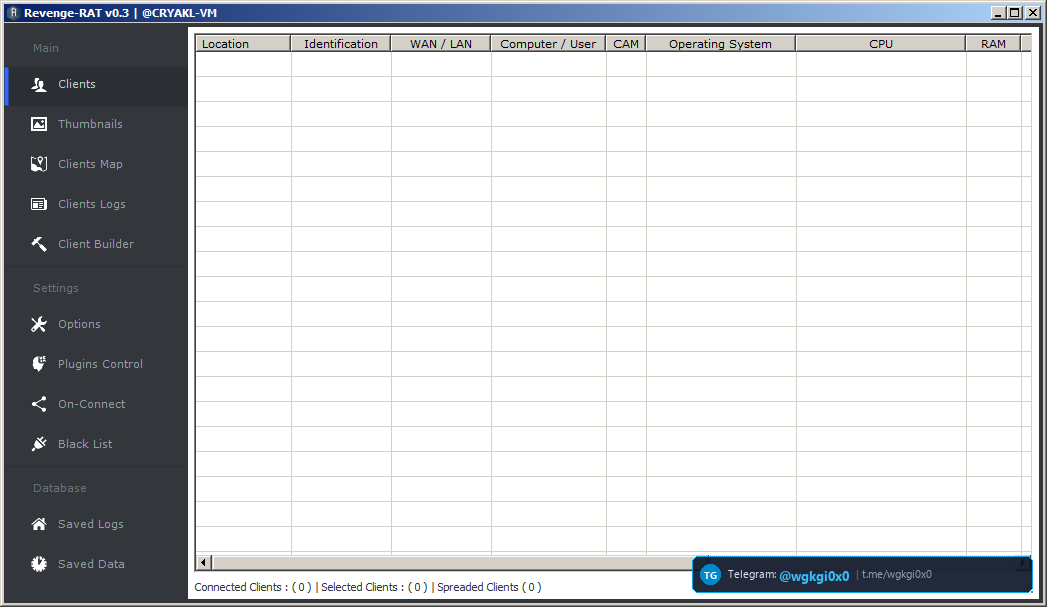
Revenge-RAT v0.3 operator console showing Clients, Thumbnails, Clients Map, Client Builder, Plugins Control, and On-Connect automation.
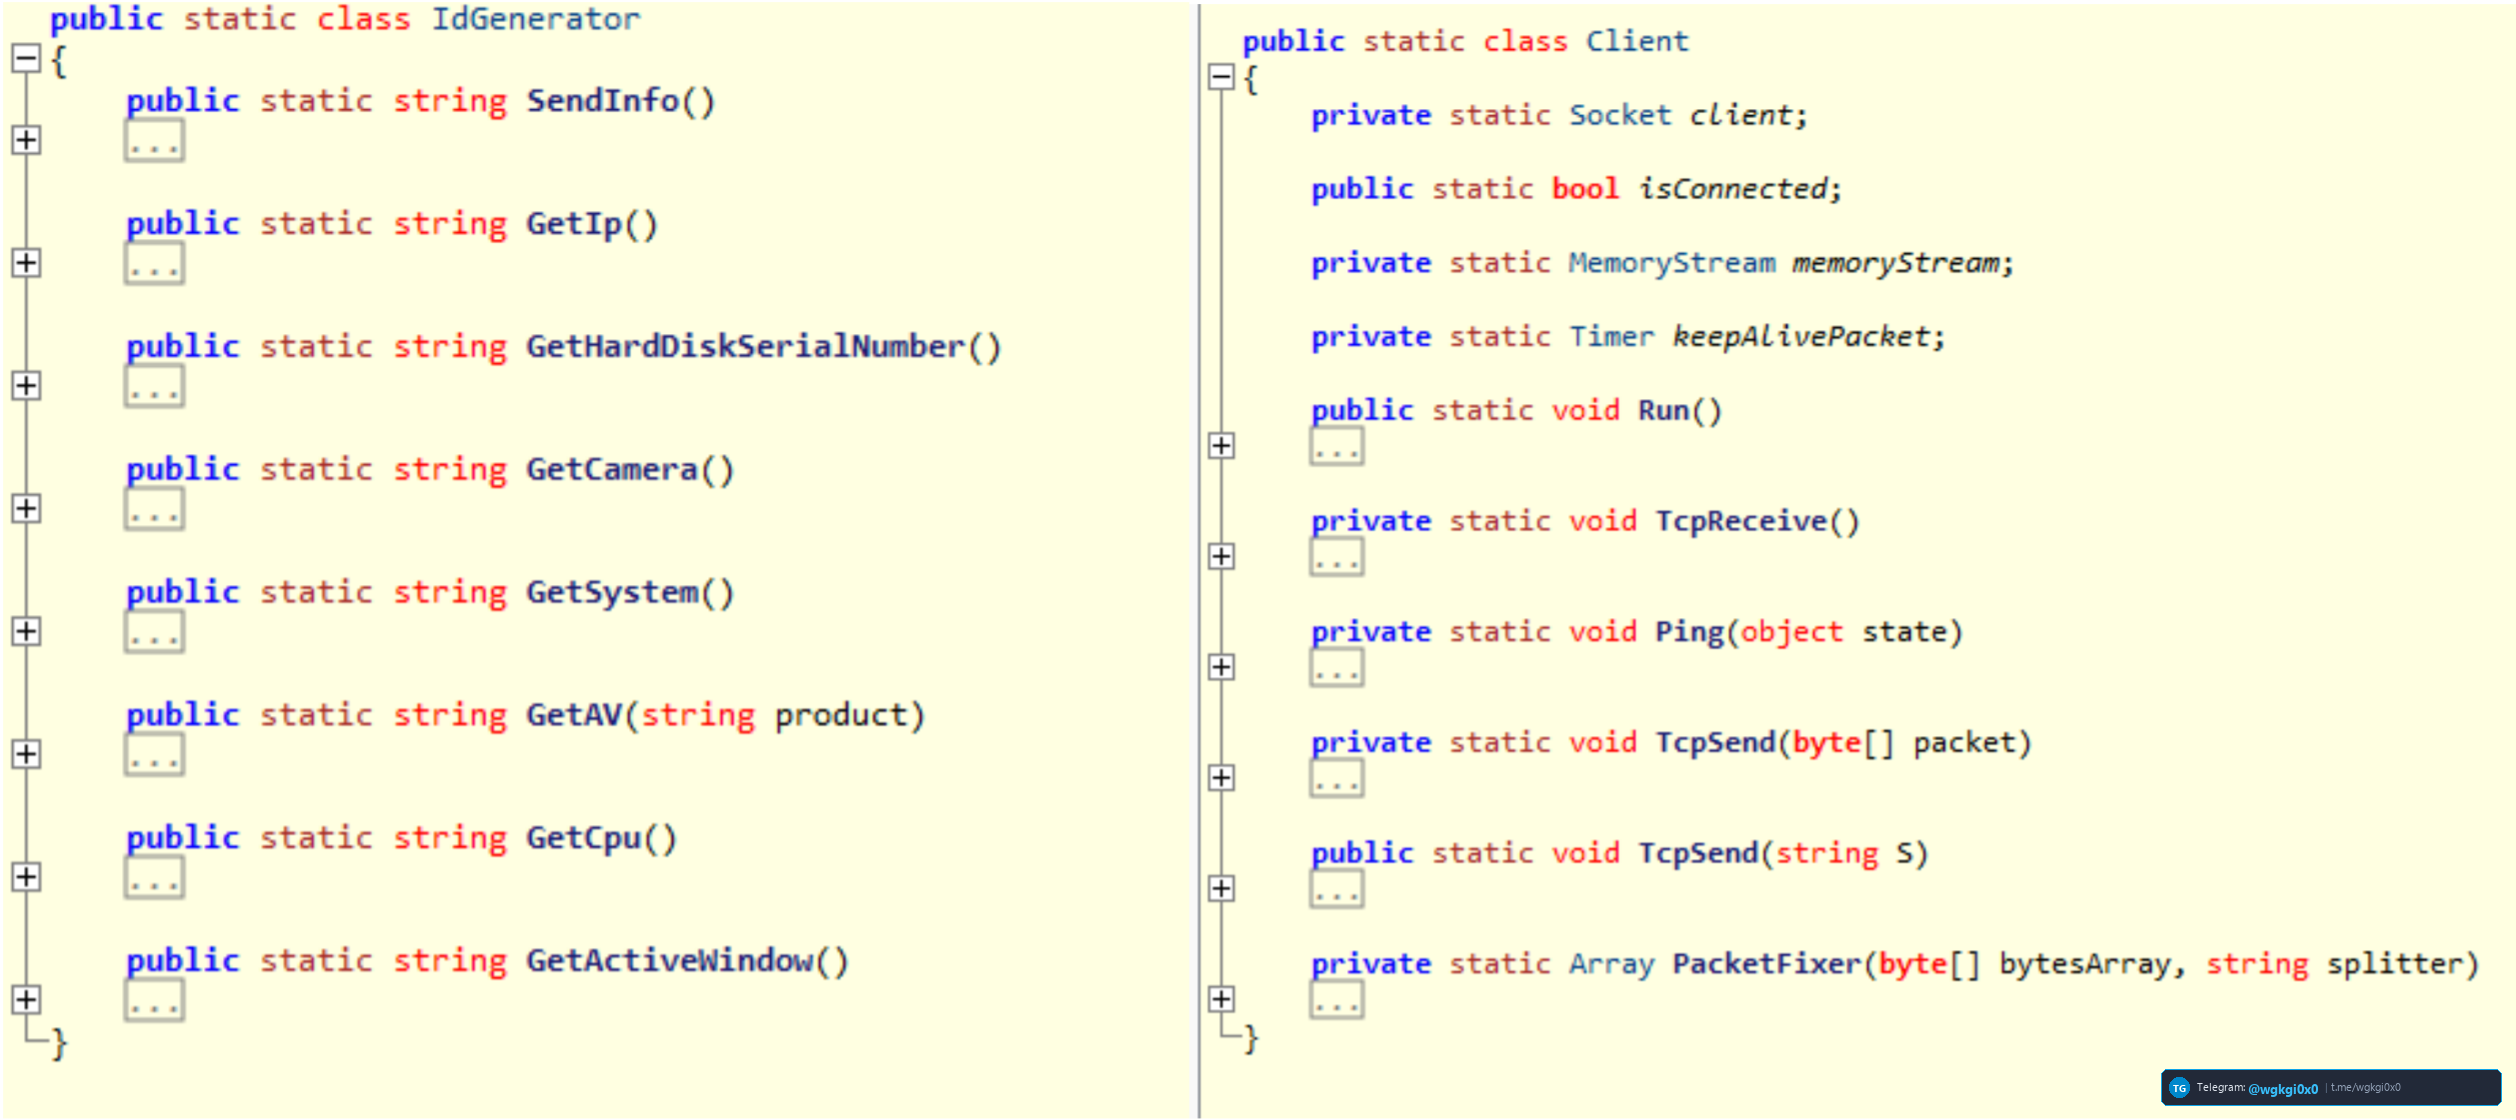
dnSpy decompilation of RevengeRAT C# stub showing IdGenerator hardware profiling and Client.PacketFixer delimiter framing.
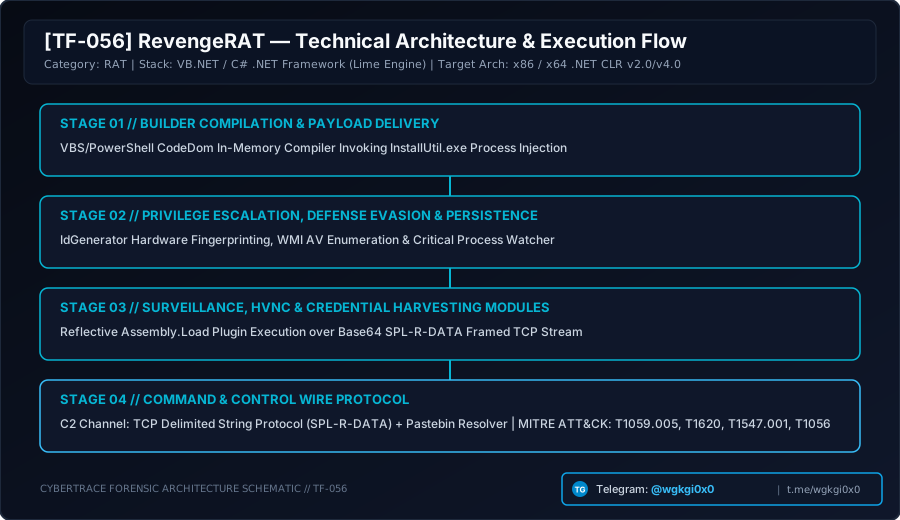
Forensic schematic mapping VBS/PowerShell CodeDom staging, InstallUtil.exe injection, IdGenerator WMI profiling, and SPL-R-DATA TCP framing.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
RevengeRAT (RAT)
Lightweight VB.NET/C# remote access trojan built on the 'Lime' engine, featuring WMI hardware profiling (IdGenerator), delimiter-framed TCP sockets (SPL-R-DATA), and reflective plugin execution.
C2 Architecture: {'framing': "Delimiter-based stream framing handled by Client.PacketFixer(byte[] bytesArray, string splitter). Packets consist of UTF-8 strings separated by Lime.Settings.SPL (default 'SPL-R-DATA' or '|-|') and terminated by Lime.Settings.KEY.", 'ser
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ RevengeRAT (RAT)
Детальный технический анализ RevengeRAT (v0.3) — модульного .NET-трояна удаленного доступа (RAT), написанного на VB.NET/C#. В отчете разбираются бесфайловая доставка через VBS/PowerShell, внедрение в легитимные процессы InstallUtil.exe и RegAsm.exe, генерация аппаратного идентификатора жертвы (IdGenerator через WMI) и динамическая подгрузка плагинов через Assembly.Load.
Архитектура C2: Асинхронный протокол поверх сырых TCP-сокетов с использованием строкового разделителя пакетов SPL-R-DATA, Base64-кодирования и GZip-сжатия.
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
RevengeRAT (RAT) विश्लेषण
RevengeRAT (v0.3) एक VB.NET/C# आधारित मॉड्यूलर विंडोज रिमोट एक्सेस ट्रोजन (RAT) है। इस तकनीकी रिपोर्ट में VBS/PowerShell CodeDom स्टेजिंग, InstallUtil.exe और RegAsm.exe प्रोसेस हॉलोइंग, IdGenerator WMI हार्डवेयर फिंगरप्रिंटिंग और इन-मेमोरी Assembly.Load प्लगइन निष्पादन का पूर्ण विश्लेषण दिया गया है।
C2 संचार: SPL-R-DATA स्ट्रिंग डिलिमिटर, Base64 एन्कोडिंग और GZip संपीड़न के साथ कच्चे TCP सॉकेट C2 प्रोटोकॉल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).