01 | Tool Specifications & Architectural Profile
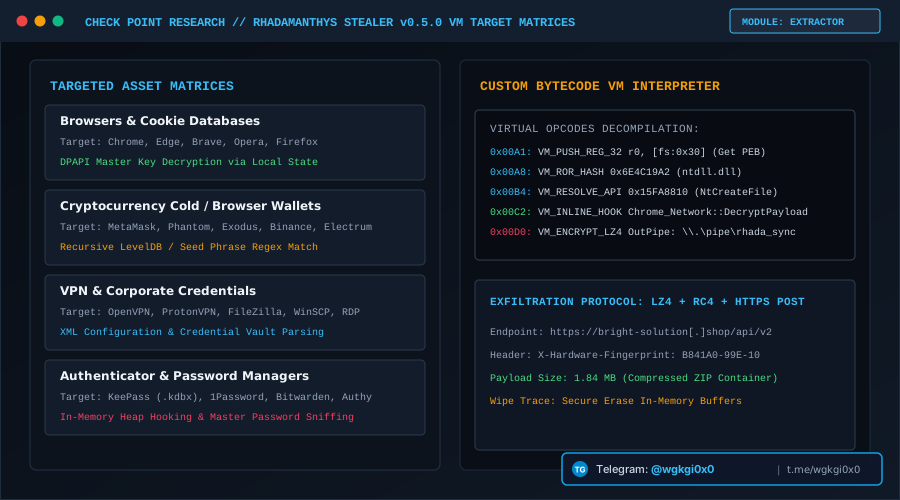
Authored in high-performance native modern C++ (MSVC), Rhadamanthys represents one of the most structurally complex infostealers in the threat catalog. Its internal architecture is centered around a proprietary, custom-designed Virtual Machine (VM) and an encrypted Virtual File System (VFS). Rather than executing static x86/x64 routines for credential extraction, the binary decrypts an embedded bytecode image and feeds it into an internal register-based VM interpreter. Modules (browser theft, wallet scrapers, network stacks) are stored as compressed virtual modules inside the VFS container, unpacked into memory dynamically using LZ4 / Zstandard algorithms without writing artifacts to disk.
02 | Operator Interface & Configuration Struct Model
Rhadamanthys is distributed under a commercial Malware-as-a-Service model managed via a dark-web web panel. Operators configure payload build profiles through a web console that compiles customized stagers: targets include Chromium browsers, Gecko browsers, 100+ cryptocurrency browser extension IDs, desktop cold wallets (Exodus, Atomic, Electrum), email clients (Outlook, Thunderbird), FTP/SSH keys (FileZilla, PuTTY, OpenVPN), and specific file grabber path patterns (.txt, .pdf, .docx, .kdbx). The configurator compiles the operator's settings directly into the encrypted VM bytecode container embedded in the .data section.
struct Rhadamanthys_Stealer_Config {
    uint32_t magic;
    char c2_host[128];
    uint16_t port;
    char install_path[260];
    char mutex[64];
    uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
Execution progresses across three internal stages: 1) The stager binary allocates a private memory arena using NtAllocateVirtualMemory. 2) Decrypts the proprietary VM bytecode interpreter and VFS container via ChaCha20/AES. 3) The VM interpreter begins executing virtual instructions via an opcode dispatcher loop. To evade endpoint detection and response (EDR) hooks, Rhadamanthys resolves syscall numbers dynamically at runtime by reading clean ntdll.dll code from disk or parsing the export directory in memory, directly issuing direct system calls (SSN execution) for memory protection and injection. It inspects loaded modules for inline hooks (checking for 0xE9 JMP or 0xCC INT3 bytes at export entry points); if hooks are detected, it overwrites the hooked bytes in memory with pristine opcodes extracted from the clean PE image on disk. It injects virtual modules into legitimate processes (such as rundll32.exe, WerFault.exe, or explorer.exe) via NtCreateSection / NtMapViewOfSection.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Rhadamanthys Stealer binary:
Advanced Chromium credential extractor: parses Local State to retrieve encrypted_key, uses DPAPI CryptUnprotectData, and implements elevated token extraction targeting Chrome v127+ App-Bound Encryption. Extracts Login Data, Cookies, Web Data (autofill, credit cards), and History. Recovers Firefox passwords by loading nss3.dll dynamically.
Mass extraction engine targeting over 100 cryptocurrency wallet extensions by scanning Chrome/Edge profile extension directories: MetaMask (nkbihfbeogaeaoehlefnkodbefgpgknn), Phantom, Coinbase, TronLink, Binance Chain, Ronin. Also extracts desktop wallet application datastores: Exodus (exodus.wallet), Atomic Wallet, Electrum, Armory, Ledger Live, and Trezor session databases.
Parses Microsoft Outlook registry profiles, Thunderbird logins.json, FileZilla sitemanager.xml, WinSCP credentials, and CoreFTP configurations.
Configurable recursive file scraper scanning Desktop, Documents, and Downloads for sensitive file extensions (.kdbx, .key, .wallet, .seed, .txt, .pdf).
In-memory clipper module swapping copied cryptocurrency wallet strings in the clipboard with operator addresses.
Extracts Discord authentication tokens, Telegram desktop session files (tdata), Steam credentials, and VPN client configuration profiles.
05 | Wire Protocol & C2 Communication Framing
Rhadamanthys employs a proprietary network protocol disguised as TLS or transmitted over raw TCP sockets. The session initiates with a cryptographic handshake: 1) Key Agreement: Uses Curve25519 Elliptic-Curve Diffie-Hellman (ECDH) to establish a shared ephemeral secret key. 2) Session Key Derivation: Derives symmetric encryption keys using HKDF-SHA256. 3) Data Framing: Packets are compressed via LZ4 or Zstandard before encryption with ChaCha20-Poly1305 authenticated encryption. Packet Header Structure: [4 Bytes Custom Protocol Magic] [16 Bytes Session Identifier] [4 Bytes Payload Length] [12 Bytes Nonce / IV] [Encrypted Payload Data] [16 Bytes Poly1305 Authentication Tag]. Network exfiltration is performed in micro-chunks to evade perimeter DLP thresholds and network inspection engines.
06 | Verified Detection Signatures (YARA & Sigma)
rule Mal_Win_Rhadamanthys_Core_VM {
    meta:
        description = "Detects Rhadamanthys stealer bytecode VM interpreter and VFS container parser"
        author = "CyberTrace CTI Swarm"
        date = "2026-10-29"
        hash = "5c77ef12e58a221f70d65b10d7a64e10c5ee91932ca4d88e7275fb6ad4862ae1"
        threat_id = "TF-010"
    strings:
        $vm_dispatcher = { 8B 45 ?? 8B 0C 85 [4] FF E1 } // Opcode switch-table jump
        $chacha_const = { 65 78 70 61 6E 64 20 33 32 2D 62 79 74 65 20 6B } // "expand 32-byte k"
        $wallet1 = "nkbihfbeogaeaoehlefnkodbefgpgknn" ascii // MetaMask extension ID
        $wallet2 = "bfnaelmomeimhlpmgjnjophhpkkoljpa" ascii // Phantom extension ID
        $vfs_header = { 56 46 53 00 } // VFS magic signature
    condition:
        uint16(0) == 0x5A4D and
        ( ($chacha_const and 1 of ($wallet*)) or ($vm_dispatcher and $chacha_const) or ($vfs_header and 1 of ($wallet*)) )
}title: Rhadamanthys Unbacked Memory Allocation and Direct Syscall Evasion
id: d4918a30-f345-4c22-8667-55e97a02e010
status: production
description: Detects unbacked executable memory allocation in rundll32.exe or WerFault.exe followed by mass querying of browser and cryptocurrency extension directories.
references:
- https://cybertrace.io/threats/rhadamanthys-whitepaper.html
author: CyberTrace CTI Swarm
date: 2026-10-29
logsource:
category: process_access
product: windows
detection:
selection_target:
TargetImage|endswith:
- '\rundll32.exe'
- '\WerFault.exe'
selection_call_trace:
CallTrace|contains:
- 'UNKNOWN'
selection_access:
GrantedAccess: '0x1F0FFF'
condition: selection_target and selection_call_trace and selection_access
falsepositives:
- Legitimate software crash handling via WerFault (rare with unbacked memory call traces)
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
5c77ef12e58a221f70d65b10d7a64e10c5ee91932ca4d88e7275fb6ad4862ae1
f8448cc40e5318db49b5c2d338fbf5bc4727142b78119ce06259f63f59db5a3e
a12b53f65cd600b3438676a6ceb52f50567dc8ef58c73c8808dcfa7ae293b679
194.36.191[.]82:443
45.15.156[.]144:8080
rhadamanthys-gate[.]cc:443
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\Rhadamanthys
HKCU\Software\AppDataLow\Software\Rhadamanthys
%LOCALAPPDATA%\Temp\nsi_stager.exe
%LOCALAPPDATA%\Google\Chrome\User Data\Default\Login Data
%APPDATA%\Exodus\exodus.wallet
Rhadamanthys_Global_VM_Mutex
Rhad_VFS_Session_Lock
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
Web-based management console tracking active victim infections, geolocations, and extracted credential counts.
Disassembly showing custom bytecode VM interpreter designed to thwart static analysis and heuristic emulators.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Custom TLS-like Protocol, Hidden TCP Handshake command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Rhadamanthys Stealer (InfoStealer)
Sophisticated C++ infostealer utilizing a custom register-based virtual machine, encrypted virtual file system (VFS), direct syscall unhooking, and Curve25519/ChaCha20 network encryption.
C2 Architecture: Rhadamanthys employs a proprietary network protocol disguised as TLS or transmitted over raw TCP sockets. The session initiates with a cryptographic handshake: 1) Key Agreement: Uses Curve25519 Elliptic-Curve Diffie-Hellman (ECDH) to establish a shar
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Rhadamanthys Stealer (InfoStealer)
Детальный технический анализ Rhadamanthys Stealer — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Microsoft Visual C++ (MSVC Modern C++17/20 Native PE). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Custom TLS-like Handshake with Curve25519 ECDH, ChaCha20 Authenticated Encryption & LZ4 Compression) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Custom TLS-like Handshake with Curve25519 ECDH, ChaCha20 Authenticated Encryption & LZ4 Compression, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Rhadamanthys Stealer (InfoStealer) विश्लेषण
Rhadamanthys Stealer एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Microsoft Visual C++ (MSVC Modern C++17/20 Native PE) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Custom TLS-like Handshake with Curve25519 ECDH, ChaCha20 Authenticated Encryption & LZ4 Compression) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Custom TLS-like Handshake with Curve25519 ECDH, ChaCha20 Authenticated Encryption & LZ4 Compression आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).