01 | Tool Specifications & Architectural Profile
{
  "compiler": "MSVC v14.29 (Visual Studio 2019/2022)",
  "runtime": "Statically linked C/C++ runtime (MSVCRT-independent)",
  "binary_footprint": "Single PE32 executable, typ. 220 KB - 480 KB",
  "stub_size": "310,272 bytes (standard unpacked binary)",
  "packer_obfuscation": "Delivered via PrivateLoader, SmokeLoader, or packed with custom polymorphic stagers",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "WinMain -> Decrypt Configuration Block -> Parse C2 IP:Port List -> Anti-Analysis & VM Probes -> Establish Raw TCP Socket Connection -> Receive Stealing Instructions & Grabber Rules -> Enumerate & Decrypt Browser Vaults (DPAPI/AES-GCM) -> Harvest Crypto Wallets & 2FA Extensions -> Collect VPN & Messaging Tokens -> Compress Archive via In-Memory ZIP -> Stream Binary TCP Packets to C2 -> Execute Self-Termination",
  "technical_summary": "RisePro is a native C++ information stealer architecturally related to the Vidar malware family. Widely disseminated through Pay-Per-Install (PPI) distribution syndicates such as PrivateLoader, RisePro communicates with its C2 infrastructure over direct raw TCP sockets (typically ports 50500 or 50501) using custom binary packet framing rather than standard HTTP. Its execution logic decrypts an embedded configuration structure, performs environmental checks, connects to the C2 to retrieve dynamic file-grabbing regex rules, extracts credentials from browsers, VPN clients, cryptocurrency wallets, and 2FA extensions, and streams the exfiltrated archive directly over the raw TCP socket."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Web Administration Dashboard & Telegram Notification Bot",
  "builder_tabs_options": [
    {
      "tab": "C2 Infrastructure",
      "options": [
        "TCP Listener Ports: Multi-port binding (50500, 50501, 55000)",
        "Failover IPs: Array of secondary listener IP addresses",
        "HTTP Fallback Gate: Optional secondary HTTP endpoint URL"
      ]
    },
    {
      "tab": "Grabber Pattern Engine",
      "options": [
        "Regex Rule Builder: Path and filename patterns for targeted documents",
        "Extension List: .txt, .doc, .docx, .kdbx, .dat, .pdf",
        "File Size Threshold: Maximum byte limit per grabbed artifact (default: 10 MB)"
      ]
    },
    {
      "tab": "Affiliate Management",
      "options": [
        "Campaign Marker: Alphanumeric tracking tag (e.g., 'priv_01', 'sub_build')",
        "Telegram Bot Webhook: Instant notification of newly received credentials",
        "Crypto Wallet Alerting: High-priority trigger when MetaMask or seed phrases are matched"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x000",
      "field": "C2_Addresses",
      "type": "CHAR[256]",
      "description": "Semicolon-delimited list of C2 IP:Port endpoints"
    },
    {
      "offset": "0x100",
      "field": "BuildTag",
      "type": "CHAR[64]",
      "description": "Operator affiliate campaign marker"
    },
    {
      "offset": "0x140",
      "field": "RC4_Key",
      "type": "BYTE[32]",
      "description": "Symmetric stream cipher encryption key"
    },
    {
      "offset": "0x160",
      "field": "GrabberRulesCount",
      "type": "DWORD",
      "description": "Number of active file grabber regex patterns"
    },
    {
      "offset": "0x164",
      "field": "Flags",
      "type": "DWORD",
      "description": "Bitmask for targeted subsystems (Passwords, Cookies, Wallets, VPN, Discord)"
    }
  ],
  "payload_generation_flags": [
    "Dynamic API resolution via custom CRC32 hashes",
    "In-line string decryption using rolling XOR stubs",
    "Stack-based buffer allocation for sensitive decrypted variables"
  ],
  "operator_commands": [
    "CMD_GET_CONFIG (0x01): Retrieve active grabbing configuration",
    "CMD_GET_RULES (0x02): Fetch dynamic regex grabber rules",
    "CMD_SEND_LOG (0x03): Stream chunked exfiltration packets",
    "CMD_PING (0x04): Heartbeat packet",
    "CMD_KILL (0x05): Terminate client process and execute cleanup"
  ],
  "interface_telemetry_analysis": "The operator interface incorporates real-time TCP socket handling servers paired with automated Telegram bot dispatchers that immediately notify operators of compromised credentials and cold storage recovery keys."
}struct RisePro_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Execution initiated by parent loader (e.g., PrivateLoader) via CreateProcessW or process injection into clean target processes using VirtualAllocEx and WriteProcessMemory.",
  "ntapi_functions": [
    "ws2_32!WSAStartup",
    "ws2_32!socket",
    "ws2_32!connect",
    "ws2_32!send",
    "ws2_32!recv",
    "crypt32!CryptUnprotectData",
    "bcrypt!BCryptOpenAlgorithmProvider",
    "bcrypt!BCryptDecrypt",
    "kernel32!VirtualAlloc"
  ],
  "process_hollowing_target": "Direct execution; when delivered packed, injected into explorer.exe or svchost.exe",
  "persistence_mechanics": [
    "No persistence routines (ephemeral execution profile)",
    "Self-terminating execution pattern designed to minimize forensic footprint",
    "Self-deletion command: cmd.exe /c choice /C Y /N /D Y /T 3 & Del \"%s\""
  ],
  "evasion_hooks": [
    "Dynamic API Resolution: Loads system libraries via LoadLibraryA and resolves function addresses via GetProcAddress",
    "NTDLL Hook Detection: Validates leading bytes of resolved NTAPI functions against expected opcode patterns (e.g., mov r10, rcx; mov eax, ...); detects presence of user-mode EDR inspection hooks"
  ],
  "anti_analysis": [
    "Hypervisor Detection: Executes CPUID instruction with EAX=1; checks ECX bit 31 (hypervisor present bit)",
    "MAC Address Validation: Checks local network adapter MAC prefixes against known VMware, VirtualBox, and QEMU OUI ranges",
    "Process Blacklisting: Traverses running processes via CreateToolhelp32Snapshot; terminates if wireshark.exe, fiddler.exe, procmon.exe, x64dbg.exe, or ida.exe are detected"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the RisePro binary:
[ "Chromium Browsers: Extracts Login Data, Cookies, Web Data, History from Chrome, Edge, Brave, Opera, Vivaldi", "Master Key Decryption: Resolves DPAPI master key from Local State via CryptUnprotectData; decrypts stored passwords using AES-256-GCM", "Gecko Browsers: Extracts passwords and cookies from Mozilla Firefox and Thunderbird profiles using nss3.dll exports", "VPN Client Credentials: Scrapes authentication profiles and tokens for NordVPN, OpenVPN, ProtonVPN, and Windscribe from %AppData% directories", "Messaging Apps: Extracts Discord authentication tokens and Telegram session state (tdata directory)" ]
[ "Hardware reconnaissance: CPU model, GPU adapter description, installed RAM, active display resolution", "Desktop screenshot capture: GDI screen buffer capture via BitBlt saved as PNG/JPEG", "Software inventory: Enumerates installed applications from HKLM\\Software\\Microsoft\\Windows\\CurrentVersion\\Uninstall" ]
[ "No interactive remote access capabilities (dedicated stealer architecture)" ]
[ "Dynamic file grabber executes regex pattern queries targeting user desktop, documents, and downloads: (?i).*(wallet|pass|seed|key|secret|btc|eth|crypto).*\\.(txt|doc|docx|pdf|dat|kdbx)", "Respects configurable maximum file size thresholds to prevent buffer exhaustion" ]
[ "Scrapes 30+ cryptocurrency browser extension wallets via extension IDs: MetaMask (ejbalbakoplchlghecdalmeeeajnimhm), TronLink (ibnejdfjmmkpcnlpebklmnkoeoihofec), Phantom (bfnaelmomeimhlpmgjnjophhpkkoljpa), Binance Chain, Coinbase Wallet", "Collects desktop wallet data for Exodus, Electrum, Atomic Wallet, and Coinomi" ]
[ "Extracts Windows Product ID and MachineGuid to generate deterministic victim HWID" ]
05 | Wire Protocol & C2 Communication Framing
{
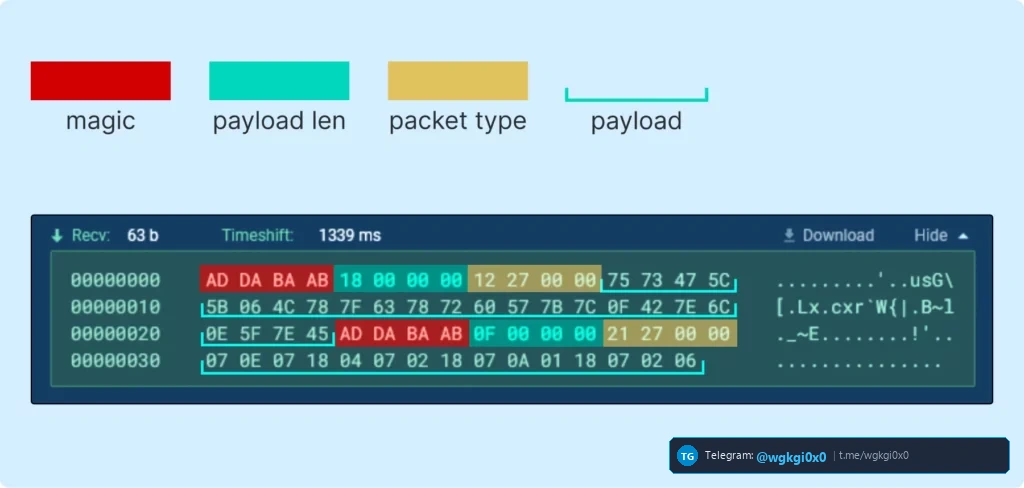
  "framing": "Custom 12-byte binary packet header: [4 bytes Magic (0x52495345 // 'RISE')][4 bytes Command ID][4 bytes Payload Length], followed by payload data",
  "serialization": "Raw binary stream containing serialized configuration structs or compressed ZIP data chunks",
  "handshake": "Client opens raw TCP connection to IP:50500 -> Sends CMD_HELLO (0x01) with HWID -> Server returns CMD_CONFIG (0x02) with dynamic regex rules -> Client executes harvesting -> Client streams CMD_LOG_DATA (0x03) chunks -> Server returns CMD_ACK (0x04) -> Socket closed",
  "cryptography": "Stream XOR or RC4 encryption using a 32-byte key derived from the embedded configuration and a dynamic session nonce",
  "packet_types": [
    {
      "header": "0x0001 (CMD_HELLO)",
      "payload": "HWID, BuildTag, OS_Version, RAM_Size",
      "direction": "Client -> Server"
    },
    {
      "header": "0x0002 (CMD_CONFIG)",
      "payload": "Flags (DWORD), Regex_Rules_Buffer",
      "direction": "Server -> Client"
    },
    {
      "header": "0x0003 (CMD_LOG_DATA)",
      "payload": "Offset (DWORD), Chunk_Size (DWORD), Encrypted_Data",
      "direction": "Client -> Server"
    },
    {
      "header": "0x0004 (CMD_ACK)",
      "payload": "Status: 0x00 (SUCCESS), Action: TERMINATE",
      "direction": "Server -> Client"
    }
  ],
  "traffic_signature": "Outbound TCP connections to non-standard high ports (50500, 50501, 55000) displaying initial 4-byte magic signature 0x52 0x49 0x53 0x45 followed by high-entropy encrypted payloads."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_RisePro_Stealer {
    meta:
        description = "Detects RisePro infostealer payloads based on binary packet signatures, config parsing, and DPAPI imports"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "RisePro"
        hash = "c871f3a29b4e5d6108e4521789c025114a78e932b1d6f5c8412e9b0147c23e85"
    strings:
        $magic = { 52 49 53 45 } // 'RISE'
        $s1 = "Chrome\\User Data" ascii wide
        $s2 = "Login Data" ascii wide
        $s3 = "encrypted_key" ascii
        $s4 = "Local State" ascii wide
        $s5 = "ejbalbakoplchlghecdalmeeeajnimhm" ascii // MetaMask
        $s6 = "ibnejdfjmmkpcnlpebklmnkoeoihofec" ascii // TronLink
        $s7 = "NordVPN" ascii wide
        $s8 = "ProtonVPN" ascii wide
        $tcp1 = "ws2_32.dll" ascii nocase
        $tcp2 = "connect" ascii
        $tcp3 = "send" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 1MB and
        ($magic or (4 of ($s*) and all of ($tcp*)))
}title: RisePro Non-Standard High-Port TCP Communication
id: d3a1f8c2-4b5e-4c7a-9f1e-8e6d2a4c0b9f
status: stable
description: Detects outbound network connections initiated by unusual processes to non-standard TCP ports typical of RisePro C2 servers (50500, 50501).
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S1096/
tags:
- attack.command_and_control
- attack.t1071
- attack.exfiltration
- attack.t1041
logsource:
category: network_connection
product: windows
detection:
selection_ports:
DestinationPort:
- 50500
- 50501
- 55000
selection_process:
Image|contains:
- '\AppData\Local\Temp\'
- '\AppData\Roaming\'
- '\Users\Public\'
condition: selection_ports and selection_process
falsepositives:
- Custom internal enterprise applications using high dynamic ports.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
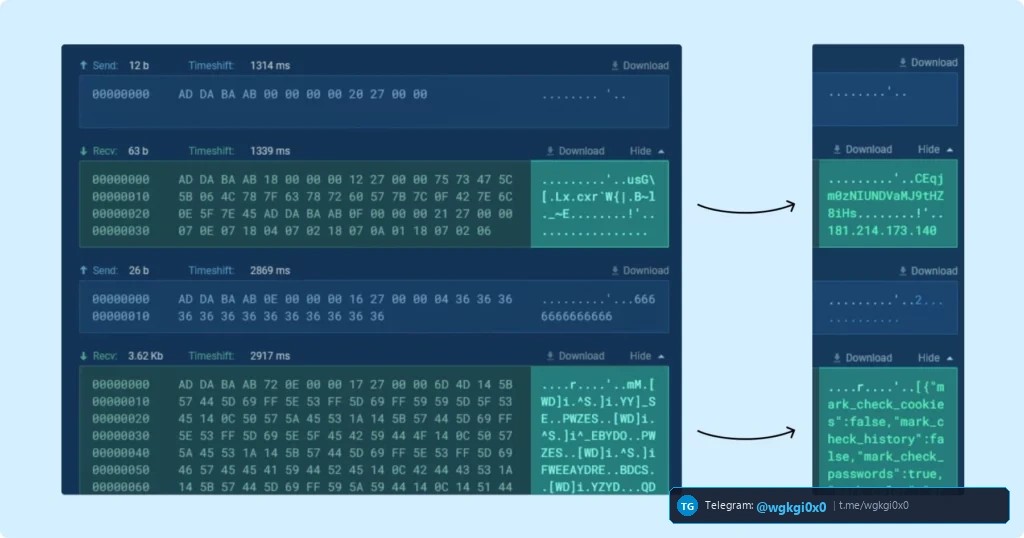
ANY.RUN forensic capture analyzing custom TCP protocol used by RisePro to transmit exfiltrated system data.
Memory analysis showing compilation of password logs, system information, and browser artifacts into C2 packets.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Encrypted TCP / Custom HTTP Webhook command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
RisePro (InfoStealer)
Native C++ commodity credential stealer communicating via raw binary TCP sockets and utilizing dynamic regex patterns to harvest browser, VPN, and crypto assets.
C2 Architecture: {'framing': "Custom 12-byte binary packet header: [4 bytes Magic (0x52495345 // 'RISE')][4 bytes Command ID][4 bytes Payload Length], followed by payload data", 'serialization': 'Raw binary stream containing serialized configuration structs or compre
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ RisePro (InfoStealer)
Детальный технический анализ RisePro — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Microsoft Visual C++ (MSVC 2019/2022) Native PE32 (x86). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Direct Raw Binary TCP Sockets (Ports 50500/50501/55000) with proprietary XOR/RC4 stream encryption; HTTP fallback) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Direct Raw Binary TCP Sockets (Ports 50500/50501/55000) with proprietary XOR/RC4 stream encryption; HTTP fallback, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
RisePro (InfoStealer) विश्लेषण
RisePro एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Microsoft Visual C++ (MSVC 2019/2022) Native PE32 (x86) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Direct Raw Binary TCP Sockets (Ports 50500/50501/55000) with proprietary XOR/RC4 stream encryption; HTTP fallback) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Direct Raw Binary TCP Sockets (Ports 50500/50501/55000) with proprietary XOR/RC4 stream encryption; HTTP fallback आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).