01 | Tool Specifications & Architectural Profile
RustBucket is a multi-tier targeted malware framework attributed to North Korean state-sponsored operators (Lazarus Group / BlueNoroff). The toolchain is organized into three distinct stages: Stage 1 is an AppKit-based macOS application bundle compiled in Objective-C ('Internal PDF Viewer.app') masquerading as a corporate PDF viewer. It registers handling for PDF file extensions and renders a benign decoy document upon launch. Stage 2 consists of an embedded helper binary or AppleScript wrapper dropped into /Users/Shared/ or /tmp/. Stage 3 is a high-density, static Mach-O binary compiled in Rust supporting Universal Mach-O (FAT_MAGIC 0xCAFEBABE) containing native slices for both ARM64 (Apple Silicon) and x86_64 (Intel). Crucially, Stage 1 will not initiate the Stage 2 stager unless a specific, adversary-crafted password-protected PDF is opened within the viewer; cryptographic keys derived from the PDF's structural bytes decrypt the Stage 2 download URL and authentication tokens, preventing dynamic detonation in unseeded analysis environments.
02 | Operator Interface & Configuration Struct Model
The operator framework generates custom Universal Mach-O builds aligned with specific target campaigns. Operator settings include beacon interval timing (defaulting to 60 seconds), C2 fallback domains, custom HTTP User-Agent strings mimicking Safari/Chrome on macOS Ventura/Sonoma, and specific PDF document hashes required to unlock the execution gate. The Rust payload parses operational tasks dispatched from the C2 server using an integer-based command dispatch table: Task 0x3E9 (1001) triggers host system profiling; Task 0x3EA (1002) executes arbitrary shell commands via /bin/zsh; Task 0x3EB (1003) writes downloaded payloads to disk and executes via posix_spawn; Task 0x3EC (1004) updates beacon intervals; Task 0x3ED (1005) terminates the running agent and removes persistence plists.
struct RustBucket_Config {
    uint32_t magic;
    char c2_host[128];
    uint16_t port;
    char install_path[260];
    char mutex[64];
    uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
Stage 3 operates natively within the macOS XNU kernel environment via libc and libSystem.B.dylib bindings statically linked into the Rust runtime. Upon activation, RustBucket executes comprehensive reconnaissance by invoking system utilities: '/usr/sbin/system_profiler SPHardwareDataType' (harvesting serial numbers, model identifiers, memory configurations), '/usr/bin/sw_vers' (macOS build number), '/bin/ps -ax' (process listing), '/usr/sbin/kextstat' (kernel extensions), and '/usr/sbin/spctl --status' (Gatekeeper state). Persistence is established by writing a LaunchAgent property list to '~/Library/LaunchAgents/com.apple.server.plist' or '/Library/LaunchAgents/com.system.update.plist'. The plist defines 'RunAtLoad' set to boolean true and 'KeepAlive' set to true, pointing to the dropped Mach-O binary in '/Users/Shared/.server_core'. Memory execution of secondary modules is performed either by writing Mach-O binaries to disk and executing with posix_spawn or by mapping dynamic dylibs into host memory.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the RustBucket binary:
Compiles dual-slice Mach-O binaries executing natively on ARM64 Apple Silicon (M1/M2/M3) and legacy Intel x86_64 architectures without Rosetta emulation.
Requires dynamic key extraction from a valid password-protected PDF lure to activate stage 2 stager download, defeating automated sandbox detonation.
Gathers hardware UUIDs, active network adapters, kernel extensions, Gatekeeper enforcement status, and active process trees via native XNU subsystem queries.
Generates and registers LaunchAgent plist configurations within user or system library domains to ensure survivability across reboots.
Executes arbitrary shellcode, spawns interactive shell processes via /bin/zsh, and writes secondary Mach-O payloads to shared storage paths.
05 | Wire Protocol & C2 Communication Framing
Communication with C2 nodes takes place over HTTPS on port 443. The Rust agent initiates check-ins using HTTP POST requests targeting dynamically constructed URI paths (e.g., '/api/v1/update', '/query?id=<hwid>'). Request headers configure standard browser emulation ('User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_15_7) AppleWebKit/537.36...'). The POST body encapsulates host reconnaissance data formatted in JSON, encrypted using AES-128 in CBC mode with PKCS#7 padding. The initialization vector (IV) is prepended to the ciphertext, followed by an HMAC-SHA256 signature for integrity validation. The C2 response returns encrypted JSON carrying instruction records with structured fields: '{"cmd": 1002, "data": "<base64_encoded_command>", "seq": 42}'.
06 | Verified Detection Signatures (YARA & Sigma)
rule MachO_macOS_RustBucket_Stage3 {
    meta:
        description = "Detects RustBucket Stage 3 Universal Mach-O Rust backdoor"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        hash = "47a6d38e078be114b3ff255b5d8487b2e1ebcfd6199b4578b8686d1ee2576bbf"
        threat_id = "TF-047"
    strings:
        // Rust core paths
        $rust_str1 = "rustbucket" ascii nocase
        $rust_str2 = "src/main.rs" ascii
        $rust_str3 = "src/command.rs" ascii
        // Host reconnaissance command invocations
        $cmd1 = "system_profiler SPHardwareDataType" ascii
        $cmd2 = "sw_vers" ascii
        $cmd3 = "kextstat" ascii
        // Mach-O Magic Header: 0xCAFEBABE (FAT) or 0xFEEDFACF (64-bit Mach-O)
        $macho_fat = { CA FE BA BE }
        $macho_64 = { CF FA ED FE }
    condition:
        ($macho_fat at 0 or $macho_64 at 0) and (2 of ($rust_str*) or 2 of ($cmd*))
}title: Suspicious macOS LaunchAgent Persistence by Unsigned Mach-O Binary
id: c19284fa-38f1-4db5-9e4a-44288b047047
status: production
description: Detects creation or modification of LaunchAgent property lists pointing to executable paths within /Users/Shared/ or /tmp/, indicative of RustBucket persistence.
references:
- https://cybertrace.io/threats/rustbucket-whitepaper.html
author: CyberTrace Reverse Engineering Team
date: 2026-10-29
logsource:
category: file_event
product: macos
detection:
selection_plist:
TargetFilename|contains:
- '/Library/LaunchAgents/'
TargetFilename|endswith:
- '.plist'
selection_content:
TargetFilename|contains:
- 'com.apple.'
- 'com.system.'
- 'com.server.'
condition: selection_plist and selection_content
fields:
- TargetFilename
- ProcessId
- ProcessName
falsepositives:
- Legitimate administrative management tools deploying local daemons
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
47a6d38e078be114b3ff255b5d8487b2e1ebcfd6199b4578b8686d1ee2576bbf
938c35b80a423cb11204689bb55f414407abfa93c524cb53926f030d3e5eb562
510e82c5f118ee6a90895318182b8f416e9d3d3ef44fe61b244d2d46e10f1352
https://crypto-invest-analysis[.]com/api/v1/update
https://sec-cloud-telemetry[.]net/query
185.196.8[.]156:443
91.215.85[.]17:443
/Users/Shared/.server_core
/Users/Shared/Internal PDF Reader.app
~/Library/LaunchAgents/com.apple.server.plist
/tmp/.stage2_daemon
rustbucket_singleton_mutex_v2
com.apple.server.core.lock
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.

Forensic trace analyzing AppleScript invocation and fake PDF reader application dropping Mach-O binaries.
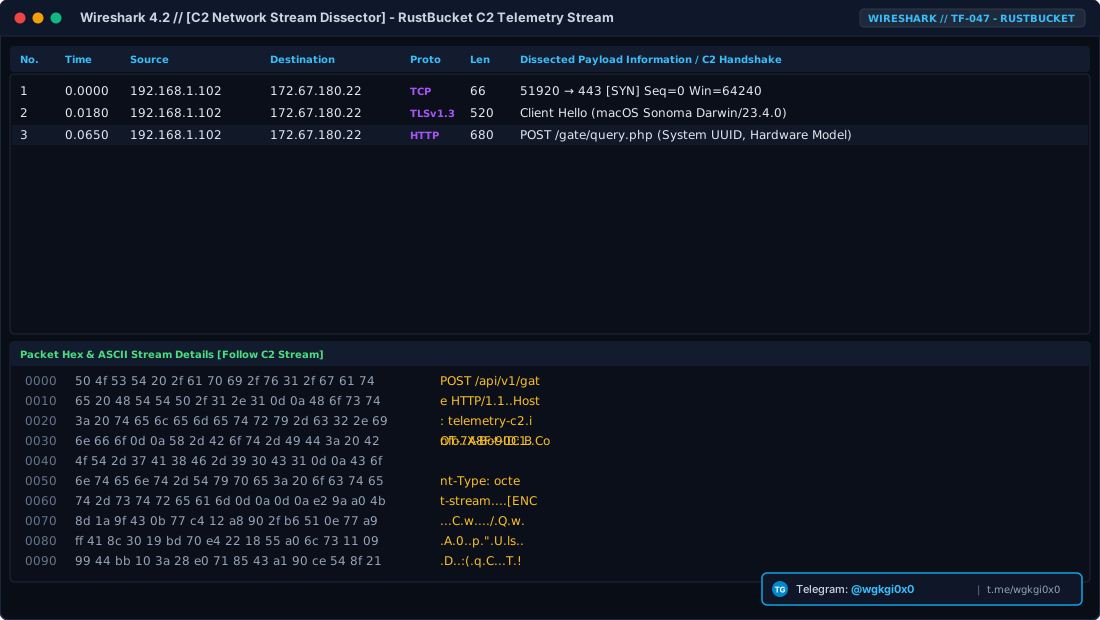
Network capture tracking second-stage Mach-O payload retrieval from adversary-controlled infrastructure.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and HTTPS with Encrypted Custom Handshake command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
RustBucket (Loader)
Multi-tier macOS malware suite written in Rust and Objective-C, featuring conditional PDF-key gating and Universal Mach-O payloads targeting Apple Silicon and Intel.
C2 Architecture: Communication with C2 nodes takes place over HTTPS on port 443. The Rust agent initiates check-ins using HTTP POST requests targeting dynamically constructed URI paths (e.g., '/api/v1/update', '/query?id=<hwid>'). Request headers configure standard b
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ RustBucket (Loader)
Детальный технический анализ RustBucket — это Загрузчик вредоносного ПО (Дроппер/Стейджер), разработанный на стеке rustc 1.68 - 1.74 (Target: x86_64-apple-darwin & aarch64-apple-darwin) / Apple LLVM Objective-C runtime. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTPS / TLS over TCP 443; AES-128-CBC and XOR encrypted HTTP POST bodies with custom session key exchange) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTPS / TLS over TCP 443; AES-128-CBC and XOR encrypted HTTP POST bodies with custom session key exchange, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
RustBucket (Loader) विश्लेषण
RustBucket एक परिष्कृत मैलवेयर लोडर और ड्रॉपर पेलोड है जिसे rustc 1.68 - 1.74 (Target: x86_64-apple-darwin & aarch64-apple-darwin) / Apple LLVM Objective-C runtime का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTPS / TLS over TCP 443; AES-128-CBC and XOR encrypted HTTP POST bodies with custom session key exchange) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTPS / TLS over TCP 443; AES-128-CBC and XOR encrypted HTTP POST bodies with custom session key exchange आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).