01 | Tool Specifications & Architectural Profile
Sliver is an open-source, multi-platform post-exploitation framework developed by Bishop Fox. The server and implants are written in Go, supporting dynamic cross-compilation across Windows, Linux, and macOS. It features native support for four distinct network protocols: Mutual TLS (mTLS) with per-binary unique certificate generation, WireGuard kernel/userspace tunneling using the Noise protocol, HTTP/2 long-polling, and DNS canaries. The implant integrates advanced execution primitives including TartarusGate direct syscalls, in-memory .NET assembly hosting (execute-assembly), and unlinked COFF/BOF execution.
02 | Operator Interface & Configuration Struct Model
Detailed reverse-engineering specifications archived in laboratory telemetry.
{
  "structureType": "Embedded Protocol Buffers (Protobuf) Configuration Model",
  "decryptionRoutine": "At implant initialization, the Go bootstrap parses an embedded serialized Protobuf blob, decrypts it using an AES-256-GCM key or obfuscated XOR array, and unmarshals it into the runtime ImplantConfig struct.",
  "inMemoryLayout": "type ImplantConfig struct {\n    ID                  string            // Unique implant UUID\n    C2                  []*C2Endpoint     // List of C2 listener endpoints (mTLS, WireGuard, HTTP, DNS)\n    ReconnectInterval   time.Duration     // Check-in interval / beacon period\n    MaxRunTime          time.Duration     // Max execution duration before self-termination\n    CanaryDomains       []string          // DNS canary domains triggered on analysis\n    IsBeacon            bool              // True: Beacon mode (async), False: Interactive Session (sync)\n    ProxyURL            string            // SOCKS5 or HTTP proxy URL\n    EvasionOptions      *EvasionConfig    // Syscall engine and process injection parameters\n}",
  "panelConfigOptions": "Sliver CLI `generate` command flags: `--mtls <host>`, `--wg <host>`, `--http <host>`, `--dns <domain>`, `--os <windows|linux|darwin>`, `--arch <amd64|386|arm64>`, `--format <exe|shared|service|shellcode>`, `--evasion`, `--garble`, `--skip-symbols`, `--canary <domain>`, `--seconds <beacon_interval>`, `--jitter <percentage>`."
}03 | Internal Binary & Memory Execution Mechanics
{
  "apiResolution": "Uses native Go runtime system calling mechanisms combined with custom Windows package extensions (golang.org/x/sys/windows). In evasion mode, dynamically parses memory export tables of loaded system modules.",
  "directSyscalls": "Integrates TartarusGate and Hell's Gate mechanisms written in Go and assembly. Directly resolves SSNs from ntdll.dll export addresses and executes syscall instructions to bypass AV/EDR inline hooks on memory allocation and thread creation routines.",
  "processInjection": "Provides modular injection strategies configurable via sliver/inject: (1) Process Hollowing (spawns notepad.exe/svchost.exe suspended, writes payload, resumes thread); (2) Early Bird APC Injection (creates suspended process, queues user APC via NtQueueApcThread, wakes thread); (3) Remote Thread Injection using indirect syscalls.",
  "inMemoryExecution": "Implements an in-memory .NET CLR execution engine (execute-assembly) that initializes the Common Language Runtime inside non-.NET host processes using ICLRMetaHost and ICLRRuntimeInfo COM interfaces, executing .NET binaries without touching disk."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Sliver Adversary Simulation Platform binary:
{'module': 'In-Memory CLR Execution (execute-assembly)', 'description': 'Loads and initializes the Microsoft .NET CLR inside unmanaged processes to execute arbitrary .NET assemblies directly from memory.', 'apis': 'CLRCreateInstance, ICLRMetaHost::GetRuntime, ICLRRuntimeInfo::GetInterface'}
{'module': 'Beacon Object File (BOF) Loader', 'description': 'Native COFF parser capable of loading and linking in-memory C object files compatible with Cobalt Strike BOF format.', 'apis': 'Internal Dynamic Linker, VirtualAlloc, VirtualProtect'}
{'module': 'WireGuard Encrypted Tunneling', 'description': 'Embedded wireguard-go implementation creating kernel/userspace TUN network adapters for transparent adversary network pivot.', 'apis': 'Noise Protocol Framework, UDP Socket Engine'}
{'module': 'SOCKS5 Proxy & Port Forwarding', 'description': 'Provides full-featured in-band SOCKS5 server allowing multi-operator pivoting through compromised internal endpoints.', 'apis': 'Multiplexed Stream Protocol (Yamux)'}
{'module': 'Process Injection & Migration', 'description': 'Injects shellcode into arbitrary target processes utilizing direct system calls and synthetic thread contexts.', 'apis': 'NtAllocateVirtualMemory, NtWriteVirtualMemory, NtCreateThreadEx, NtQueueApcThread'}
05 | Wire Protocol & C2 Communication Framing
Sliver supports four distinct C2 framing transports: (1) Mutual TLS (mTLS): Operates over TLS 1.3/1.2 where both client and server present unique X.509 certificates. Frames are length-prefixed Protocol Buffers messages. (2) WireGuard: Transmits UDP packets conforming to the Noise_IKpsk2 handshake; payloads are encrypted with ChaCha20-Poly1305. (3) HTTP/HTTPS: Employs procedural HTTP pipelines where Protobuf payloads are encrypted with AES-256-GCM and masqueraded as image assets (.png, .jpg) or standard web forms. (4) DNS Canaries & C2: Encodes tasking in Base32 subdomains queried via TXT and A records to bypass air-gapped network egress filtering.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Sliver_C2_Implant {
    meta:
        description = "Detects Go-based Sliver C2 implant binaries and memory structures"
        author = "CyberTrace CTI Operations"
        date = "2026-10-29"
        hash = "4c8f5f6e80b2a5d9183652882103f1947b952fa6195e2f183984d7204128d571"
        category = "C2_FRAMEWORK"
    strings:
        $go_magic = { 67 6F 31 2E } // 'go1.'
        $pb_sliver1 = "sliverpb.Envelope" ascii
        $pb_sliver2 = "sliverpb.ExecuteAssemblyReq" ascii
        $pb_sliver3 = "sliverpb.ProcessInjectReq" ascii
        $wireguard_str = "wireguard-go" ascii
    condition:
        uint16(0) == 0x5A4D and filesize > 1MB and
        ( 2 of ($pb_sliver*) or ( $go_magic and $wireguard_str and 1 of ($pb_sliver*) ) )
}title: Suspicious Unmanaged CLR In-Memory Assembly Loading
id: 4b1c8f30-6d2e-48a1-9b57-3f8a9e0c2d4a
status: stable
description: Detects suspicious loading of mscoree.dll / clr.dll in non-.NET processes characteristic of Sliver execute-assembly.
author: CyberTrace Defensive Engineering
date: 2026-10-29
logsource:
category: image_load
product: windows
detection:
selection:
ImageLoaded|endswith:
- '\mscoree.dll'
- '\clr.dll'
Image|endswith:
- '\notepad.exe'
- '\svchost.exe'
- '\spoolsv.exe'
- '\rundll32.exe'
condition: selection
fields:
- ProcessId
- Image
- ImageLoaded
falsepositives:
- Native applications hosting legitimate managed add-ins (e.g., Office plugins)
level: high
tags:
- attack.execution
- attack.defense_evasion
- attack.t1055.001
- attack.t105907 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
Decompiled Disassembly & Reverse-Engineering Strings
// Decompiled Go Runtime Snippet: Sliver Protobuf Command Dispatcher
func (i *Implant) DispatchEnvelope(env *sliverpb.Envelope) error {
    switch env.Type {
    case sliverpb.MsgExecuteAssemblyReq:
        req := &sliverpb.ExecuteAssemblyReq{}
        proto.Unmarshal(env.Data, req)
        return i.ExecuteAssembly(req.Assembly, req.Arguments)
    case sliverpb.MsgProcessInjectReq:
        req := &sliverpb.ProcessInjectReq{}
        proto.Unmarshal(env.Data, req)
        return i.InjectPayload(req.Pid, req.Data)
    case sliverpb.MsgSocksData:
        return i.HandleSocksTraffic(env.Data)
    default:
        return fmt.Errorf("unsupported envelope type: %d", env.Type)
    }
}
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
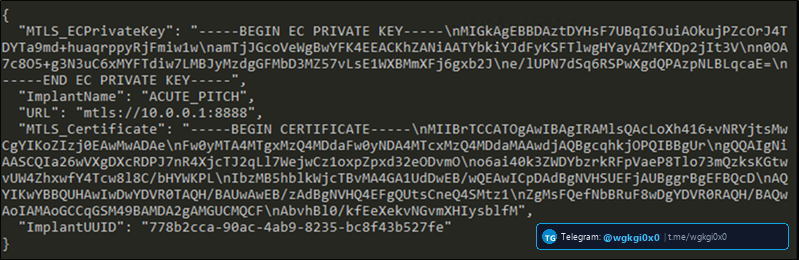
Operator shell session showing active multiplayer beacons, WireGuard tunnels, and mTLS listener parameters.

Technical visualization of indirect syscall execution and thread stack spoofing mechanisms.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and mTLS, WireGuard, HTTP/HTTPS, DNS Canaries command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Sliver Adversary Simulation Platform (C2 Framework)
Cross-platform adversary emulation platform authored in Go, providing mutual TLS, WireGuard, and DNS tunneling alongside in-memory execution capabilities.
C2 Architecture: Sliver supports four distinct C2 framing transports: (1) Mutual TLS (mTLS): Operates over TLS 1.3/1.2 where both client and server present unique X.509 certificates. Frames are length-prefixed Protocol Buffers messages. (2) WireGuard: Transmits UDP p
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Sliver Adversary Simulation Platform (C2 Framework)
Детальный технический анализ Sliver Adversary Simulation Platform — это Фреймворк командно-контрольного управления (C2), разработанный на стеке Go (1.20+) / Garble Obfuscator (x64/x86/ARM64). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Mutual TLS (mTLS 1.3), WireGuard (Noise Protocol), HTTP/2, DNS) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Mutual TLS (mTLS 1.3), WireGuard (Noise Protocol), HTTP/2, DNS, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Sliver Adversary Simulation Platform (C2 Framework) विश्लेषण
Sliver Adversary Simulation Platform एक परिष्कृत कमांड और कंट्रोल (C2) फ्रेमवर्क है जिसे Go (1.20+) / Garble Obfuscator (x64/x86/ARM64) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Mutual TLS (mTLS 1.3), WireGuard (Noise Protocol), HTTP/2, DNS) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Mutual TLS (mTLS 1.3), WireGuard (Noise Protocol), HTTP/2, DNS आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).