01 | Tool Specifications & Architectural Profile
{
  "compiler": "Java SE Runtime executing apktool.jar (build) + signapk.jar (X.509 testkey signing) driven by .NET WinForms Builder",
  "runtime": "Android Runtime (ART) / Dalvik VM",
  "binary_footprint": "Standalone or merged APK package, typ. 400 KB - 2.5 MB uncompressed DEX and resource bundle",
  "stub_size": "680,000 bytes (base template APK situated in Server\\Resources\\stub.apk)",
  "packer_obfuscation": "Random ASCII/alphanumeric Smali identifier substitution, manifest permission inflation, and optional DEX asset encryption in CypherRAT/SpyMax forks",
  "subsystem": "Android Background Service + DeviceAdminReceiver + AccessibilityService",
  "entry_point_flow": "MainActivity -> Request DeviceAdmin / AccessibilityService privileges -> Hide launcher icon via PackageManager.setComponentEnabledSetting -> Start foreground CameraManager/ConnectionService -> Register SensorRestarterBroadcastReceiver -> Connect TCP socket to C2",
  "technical_summary": "SpyNote (and its direct source derivatives SpyMax v2/v4 and CypherRAT v3.5) is the foundational Android RAT architecture upon which modern commercial families were built. Following the public leak of its v5.0/v6.4 builder and stub source code, it became ubiquitous across mobile threat operations. The framework pairs a VB.NET/C# Windows server with a Java Android stub that leverages AccessibilityService auto-clicking, DeviceAdminReceiver deletion prevention, MediaProjection screen streaming, and SensorRestarterBroadcastReceiver service resurrection."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "GUI Builder / Operator Console",
  "builder_tabs_options": [
    {
      "tab": "Build / App Settings",
      "options": [
        "Service Name: Foreground service label displayed in Android system settings",
        "App Name: Application title patched into strings.xml",
        "Version: Version string metadata",
        "App Icon: Custom icon image injected into drawable/mipmap folders",
        "Merge With APK: Binds SpyNote Smali classes and manifest receivers into a legitimate host APK"
      ]
    },
    {
      "tab": "Connection Settings",
      "options": [
        "DNS / IP Host: Target C2 IPv4 address or Dynamic DNS domain",
        "Port: Listening TCP port (default 2222, 3210, or 7771/7772 in SpyMax)",
        "Client Name / Victim ID: Tag string identifying the deployment batch",
        "Key / Password: Socket authentication secret shared between server and stub"
      ]
    },
    {
      "tab": "Installation & Persistence",
      "options": [
        "Hide Application Icon: Disables MainActivity launcher alias upon first execution",
        "Device Administrator: Prompts victim to activate BIND_DEVICE_ADMIN to block standard uninstallation",
        "Accessibility Service: Enables automated permission clicking and keystroke logging",
        "Foreground Service Notification: Configures persistent notification or silent channel hiding"
      ]
    },
    {
      "tab": "Ports & Network",
      "options": [
        "Listener Ports Array: Configures single or dual TCP listener sockets on the Windows host",
        "Connection Password: Drops unauthorized TCP peers that fail initial key validation"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "res/values/strings.xml -> h",
      "field": "Host",
      "type": "String",
      "description": "C2 Server IP address or DNS hostname patched during APK build"
    },
    {
      "offset": "res/values/strings.xml -> p",
      "field": "Port",
      "type": "String",
      "description": "C2 TCP listener port number"
    },
    {
      "offset": "res/values/strings.xml -> n",
      "field": "ClientName",
      "type": "String",
      "description": "Operator-defined victim identifier string"
    },
    {
      "offset": "res/values/strings.xml -> s",
      "field": "ServiceName",
      "type": "String",
      "description": "Background Android service display name"
    },
    {
      "offset": "CameraManager / Config.SPL",
      "field": "Splitter",
      "type": "String",
      "description": "Packet delimiter token separating fields and binary chunks"
    }
  ],
  "payload_generation_flags": [
    "Toolchain: java -jar apktool.jar b -f -o built.apk",
    "Signing: java -jar signapk.jar certificate.pem key.pk8 built.apk out.apk",
    "ZipAlign: zipalign -v 4 out.apk final.apk"
  ],
  "operator_commands": [
    "FileManager: Browses internal/external storage, downloads files, edits text, and uploads payloads",
    "SMSManager: Dumps content://sms/inbox and content://sms/sent, and sends SMS via SmsManager.sendTextMessage",
    "CallManager: Reads CallLog.Calls content provider and initiates or terminates phone calls",
    "ContactsManager: Exfiltrates address book entries from ContactsContract.CommonDataKinds.Phone",
    "Microphone: Captures live ambient audio via AudioRecord at configurable sample rates (8000Hz - 44100Hz)",
    "CameraManager: Captures still photographs or live video streams from front/back cameras",
    "Keylogger: Streams real-time Accessibility text events and pulls saved offline log files",
    "LocationManager: Streams live GPS coordinates and renders victim position on an integrated map view"
  ],
  "interface_telemetry_analysis": "The SpyNote v6.4 and SpyMax v4.0 operator interfaces present a Windows Forms DataGridView listing active mobile sessions. Columns report the client IP, country flag, victim identifier, device manufacturer/model, Android OS version, root status, battery level, and active screen state. Right-clicking any row opens a hierarchical context menu organized into Account Manager, File Manager, SMS Manager, Call Manager, Contacts, Camera, Microphone, Keylogger, Terminal Shell, and Fun/System actions."
}struct SpyNote_(SpyMax_/_CypherRAT_Lineage)_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "APK Execution -> MainActivity launches AccessibilityService and DeviceAdmin activation intents -> AccessibilityService auto-approves runtime permissions (READ_SMS, RECORD_AUDIO, CAMERA, ACCESS_FINE_LOCATION) and DeviceAdmin prompt -> PackageManager hides launcher icon -> Persistent foreground service spawns Socket worker thread -> SensorRestarterBroadcastReceiver and JobScheduler maintain execution across process kills.",
  "ntapi_functions": [
    "android.media.AudioRecord!startRecording",
    "android.hardware.Camera!open",
    "android.media.projection.MediaProjection!createVirtualDisplay",
    "android.telephony.SmsManager!sendTextMessage",
    "android.location.LocationManager!requestLocationUpdates",
    "android.app.admin.DevicePolicyManager!resetPassword",
    "android.content.pm.PackageManager!setComponentEnabledSetting"
  ],
  "process_hollowing_target": "Standalone background service process or merged host APK activity lifecycle",
  "persistence_mechanics": [
    "SensorRestarterBroadcastReceiver: Broadcast intent fired inside Service.onDestroy() and Service.onTaskRemoved() that immediately restarts the core C2 service",
    "JobScheduler / AlarmManager Heartbeat: Schedules periodic wakeup jobs every 5-15 minutes to verify socket health and re-establish dropped connections",
    "BOOT_COMPLETED BroadcastReceiver: Starts the background service upon Android OS boot completion or PACKAGE_REPLACED events",
    "DeviceAdminReceiver Protection: Registers android.app.action.DEVICE_ADMIN_ENABLED to grey out the 'Uninstall' button in Android Settings",
    "WakeLock Acquisition: Holds PowerManager.PARTIAL_WAKE_LOCK to keep CPU scheduling active when the screen is off"
  ],
  "evasion_hooks": [
    "Launcher Icon Suppression: Invokes PackageManager.setComponentEnabledSetting(ComponentName, COMPONENT_ENABLED_STATE_DISABLED, DONT_KILL_APP)",
    "Accessibility Settings Guard: Monitors foreground window package names and executes performGlobalAction(GLOBAL_ACTION_BACK) if the user attempts to revoke Device Admin or Accessibility privileges",
    "Silent Notification Channel: Creates low-importance or collapsed NotificationChannel entries to conceal the mandatory startForeground() service indicator"
  ],
  "anti_analysis": [
    "Root & Debugger Checks: Inspects /system/bin/su, /system/xbin/su, and Build.TAGS for 'test-keys'",
    "Emulator Detection: Evaluates TelephonyManager.getNetworkOperatorName() for 'Android' and checks Build.MODEL for 'sdk' or 'google_sdk'",
    "Decompiler Evasion (CypherRAT/SpyMax variants): Appends oversized junk byte arrays and invalid opcodes into unused Smali methods"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the SpyNote (SpyMax / CypherRAT Lineage) binary:
[ "Accessibility Keylogger: Captures every AccessibilityEvent.TYPE_VIEW_TEXT_CHANGED and TYPE_VIEW_CLICKED event across all installed applications", "SMS 2FA Interception: Registers high-priority BroadcastReceiver for android.provider.Telephony.SMS_RECEIVED and queries content://sms/ to steal one-time passwords", "Account Manager Enumeration: Queries AccountManager.getAccounts() to harvest registered Google, WhatsApp, Facebook, and corporate email identities", "Notification Listener Scraping: Intercepts StatusBarNotification objects to read incoming WhatsApp, Telegram, and banking push alerts", "Saved Wi-Fi & Clipboard Harvesting: Extracts clipboard buffers via ClipboardManager and enumerates configured SSID metadata" ]
[ "Live Screen Streaming: Uses MediaProjectionManager and VirtualDisplay + ImageReader to capture and compress real-time screen frames", "Ambient Microphone Bugging: Streams continuous PCM audio via AudioRecord wrapped in GZIP packets to the operator console", "Stealth Camera Capture: Acquires front or rear Camera hardware without shutter sound using a dummy SurfaceTexture", "GPS & Cell Tower Tracking: Polls LocationManager and TelephonyManager (CellLocation) for real-time geographic coordinates", "Call Log & SMS Database Dump: Exfiltrates complete historical call records and SMS threads" ]
[ "Interactive Shell Terminal: Executes system commands via /system/bin/sh and pipes output back to the operator GUI", "Application Launcher & Manager: Lists all installed packages, extracts APK files from /data/app/, or launches specific intents", "Remote Touch & Key Injection (SpyMax/CypherRAT): Dispatches synthetic clicks and back/home actions via AccessibilityService" ]
[ "SDCard & Internal Directory Explorer: Full read/write/delete access to /sdcard/ and accessible storage volumes", "Thumbnail & Gallery Exfiltration: Generates and streams image previews from DCIM and Pictures directories", "Remote Payload Staging: Downloads secondary APK or binary files from C2 and triggers PackageInstaller intents" ]
[ "Clipboard Monitoring & Injection: Reads and overwrites Android clipboard contents via ClipboardManager.setPrimaryClip()" ]
[ "Device Lock & Password Reset: Invokes DevicePolicyManager.lockNow() and resetPassword() (on legacy API levels) to lock victims out of their handsets", "Audio & Vibrator Control: Manipulates AudioManager stream volumes (Ring, Media, Alarm) and triggers device vibration", "Outbound SMS & Call Dispatch: Silently sends SMS messages to premium numbers or initiates outbound phone calls" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Custom ASCII string delimiters separating command headers and arguments, followed by a null byte or delimiter token and GZIP-compressed payload bytes",
  "serialization": "Custom delimited text arrays (e.g., separated by 'SPL_DATA' or '0x0F0x0F') paired with GZIPInputStream / GZIPOutputStream binary blocks",
  "handshake": "Android stub connects via java.net.Socket to C2 IP:Port -> Transmits initial GZIP-compressed identification string (ClientName, IP, Device Model, Android Version, Battery, Camera flag) -> Server validates delimiter format and registers session in UI grid",
  "cryptography": "Unencrypted raw TCP transport utilizing GZIP stream compression (0x1F 0x8B magic bytes) for bandwidth reduction; optional static XOR or Base64 encoding on string arguments",
  "packet_types": [
    {
      "header": "files / file_manager",
      "payload": "Delimited directory listing (FileName, Size, LastModified, Type)",
      "direction": "Client -> Server"
    },
    {
      "header": "mic / audio",
      "payload": "GZIP-compressed raw PCM audio buffer recorded from AudioRecord",
      "direction": "Client -> Server"
    },
    {
      "header": "cam / camera",
      "payload": "GZIP-compressed JPEG byte array captured from Camera preview callback",
      "direction": "Client -> Server"
    },
    {
      "header": "sms / call_log",
      "payload": "Delimited records containing Address, Body, Date, and Thread Type",
      "direction": "Client -> Server"
    },
    {
      "header": "keylogger",
      "payload": "Accessibility event stream containing PackageName, EventType, and CapturedText",
      "direction": "Client -> Server"
    }
  ],
  "traffic_signature": "Raw TCP streams over ports 2222, 3210, 7771, or 7772 containing repetitive GZIP headers (1F 8B 08 00) immediately preceded or followed by hardcoded ASCII delimiter strings."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_SpyNote_SpyMax_DEX {
    meta:
        description = "Identifies SpyNote, SpyMax, and CypherRAT Android DEX payloads via characteristic service and receiver class names"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-30"
        family = "SpyNote"
        platform = "Android"
    strings:
        $dex = { 64 65 78 0A 30 33 ?? 00 }
        $c1 = "SensorRestarterBroadcastReceiver" ascii
        $c2 = "CameraManager" ascii
        $c3 = "Keylogger" ascii
        $c4 = "DeviceAdmin" ascii
        $s1 = "content://sms/inbox" ascii
        $s2 = "android.provider.Telephony.SMS_RECEIVED" ascii
        $s3 = "MediaProjectionManager" ascii
        $s4 = "setComponentEnabledSetting" ascii
    condition:
        $dex at 0 and
        (3 of ($c*) and 2 of ($s*))
}title: SpyNote and SpyMax APK Builder Compilation Activity
id: 7c9d2e3f-4a5b-4c6d-8e9f-0a1b2c3d4e5f
status: stable
description: Detects the Windows-based SpyNote or SpyMax builder invoking apktool.jar and signapk.jar to compile and sign weaponized Android APK payloads.
author: CyberTrace Defense Engineering
date: 2026/10/30
references:
- https://attack.mitre.org/Mobile/software/S0428/
tags:
- attack.execution
- attack.defense_evasion
logsource:
category: process_creation
product: windows
detection:
selection_signapk:
Image|endswith:
- '\java.exe'
- '\javaw.exe'
CommandLine|contains|all:
- '-jar'
- 'signapk.jar'
- 'certificate.pem'
- 'key.pk8'
selection_apktool:
Image|endswith:
- '\java.exe'
- '\javaw.exe'
CommandLine|contains|all:
- '-jar'
- 'apktool'
- ' b '
condition: selection_signapk or selection_apktool
falsepositives:
- Legitimate Android reverse-engineering or security research workstations.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
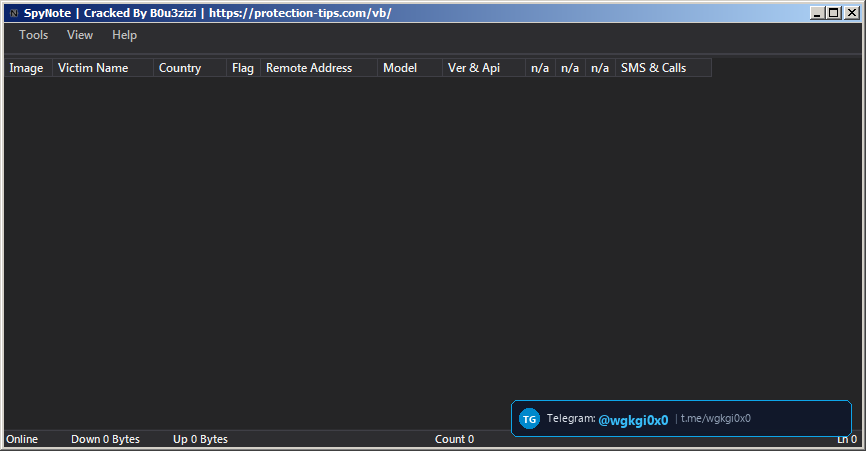
SpyNote Windows desktop controller enumerating connected Android endpoints, API levels, device models, and remote surveillance modules.
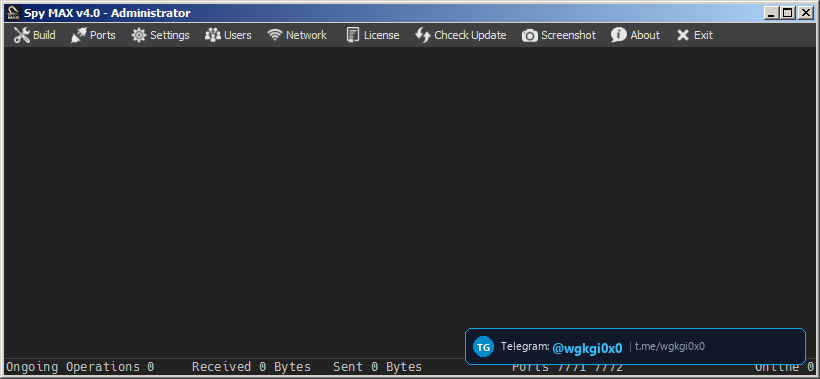
SpyMax v4.0 operator toolbar exposing Build, Ports (7771/7772), Network telemetry, and APK payload generation.
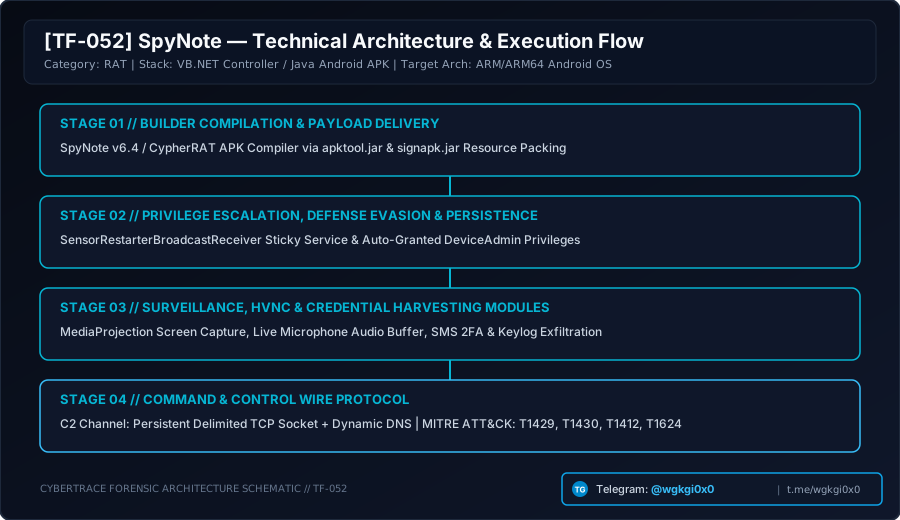
Forensic architecture schematic illustrating apktool/signapk payload compilation, SensorRestarterBroadcastReceiver persistence, MediaProjection screen capture, and delimited TCP socket C2.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
SpyNote (SpyMax / CypherRAT Lineage) (RAT)
Foundational Android RAT family (including SpyMax and CypherRAT) utilizing apktool/signapk payload generation, Accessibility auto-granting, and delimited GZIP TCP streams.
C2 Architecture: {'framing': 'Custom ASCII string delimiters separating command headers and arguments, followed by a null byte or delimiter token and GZIP-compressed payload bytes', 'serialization': "Custom delimited text arrays (e.g., separated by 'SPL_DATA' or '0x0
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ SpyNote (SpyMax / CypherRAT Lineage) (RAT)
Детальный технический анализ SpyNote (v6.4 / SpyMax v4.0 / CypherRAT) — модульного Android-трояна удаленного доступа (RAT). В досье разбираются автоматическая компиляция APK через apktool и signapk.jar, удержание присутствия через SensorRestarterBroadcastReceiver, захват экрана через MediaProjection API и кейлоггинг системных событий доступности.
Архитектура C2: Асинхронный протокол поверх TCP-сокетов (порты 7771/7772) с использованием разделителей пакетов и GZip-сжатия телеметрии.
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
SpyNote (SpyMax / CypherRAT Lineage) (RAT) विश्लेषण
SpyNote (v6.4 / SpyMax v4.0 / CypherRAT) एक परिष्कृत Android रिमोट एक्सेस ट्रोजन (RAT) है। इस तकनीकी रिपोर्ट में apktool/signapk पेलोड संकलन, SensorRestarterBroadcastReceiver पर्सिस्टेंस, MediaProjection स्क्रीन कैप्चर और AccessibilityService कीलॉगिंग तंत्र का विस्तृत विश्लेषण किया गया है।
C2 संचार: कस्टम स्ट्रिंग डिलिमिटर और GZip-संपीड़ित बाइट स्ट्रीम के साथ TCP सॉकेट (पोर्ट 7771/7772) C2 संचार।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).