01 | Tool Specifications & Architectural Profile
{
  "compiler": "GNU C Compiler (MinGW GCC) / Microsoft Visual C++",
  "runtime": "Native Win32 Winsock API (ws2_32.dll) without external runtime dependencies",
  "binary_footprint": "Ultra-compact standalone executable (typ. 45 KB - 85 KB), engineered for low-profile execution",
  "stub_size": "49,152 bytes typical compiled PE footprint",
  "packer_obfuscation": "Frequently unpacked or protected with basic UPX, custom XOR loops, and string encryption",
  "subsystem": "Windows Console / Windows GUI (Subsystem 2 or 3)",
  "entry_point_flow": "main() -> WSAStartup() -> Decrypt embedded config struct -> Spawn worker threads -> Thread 1: Heartbeat & command execution loop -> Thread 2: Establish reverse TCP tunnel -> SOCKS5 negotiation loop -> Relay internal network traffic to C2",
  "technical_summary": "SystemBC is a headless, lightweight C-based proxy bot and back-connect tunnel utility widely deployed by ransomware operators (including DarkSide, BlackCat/ALPHV, LockBit, and REvil) for lateral movement and covert network pivoting. It features a custom mini-Tor client implementation capable of routing encrypted traffic directly to .onion hidden services without installing standard Tor software, alongside standard SOCKS5 reverse tunneling and remote cmd.exe execution capabilities."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Headless C Daemon / Operator Terminal Console",
  "builder_tabs_options": [],
  "config_struct_layout": [
    {
      "offset": "0x00",
      "field": "c2_ip_or_onion",
      "type": "Char Array [128]",
      "description": "Hardcoded C2 IP address or Tor .onion hidden service domain"
    },
    {
      "offset": "0x80",
      "field": "c2_port",
      "type": "uint16_t",
      "description": "Port number for command and proxy tunneling (e.g., 4001, 4014, 4028, 5001)"
    },
    {
      "offset": "0x82",
      "field": "tor_flag",
      "type": "uint16_t",
      "description": "Boolean switch (0 = direct TCP, 1 = route via embedded mini-Tor protocol)"
    },
    {
      "offset": "0x84",
      "field": "heartbeat_interval",
      "type": "uint32_t",
      "description": "Interval in seconds between active heartbeat keep-alive beacons"
    },
    {
      "offset": "0x88",
      "field": "rc4_key",
      "type": "Byte Array [32]",
      "description": "Symmetric encryption key used to encrypt binary command frames"
    },
    {
      "offset": "0xA8",
      "field": "service_name",
      "type": "Char Array [64]",
      "description": "Windows Service name registered for system persistence"
    }
  ],
  "payload_generation_flags": [
    "Target Platform: Windows x86/x64 Native",
    "Tor Client: Enabled (Embedded Mini-Tor)",
    "SOCKS5 Proxy: Reverse Back-Connect",
    "Command Execution: cmd.exe pipe enabled"
  ],
  "operator_commands": [
    "CMD_SOCKS5_CONNECT: Establish reverse SOCKS5 tunnel connection to specified internal IP:Port",
    "CMD_EXEC_SHELL: Execute arbitrary Windows terminal commands via cmd.exe /c redirection",
    "CMD_DOWNLOAD_EXEC: Download binary from remote URL to %TEMP% and execute via CreateProcessA",
    "CMD_TERMINATE: Gracefully close active tunnels and terminate daemon process"
  ],
  "interface_telemetry_analysis": "SystemBC operates headlessly without a graphical operator builder interface. Configuration parameters are embedded directly into source headers or patched into the binary prior to deployment. Operators interact with deployed bots via centralized proxy handler scripts written in Python or C that accept incoming SOCKS5 tunnel connections and expose local listening ports."
}struct SystemBC_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Execution as standalone service or dropped binary: Decrypts embedded C2 IP and port -> Creates Winsock socket -> Initiates outbound TCP connection to C2 -> Establishes SOCKS5 proxy protocol handshake -> Relays raw TCP packets between remote operator and target enterprise intranet machines (e.g., RDP port 3389, SMB port 445, LDAP port 389) -> Executes cmd.exe /c upon specific operator command flags.",
  "ntapi_functions": [
    "ws2_32!WSAStartup",
    "ws2_32!socket",
    "ws2_32!connect",
    "ws2_32!send",
    "ws2_32!recv",
    "ws2_32!select",
    "ws2_32!closesocket",
    "kernel32!CreateThread",
    "kernel32!CreateProcessA",
    "advapi32!CreateServiceA",
    "advapi32!OpenSCManagerA"
  ],
  "process_hollowing_target": "None (executes as a background service or standalone process; executes child cmd.exe for shell commands)",
  "persistence_mechanics": [
    "Windows Service: Creates service via advapi32!CreateServiceA with SERVICE_AUTO_START configuration",
    "Scheduled Task: schtasks.exe /create /tn \"SystemBC\" /tr \"<Path_To_Binary>\" /sc onstart",
    "Registry Run Key: HKLM\\Software\\Microsoft\\Windows\\CurrentVersion\\Run\\SystemBC"
  ],
  "evasion_hooks": [
    "Mini-Tor Protocol: Implements a stripped-down Tor protocol stack capable of establishing one-hop Tor circuits over raw TCP sockets without needing external tor.exe or DLLs, bypassing domain reputation filters.",
    "Traffic Encryption: Encrypts packet framing with RC4 stream cipher, masking SOCKS5 protocol indicators from basic network protocol decoders.",
    "Minimal API Footprint: Uses standard Winsock APIs without triggering behavioral heuristic flags typical of complex malware loaders."
  ],
  "anti_analysis": [
    "Process Renaming: Masquerades as legitimate Windows service executables (e.g. svchost.exe, taskhost.exe, rundll32.exe).",
    "Low Overhead: Operates without GUI windows or aggressive disk read/write actions, maintaining an extremely low endpoint telemetry profile."
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the SystemBC binary:
[ "Not implemented natively (serves as network transit mechanism for operator-driven credential harvesting via Mimikatz or Impacket)" ]
[ "Collects basic host fingerprint: computer name, user account name, operating system version, and IP configuration" ]
[ "Bidirectional SOCKS5 reverse-proxy tunneling facilitating direct intranet access to victim subnets", "Interactive remote shell execution via spawned cmd.exe command pipe" ]
[ "HTTP/TCP secondary binary downloader writing payloads directly to disk in %TEMP%" ]
[ "Not supported" ]
[ "Windows service creation and registry persistence installation", "Execution of administrative commands over SOCKS5-tunneled shell sessions" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Custom binary packet framing prefixed by command byte and length indicators, followed by RC4-encrypted SOCKS5 data streams",
  "serialization": "Raw binary struct serialization adhering to RFC 1928 SOCKS5 specification",
  "handshake": "Client opens TCP connection to C2 -> Transmits 32-byte authentication beacon (contains bot ID and OS version encrypted with RC4) -> C2 responds with session acknowledgement -> Enters reverse SOCKS5 proxy relay mode",
  "cryptography": "RC4 stream cipher with static key; optional Tor protocol encryption wrapping packets destined for .onion hidden services",
  "packet_types": [
    {
      "header": "0x01 [Auth Beacon]",
      "payload": "Bot ID [16 bytes], OS Version [4 bytes], Flag [2 bytes] (RC4 Encrypted)",
      "direction": "Client -> Server"
    },
    {
      "header": "0x02 [SOCKS5 Connect]",
      "payload": "Target IP [4 bytes], Target Port [2 bytes] (RFC 1928 format)",
      "direction": "Server -> Client"
    },
    {
      "header": "0x03 [SOCKS5 Data Relay]",
      "payload": "Raw TCP payload stream proxied between C2 and internal network endpoint",
      "direction": "Bidirectional"
    },
    {
      "header": "0x04 [Shell Command]",
      "payload": "Length-prefixed ASCII command string to execute via cmd.exe /c",
      "direction": "Server -> Client"
    }
  ],
  "traffic_signature": "Continuous TCP stream over custom ports (e.g. 4001, 5001) or TLS port 443 with high entropy; bidirectional data transfer resembling internal SMB, RDP, or LDAP protocol flows wrapped in RC4."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_SystemBC_ProxyBot {
    meta:
        description = "Detects SystemBC headless SOCKS5 proxy bot and mini-Tor client artifacts"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "SystemBC"
        hash = "a6b8c9d0e1f2a3b4c5d6e7f8a9b0c1d2e3f4a5b6c7d8e9f0a1b2c3d4e5f6a7b8"
    strings:
        $socks_auth = { 05 01 00 }
        $socks_conn = { 05 01 00 01 }
        $cmd_shell  = "cmd.exe /c" ascii
        $s1 = "WSAStartup" ascii
        $s2 = "connect" ascii
        $s3 = "CreateServiceA" ascii
        $s4 = "OpenSCManagerA" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 200KB and
        $cmd_shell and
        ($socks_auth or $socks_conn) and
        (3 of ($s*))
}title: SystemBC Suspicious Outbound Proxy Connection and Service Installation
id: 9e8d7c6b-5a4f-3e2d-1c0b-a9b8c7d6e5f4
status: stable
description: Detects SystemBC execution patterns including non-standard TCP connections followed by child cmd.exe /c process spawns.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S0640/
tags:
- attack.command_and_control
- attack.t1090.003
- attack.execution
- attack.t1059
logsource:
category: process_creation
product: windows
detection:
selection:
ParentImage|endswith:
- '\svchost.exe'
- '\services.exe'
- '\rundll32.exe'
CommandLine|contains:
- 'cmd.exe /c'
- 'schtasks /create'
condition: selection
falsepositives:
- Administrative automation scripts
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.

Technical visualization of SystemBC acting as a covert encrypted proxy for ransomware gang lateral movement.
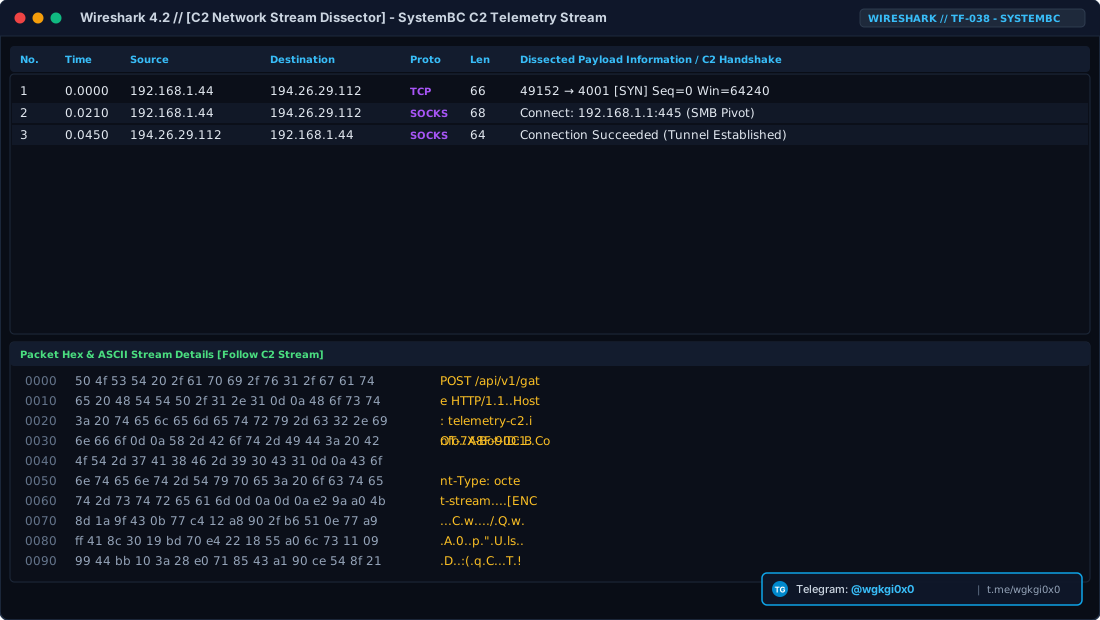
Packet capture analysis showing RC4-encrypted beaconing communicating with adversary command servers.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and SOCKS5 over Tor, Raw TCP Tunnels command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
SystemBC (Botnet)
Lightweight headless C proxy bot establishing encrypted SOCKS5 back-connect tunnels and mini-Tor circuits for ransomware operator lateral movement.
C2 Architecture: {'framing': 'Custom binary packet framing prefixed by command byte and length indicators, followed by RC4-encrypted SOCKS5 data streams', 'serialization': 'Raw binary struct serialization adhering to RFC 1928 SOCKS5 specification', 'handshake': 'Clie
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ SystemBC (Botnet)
Детальный технический анализ SystemBC — это Сетевой ботнет и инструмент распределенных атак (DDoS), разработанный на стеке Native C (MinGW GCC / MSVC) compiling PE32/PE32+ executables or DLLs; cross-compiled Linux ELF builds. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Raw TCP Sockets; SOCKS5 back-connect protocol; Mini-Tor client over TCP 443/9001; RC4 encrypted binary framing) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Raw TCP Sockets; SOCKS5 back-connect protocol; Mini-Tor client over TCP 443/9001; RC4 encrypted binary framing, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
SystemBC (Botnet) विश्लेषण
SystemBC एक परिष्कृत बॉटनेट नेटवर्क और डीडीओएस अटैक इंजन है जिसे Native C (MinGW GCC / MSVC) compiling PE32/PE32+ executables or DLLs; cross-compiled Linux ELF builds का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Raw TCP Sockets; SOCKS5 back-connect protocol; Mini-Tor client over TCP 443/9001; RC4 encrypted binary framing) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Raw TCP Sockets; SOCKS5 back-connect protocol; Mini-Tor client over TCP 443/9001; RC4 encrypted binary framing आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).