01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C# Compiler (Roslyn / dnlib post-build assembly rewriter)",
  "runtime": ".NET Common Language Runtime (CLR) v4.0.30319",
  "binary_footprint": "PE32 .NET CIL executable stub (52 KB - 145 KB base binary; 450 KB+ when bundled with HVNC helper and Recovery.dll)",
  "stub_size": "61,440 bytes (unpacked client stub), expanding to 350 KB - 1.8 MB with SmartAssembly, ConfuserEx, or Donut shellcode wrappers",
  "packer_obfuscation": "ConfuserEx, KoiVM, Babel Obfuscator, .NET Reactor, or BatCloak / PowerShell AMSI-bypassed reflective loaders",
  "subsystem": "Windows GUI (IMAGE_SUBSYSTEM_WINDOWS_GUI = 2)",
  "entry_point_flow": "Client.Program.Main() -> Settings.InitializeSettings() -> MutexControl.CreateMutex() -> Anti_Analysis.RunAntiAnalysis() -> Install.Run() -> ClientSocket.InitializeClient() -> SslStream.AuthenticateAsClient() -> MsgPack read/write loop",
  "technical_summary": "VenomRAT is a commercialized C# remote administration and Hidden VNC (HVNC) framework forked from the QuasarRAT and AsyncRAT codebases. It integrates an operator console ('Venom Software') featuring six primary operational views: Dashboard, Password Recovery, Fetching Data, Thumbnail, Builder Settings, and HVNC Panel. Beyond standard asynchronous MessagePack C2 operations, VenomRAT implements native Win32 desktop object creation (CreateDesktopA / SetThreadDesktop) for non-intrusive graphical session interaction, automated browser user-data directory cloning for concurrent session hijacking, and an in-memory Recovery.dll plugin engineered for Chromium v10/v20 AES-GCM decryption and payment card regex scraping."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Venom Software GUI & Builder (WinForms Operator Console)",
  "builder_tabs_options": [
    {
      "tab": "Dashboard & Listener",
      "options": [
        "Client Folder: Opens local server-side directory storing exfiltrated logs, SQLite databases, and keystrokes per victim HWID",
        "Builder: Launches integrated dnlib-based payload compiler modal",
        "HVNC Panel: Opens dedicated Hidden Virtual Network Computing listener port (default: 4448/TCP)",
        "Tasks Manager: Configures automated On-Connect command queues (Auto-Recovery, Auto-Keylogger, Auto-Miner, Download & Execute)"
      ]
    },
    {
      "tab": "Password Recovery & Fetching Data",
      "options": [
        "Password Recovery: Displays tabulated credentials, cookies, autofill records, and cryptocurrency wallet paths parsed from Recovery.dll",
        "Fetching Data: Tracks real-time progress of bulk browser profile exfiltration, Discord token scraping, and file grabber streams",
        "Thumbnail: Renders periodic low-resolution GDI screen previews across all connected endpoints"
      ]
    },
    {
      "tab": "Builder Settings - Connection & Installation",
      "options": [
        "Hosts / IP / DNS: Primary and fallback C2 addresses with port array (default: 4449, 6606, 4448 for HVNC)",
        "Install Client: Drops persistence binary into %AppData%, %LocalAppData%, or %Temp% with Task Scheduler registration",
        "Group Tag & Mutex: Custom campaign tag and unique mutex identifier (e.g., VenomMutex_v6)",
        "Startup Persistence: Dual Registry Run key and elevated schtasks.exe trigger"
      ]
    },
    {
      "tab": "Builder Settings - Evasion & Protection",
      "options": [
        "Anti-VM / Anti-Debugger: Queries WMI Win32_CacheMemory, Win32_ComputerSystem, and CheckRemoteDebuggerPresent",
        "Disable Windows Defender: Executes PowerShell Set-MpPreference and WMI root\\Microsoft\\Windows\\Defender exclusions",
        "BSOD on Termination: Invokes ntdll!RtlSetProcessIsCritical to trigger BugCheck 0xEF if terminated",
        "UACBypass: Integrates fodhelper.exe, computerdefaults.exe, and CMSTP COM elevation routines"
      ]
    },
    {
      "tab": "HVNC Panel Controls",
      "options": [
        "Clone Chrome / Edge / Brave / Firefox: Copies live browser User Data profile to %Temp%\\VenomHVNC and spawns isolated browser instance",
        "Start Explorer / CMD / PowerShell: Launches interactive shell or explorer.exe inside hidden desktop context",
        "Quality & Resize Slider: Adjusts GDI PrintWindow JPEG compression ratio (10% - 100%)"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "Client.Settings.Ports",
      "field": "Ports",
      "type": "String",
      "description": "AES-256-CBC encrypted Base64 string of comma-delimited C2 TCP ports"
    },
    {
      "offset": "Client.Settings.Hosts",
      "field": "Hosts",
      "type": "String",
      "description": "AES-256-CBC encrypted C2 IPv4/DNS endpoint list"
    },
    {
      "offset": "Client.Settings.Version",
      "field": "Version",
      "type": "String",
      "description": "Encrypted build version identifier (e.g., VenomRAT v6.0.5 / v6.1.0)"
    },
    {
      "offset": "Client.Settings.Install",
      "field": "Install",
      "type": "String",
      "description": "Boolean string flag ('true'/'false') governing local persistence drop"
    },
    {
      "offset": "Client.Settings.InstallFolder",
      "field": "InstallFolder",
      "type": "String",
      "description": "SpecialFolder enumeration target (ApplicationData, LocalApplicationData, Templates)"
    },
    {
      "offset": "Client.Settings.InstallFile",
      "field": "InstallFile",
      "type": "String",
      "description": "Masqueraded filename for persistent binary (e.g., OneDriveUpdate.exe)"
    },
    {
      "offset": "Client.Settings.Key",
      "field": "Key",
      "type": "String",
      "description": "Master passphrase used by Rfc2898DeriveBytes (PBKDF2) to derive AES-256 key and HMAC-SHA256 key"
    },
    {
      "offset": "Client.Settings.MTX",
      "field": "MTX",
      "type": "String",
      "description": "Unique synchronization mutex name preventing duplicate stub instances"
    },
    {
      "offset": "Client.Settings.Certificate",
      "field": "ServerCertificate",
      "type": "String",
      "description": "Encrypted Base64 X.509 certificate used to validate the C2 server TLS handshake"
    },
    {
      "offset": "Client.Settings.Group",
      "field": "Group",
      "type": "String",
      "description": "Encrypted operator campaign identifier displayed in the Dashboard grid"
    }
  ],
  "payload_generation_flags": [
    "Target CLR: .NET Framework 4.5.2 / 4.8 (AnyCPU)",
    "Assembly Rewriting: dnlib instruction patching of Client.Settings.cctor",
    "Resource Compression: GZipStream compression of embedded plugins (Recovery.dll, HVNC.dll)"
  ],
  "operator_commands": [
    "recovery: Reflectively loads Recovery.dll to extract browser credentials, cookies, credit cards, and crypto wallets",
    "hvnc: Spawns or attaches to hidden desktop 'VenomHVNC' and initiates GDI WM_PRINT window frame streaming",
    "plugin: Transfers GZip-compressed .NET plugin assembly and executes Plugin.Run() in memory",
    "rdp: Installs or configures hidden remote desktop session and streams desktop frames",
    "fun: Triggers operator control routines (monitor power off, swap mouse buttons, block input via user32!BlockInput)",
    "keylogger: Streams real-time WH_KEYBOARD_LL keystroke buffer with active window context",
    "reverseProxy: Initiates SOCKS5 tunnel multiplexing over the C2 socket",
    "uac: Executes silent privilege elevation via fodhelper.exe registry hijacking"
  ],
  "interface_telemetry_analysis": "The VenomRAT v6.x operator console uses a dark-themed WinForms ribbon interface organized into six primary navigation tabs: Dashboard, Password Recovery, Fetching Data, Thumbnail, Builder Settings, and HVNC Panel. The top status header tracks real-time counters for Connected clients, Selected targets, Logs collected, USB Spread events, and Total network bytes sent/received."
}struct VenomRAT_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "HVNC Desktop Session Isolation & Browser Cloning: Invokes user32!OpenDesktopA(\"VenomHVNC\", 0, false, GENERIC_ALL) -> falls back to user32!CreateDesktopA(\"VenomHVNC\", NULL, NULL, 0, GENERIC_ALL, NULL) -> binds rendering thread via user32!SetThreadDesktop(hDesktop) -> clones %LocalAppData%\\Google\\Chrome\\User Data to %Temp%\\VenomChromeData -> spawns chrome.exe into hidden desktop via kernel32!CreateProcessA with STARTUPINFOA.lpDesktop = \"VenomHVNC\" and flags \"--no-sandbox --allow-no-sandbox-job --disable-3d-apis --disable-gpu --disable-d3d11 --user-data-dir=...\".",
  "ntapi_functions": [
    "user32!CreateDesktopA",
    "user32!OpenDesktopA",
    "user32!SetThreadDesktop",
    "user32!PrintWindow",
    "user32!SendMessageA",
    "bcrypt!BCryptOpenAlgorithmProvider",
    "bcrypt!BCryptDecrypt",
    "crypt32!CryptUnprotectData",
    "ntdll!RtlSetProcessIsCritical"
  ],
  "process_hollowing_target": "RegSvcs.exe, InstallUtil.exe, MSBuild.exe, or hidden desktop instances of chrome.exe, msedge.exe, and explorer.exe",
  "persistence_mechanics": [
    "Scheduled Task: cmd.exe /c schtasks /create /f /sc onlogon /rl highest /tn \"VenomUpdateTask\" /tr \"'%AppData%\\FileName.exe'\"",
    "Registry Run Key: HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Run\\[InstallFile]",
    "Batch Self-Startup Script: Drops temporary .bat script in %Temp% to re-launch binary and apply +h +s file attributes via attrib.exe"
  ],
  "evasion_hooks": [
    "AMSI Patching: Overwrites amsi!AmsiScanBuffer prologue in memory prior to reflective Assembly.Load(byte[]) calls",
    "Defender Tampering: Invokes powershell.exe -WindowStyle Hidden -Command \"Add-MpPreference -ExclusionPath 'C:\\Users' -ExclusionProcess 'chrome.exe'\"",
    "Process Criticality: Calls ntdll!RtlSetProcessIsCritical(1, 0, 0) when process holds SeDebugPrivilege"
  ],
  "anti_analysis": [
    "WMI Hardware Validation: Queries SELECT * FROM Win32_ComputerSystem for 'VMware', 'VIRTUAL', 'VBox', and 'QEMU' strings",
    "Loaded DLL Inspection: Checks kernel32!GetModuleHandleA for SbieDll.dll (Sandboxie), sxIn.dll (360 Sandbox), and cmdvrt32.dll (Comodo)",
    "Debugger Verification: Executes kernel32!CheckRemoteDebuggerPresent and inspects System.Diagnostics.Debugger.IsAttached"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the VenomRAT binary:
[ "In-memory Recovery.dll plugin containing namespaces Stealer, Stealer.Banking, cAesGcm, and cBCrypt", "Chromium v80+ Master Key extraction from Local State JSON via CryptUnprotectData and AES-256-GCM decryption via bcrypt.dll", "Payment card type classification via CreditCardTypes regex dictionary matching Visa, Mastercard, Amex, Diners Club, Discover, and JCB patterns", "Banking domain keyword detector flagging active sessions across financial portals and cryptocurrency exchanges", "Discord token extraction from %AppData%\\discord\\Local Storage\\leveldb using regex [\\w-]{24}\\.[\\w-]{6}\\.[\\w-]{27} and dQw4w9WgXcQ: encrypted token parsing" ]
[ "Hidden VNC (HVNC) rendering loop enumerating windows via EnumDesktopWindows and capturing bitmaps via WM_PRINT / PrintWindow", "Interactive Remote Desktop streaming via GDI BitBlt / CopyFromScreen with delta frame encoding", "Asynchronous low-level keystroke logger (SetWindowsHookEx WH_KEYBOARD_LL) with clipboard state tracking", "Webcam and microphone capture plugins loaded dynamically via AppDomain.CurrentDomain.Load" ]
[ "Interactive Hidden VNC mouse and keyboard synthesis via PostMessageA (WM_LBUTTONDOWN, WM_LBUTTONUP, WM_CHAR, WM_KEYDOWN) directly to target HWND handles", "Cloned browser session execution bypassing file locks on Cookies and Login Data SQLite databases", "Bidirectional reverse command shell (cmd.exe and powershell.exe) over TLS stream", "SOCKS5 reverse proxy for internal network pivoting using victim residential IP" ]
[ "Full filesystem explorer supporting recursive directory listing, ZIP archive compression, upload, download, and secure deletion", "Automated Fetching Data grabber harvesting .txt, .doc, .docx, .pdf, .kdbx, .rdp, and seed phrase files from Desktop and Documents" ]
[ "Background clipboard monitor replacing copied wallet addresses for BTC, ETH, LTC, XMR, and TRC20 USDT", "Wallet directory exfiltration targeting Electrum, Exodus, Atomic, Coinomi, and MetaMask / Phantom browser extensions" ]
[ "Silent UAC elevation utilizing fodhelper.exe (HKCU\\Software\\Classes\\ms-settings\\Shell\\Open\\command)", "Hosts file manipulation redirecting antivirus update domains to 127.0.0.1", "Task Manager, Registry Editor, and Windows Defender service disabling via HKCU\\Software\\Microsoft\\Windows\\CurrentVersion\\Policies\\System" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "4-byte Little-Endian integer length header indicating compressed payload size, followed by a 4-byte Little-Endian integer indicating uncompressed MessagePack size, followed by GZip-compressed MessagePack bytes",
  "serialization": "Custom lightweight MessagePack binary serialization (Client.MessagePackLib.MsgPack) encoding nested key-value dictionaries",
  "handshake": "Client connects via TCP -> Wraps socket in System.Net.Security.SslStream -> Validates Server X.509 Certificate against embedded Client.Settings.ServerCertificate -> Transmits 'ClientInfo' MsgPack registration packet",
  "cryptography": "Transport secured via TLS 1.2 (SslProtocols.Tls12 with RSA-2048 self-signed certificate CN=VenomRAT Server). Configuration strings encrypted via AES-256-CBC with HMAC-SHA256 integrity verification (PBKDF2 50,000 iterations, 32-byte static salt).",
  "packet_types": [
    {
      "header": "Pac_ket: ClientInfo",
      "payload": "HWID, User, OS, Camera, Path, Version, Admin, Performance, Pastebin, Antivirus, Installed, Pong, Group",
      "direction": "Client -> Server"
    },
    {
      "header": "Pac_ket: recoveryPassword",
      "payload": "GZip-compressed archive of credentials, cookies, autofill data, and credit card records extracted by Recovery.dll",
      "direction": "Client -> Server"
    },
    {
      "header": "Pac_ket: hvnc",
      "payload": "Hidden desktop bitmap stream, window coordinate click events, and browser clone launch triggers (CloneChrome, CloneEdge)",
      "direction": "Bidirectional"
    },
    {
      "header": "Pac_ket: plugin",
      "payload": "SHA256 plugin identifier and raw GZip-compressed .NET assembly bytes for in-memory execution",
      "direction": "Server -> Client"
    },
    {
      "header": "Pac_ket: Logs",
      "payload": "Real-time status notification strings updating the VenomRAT Dashboard Fetching Data and Logs counters",
      "direction": "Client -> Server"
    }
  ],
  "traffic_signature": "TLS 1.2 session presenting self-signed certificate Subject/Issuer CN='VenomRAT Server' or 'AsyncRAT Server'. Decrypted stream contains GZip magic bytes (1F 8B 08 00) preceded by an 8-byte dual length header and decompresses to MessagePack maps containing the key string 'Pac_ket'."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_VenomRAT_And_RecoveryPlugin {
    meta:
        description = "Detects VenomRAT client stubs, HVNC modules, and in-memory Recovery.dll stealer plugins"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-31"
        family = "VenomRAT"
        hash = "9c4b8e1f72a30d56b84129c0e3f4a1d28c7b6a59e01234f56789abcdef012345"
    strings:
        $v1 = "VenomRAT" ascii wide nocase
        $v2 = "VenomHVNC" ascii wide
        $v3 = "Pac_ket" ascii wide
        $v4 = "ServerCertificate" ascii
        $hvnc1 = "--no-sandbox --allow-no-sandbox-job --disable-3d-apis --disable-gpu" ascii wide
        $hvnc2 = "CreateDesktop" ascii
        $hvnc3 = "SetThreadDesktop" ascii
        $rec1 = "Stealer.Banking" ascii
        $rec2 = "CreditCardTypes" ascii
        $rec3 = "cAesGcm" ascii
        $rec4 = "cBCrypt" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 5MB and
        (
            (2 of ($v*) and 1 of ($hvnc*)) or
            (3 of ($rec*)) or
            ($v3 and $v4 and $hvnc1)
        )
}title: VenomRAT HVNC Hidden Browser Profile Cloning and Sandbox Bypass Flags
id: 4f8e2a1c-9b3d-4e7f-8a2c-1d5e6f7a8b9c
status: stable
description: Detects VenomRAT HVNC spawning Chromium-based browsers inside a hidden desktop with sandbox and GPU acceleration disabled pointing to a cloned User Data directory.
author: CyberTrace Defense Engineering
date: 2026/10/31
references:
- https://attack.mitre.org/techniques/T1113/
- https://attack.mitre.org/techniques/T1539/
tags:
- attack.collection
- attack.t1113
- attack.credential_access
- attack.t1539
logsource:
category: process_creation
product: windows
detection:
selection_browser:
Image|endswith:
- '\chrome.exe'
- '\msedge.exe'
- '\brave.exe'
selection_flags:
CommandLine|contains|all:
- '--no-sandbox'
- '--allow-no-sandbox-job'
- '--disable-3d-apis'
- '--disable-gpu'
condition: selection_browser and selection_flags
falsepositives:
- Unlikely in standard enterprise workstation environments.
level: critical07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
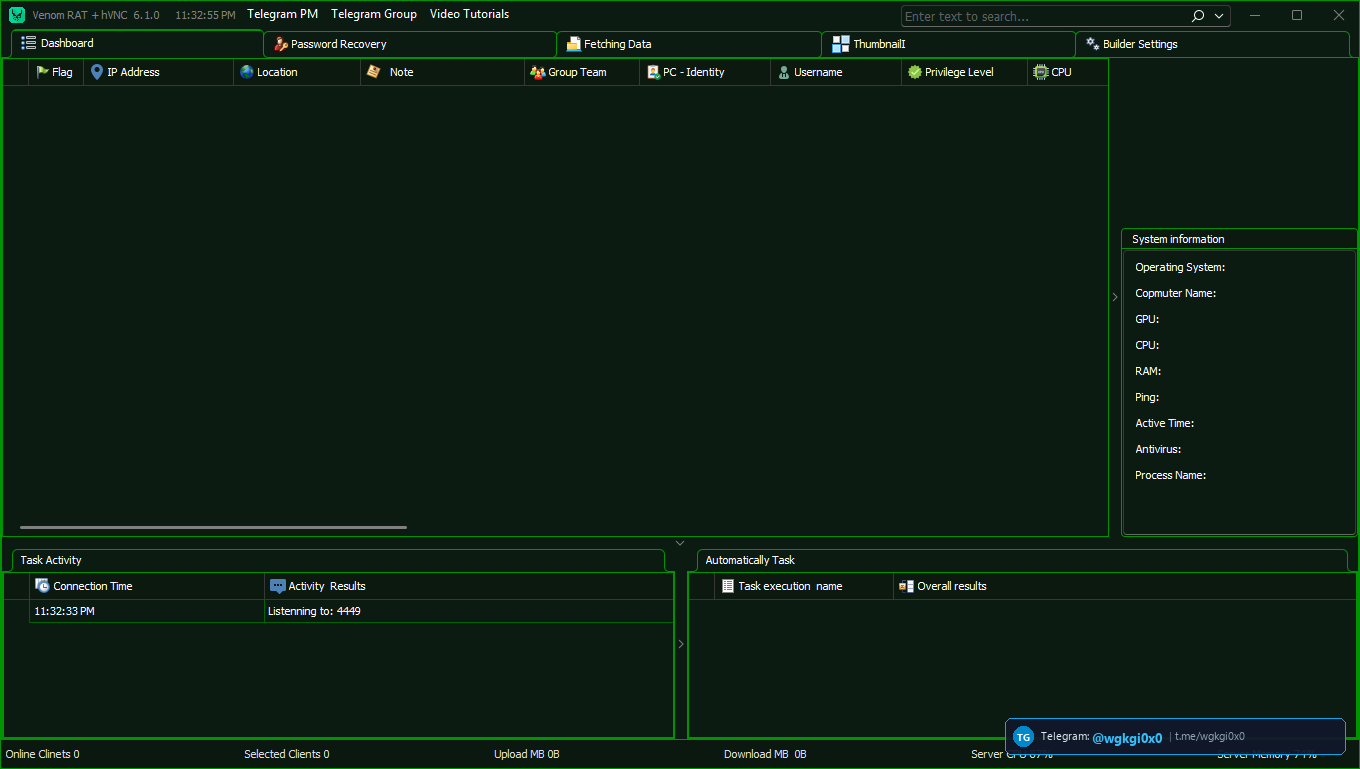
VenomRAT v6.1.0 WinForms controller displaying connected clients, Password Recovery tab, Builder Settings, and automated task execution.
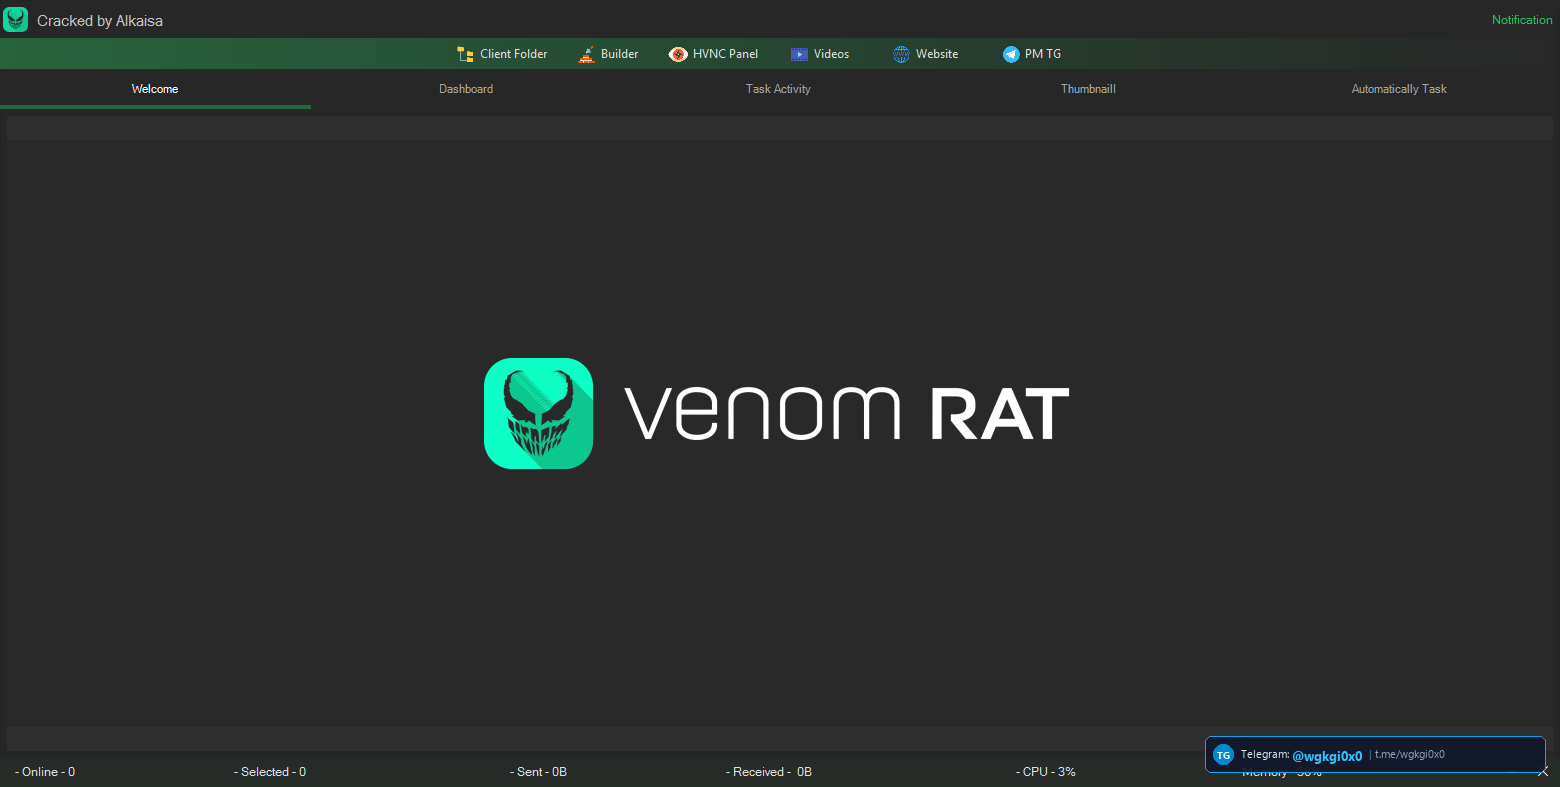
VenomRAT main dashboard highlighting Client Folder, Builder, HVNC Panel, and active listener telemetry.
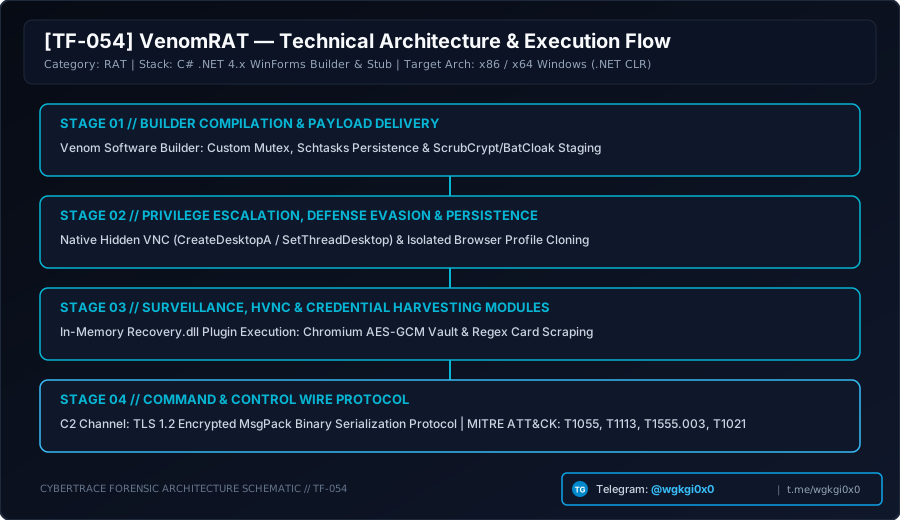
Forensic architecture schematic detailing VenomRAT .NET stub execution, CreateDesktopA HVNC session cloning, Recovery.dll stealer plugin, and TLS MessagePack C2.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
VenomRAT (RAT)
.NET remote access trojan derived from Quasar/AsyncRAT featuring native CreateDesktopA Hidden VNC (HVNC), automated browser profile cloning, and an in-memory Recovery.dll stealer module.
C2 Architecture: {'framing': '4-byte Little-Endian integer length header indicating compressed payload size, followed by a 4-byte Little-Endian integer indicating uncompressed MessagePack size, followed by GZip-compressed MessagePack bytes', 'serialization': 'Custom
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ VenomRAT (RAT)
Детальный технический анализ VenomRAT + HVNC (v6.1.0) — трояна удаленного доступа (RAT) и стилера на базе C# .NET. В отчете рассматриваются создание скрытого рабочего стола через Win32 API CreateDesktopA (HVNC), клонирование профилей браузеров, извлечение учетных данных с помощью плагина Recovery.dll, UAC-байпас через fodhelper.exe и защита сборок обфускатором ConfuserEx.
Архитектура C2: Бинарная сериализация MessagePack поверх TLS 1.2 (SslStream) с AES-256 шифрованием конфигурации и проверкой взаимных сертификатов.
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
VenomRAT (RAT) विश्लेषण
VenomRAT + HVNC (v6.1.0) एक C# .NET आधारित विंडोज रिमोट एक्सेस ट्रोजन (RAT) और स्टीलर फ्रेमवर्क है। इस तकनीकी CTI विश्लेषण में CreateDesktopA हिडन डेस्कटॉप (HVNC) क्लोनिंग, Recovery.dll ब्राउज़र क्रेडेंशियल हार्वेस्टिंग, fodhelper UAC बाईपास और मेमोरी इंजेक्शन तकनीक का पूर्ण विवरण दिया गया है।
C2 संचार: TLS 1.2 (SslStream) और AES-256 एन्क्रिप्टेड कॉन्फ़िगरेशन के साथ संपीड़ित MessagePack बाइनरी C2 प्रोटोकॉल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).