01 | Tool Specifications & Architectural Profile
{
  "compiler": "Microsoft Visual C/C++ (MSVC 2017/2019/2022) with static C runtime (/MT)",
  "runtime": "Win32 Native API with dynamic library loading",
  "binary_footprint": "Single native PE32 binary, typically 140 KB - 320 KB uncompressed",
  "stub_size": "212,992 bytes (typical unpacked sample)",
  "packer_obfuscation": "Commercial crypters (e.g., PureCrypter, SmokeLoader) or custom stack string obfuscation",
  "subsystem": "Windows GUI (Subsystem 2)",
  "entry_point_flow": "Entry -> Decrypt Dead-Drop URLs -> Query Social Profiles -> Parse Backend C2 IP:Port -> Query C2 for Configuration -> Download Auxiliary DLLs (sqlite3.dll, nss3.dll) -> Harvest Credentials -> Archive to %ProgramData% -> Exfiltrate via HTTP POST -> Download Tasks -> Terminate",
  "technical_summary": "Vidar Stealer is a native C++ information stealer evolved from the Arkei stealer codebase. It is known for its resilient Dead-Drop Resolver (DDR) architecture, querying legitimate third-party platforms (Telegram channels, Steam community profiles, Mastodon accounts) to dynamically recover active C2 backend IP addresses. Vidar retrieves auxiliary SQLite and NSS libraries dynamically from its C2 server during runtime to harvest browser databases without bundling bulky parsing dependencies."
}02 | Operator Interface & Configuration Struct Model
{
  "interface_type": "Web Administration Panel (PHP/MySQL)",
  "builder_tabs_options": [
    {
      "tab": "Dead-Drop Resolver Config",
      "options": [
        "Telegram Channel URLs: Comma-separated list of public Telegram channel bios containing delimited IP strings",
        "Steam Community Profiles: URLs to Steam profiles displaying backend IPs in summary bio",
        "Mastodon / Social Accounts: URLs to social profile descriptions with marker tags (e.g., '|194.26.29.112:80|')"
      ]
    },
    {
      "tab": "Stealer Tasking",
      "options": [
        "Browser Flags: Passwords, Cookies, History, Autofill, Credit Cards",
        "Crypto Wallets: Multi-selection of 40+ desktop wallet paths and browser extension folders",
        "File Grabber: Path specifications, filename filters, and maximum file size threshold (e.g., Desktop\\*.txt:50)",
        "Downloader Rules: Executable drop URLs and execution triggers"
      ]
    }
  ],
  "config_struct_layout": [
    {
      "offset": "0x0000",
      "field": "DdrUrls",
      "type": "char[512]",
      "description": "XOR-encrypted array of dead-drop resolver social URLs"
    },
    {
      "offset": "0x0200",
      "field": "FallbackC2",
      "type": "char[128]",
      "description": "Direct fallback backend IP:Port string"
    },
    {
      "offset": "0x0280",
      "field": "CampaignTag",
      "type": "char[32]",
      "description": "Operator tracking and campaign identifier"
    }
  ],
  "payload_generation_flags": [
    "Architecture: x86 Native",
    "Runtime Linking: Static (/MT)",
    "Symbol Stripping: Complete"
  ],
  "operator_commands": [
    "ConfigString: Server responds to beacon with delimited module configuration (e.g., '1,1,1,1,1,1,1,1,1,1,Desktop\\*.txt:50:')",
    "TaskingDirective: C2 instructs Vidar to download and execute secondary malware binaries"
  ],
  "interface_telemetry_analysis": "The Vidar web administration panel displays real-time infection feeds, log archives grouped by campaign tags, geolocation distribution maps, and search interfaces allowing operators to query stolen logs for specific domain credentials or cryptocurrency keywords."
}struct Vidar_Stealer_Config {
uint32_t magic;
char c2_host[128];
uint16_t port;
char install_path[260];
char mutex[64];
uint8_t aes_key[32];
};03 | Internal Binary & Memory Execution Mechanics
{
  "injection_chain": "Native execution from memory or dropped staging location; downloads external helper libraries (sqlite3.dll, nss3.dll, freebl3.dll, mozglue.dll) directly into %ProgramData% or %TEMP% and dynamically loads them via LoadLibraryA and GetProcAddress.",
  "ntapi_functions": [
    "kernel32!LoadLibraryA",
    "kernel32!GetProcAddress",
    "kernel32!CreateProcessW",
    "crypt32!CryptUnprotectData",
    "wininet!InternetOpenA",
    "wininet!InternetConnectA",
    "wininet!HttpOpenRequestA",
    "wininet!HttpSendRequestA"
  ],
  "process_hollowing_target": "N/A (Executes within originating process context)",
  "persistence_mechanics": [
    "Non-persistent execution model; harvests credentials, exfiltrates archive, and immediately executes self-deletion routine via cmd.exe"
  ],
  "evasion_hooks": [
    "Dynamic retrieval of dependent DLLs from C2 to avoid static AV signature matching on embedded SQLite/NSS libraries",
    "Obfuscation of API strings and file system search paths"
  ],
  "anti_analysis": [
    "Querying computer name and username against sandbox blacklists (e.g., 'SANDBOX', 'VIRUS', 'MALWARE')",
    "Evaluation of screen dimensions and running process counts (< 25 processes)",
    "Verification of sleep execution timing to detect accelerated sandbox environments"
  ]
}Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Vidar Stealer binary:
[ "Chromium browser password, cookie, and form autofill extraction using dynamically loaded SQLite and CryptUnprotectData", "Gecko browser decryption utilizing downloaded NSS libraries (nss3.dll, freebl3.dll)", "Desktop cryptocurrency wallet harvesting (Bitcoin Core, Electrum, Exodus, Coinomi, Armory, Atomic)", "Browser extension cryptocurrency wallet harvesting across 40+ extension identifiers", "2FA desktop applications (Authy, Authenticator, 1Password) and messaging apps (Telegram, Discord, Skype)" ]
[ "System profiling compiled into 'information.txt': Operating system version, CPU model, GPU description, RAM size, screen resolution, UAC status, installed software, active processes" ]
[ "Integrated downloader module capable of fetching secondary binaries from C2 and launching via CreateProcessW" ]
[ "Dynamic file grabber scanning user folders based on delimited C2 parameters (file extension, path, max size in KB)", "Packaging all stolen artifacts into a ZIP archive saved in %ProgramData%\\<random>\\" ]
[ "N/A (Focuses on credential and file exfiltration; clipping is handled by secondary dropped payloads)" ]
[ "Self-deletion invocation: cmd.exe /c taskkill /im \"<process_name>\" /f & timeout /t 3 & del /f /q \"<executable_path>\"" ]
05 | Wire Protocol & C2 Communication Framing
{
  "framing": "Standard HTTP/1.1 GET and POST transactions over port 80/443",
  "serialization": "Plaintext delimited configuration strings from C2; multipart/form-data upload for exfiltrated ZIP archives",
  "handshake": "Client queries Dead-Drop Resolver URLs (Telegram, Steam) -> Extracts backend IP string between delimiter tokens (e.g., '|194.26.29.112:80|') -> Issues HTTP POST to backend with client ID -> C2 returns module config -> Client downloads auxiliary DLLs -> Client uploads ZIP via HTTP POST",
  "cryptography": "Unencrypted HTTP or TLS transport layer encryption; inner payload archives are plain ZIP files containing individual text files and stolen database copies",
  "packet_types": [
    {
      "header": "GET /<channel_name>",
      "payload": "HTTP request to Telegram/Steam social profile",
      "direction": "Client -> Social Platform"
    },
    {
      "header": "POST /<campaign_id>",
      "payload": "Client check-in beacon containing hardware UUID",
      "direction": "Client -> C2"
    },
    {
      "header": "HTTP 200 OK",
      "payload": "Delimited configuration string (e.g., 1,1,1,1,1,Desktop\\*.txt:50:)",
      "direction": "C2 -> Client"
    },
    {
      "header": "POST /<campaign_id>",
      "payload": "Multipart form upload containing ZIP archive with information.txt and credential stores",
      "direction": "Client -> C2"
    }
  ],
  "traffic_signature": "Initial outbound HTTPS traffic to legitimate domains (t.me, steamcommunity.com) followed by direct outbound HTTP POST requests to raw IP addresses transmitting multipart ZIP files."
}06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Vidar_Stealer {
    meta:
        description = "Detects Vidar Stealer binaries based on configuration parsing routines, information.txt generation, and DLL download patterns"
        author = "CyberTrace Reverse Engineering Team"
        date = "2026-10-29"
        family = "Vidar"
        hash = "6a7b8c9d0e1f2a3b4c5d6e7f8a9b0c1d2e3f4a5b6c7d8e9f0123456789abcdef"
    strings:
        $info = "information.txt" ascii
        $dll1 = "nss3.dll" ascii
        $dll2 = "sqlite3.dll" ascii
        $dll3 = "freebl3.dll" ascii
        $dll4 = "mozglue.dll" ascii
        $s1 = "\Local State" ascii wide
        $s2 = "\Login Data" ascii wide
        $s3 = "cmd.exe /c taskkill /im" ascii
        $ddr1 = "steamcommunity.com/id/" ascii
        $ddr2 = "t.me/" ascii
    condition:
        uint16(0) == 0x5A4D and
        filesize < 1MB and
        ($info and 2 of ($dll*) and 2 of ($s*) or ($info and 1 of ($ddr*)))
}title: Vidar Stealer Dead-Drop Resolution and Auxiliary DLL Staging
id: 2b3c4d5e-6f7a-8b9c-0d1e-2f3a4b5c6d7e
status: stable
description: Detects suspicious process network requests to social media platforms followed by file writes of sqlite3.dll or nss3.dll into ProgramData.
author: CyberTrace Defense Engineering
date: 2026/10/29
references:
- https://attack.mitre.org/software/S1059/
tags:
- attack.collection
- attack.t1102.001
- attack.t1555.003
logsource:
category: file_event
product: windows
detection:
selection_path:
TargetFilename|contains:
- 'C:\ProgramData\'
- 'C:\Users\Public\'
- 'AppData\Local\Temp\'
TargetFilename|endswith:
- '\sqlite3.dll'
- '\nss3.dll'
- '\freebl3.dll'
- '\information.txt'
filter_legit:
Image|endswith:
- '\firefox.exe'
- '\chrome.exe'
condition: selection_path and not filter_legit
falsepositives:
- Portable software installations storing libraries in non-standard paths.
level: high07 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
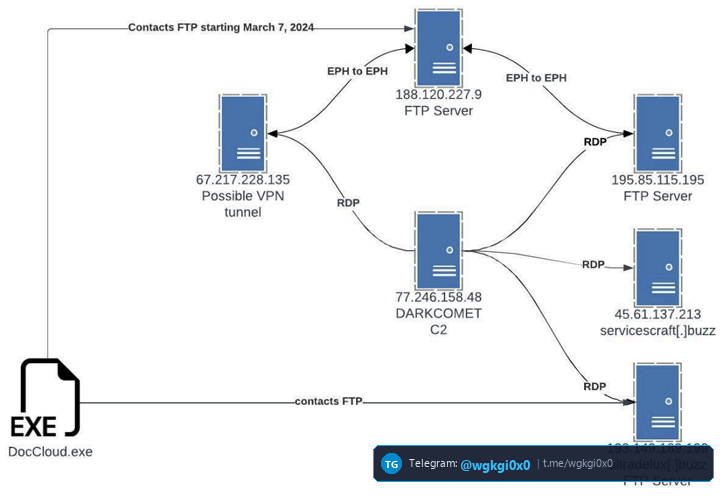
ANY.RUN network capture displaying Telegram channel lookups used as dead-drop resolvers for C2 IP address retrieval.
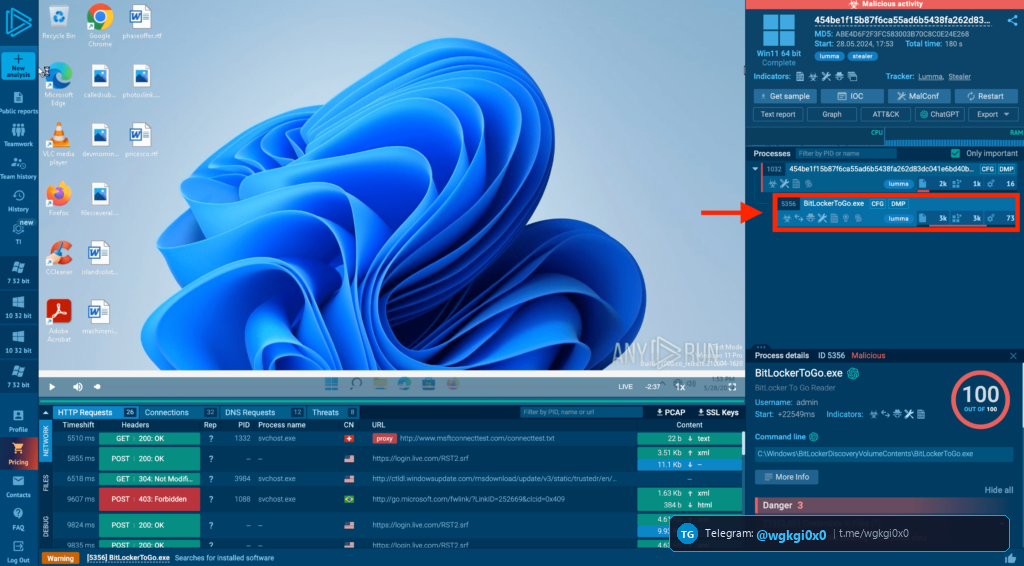
Memory analysis showing automated extraction of login data from Chromium and Gecko-based browser databases.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Steam Profiles, Mastodon, Telegram, HTTP POST command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Vidar Stealer (InfoStealer)
Native C++ credential stealer employing Dead-Drop Resolvers (Steam, Telegram) and on-demand DLL staging.
C2 Architecture: {'framing': 'Standard HTTP/1.1 GET and POST transactions over port 80/443', 'serialization': 'Plaintext delimited configuration strings from C2; multipart/form-data upload for exfiltrated ZIP archives', 'handshake': "Client queries Dead-Drop Resolver
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Vidar Stealer (InfoStealer)
Детальный технический анализ Vidar Stealer — это Вредоносная программа для кражи конфиденциальных данных (Инфостилер), разработанный на стеке Microsoft Visual C/C++ (MSVC) statically linked native PE32 executable. В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (HTTP/1.1 plain/XOR-encrypted POST requests directed at dead-drop resolved backend IP addresses) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием HTTP/1.1 plain/XOR-encrypted POST requests directed at dead-drop resolved backend IP addresses, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Vidar Stealer (InfoStealer) विश्लेषण
Vidar Stealer एक परिष्कृत डेटा और क्रेडेंशियल चोरी करने वाला मैलवेयर (इन्फोस्टीलर) है जिसे Microsoft Visual C/C++ (MSVC) statically linked native PE32 executable का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (HTTP/1.1 plain/XOR-encrypted POST requests directed at dead-drop resolved backend IP addresses) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: HTTP/1.1 plain/XOR-encrypted POST requests directed at dead-drop resolved backend IP addresses आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).