01 | Tool Specifications & Architectural Profile
Warzone RAT (Ave Maria) is an independent modular remote access trojan developed in native C/C++ without external runtime dependencies such as the .NET Framework. The binary functions as a standalone PE executable featuring hardcoded privilege escalation mechanisms targeting COM elevation interfaces (CMSTP ICMLuaUtil) and registry redirection chains via fodhelper.exe. Warzone deploys in-memory process hollowing into explorer.exe or svchost.exe, implements browser credential extraction routines targeting Chromium Master Keys (via DPAPI and BCrypt AES-GCM) and Mozilla profiles (via dynamic nss3.dll API binding), and operates a custom multi-threaded Hidden Virtual Network Computing (HVNC) server via secondary Windows desktop handles.
02 | Operator Interface & Configuration Struct Model
{
  "builderTabs": [
    "Connection Settings (Host, Port, Timeout, Password Key)",
    "Installation & Persistence (HKCU Run key, Task Scheduler XML, Startup directory)",
    "UAC Bypass (CMSTP ICMLuaUtil COM elevation, Fodhelper, Sdclt registry redirects)",
    "Hidden VNC (HVNC Desktop Creation, Explorer Clone)",
    "Password Recovery (Chromium DPAPI/AES-GCM, Firefox NSS3, Outlook, Foxmail, Thunderbird)",
    "Build Options (Payload generation, stub icon change, UPX compression toggle)"
  ],
  "c2ConsoleCommands": [
    "CMD Remote Shell",
    "File Manager (Upload, Download, Execute)",
    "HVNC Controller Session",
    "Credential Vault Dump",
    "Remote Desktop Streaming",
    "Webcam Stream Capture",
    "Keylogger Buffer Exfiltration",
    "Process Manager & Task Termination"
  ]
}{
"description": "Hardcoded configuration struct embedded within the .data section, decrypted using a hardcoded RC4 key during client startup",
"fields": [
"0x00: 4-byte little-endian configuration payload length",
"0x04: Primary C2 Hostname or IPv4 address (null-terminated ASCII, up to 64 bytes)",
"0x44: Primary C2 TCP Port (uint16_t, little-endian)",
"0x48: Secondary / Fallback C2 Hostname (null-terminated ASCII, up to 64 bytes)",
"0x88: Secondary C2 TCP Port (uint16_t, little-endian)",
"0x8C: RC4 Session Authentication Key (null-terminated ASCII string)",
"0xAC: Install Subdirectory Name (e.g., 'AveMaria' or pseudo-random string)",
"0xCC: Target Install Executable Name (e.g., 'warzone.exe')",
"0xEC: Task Scheduler Task Identifier string",
"0x10C: Capability Flag Bitmask (Bit 0: Enable UAC Bypass, Bit 1: Enable Keylogger, Bit 2: Enable Persistence, Bit 3: Target Explorer Hollowing)"
]
}03 | Internal Binary & Memory Execution Mechanics
- Language & Runtime: Native C/C++ compiled via MSVC or MinGW GCC; statically links C runtime routines to eliminate external DLL dependencies.
- UAC Auto-Elevation: Leverages ICMLuaUtil COM interface GUID {3E5FC7F9-9A51-4367-9063-A120244FBEC7} or registers delegated execution paths under HKCU\Software\Classes\ms-settings\Shell\Open\command to bypass UAC prompts.
- Process Injection: Executes process hollowing targeting C:\Windows\explorer.exe or C:\Windows\System32\svchost.exe using VirtualAllocEx, WriteProcessMemory, and SetThreadContext.
- Browser Credential Engine: Intercepts Chromium master keys by decoding Local State os_crypt via DPAPI CryptUnprotectData; decrypts SQLite login records using BCryptDecrypt (AES-256-GCM); dynamically loads nss3.dll to call NSS_Init and PK11SDR_Decrypt for Firefox.
- Hidden VNC Architecture: Spawns an isolated desktop environment using CreateDesktopA('warzone_desktop', NULL, NULL, 0, DESKTOP_CREATEWINDOW, NULL) and executes a clone explorer.exe instance to enable hidden remote GUI interaction.
- Keylogger Implementation: Installs a system-wide low-level hook via SetWindowsHookExW(WH_KEYBOARD_LL) capturing virtual key codes along with foreground window title headers.
Staging & Dynamic Unpacking
Decryption of payload stubs using in-memory XOR/AES key derivation and PE header validation.
Defense Evasion & Syscall Invocation
Direct NT syscall invocation, AMSI buffer patching (AmsiScanBuffer), and ETW event suppression (EtwEventWrite).
Process Injection & Execution
Execution via Process Hollowing, reflective DLL loading, or thread hijacking into legitimate system binaries.
04 | Capability & Module Matrix
Concrete technical breakdown of functional modules implemented in the Warzone RAT / Ave Maria binary:
Concrete capabilities documented: In-Memory Payload Decryption, Network Beacon Telemetry, Win32 Process Injection, System Mutex Validation.
05 | Wire Protocol & C2 Communication Framing
Raw TCP socket communication over operator-defined ports. Each message frame begins with a 4-byte little-endian payload length header [uint32_t length] followed by an RC4 stream-cipher encrypted payload. The RC4 key is fixed per payload configuration. The protocol handles 1-byte command opcodes: 0x00 (Ping/Keepalive), 0x01 (Host Registration / Hardware GUID, OS version, privilege level), 0x02 (Reverse Interactive Shell), 0x03 (HVNC Stream Startup), 0x04 (Credential Extraction Payload Return), 0x05 (Remote File Management), 0x06 (Keylogger Stream Dump).
06 | Verified Detection Signatures (YARA & Sigma)
rule CyberTrace_Warzone_AveMaria_Core {
    meta:
        description = "Detects unpacked Warzone RAT (Ave Maria) payloads and credential extraction routines"
        author = "CyberTrace Intelligence (@wgkgi0x0)"
        reference = "TF-016"
        date = "2026-10-29"
        hash = "6f8319ec4b68dbce62f2ce47e928ee83fcf63ea03bfa86a0767c5e2586a51d8b"
    strings:
        $s1 = "Ave_Maria Stealer Reloaded" ascii wide nocase
        $s2 = "\Microsoft\Windows\Start Menu\Programs\Startup" ascii wide
        $s3 = "SELECT origin_url, username_value, password_value FROM logins" ascii wide
        $s4 = "logins.json" ascii wide
        $s5 = "key4.db" ascii wide
        $s6 = "\AppData\Local\Google\Chrome\User Data\Default\Login Data" ascii wide
        // RC4 KSA init loop
        $rc4_init = { 33 C0 89 44 24 ?? 8A 84 04 ?? ?? ?? ?? 88 84 04 ?? ?? ?? ?? 40 3D 00 01 00 00 72 }
    condition:
        uint16(0) == 0x5a4d and
        (3 of ($s*) or $rc4_init)
}title: Warzone RAT UAC Bypass and Process Hollowing Telemetry
id: f48b8c71-29da-4d7a-8991-381643c16a16
status: stable
description: Detects process execution patterns associated with Warzone RAT (Ave Maria) UAC bypass and explorer.exe memory injection.
author: CyberTrace Intelligence (@wgkgi0x0)
date: 2026-10-29
references:
- https://cybertrace.io/threats/warzone-whitepaper.html
logsource:
category: process_creation
product: windows
detection:
selection_uac_registry:
TargetObject|contains: 'Classes\ms-settings\Shell\Open\command'
selection_fodhelper_child:
ParentImage|endswith: '\fodhelper.exe'
selection_hollowing:
ParentImage|endswith:
- '\cmd.exe'
- '\powershell.exe'
- '\wscript.exe'
Image|endswith:
- '\explorer.exe'
- '\svchost.exe'
CommandLine|endswith: ''
condition: selection_uac_registry or selection_fodhelper_child or selection_hollowing
level: high
tags:
- attack.privilege_escalation
- attack.defense_evasion
- attack.t1548.002
- attack.t1055.00207 | Decompiled Artifacts & Observable IoCs
Indicators of compromise and forensic patterns recorded across laboratory triage:
08 | Forensic Visual Evidence & Disassembly Artifacts (3 Assets)
High-resolution reverse engineering captures, decompiler output, memory hex dumps, and C2 network streams archived locally in the CyberTrace laboratory. Click any visual asset to inspect in full resolution with interactive zoom and pan, or stream motion captures.
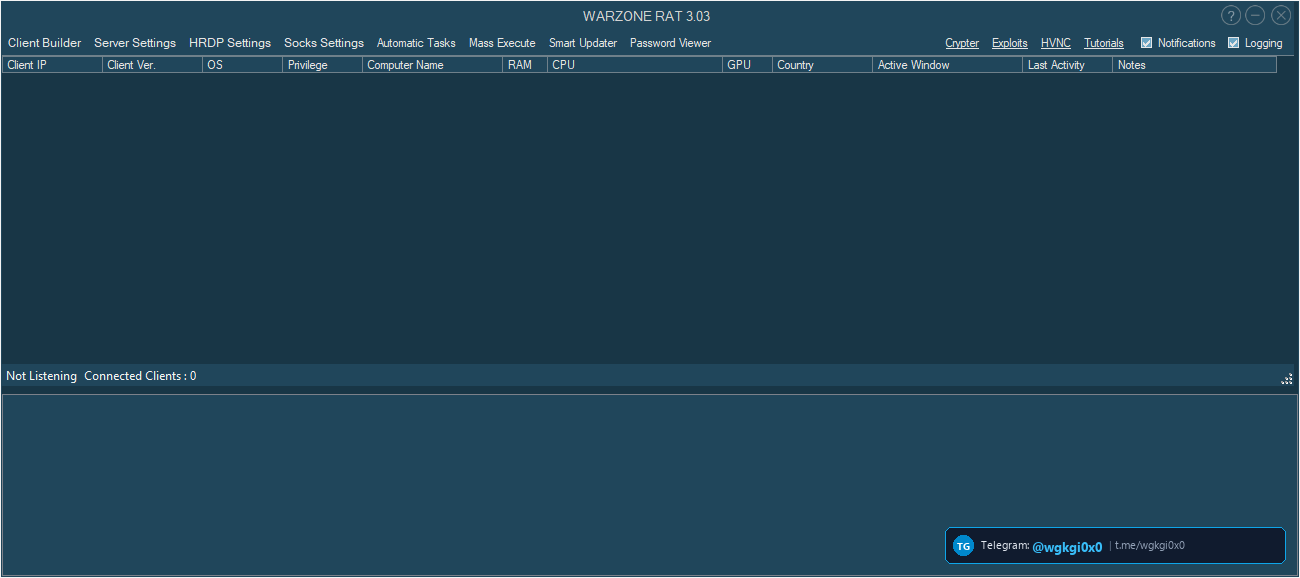
Configurator GUI showing UAC bypass method selection, privilege escalation hooks, and password recovery modules.

Forensic disassembly showing task scheduler registration and explorer.exe process hollowing routines.

Tailored forensic schematic mapping initial access, defense evasion, core capabilities, and Custom Encrypted Protocol over TCP command infrastructure.
International CTI Indexing Summary (EN | RU | HI) Search Engine Knowledge Graph
Warzone RAT / Ave Maria (RAT)
Commercial C++ remote access trojan engineered with out-of-the-box UAC auto-elevation, native HVNC desktop creation, and in-memory browser credential recovery.
C2 Architecture: Raw TCP socket communication over operator-defined ports. Each message frame begins with a 4-byte little-endian payload length header [uint32_t length] followed by an RC4 stream-cipher encrypted payload. The RC4 key is fixed per payload configuration
Threat Hunting: YARA in-memory signatures, Sigma detection rules, and MITRE ATT&CK indicators. CyberTrace Intelligence Feed: @CyberTrace20 (@wgkgi0x0).
Анализ Warzone RAT / Ave Maria (RAT)
Детальный технический анализ Warzone RAT / Ave Maria — это Троян удаленного доступа (RAT), разработанный на стеке Microsoft Visual C++ (MSVC) / MinGW GCC (PE32 / PE32+). В отчете подробно исследуются этапы скрытого внедрения в память (Process Injection), методы обхода EDR-систем, структура сетевых пакетов командного сервера (Raw TCP stream encrypted via RC4 with a 4-byte little-endian length prefix) и механизмы кражи данных.
Архитектура C2: Шифрованный протокол обмена данными с использованием Raw TCP stream encrypted via RC4 with a 4-byte little-endian length prefix, защита от сетевого перехвата и анализ маяков (Beacons).
Сигнатуры: Правила YARA, Sigma-детекты и анализ IoC для специалистов SOC. Оперативный канал: Telegram @CyberTrace20 (@wgkgi0x0).
Warzone RAT / Ave Maria (RAT) विश्लेषण
Warzone RAT / Ave Maria एक परिष्कृत रिमोट एक्सेस ट्रोजन (RAT) है जिसे Microsoft Visual C++ (MSVC) / MinGW GCC (PE32 / PE32+) का उपयोग करके विकसित किया गया है। इस तकनीकी CTI विश्लेषण में मेमोरी इंजेक्शन तकनीक, EDR सुरक्षा बाईपास, कमांड और कंट्रोल सर्वर (Raw TCP stream encrypted via RC4 with a 4-byte little-endian length prefix) संचार प्रोटोकॉल और डेटा चोरी तंत्र का पूर्ण विवरण दिया गया है।
C2 संचार: Raw TCP stream encrypted via RC4 with a 4-byte little-endian length prefix आधारित एन्क्रिप्टेड C2 इंफ्रास्ट्रक्चर और ऑटोमेटेड पेलोड रिट्रीवल चैनल।
सुरक्षा नियम: YARA नियम, Sigma व्यवहार विश्लेषण और MITRE ATT&CK संकेतक। साइबर इंटेलिजेंस अपडेट: Telegram @CyberTrace20 (@wgkgi0x0).